
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
18 results
columbo preview

columbo

GitHubvisma-prodsec/columbo

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

anomaly-detectionbinary-analysisdigital-forensics+3
61
4 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
672 months ago
KsDumper preview

KsDumper

GitHubequifox/ksdumper

Dumping processes using the power of kernel space !
binary-analysiseducationexploitation+2
1.1k3 years ago
pe_tree preview
Archived

pe_tree

GitHubblackberry/pe_tree

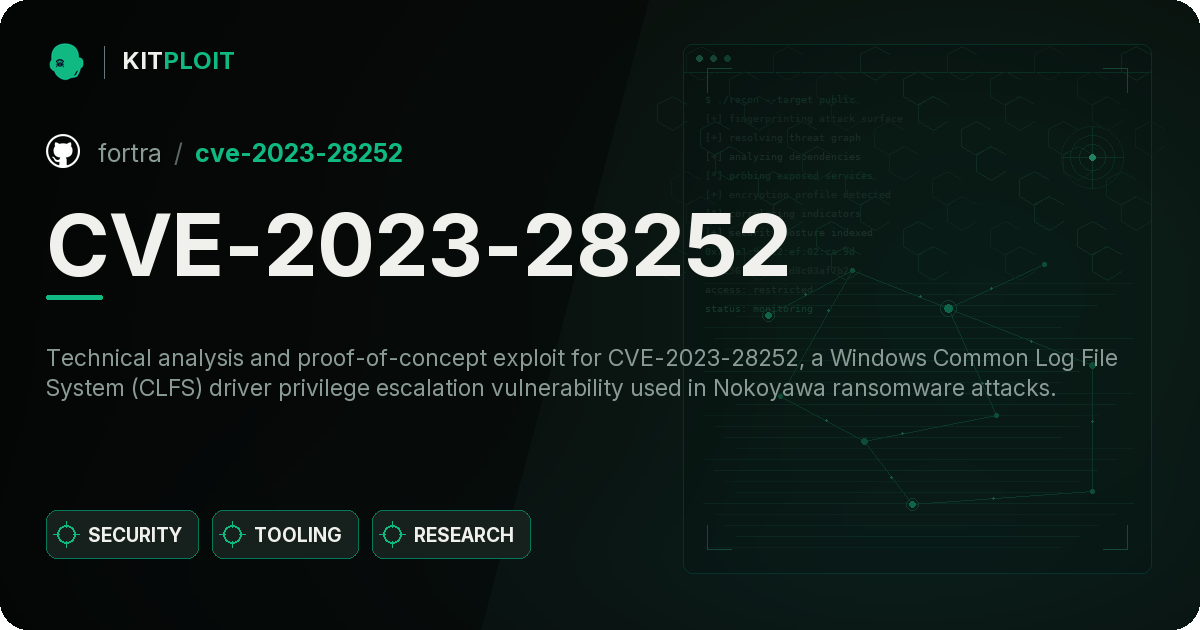
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
binary-analysisdebuggersdigital-forensics+5
1.3k4 years ago
CVE-2023-28252 preview

CVE-2023-28252

GitHubfortra/cve-2023-28252

Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…

binary-exploitationdebuggersexploitation+4
1843 years ago
CVE-2020-17057 preview

CVE-2020-17057

GitHublsw29475/cve-2020-17057

Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.
binary-exploitationexploitationmemory-forensics+1
25 years ago
throttlestop-exploit-rw preview

throttlestop-exploit-rw

GitHubamrhuss/throttlestop-exploit-rw

Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
binary-exploitationeducationexploitation+3
1510 months ago
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
digital-forensicsforensicsinformation-gathering+3
8617 years ago
r0ak preview

r0ak

GitHubharryanon/r0ak

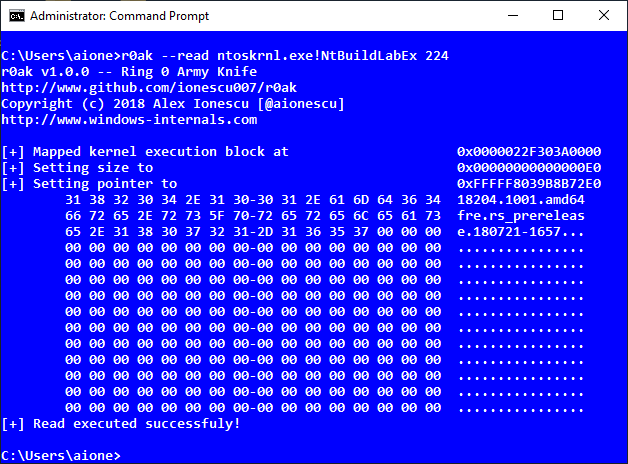
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
binary-exploitationdebuggersexploitation+5
1088 years ago
nullmap preview

nullmap

GitHubsamueltulach/nullmap

Using CVE-2023-21768 to manual map kernel mode driver
binary-exploitationexploitationmemory-forensics+3
2013 years ago
NativeDump preview

NativeDump

GitHubricardojoserf/nativedump

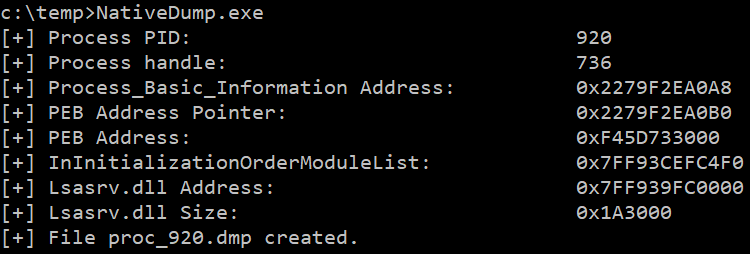
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)

memory-forensicspost-exploitationred-teaming
7501 month ago
HandleKatz preview

HandleKatz

GitHubcodewhitesec/handlekatz

PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
defensive-toolsmemory-forensicspayload-generation+3
5973 years ago
extractTVpasswords preview

extractTVpasswords

GitHubvah13/extracttvpasswords

tool to extract passwords from TeamViewer memory using Frida
exploitationmemory-forensicspassword-cracking+3
4638 years ago
DeepSleep preview

DeepSleep

GitHubtheflink/deepsleep

A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
exploitationmemory-forensicspayload-development+1
3754 years ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
cryptographydigital-forensicseducation+7
314 months ago
CVE-2025-7771-Vulnerability-Exploration preview

CVE-2025-7771-Vulnerability-Exploration

GitHubd4rkks/cve-2025-7771-vulnerability-exploration

Escalating privilege in the system from unsigned driver using throttlestop vulnerability
binary-exploitationeducationexploitation+4
135 months ago
CVE-2023-32784-kdbxpassdmp preview

CVE-2023-32784-kdbxpassdmp

GitHubamperclock/cve-2023-32784-kdbxpassdmp

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.

digital-forensicsexploitationforensics+3
4 months ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k11h 31m ago