
Blackbone
 darthton/blackbone
Windows memory hacking library
binary-analysisdebuggersdynamic-analysis-sandboxing+9
darthton/blackboneWindows memory hacking library
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
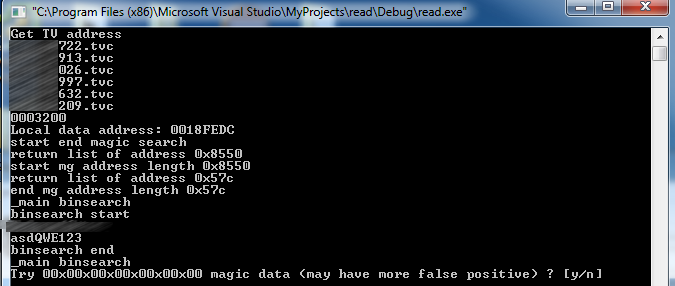 vah13/extracttvpasswords
tool to extract passwords from TeamViewer memory using Frida
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
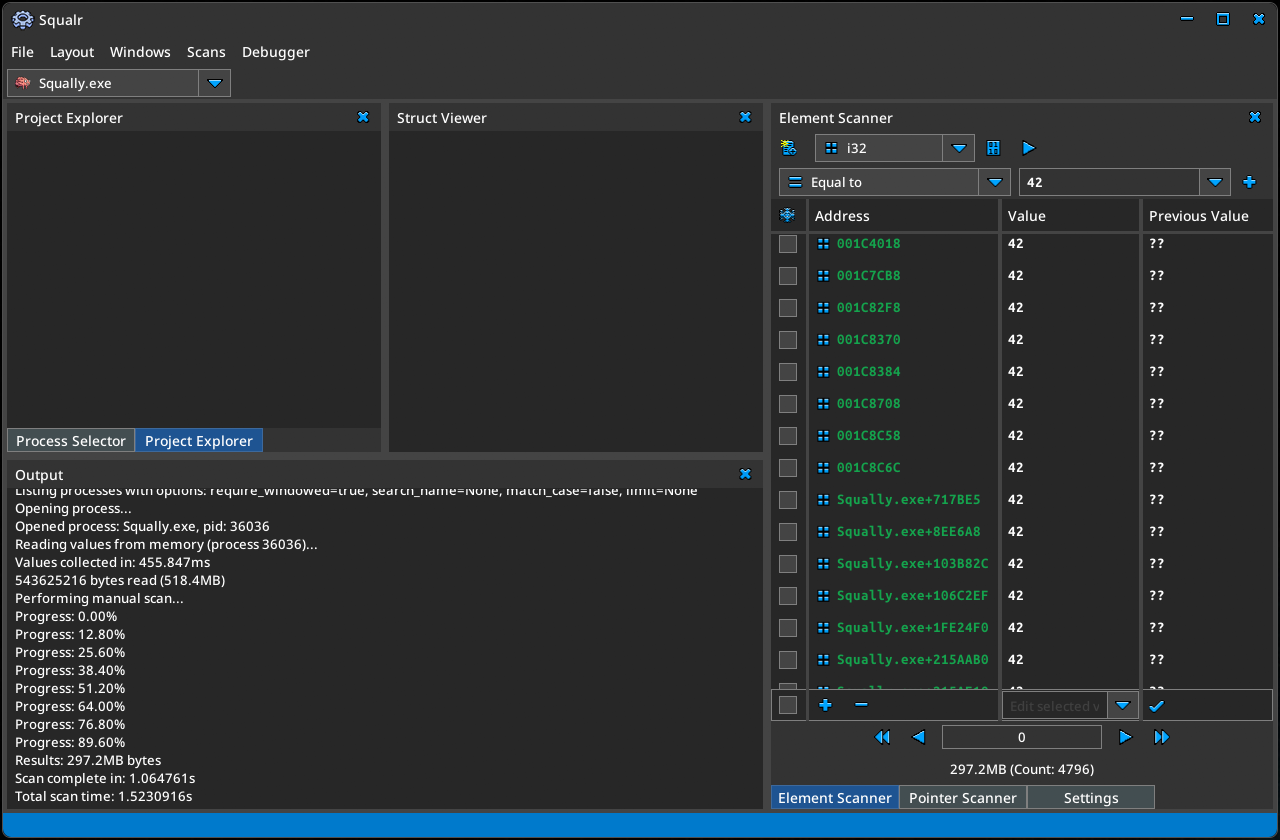 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.