
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
fridump preview

fridump

GitHubnightbringer21/fridump

Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…

digital-forensicsforensicsinformation-gathering+3
861
7 years ago
invoker preview
Archived

invoker

GitHubivan-sincek/invoker

Penetration testing utility and antivirus assessment tool.

binary-analysiseducationexploitation+6
3123 years ago
ghidra preview

ghidra

GitHubnationalsecurityagency/ghidra

Ghidra is a software reverse engineering (SRE) framework

ai-assisted-reversingandroid-securitybinary-analysis+17
75.8k17h 50m ago
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset

ai-assisted-reversingandroid-securitybinary-analysis+16
24.8k1 day ago
objection preview

objection

GitHubsensepost/objection

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
android-securitydynamic-analysis-sandboxingexploitation+9
9.4k1 month ago
ThreadStackSpoofer preview

ThreadStackSpoofer

GitHubmgeeky/threadstackspoofer

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…

exploit-frameworksmalware-analysismemory-forensics+4
1.2k4 years ago
AceLdr preview

AceLdr

GitHubkyleavery/aceldr

Cobalt Strike UDRL for memory scanner evasion.
exploit-frameworksmemory-forensicspayload-development+2
1.0k2 years ago
Pixel_GPU_Exploit preview

Pixel_GPU_Exploit

GitHub0x36/pixel_gpu_exploit

Android 14 kernel exploit for Pixel7/8 Pro
android-securitybinary-exploitationeducation+4
5622 years ago
apk-medit preview

apk-medit

GitHubsterrasec/apk-medit

memory search and patch tool on debuggable apk without root & ndk

android-securitybinary-analysismemory-forensics+2
4343 months ago
Shelter preview

Shelter

GitHubkudaes/shelter

ROP-based sleep obfuscation to evade memory scanners
exploit-frameworksmemory-forensicsred-teaming
3931 year ago
cve-2019-2215 preview

cve-2019-2215

GitHubkangtastic/cve-2019-2215

Temproot for Pixel 2 and Pixel 2 XL via CVE-2019-2215
android-securitybinary-exploitationdebuggers+4
1376 years ago
ulexecve preview

ulexecve

GitHubanvilsecure/ulexecve

Executes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…
exploitationmemory-forensicspenetration-testing+3
2162 years ago
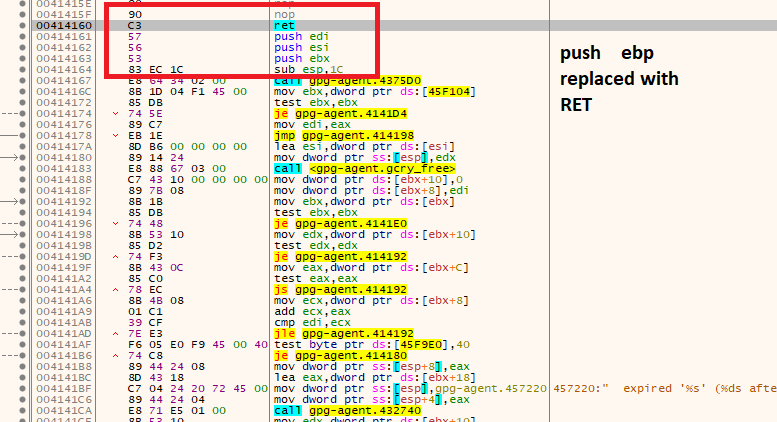
gpg_reaper preview

gpg_reaper

GitHubkacperszurek/gpg_reaper

GPG Reaper - Obtain/Steal/Restore GPG Private Keys from gpg-agent cache/memory

exploitationmemory-forensicspenetration-testing+1
968 years ago
Astral_Projection preview

Astral_Projection

GitHubkuwaitist/astral_projection

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
exploit-frameworksmemory-forensicspayload-development+4
734 months ago
oppo-ghostlock preview

oppo-ghostlock

GitHubpubglite55/oppo-ghostlock

OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation

android-securitybinary-exploitationeducation+7
656 days ago
CVE-2015-6620-POC preview

CVE-2015-6620-POC

GitHubflankerhqd/cve-2015-6620-poc

POC for CVE-2015-6620, AMessage unmarshal arbitrary write
android-securitybinary-exploitationexploitation+3
3810 years ago
CVE-2020-0022 preview

CVE-2020-0022

GitHubpolo35/cve-2020-0022

CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
android-securitybinary-exploitationbluetooth-security+5
375 years ago
libmsm_vfe_read_exploit preview

libmsm_vfe_read_exploit

GitHubandroid-rooting-tools/libmsm_vfe_read_exploit

CVE-2014-4321 exploit

android-securitybinary-exploitationexploitation+2
2211 years ago
Previous123Next