
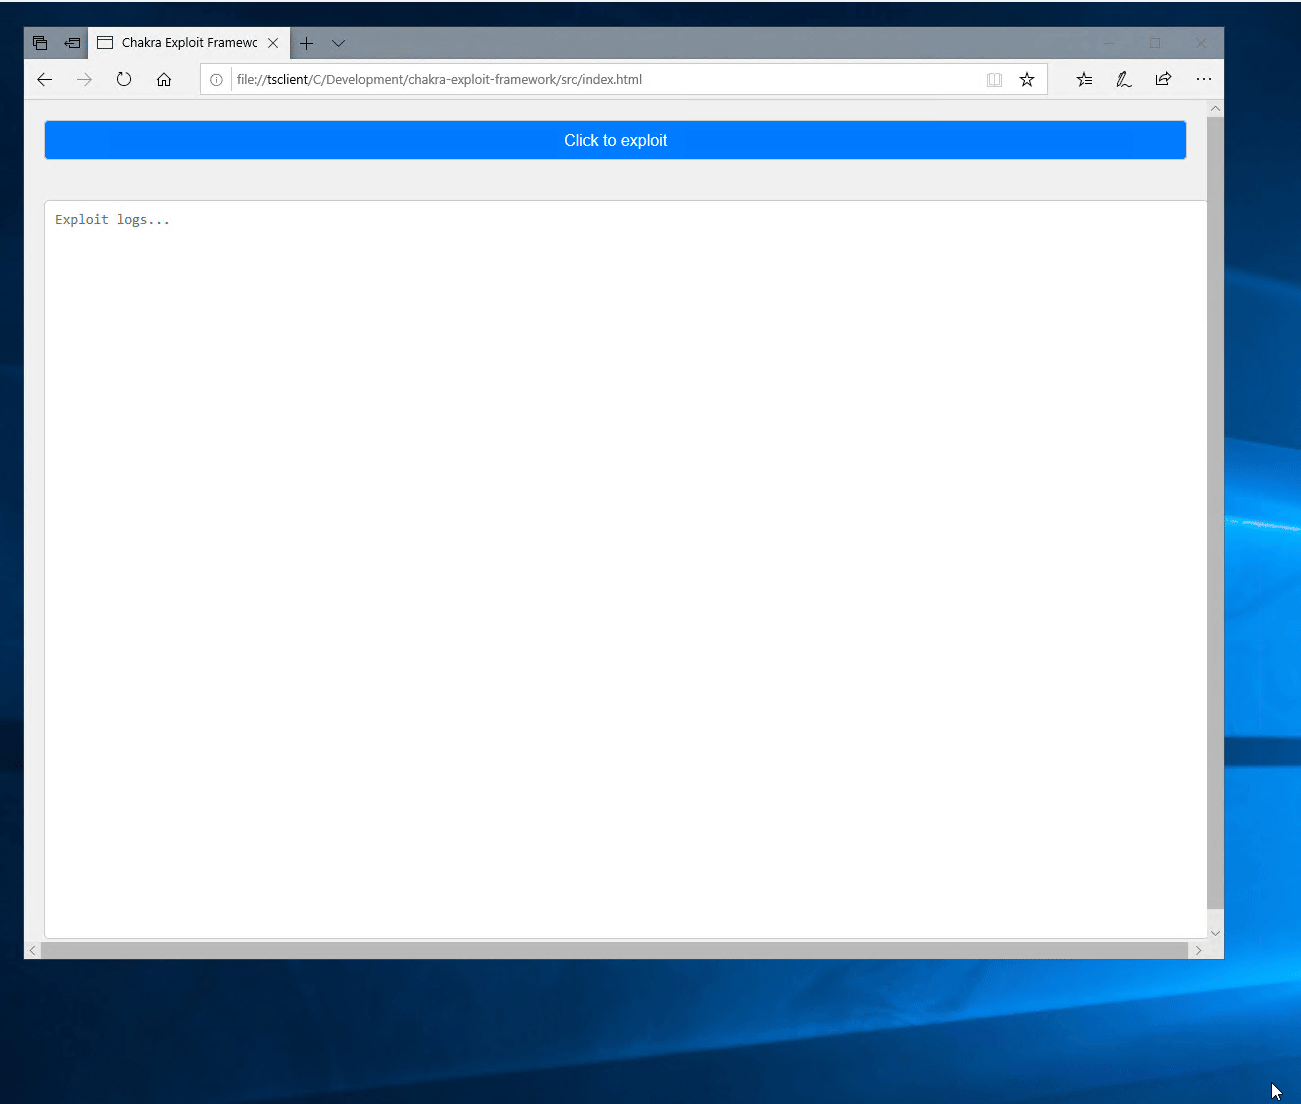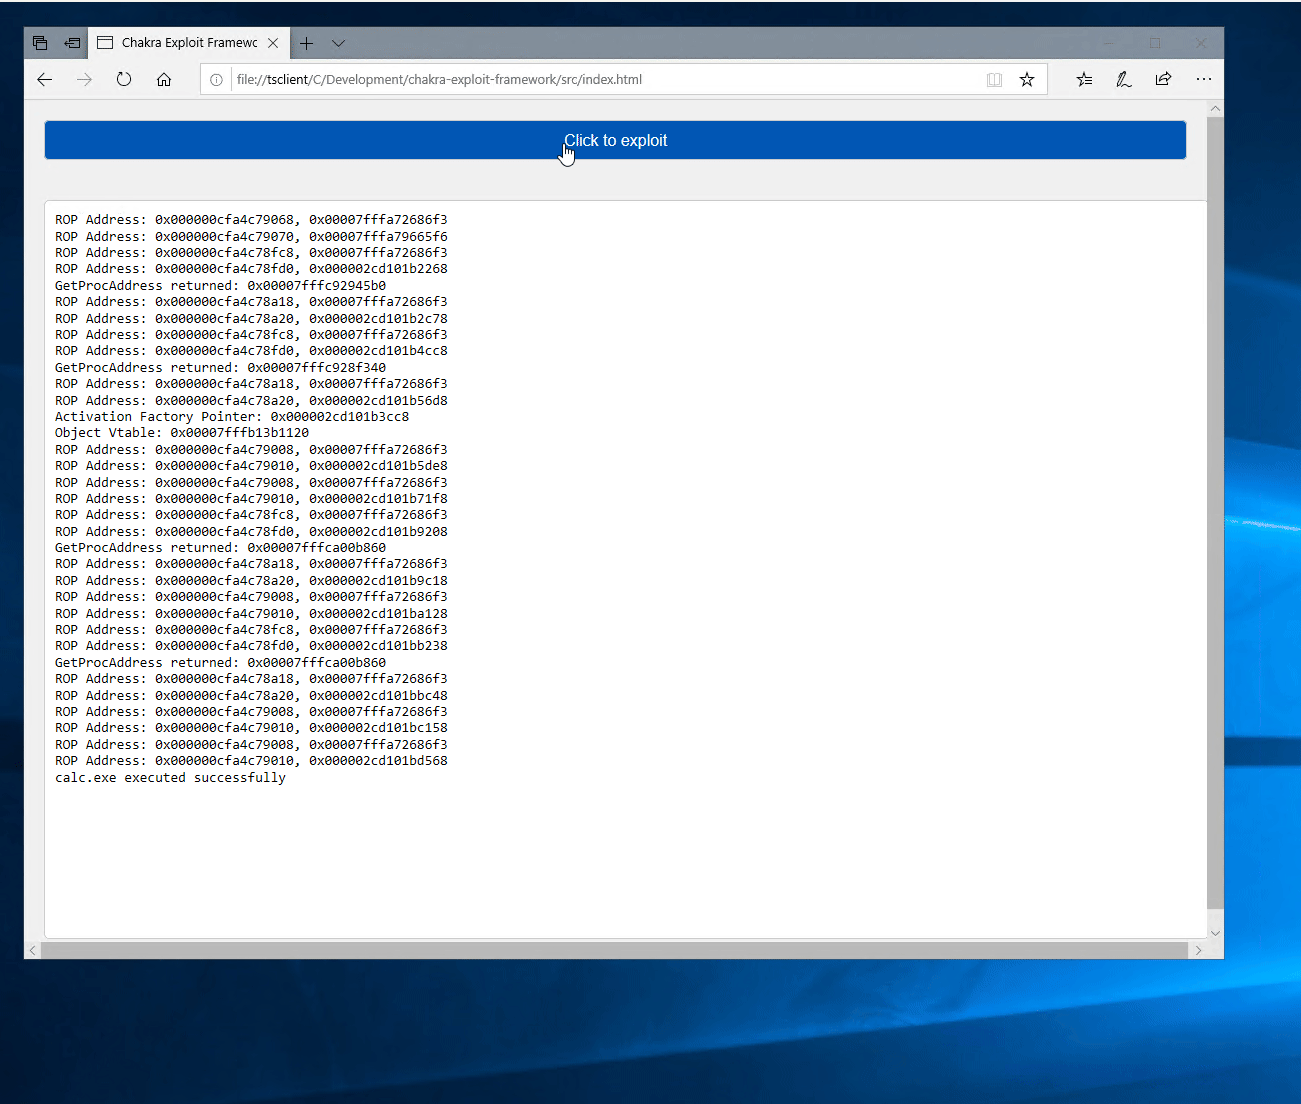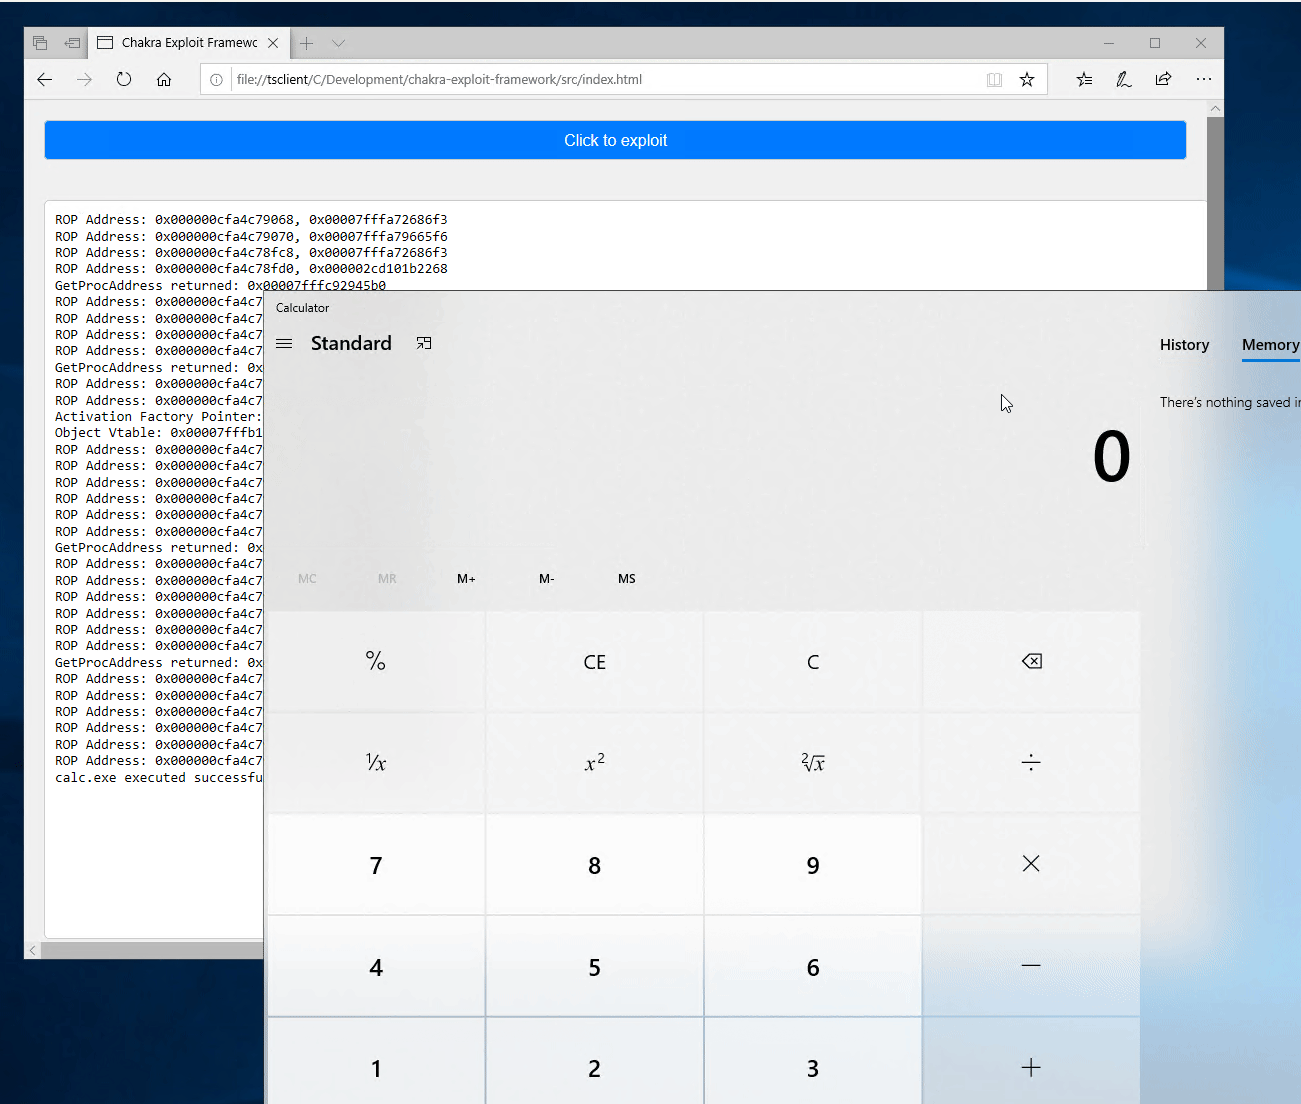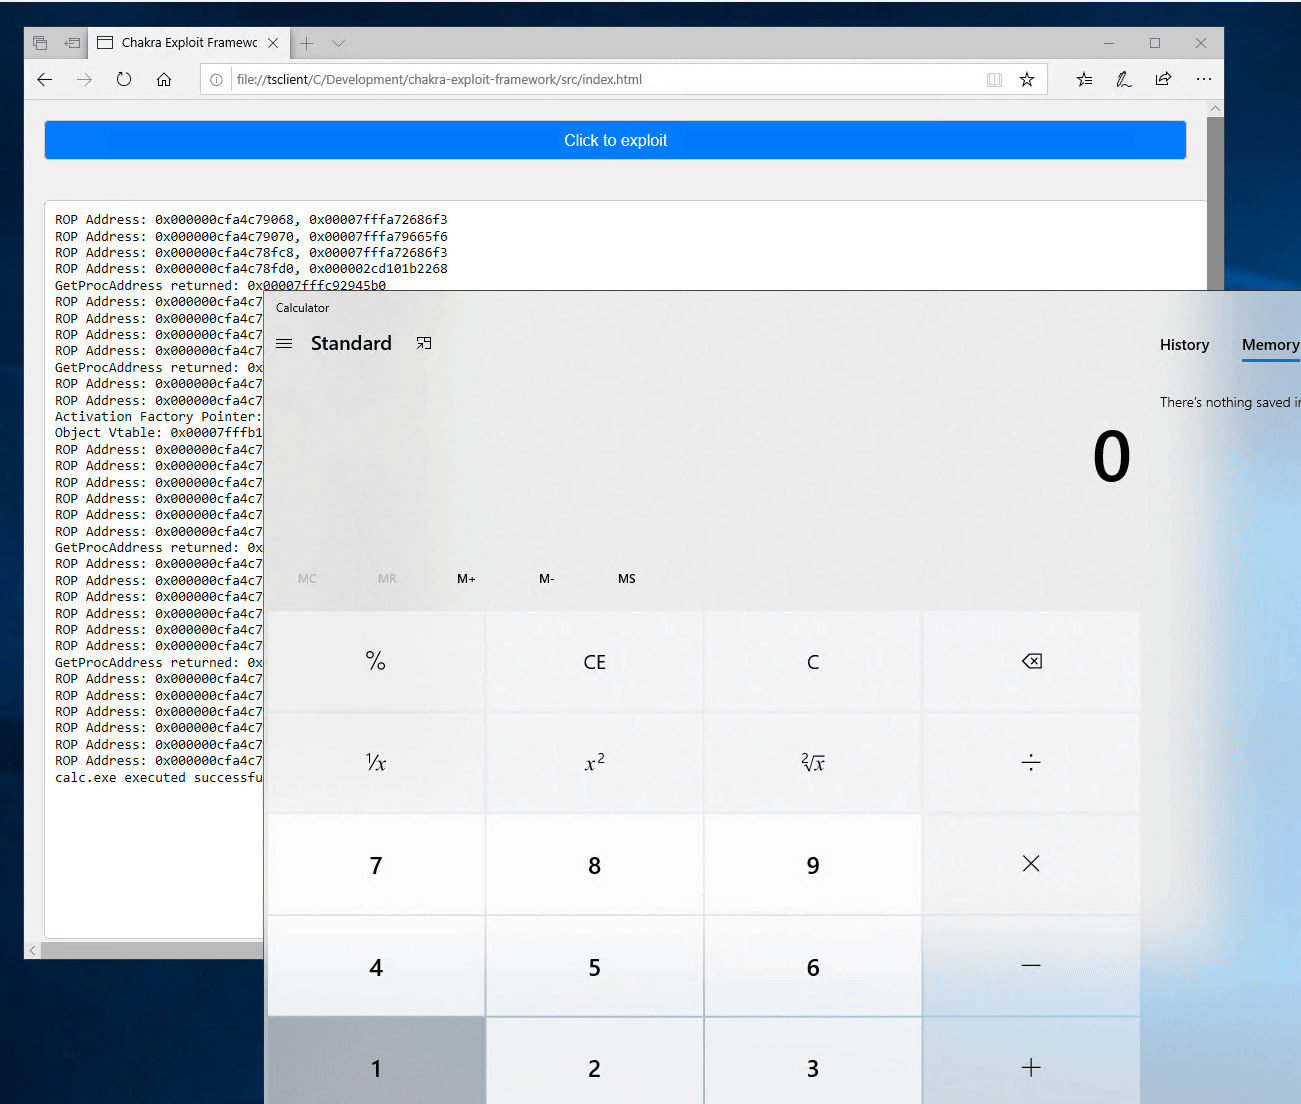
chakra-exploit-framework
 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
binary-exploitationeducationexploit-frameworks+6
1
ntdelta/chakra-exploit-frameworkBrowser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
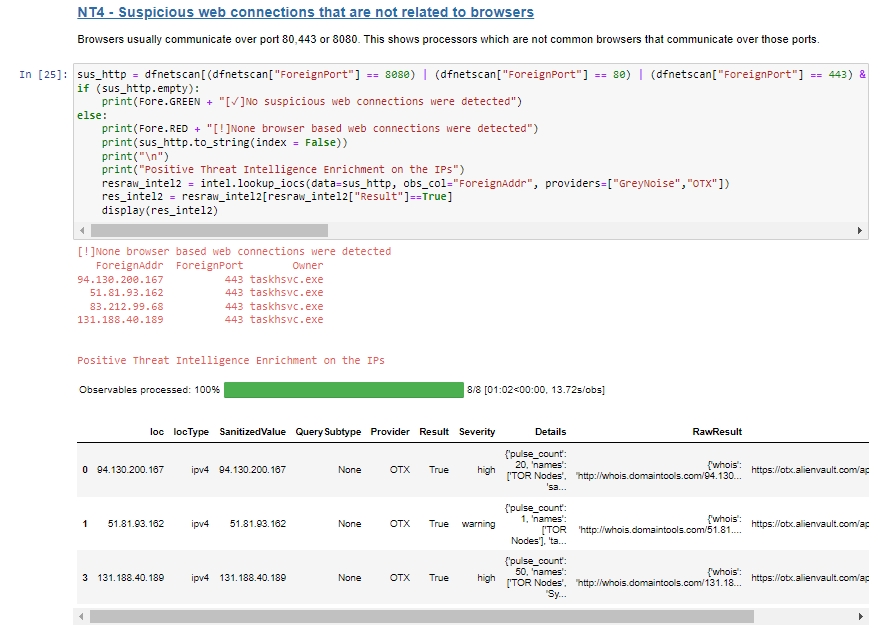 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
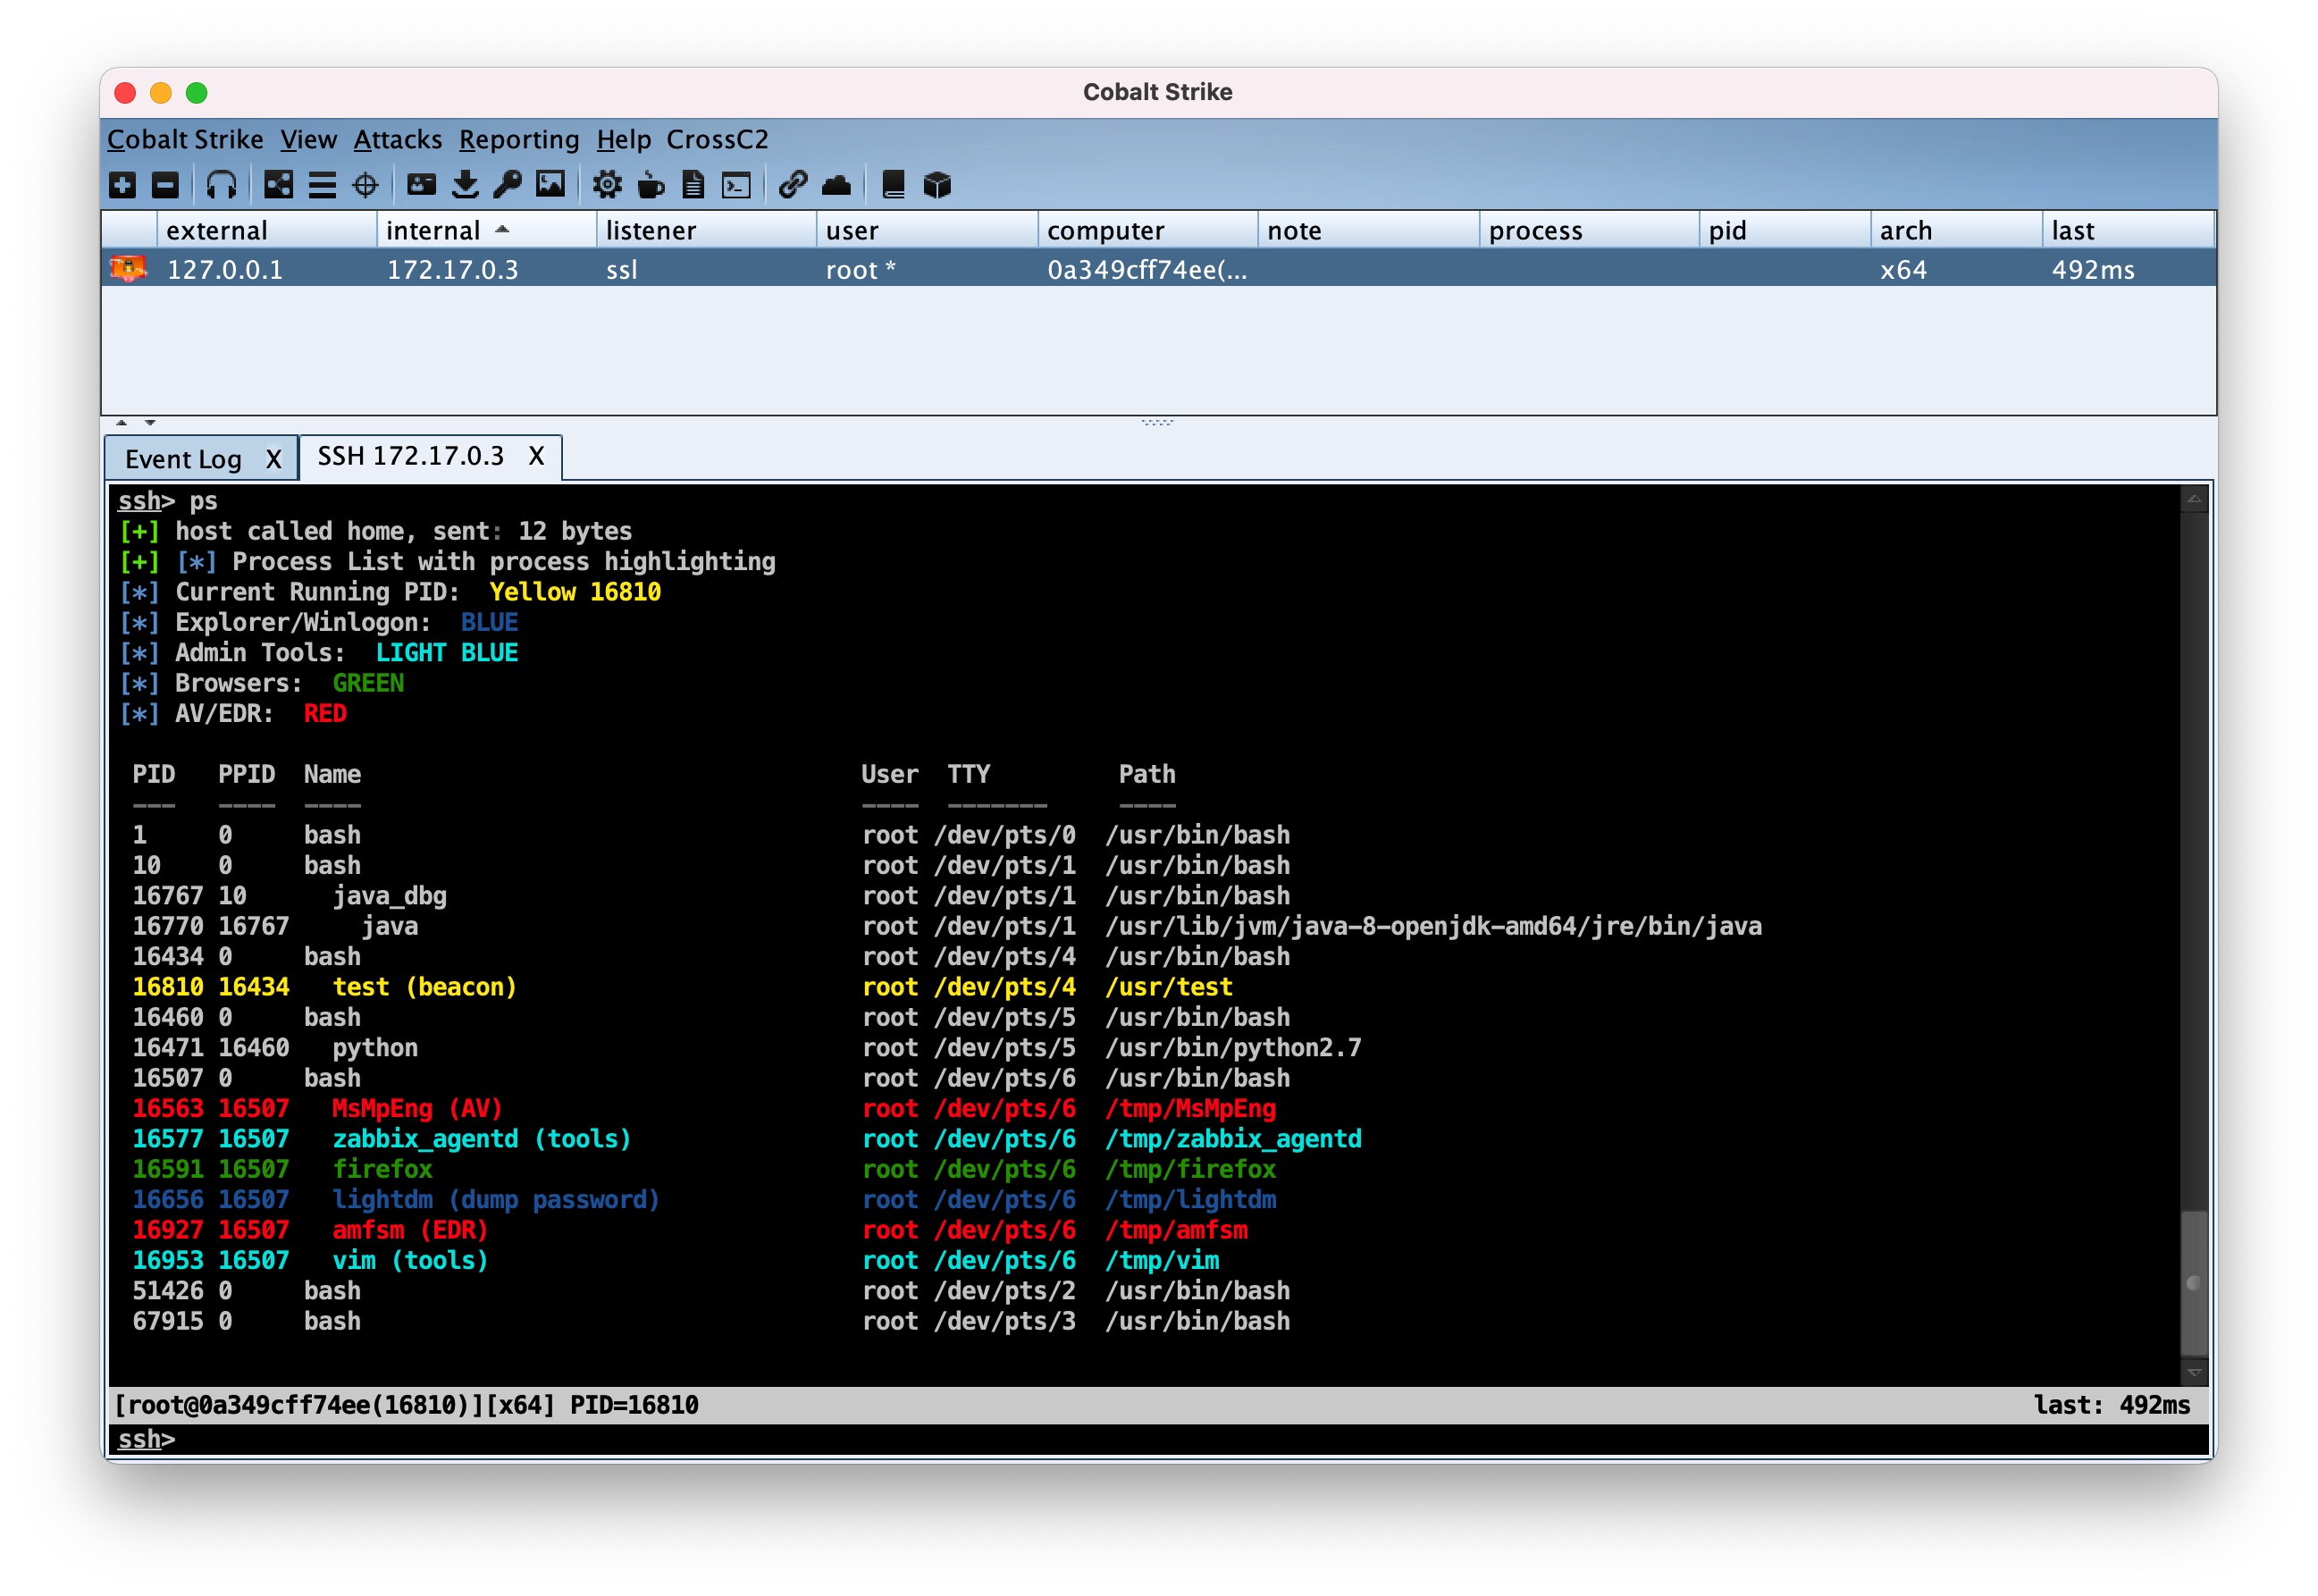 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 volatilityfoundation/volatility
An advanced memory forensics framework
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
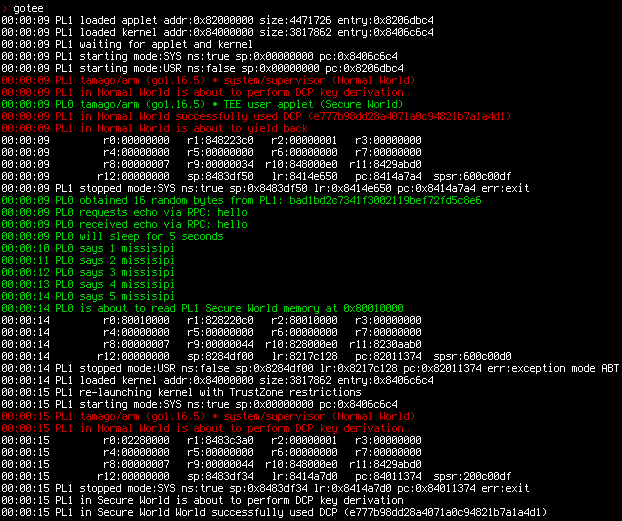 usbarmory/gotee-example
GoTEE - example application
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

 feliam/cve-2014-4481
Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
 kudaes/shelter
ROP-based sleep obfuscation to evade memory scanners
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…