
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
371 results
PPLBlade preview

PPLBlade

GitHubtastypepperoni/pplblade

Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
data-exfiltrationexploitationmemory-forensics+2
598
3 years ago
cve-2023-32784 preview

cve-2023-32784

GitHubmister-turtle/cve-2023-32784

Extracts KeePass master passwords from memory dumps of unlocked databases, outputting potential characters by position, a passphrase, and a…
digital-forensicsexploitationforensics+3
42 years ago
Pixel_GPU_Exploit preview

Pixel_GPU_Exploit

GitHub0x36/pixel_gpu_exploit

Android 14 kernel exploit for Pixel7/8 Pro
android-securitybinary-exploitationeducation+4
5622 years ago
CVE-2021-45067 preview

CVE-2021-45067

GitHubhacksysteam/cve-2021-45067

Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
binary-exploitationdata-exfiltrationexploitation+3
233 years ago
ATMMalScan preview

ATMMalScan

GitHubfboldewin/atmmalscan

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…

digital-forensicsdisk-forensicsincident-response+2
575 years ago
CVE-2024-1065 preview

CVE-2024-1065

GitHubkuzeyardabulut/cve-2024-1065

Proof-of-concept exploit for CVE-2024-1065, demonstrating page cache exploitation via a use-after-free in the ARM Mali GPU kernel driver to achieve…
binary-exploitationexploitationmemory-forensics+4
53 months ago
chakra-exploit-framework preview

chakra-exploit-framework

GitHubntdelta/chakra-exploit-framework

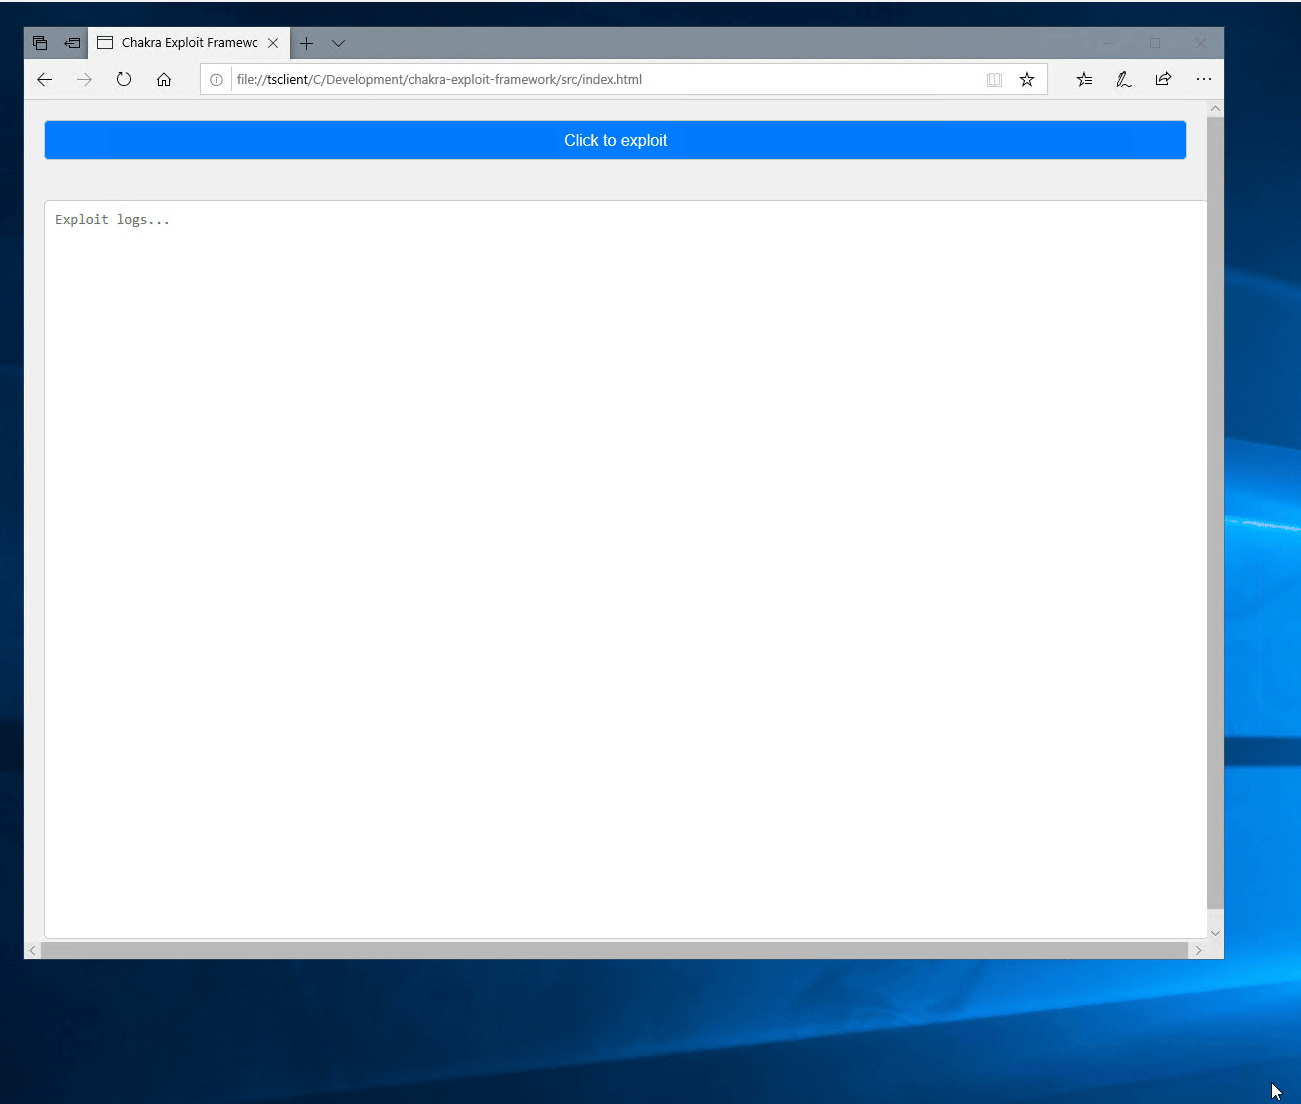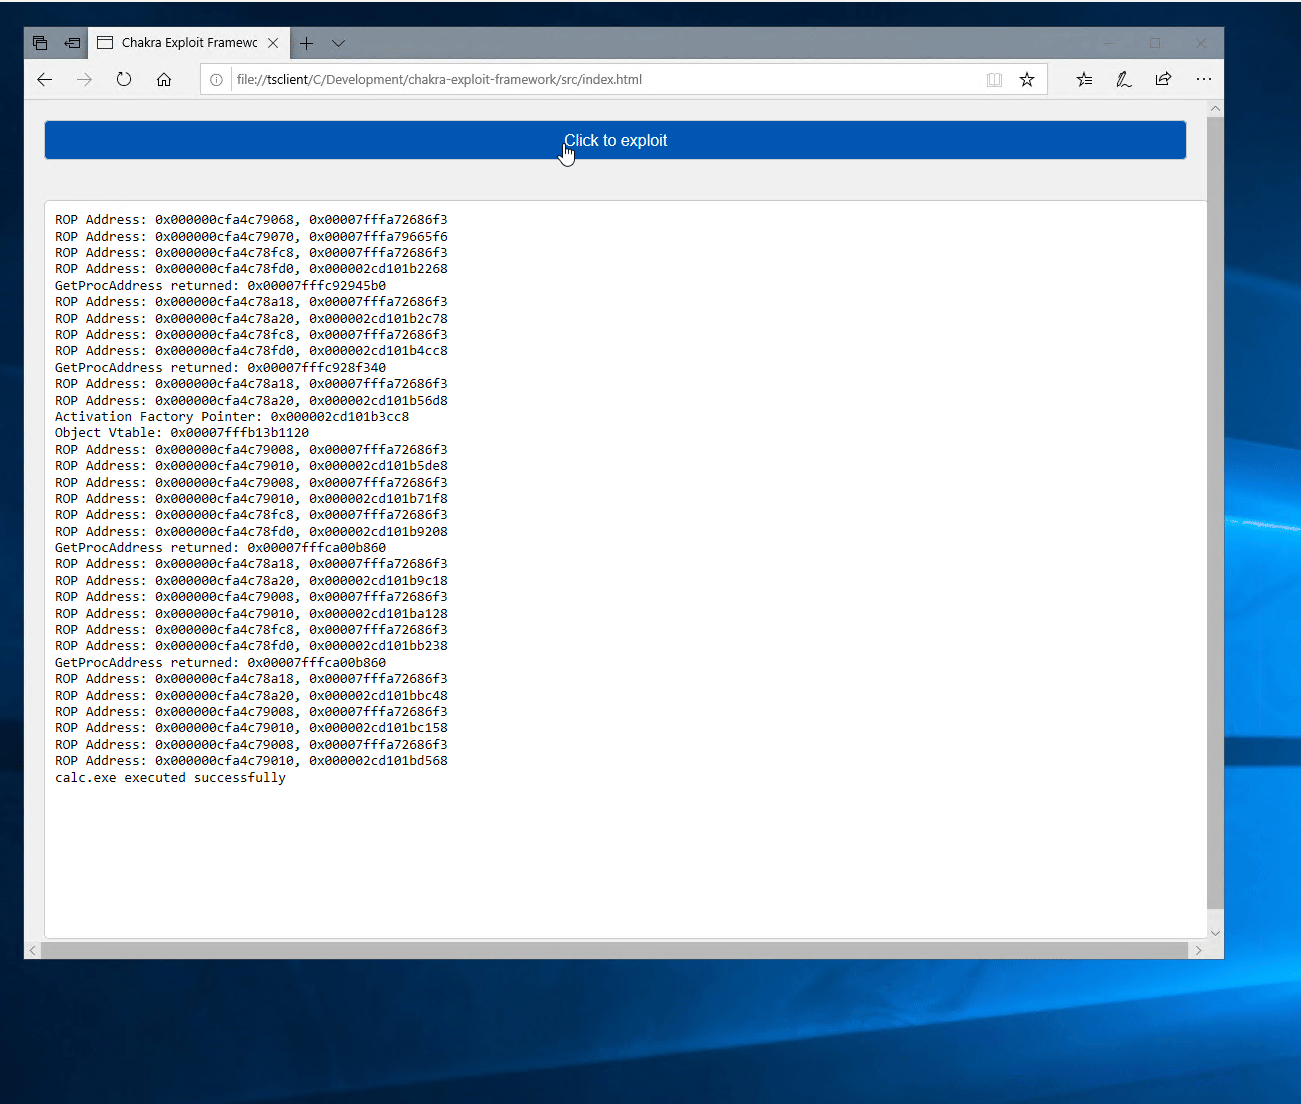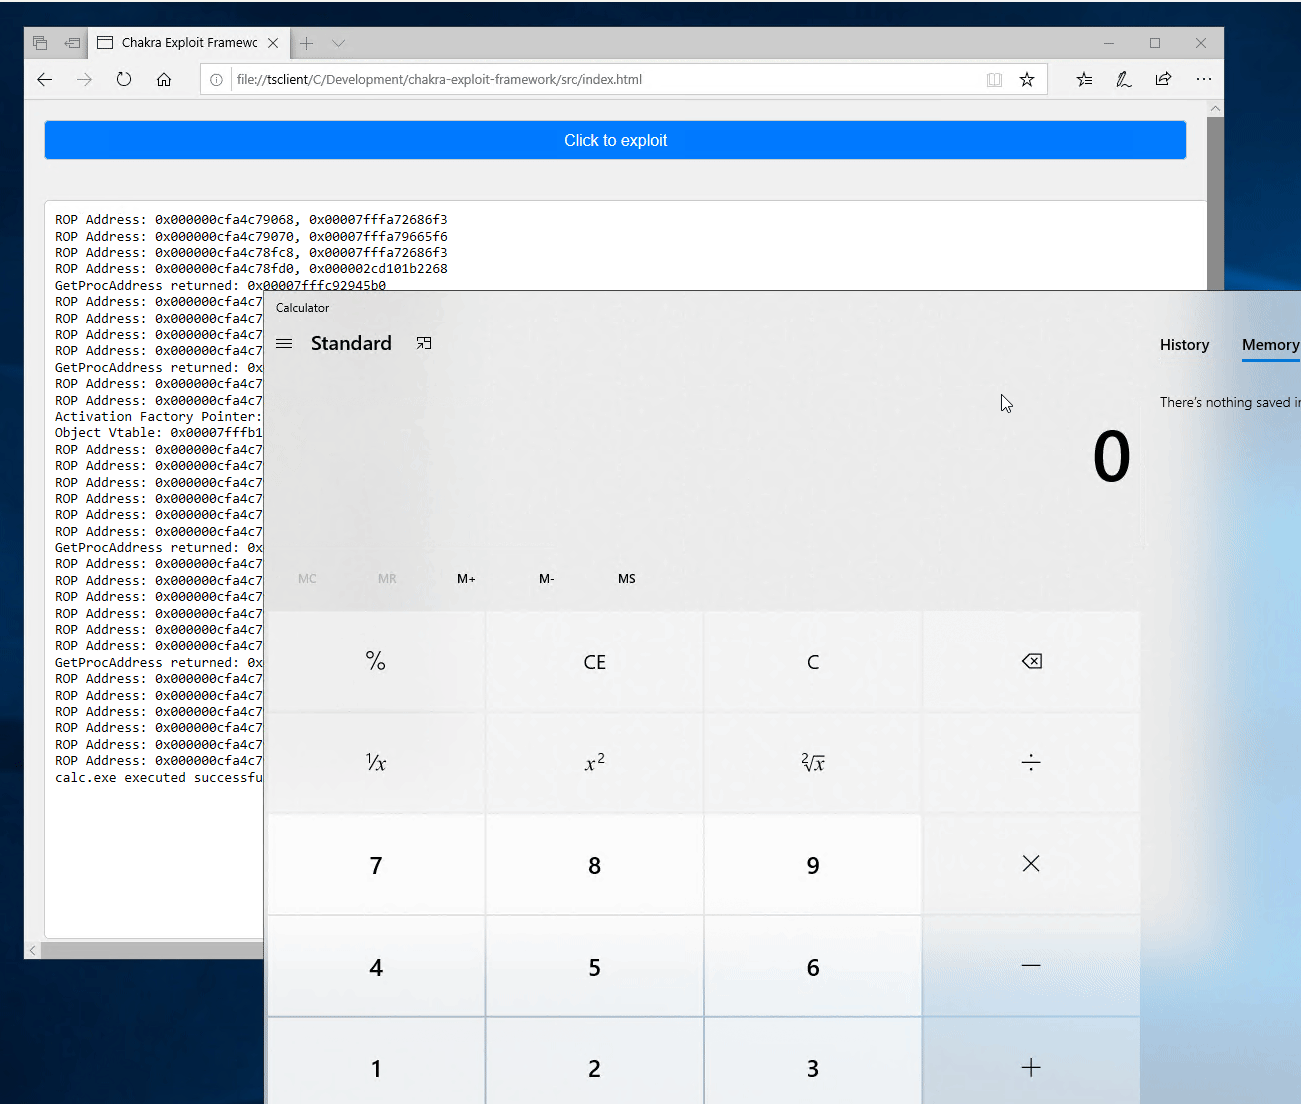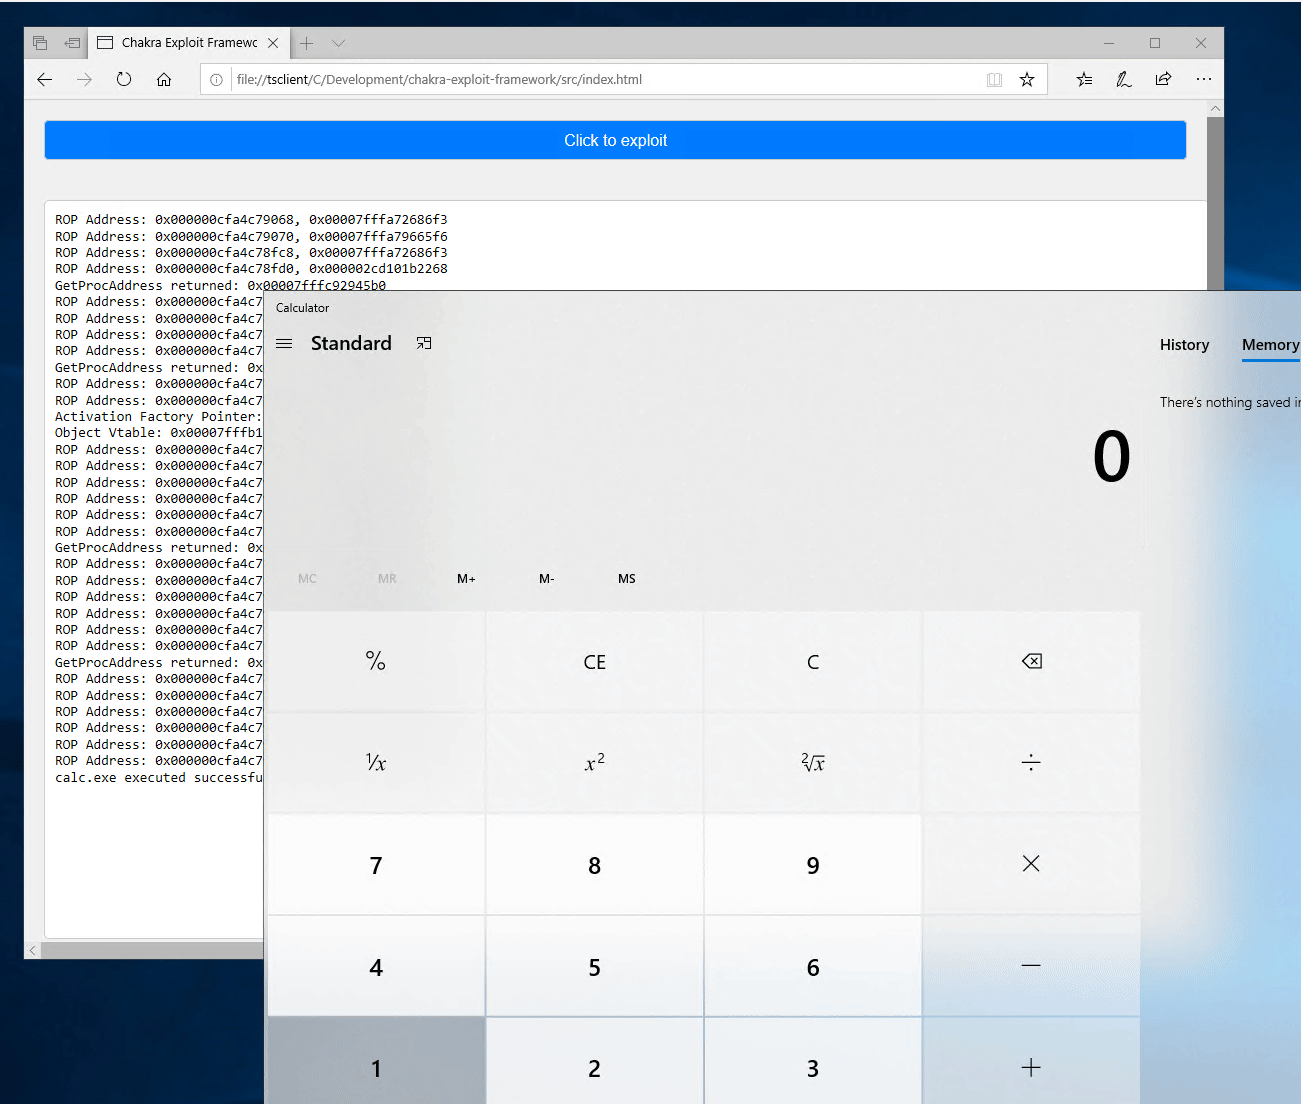
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
binary-exploitationeducationexploit-frameworks+6
11 year ago
CVE-2025-24201-WebKit-Vulnerability-Detector-PoC- preview

CVE-2025-24201-WebKit-Vulnerability-Detector-PoC-

GitHubthe-maxu/cve-2025-24201-webkit-vulnerability-detector-poc-

CVE-2025-24201 WebKit Vulnerability Detector (PoC)
exploitationmemory-forensicspenetration-testing+2
61 year ago
CVE-2025-62821 preview

CVE-2025-62821

GitHubhyunjungg/cve-2025-62821

Microsoft HEIF Extension (msheif_store.dll) OOB-read
binary-analysisexploitationfuzzing+3
11 months ago
-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis- preview

-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis-

GitHubkaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-

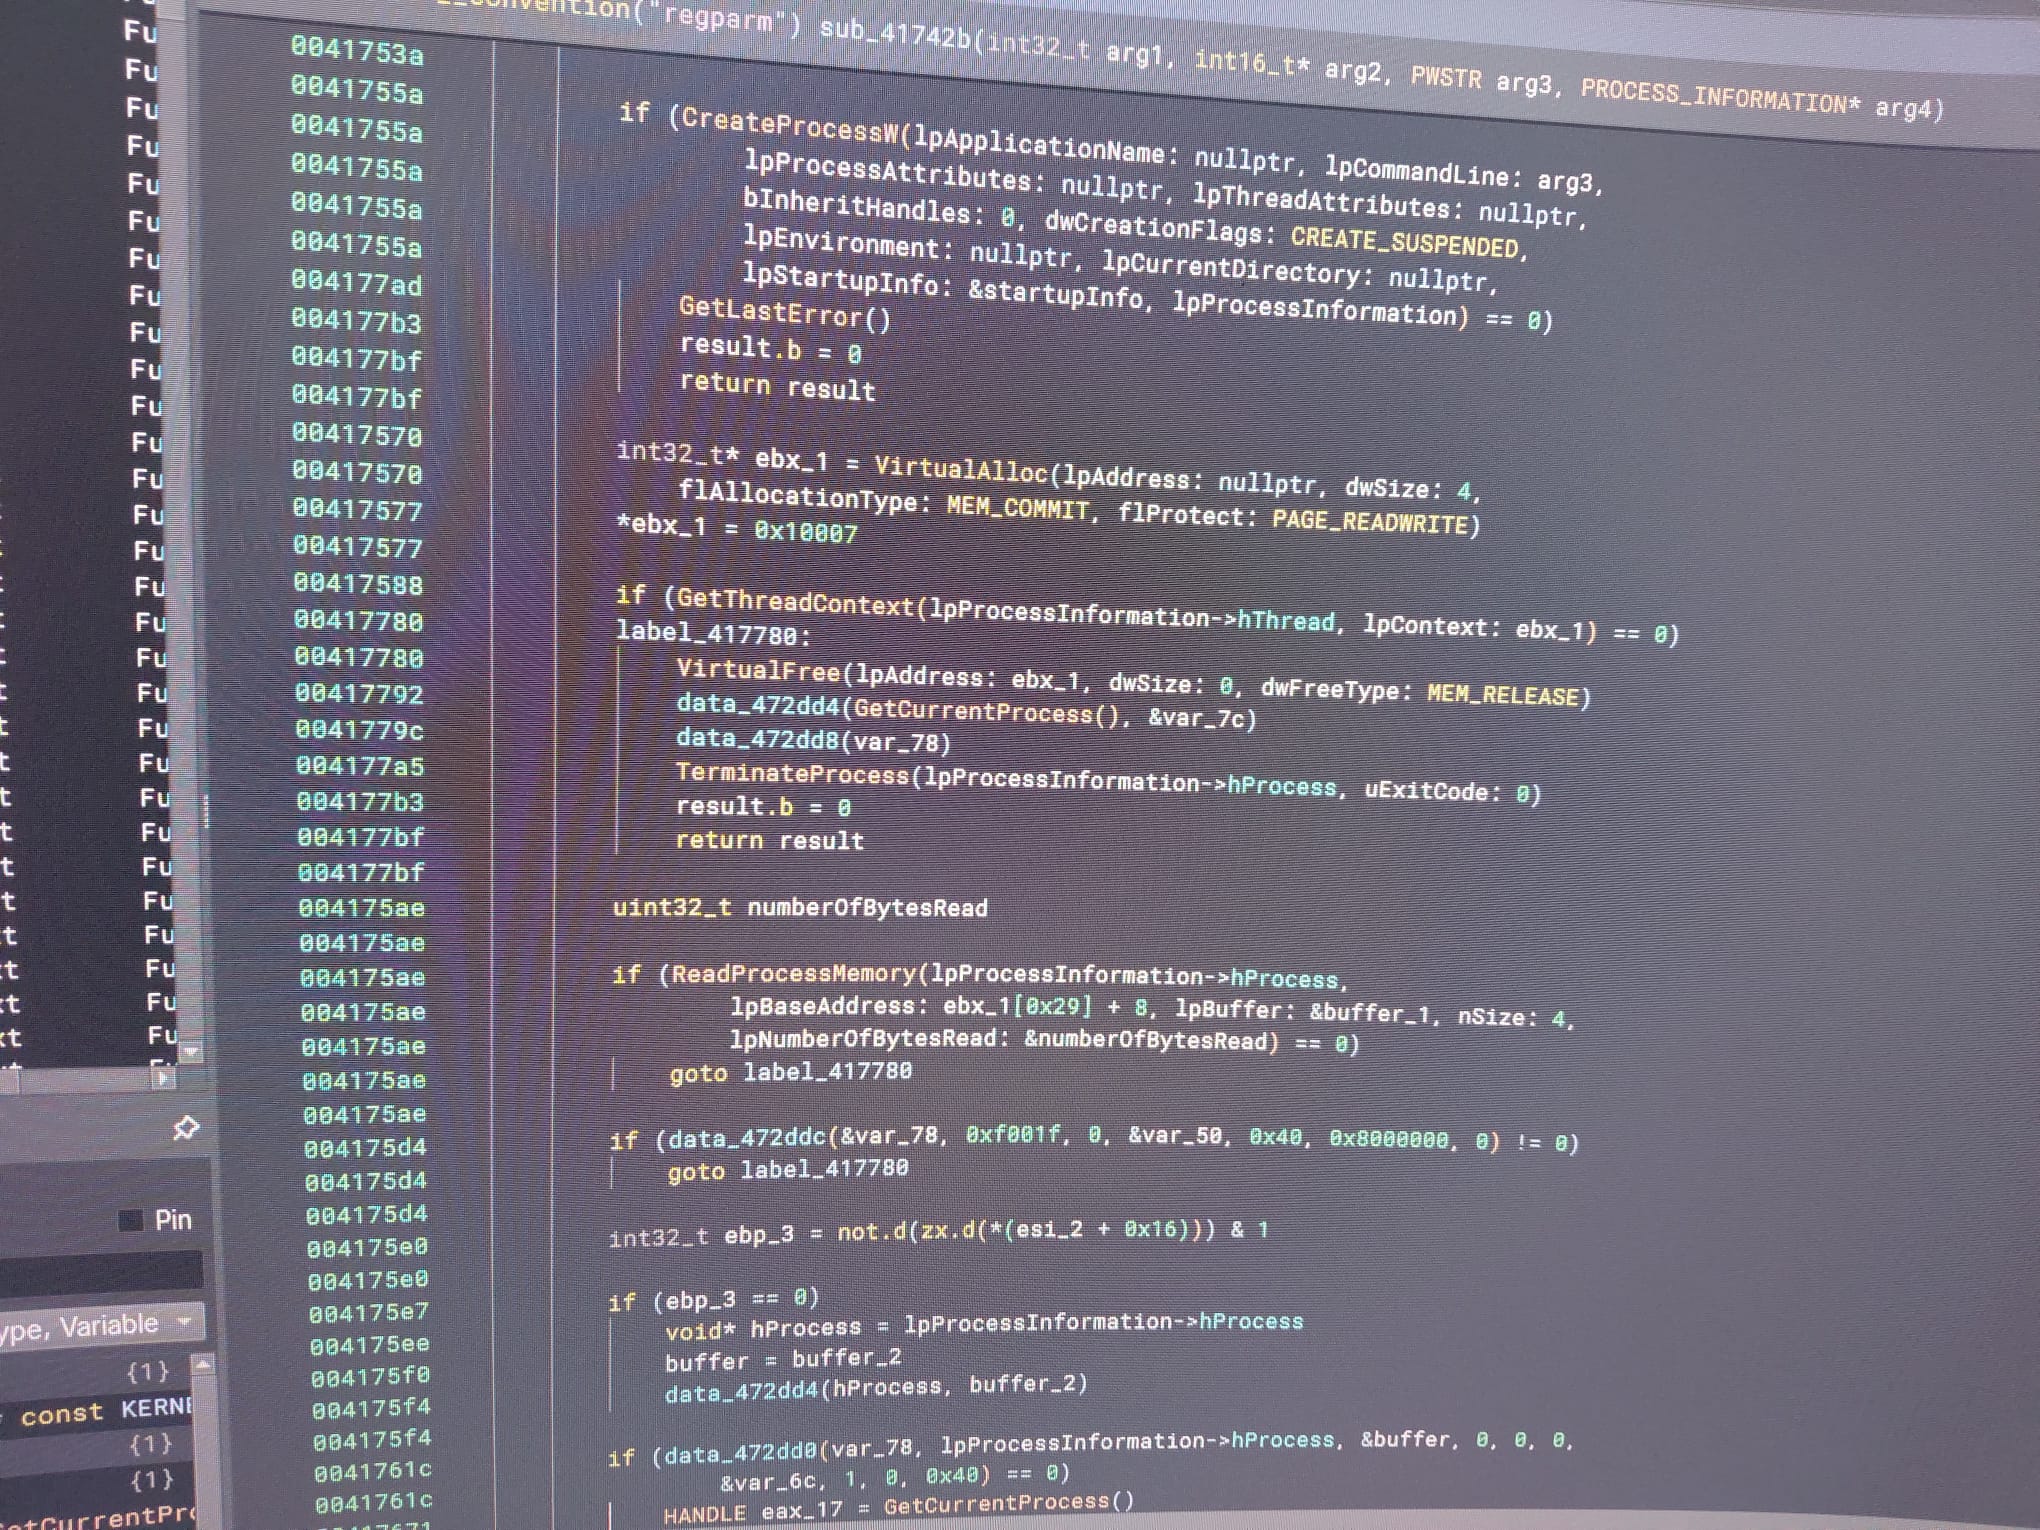
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
api-securitybinary-analysisdynamic-analysis-sandboxing+8
22 months ago
CVE-2021-22555-Poc preview

CVE-2021-22555-Poc

GitHubspydomain/cve-2021-22555-poc

Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
binary-exploitationexploitationinformation-gathering+3
17 months ago
copyfail-dfir preview

copyfail-dfir

GitHubledlight33/copyfail-dfir

Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
digital-forensicseducationincident-response+2
14 months ago
full-poc-CVE-2025_21298 preview

full-poc-CVE-2025_21298

GitHubfy-poc/full-poc-cve-2025_21298

Complete analysis of CVE-2025-21298, a double free vulnerability related to ole32 library in windows.

binary-exploitationeducationexploitation+3
111 months ago
Driver-PiDqSerializationWrite-Example preview

Driver-PiDqSerializationWrite-Example

GitHubgmh5225/driver-pidqserializationwrite-example

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
binary-analysisdebuggersdynamic-analysis-sandboxing+5
23 years ago
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

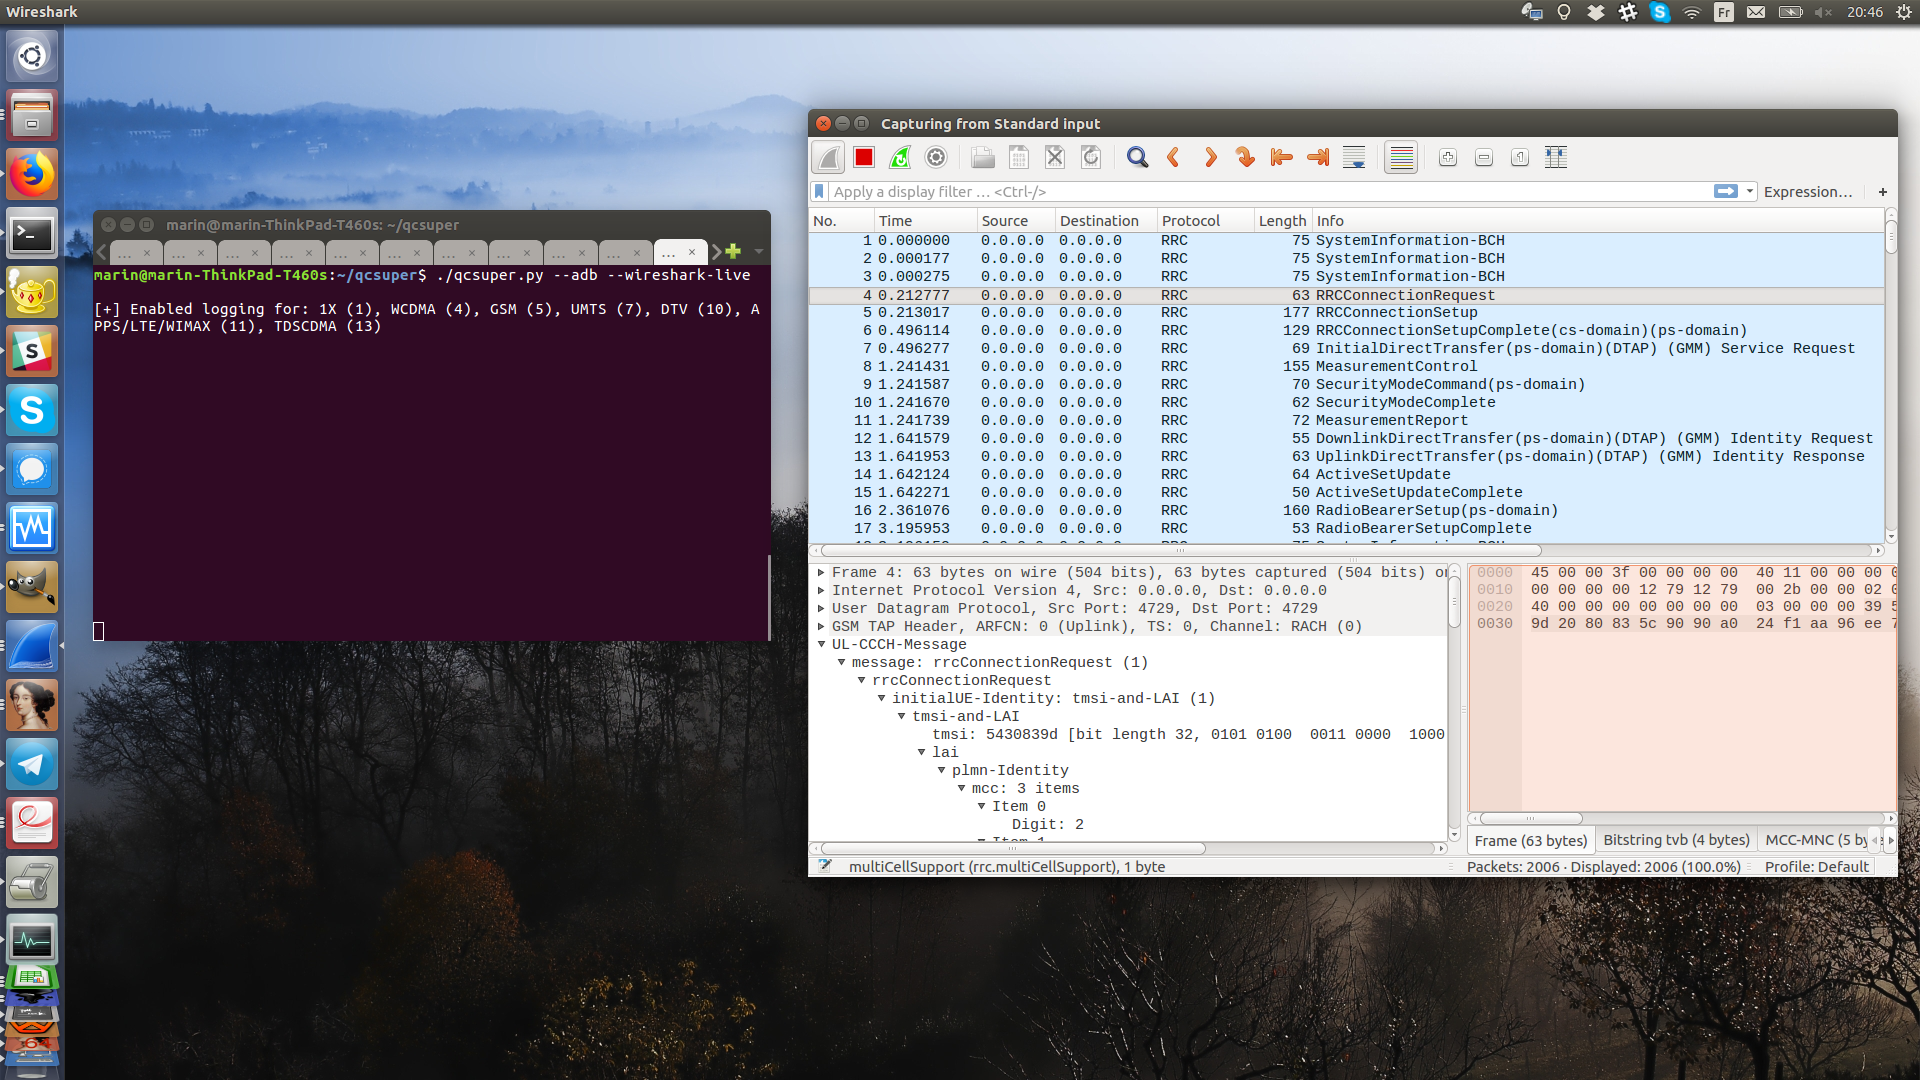
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.6k1 month ago
CVE-2025-29824 preview

CVE-2025-29824

GitHubencrypter15/cve-2025-29824

Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
binary-exploitationdebuggerseducation+7
301 year ago
cormem-read-poc preview

cormem-read-poc

GitHub4d4j/cormem-read-poc

This tool demonstrates CVE-2026-38194, a vulnerability in Teledyne Digital Imaging Sapera Memory Manager (v9.0.0.0 and below). The CORMEM.SYS kernel…
binary-exploitationeducationexploitation+3
92 months ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.

binary-analysisforensicsmalware-analysis+2
1.9k3 years ago
Previous1…567…21Next