Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
124 results
pwndbg preview

pwndbg

GitHubpwndbg/pwndbg

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

ai-assisted-reversingbinary-analysisbinary-exploitation+12
11.1k1 day ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.5k10 days ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k4 months ago
PowerShellArsenal preview

PowerShellArsenal

GitHubmattifestation/powershellarsenal

A PowerShell Module Dedicated to Reverse Engineering

binary-analysisdebuggersdynamic-analysis-sandboxing+6
9015 years ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
6091 month ago
ThreadStackSpoofer preview

ThreadStackSpoofer

GitHubmgeeky/threadstackspoofer

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…


exploit-frameworksmalware-analysismemory-forensics+4
1.3k4 years ago
sift preview

sift

GitHubteamdfir/sift

SIFT

cloud-securitydigital-forensicsdisk-forensics+3
5532 years ago
ir-rescue preview

ir-rescue

GitHubdiogo-fernan/ir-rescue

A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.

digital-forensicsdisk-forensicsforensics+6
4895 years ago
awesome-dfir-skills preview

awesome-dfir-skills

GitHubtsale/awesome-dfir-skills

A curated collection of DFIR skills and workflows for InfoSec practitioners.
curated-resourcesdigital-forensicseducation+7
3255 months ago
Shelter preview

Shelter

GitHubkudaes/shelter

ROP-based sleep obfuscation to evade memory scanners
exploit-frameworksmemory-forensicsred-teaming
3901 year ago
dismember preview

dismember

GitHubliamg/dismember

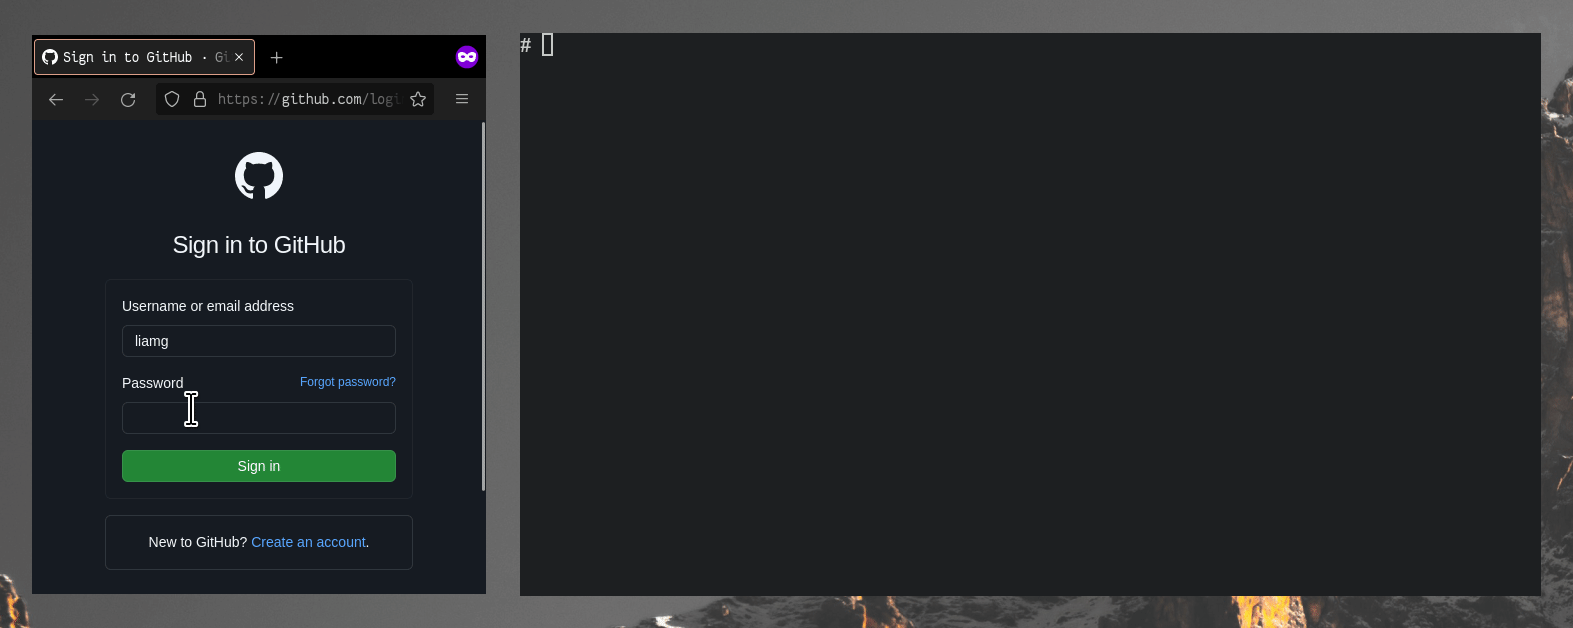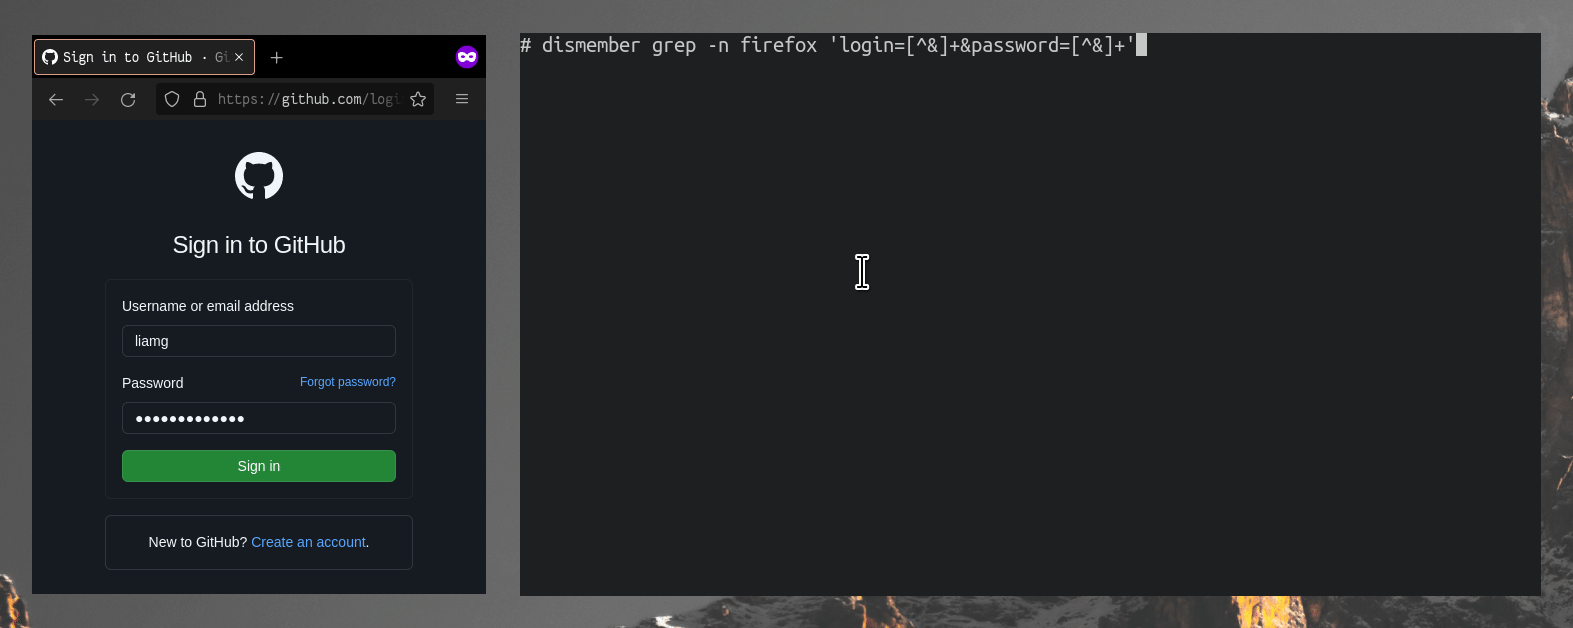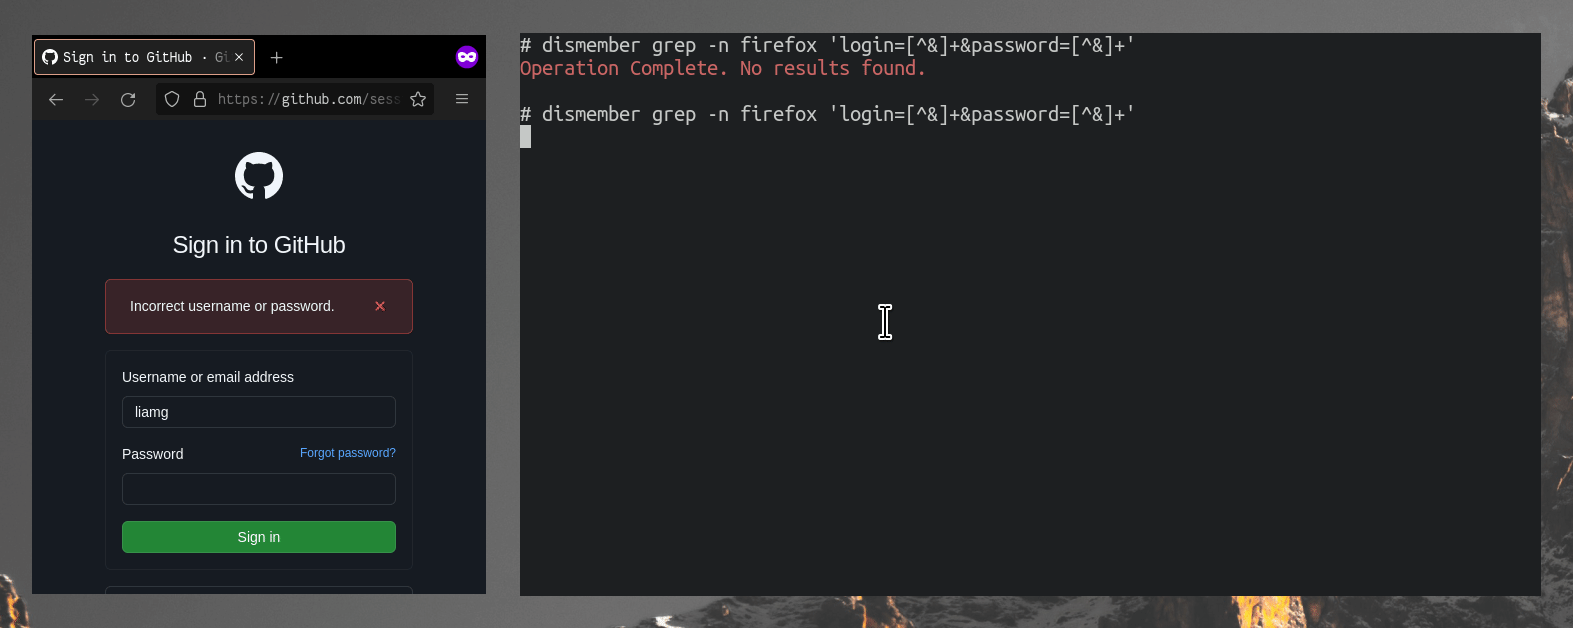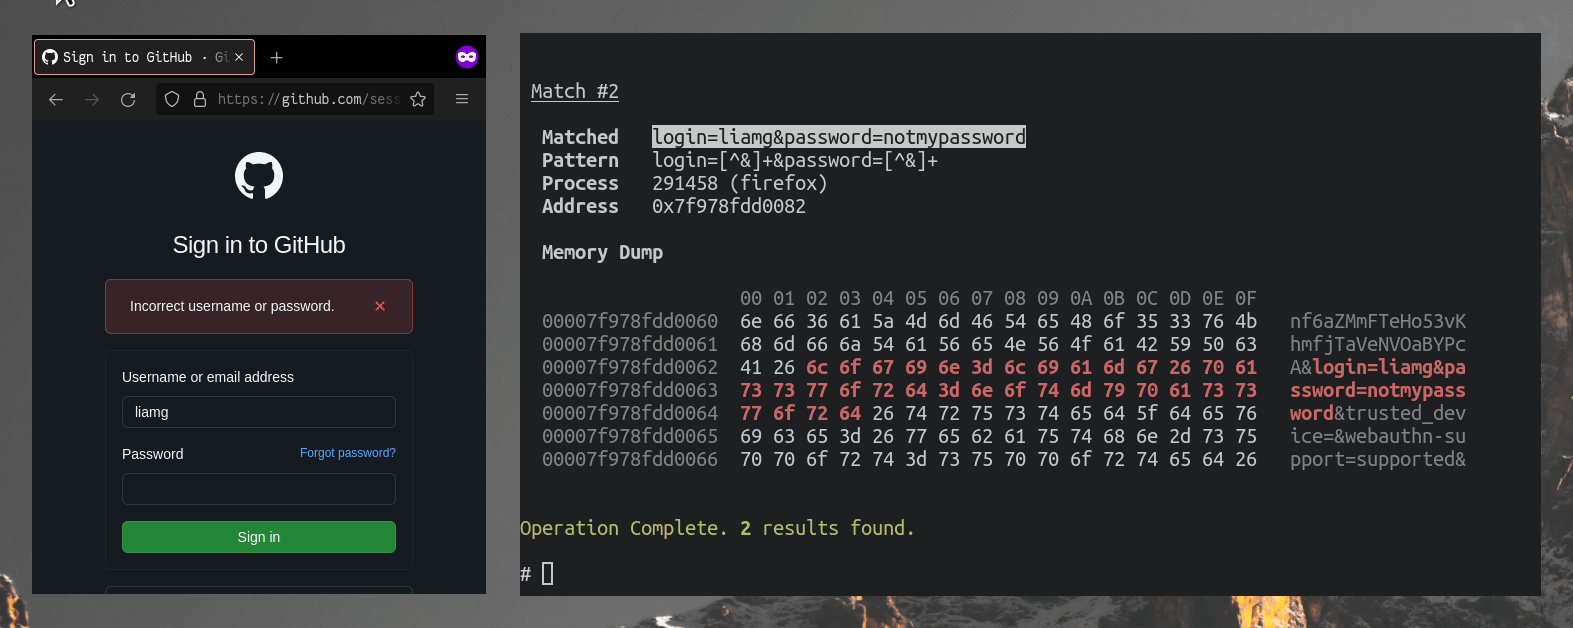
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
ctfforensicsinformation-gathering+2
6734 years ago
memoro preview

memoro

GitHubepfl-vlsc/memoro

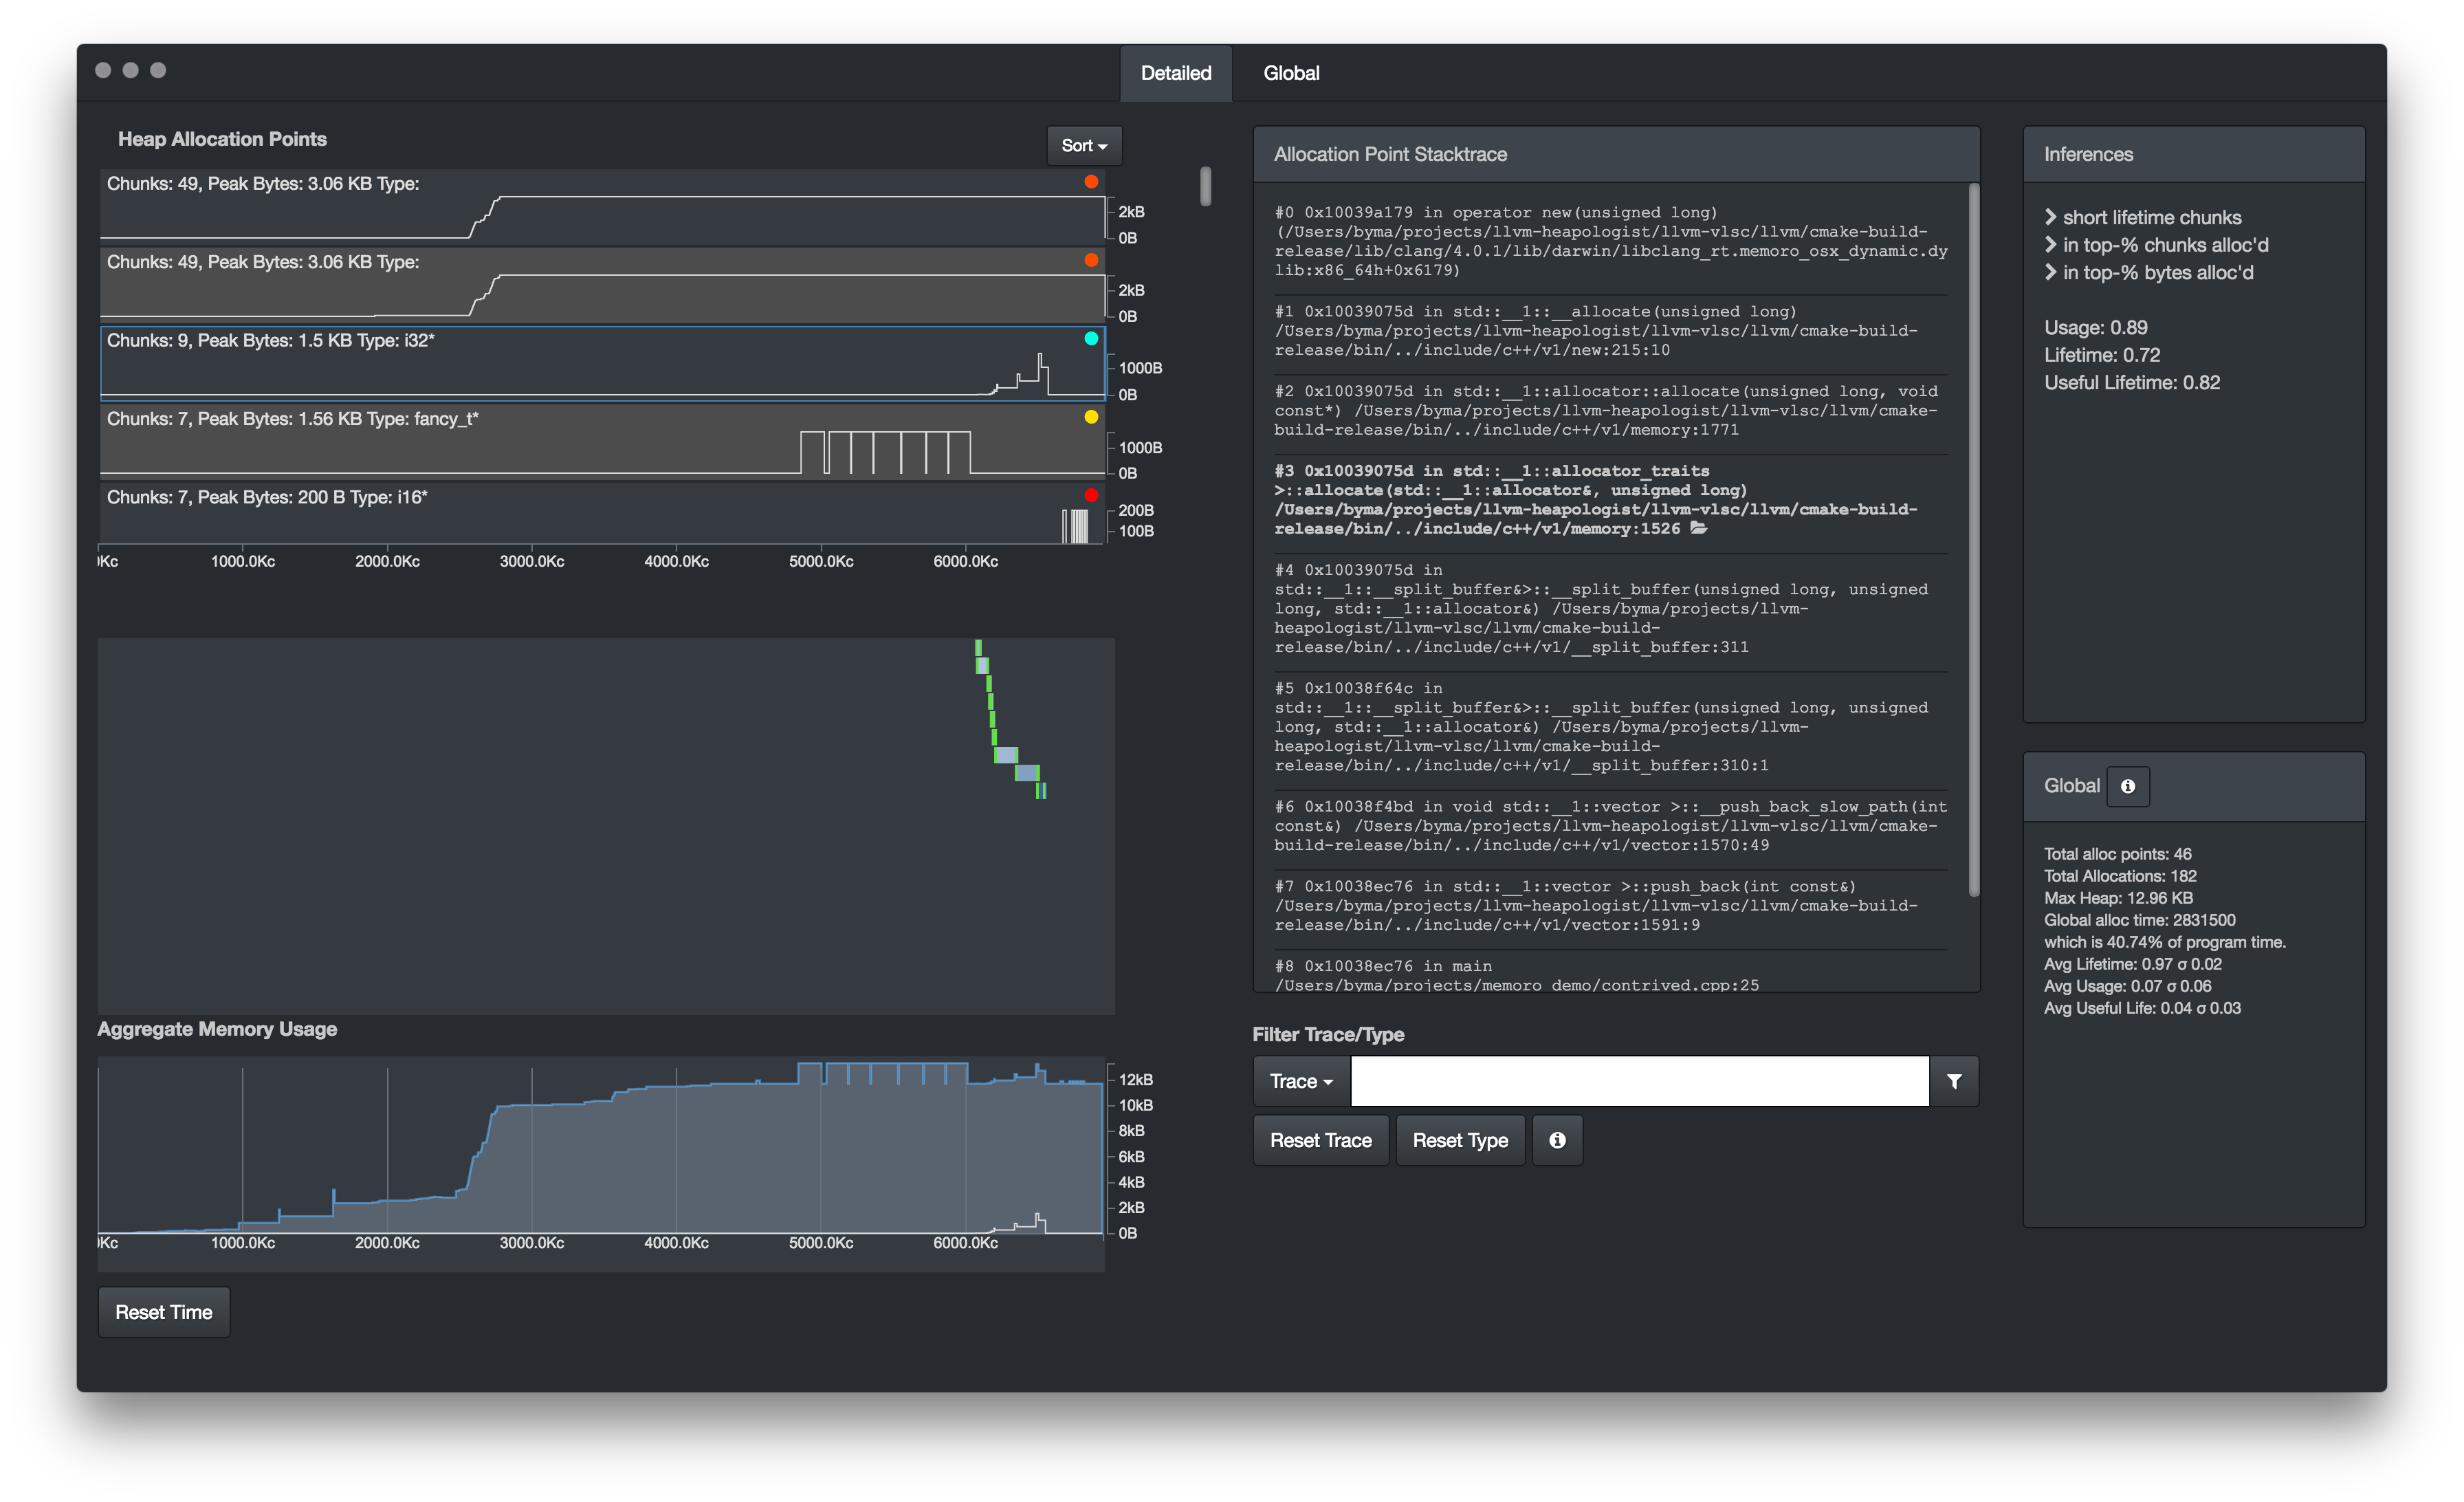
Memoro: A Detailed Heap Profiler
binary-analysisdebuggersdynamic-analysis-sandboxing+1
1855 years ago
DetectWindowsCopyOnWriteForAPI preview

DetectWindowsCopyOnWriteForAPI

GitHubnccgroup/detectwindowscopyonwriteforapi

Enumerate various traits from Windows processes as an aid to threat hunting
anomaly-detectiondefensive-toolsforensics+3
1984 years ago
shed preview

shed

GitHubenkomio/shed

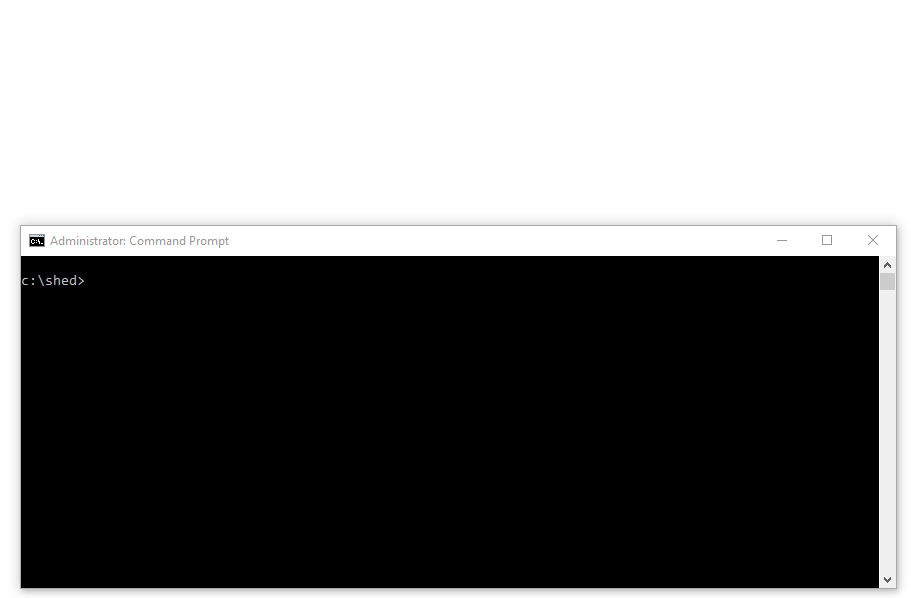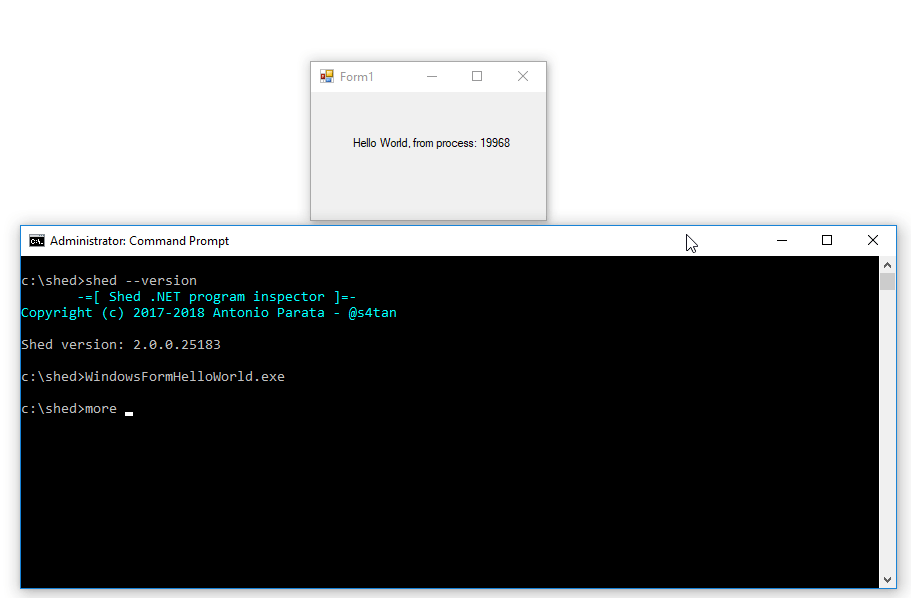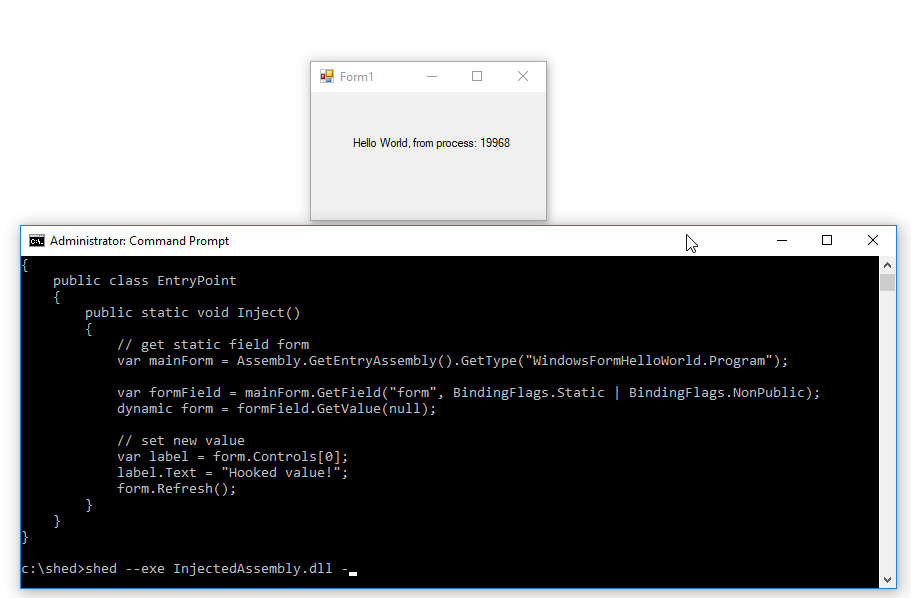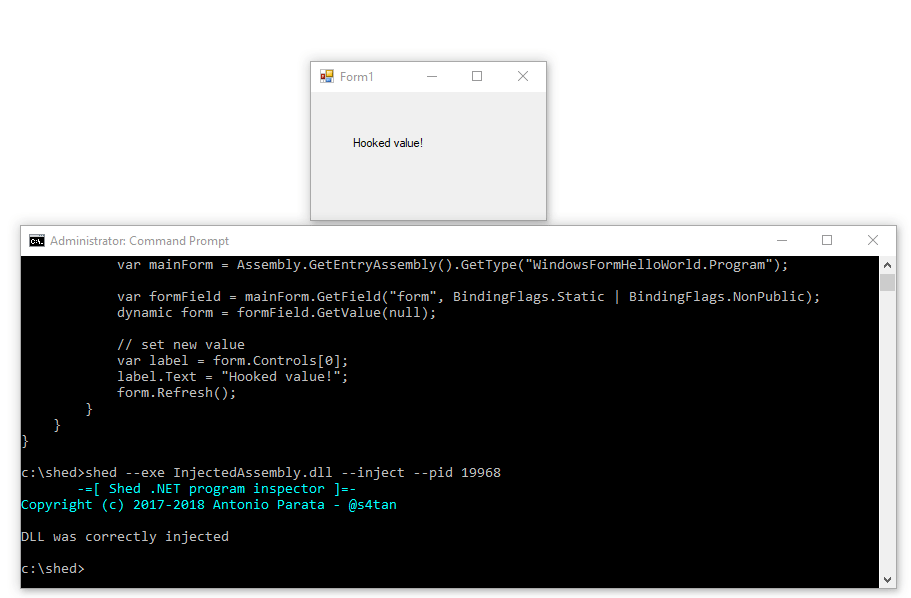
.NET runtime inspector

dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
2757 years ago
Platbox preview

Platbox

GitHubioactive/platbox

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
binary-analysisfirmware-analysisfuzzing+3
2241 year ago
CVE-2023-0179-PoC preview

CVE-2023-0179-PoC

GitHubh4k6/cve-2023-0179-poc

针对(CVE-2023-0179)漏洞利用 该漏洞被分配为CVE-2023-0179,影响了从5.5到6.2-rc3的所有Linux版本,该漏洞在6.1.6上被测试。 漏洞的细节和文章可以在os-security上找到。
binary-exploitationexploitationmemory-forensics+2
1993 years ago
CVE-2023-28252 preview

CVE-2023-28252

GitHubfortra/cve-2023-28252

Technical analysis and proof-of-concept exploit for CVE-2023-28252, a Windows Common Log File System (CLFS) driver privilege escalation vulnerability…
binary-exploitationdebuggersexploitation+4
1843 years ago
kdmp-parser preview

kdmp-parser

GitHub0vercl0k/kdmp-parser

A Windows kernel dump C++ parser library with Python 3 bindings.

digital-forensicsforensicsincident-response+1
2171 year ago
Previous1234567Next