Remote-Desktop-Caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.

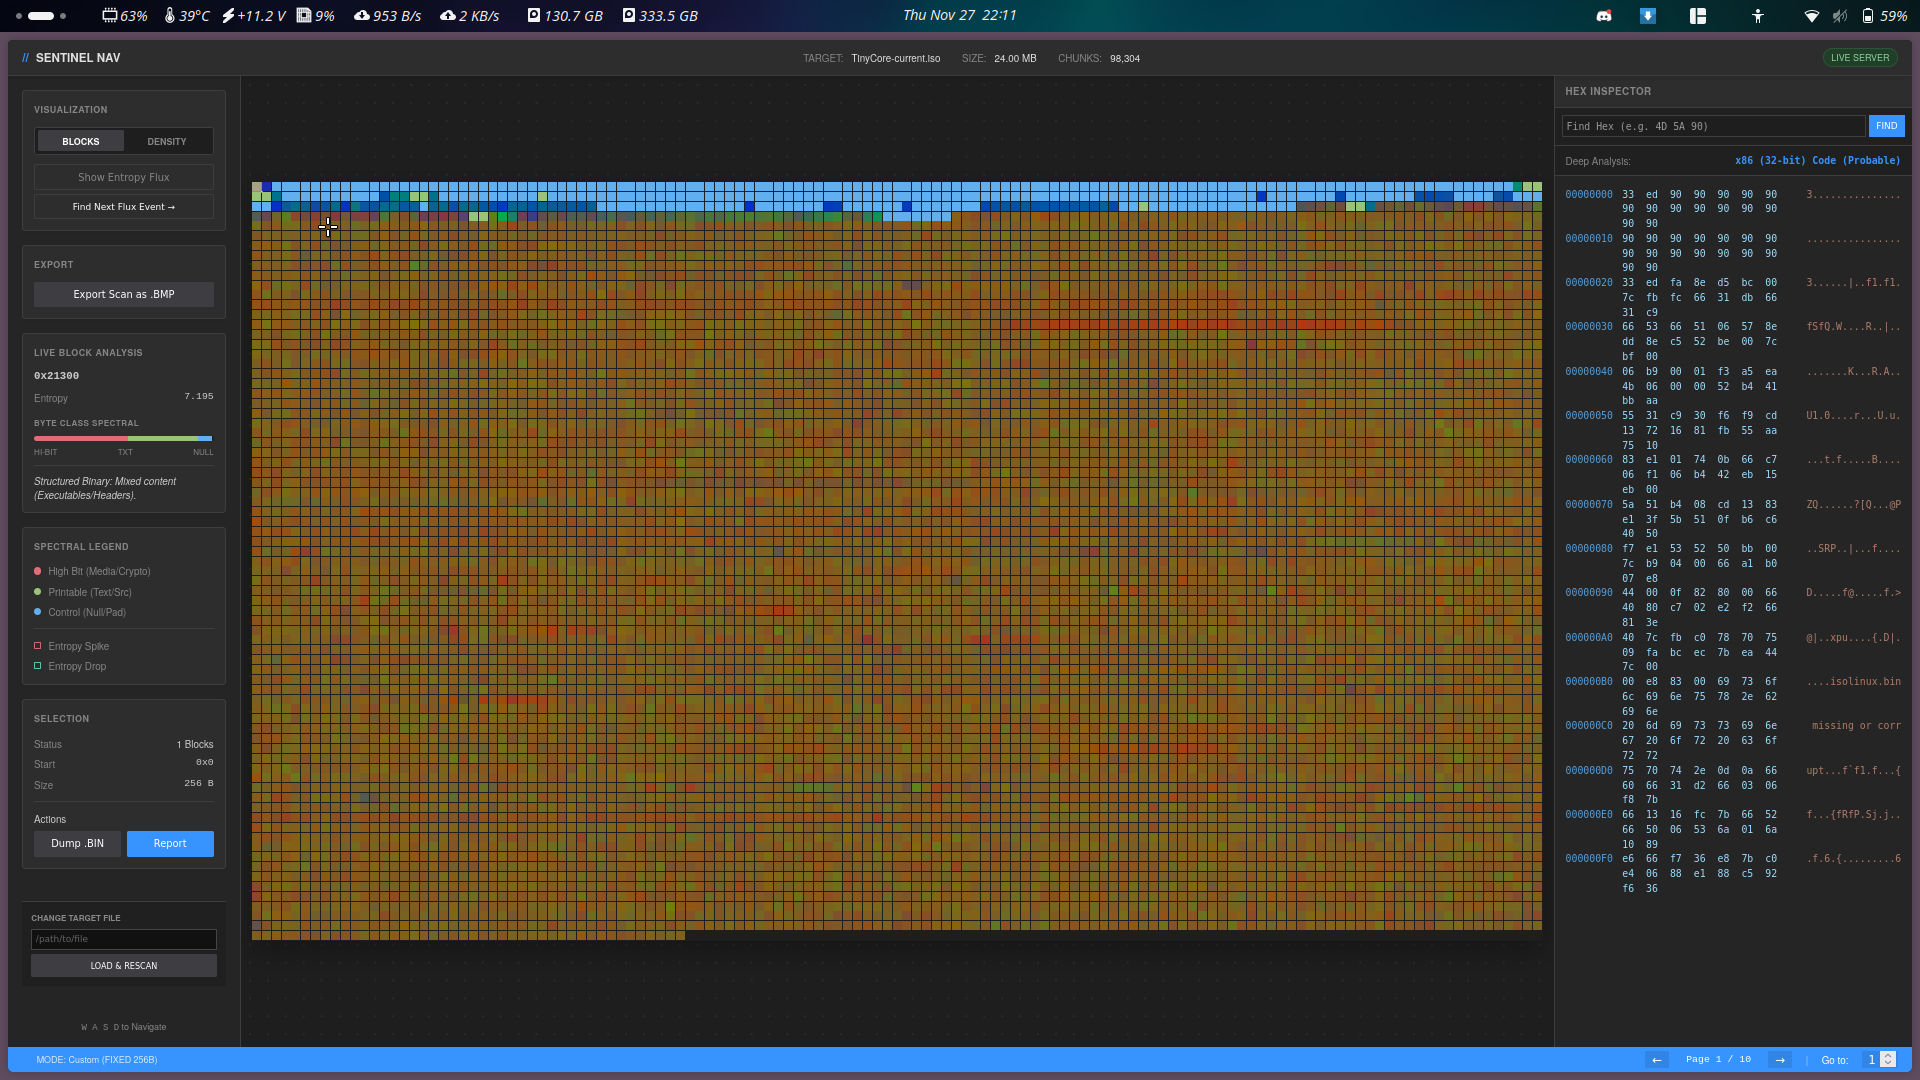
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

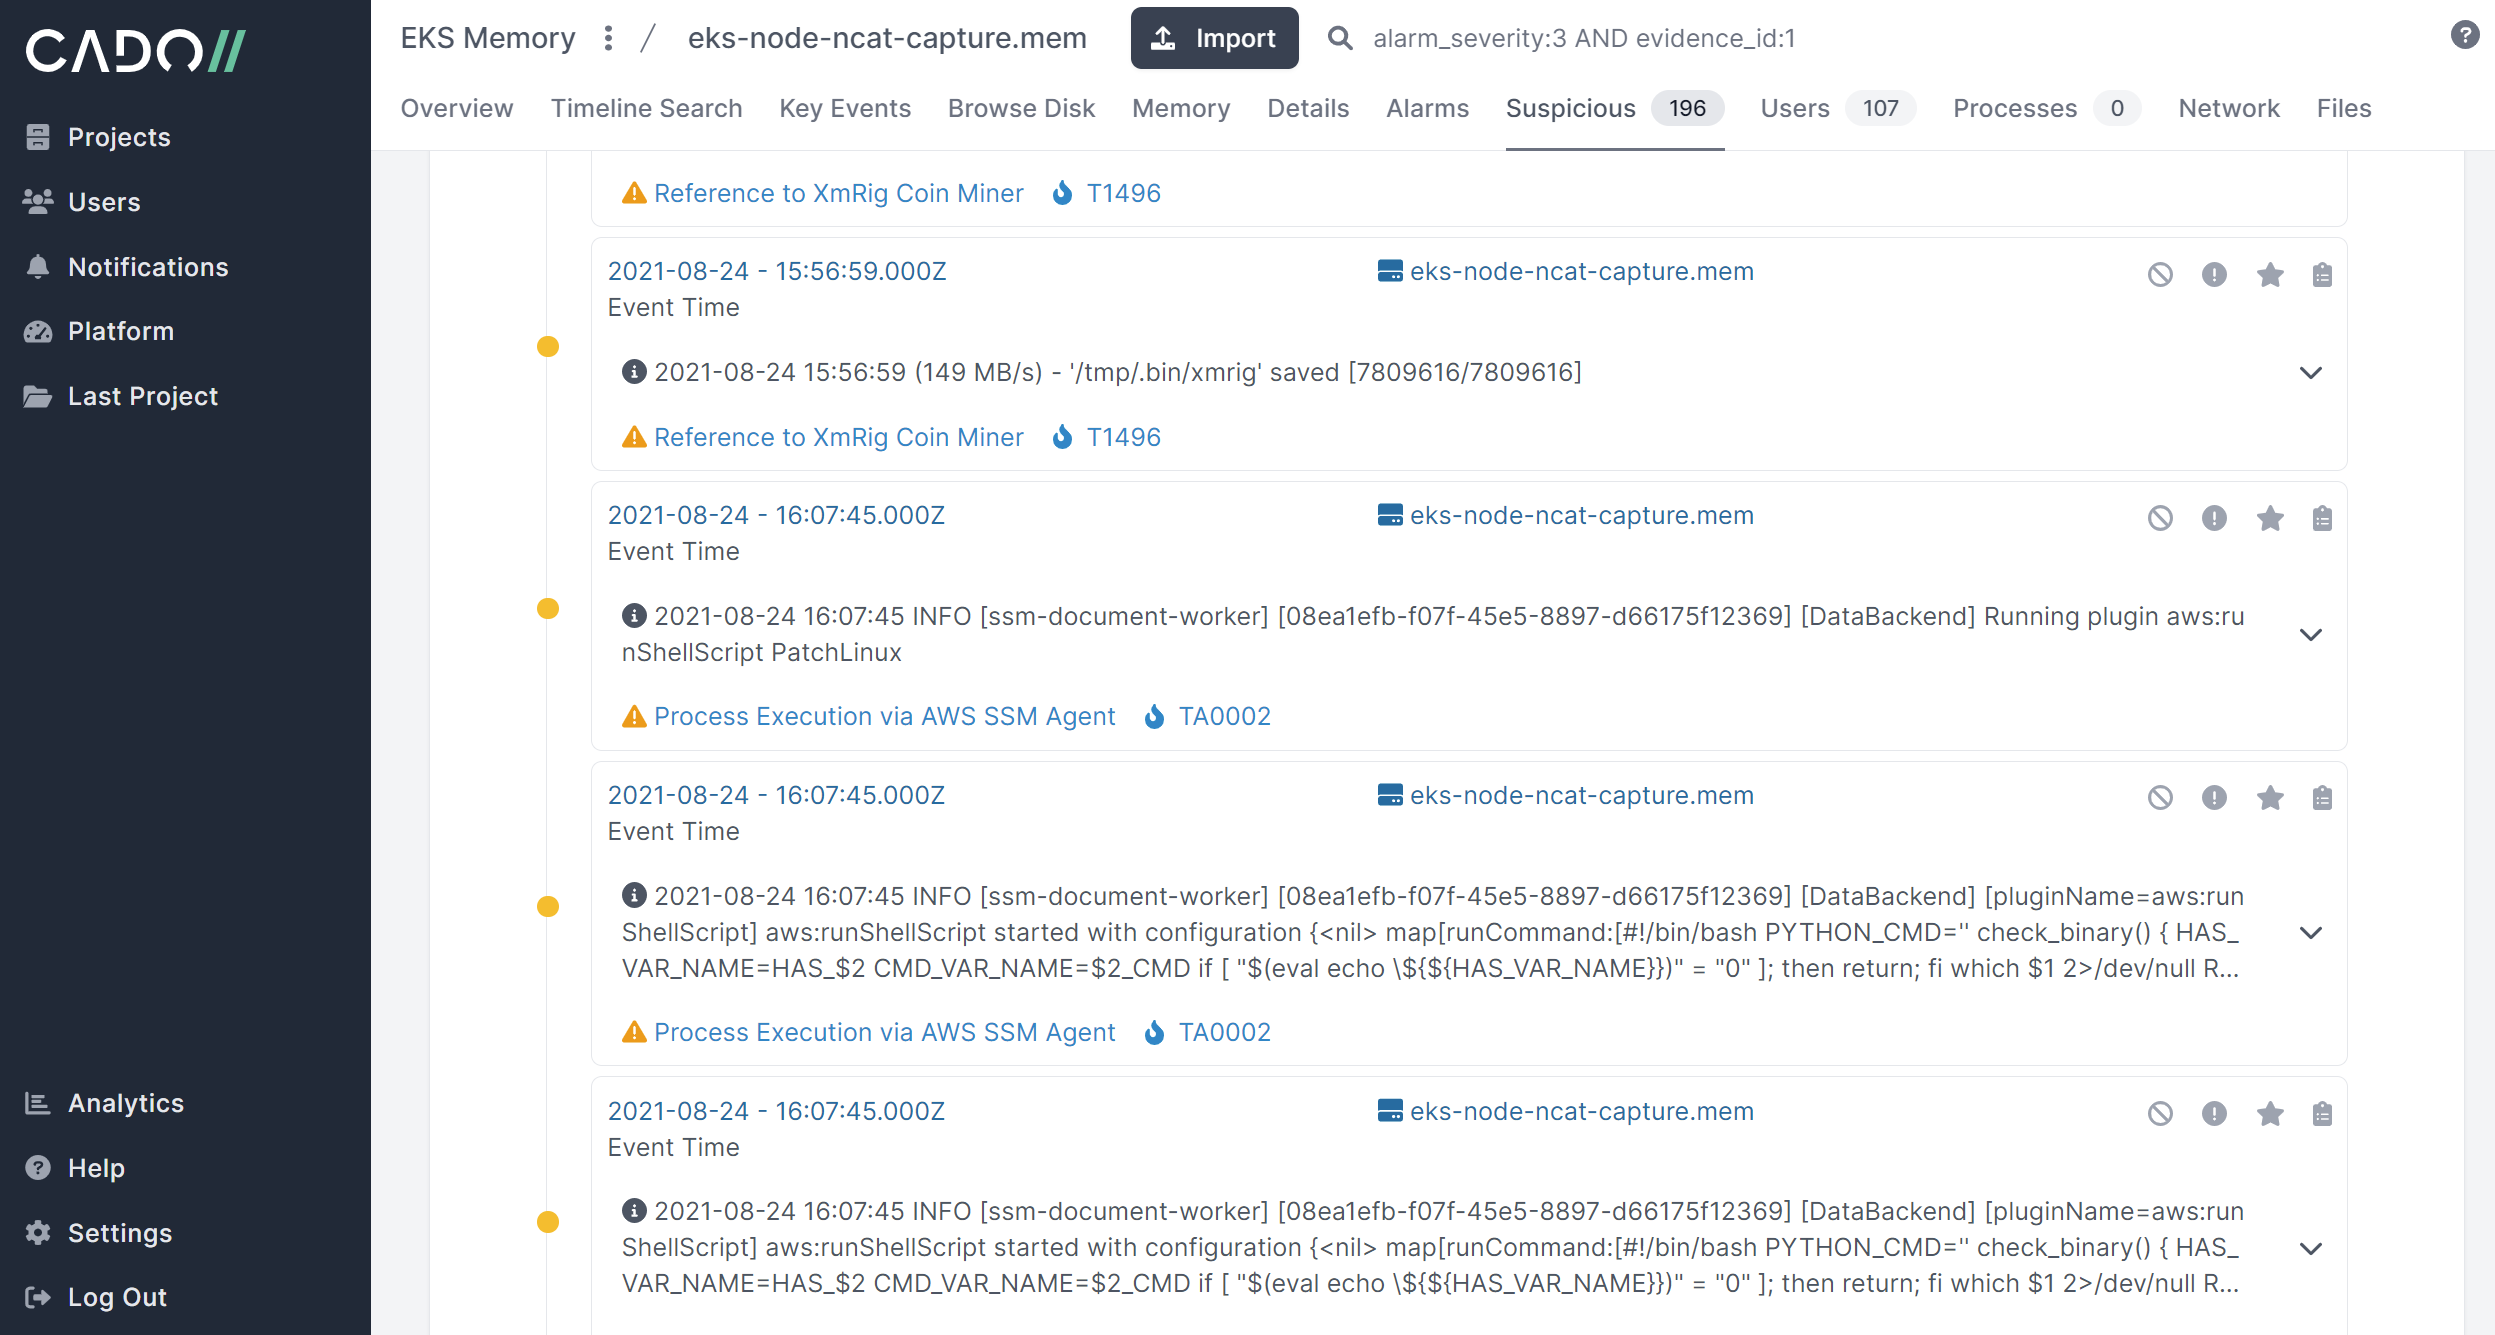
Rip Raw is a small tool to analyse the memory of compromised Linux systems.

Windows Analysis and Research Toolkit

Differential Analysis of Malware in Memory

Mimikatz implementation in pure Python

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

Panic button for protection against cold boot attacks

A Runtime Crypter in C for Linux ELF binaries.

Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.

Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…

A memory-based evasion technique which makes shellcode invisible from process start to end.

PoC and technical details of CVE-2025-24204

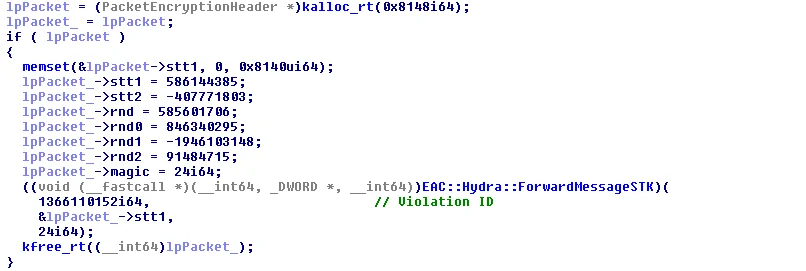
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…