
cve_2023_38831_scanner
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
dynamic-analysis-sandboxingeducationexploitation+5
1
yezzfusl/cve_2023_38831_scannerThis Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 zodiacon/alltools
All reasonably stable tools
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
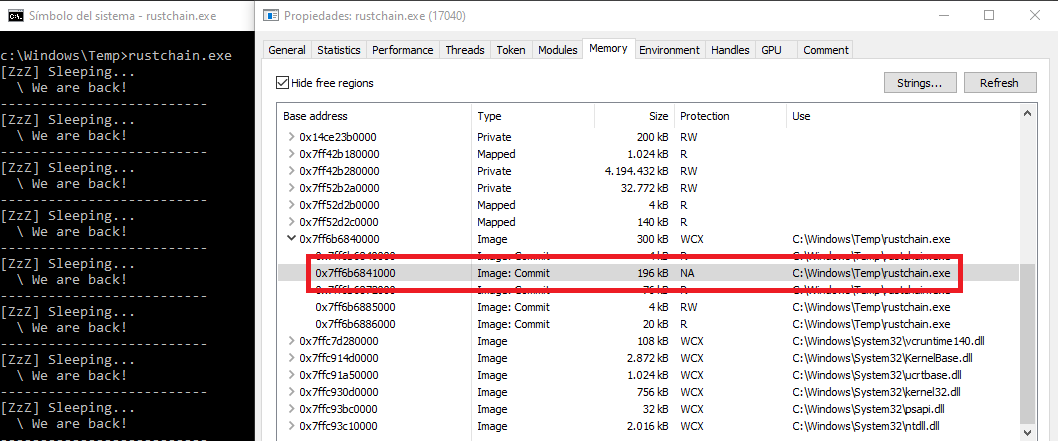 kudaes/rustchain
Hide memory artifacts using ROP and hardware breakpoints.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
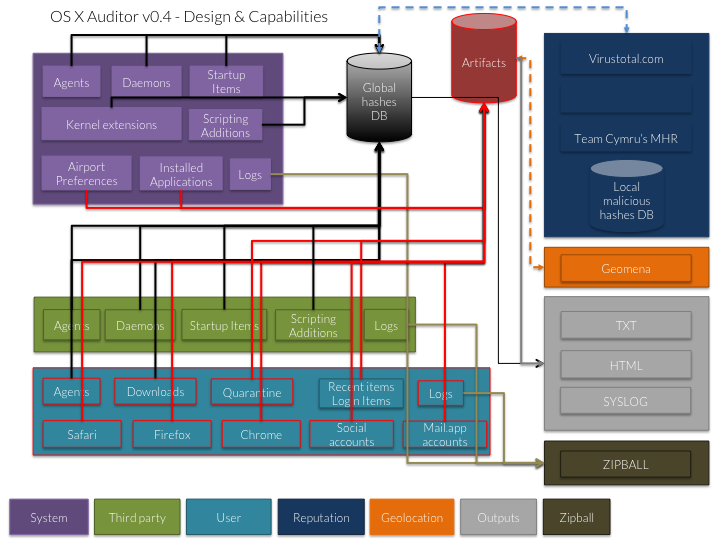 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
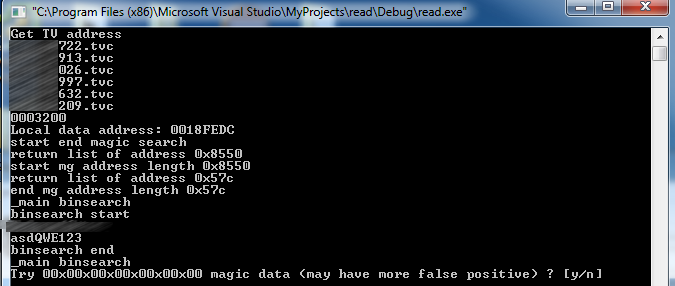 vah13/extracttvpasswords
tool to extract passwords from TeamViewer memory using Frida
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 nccgroup/asatools
Main repository to pull all NCC Group Cisco ASA-related tool projects.
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 0xpoly/centry
Panic button for protection against cold boot attacks
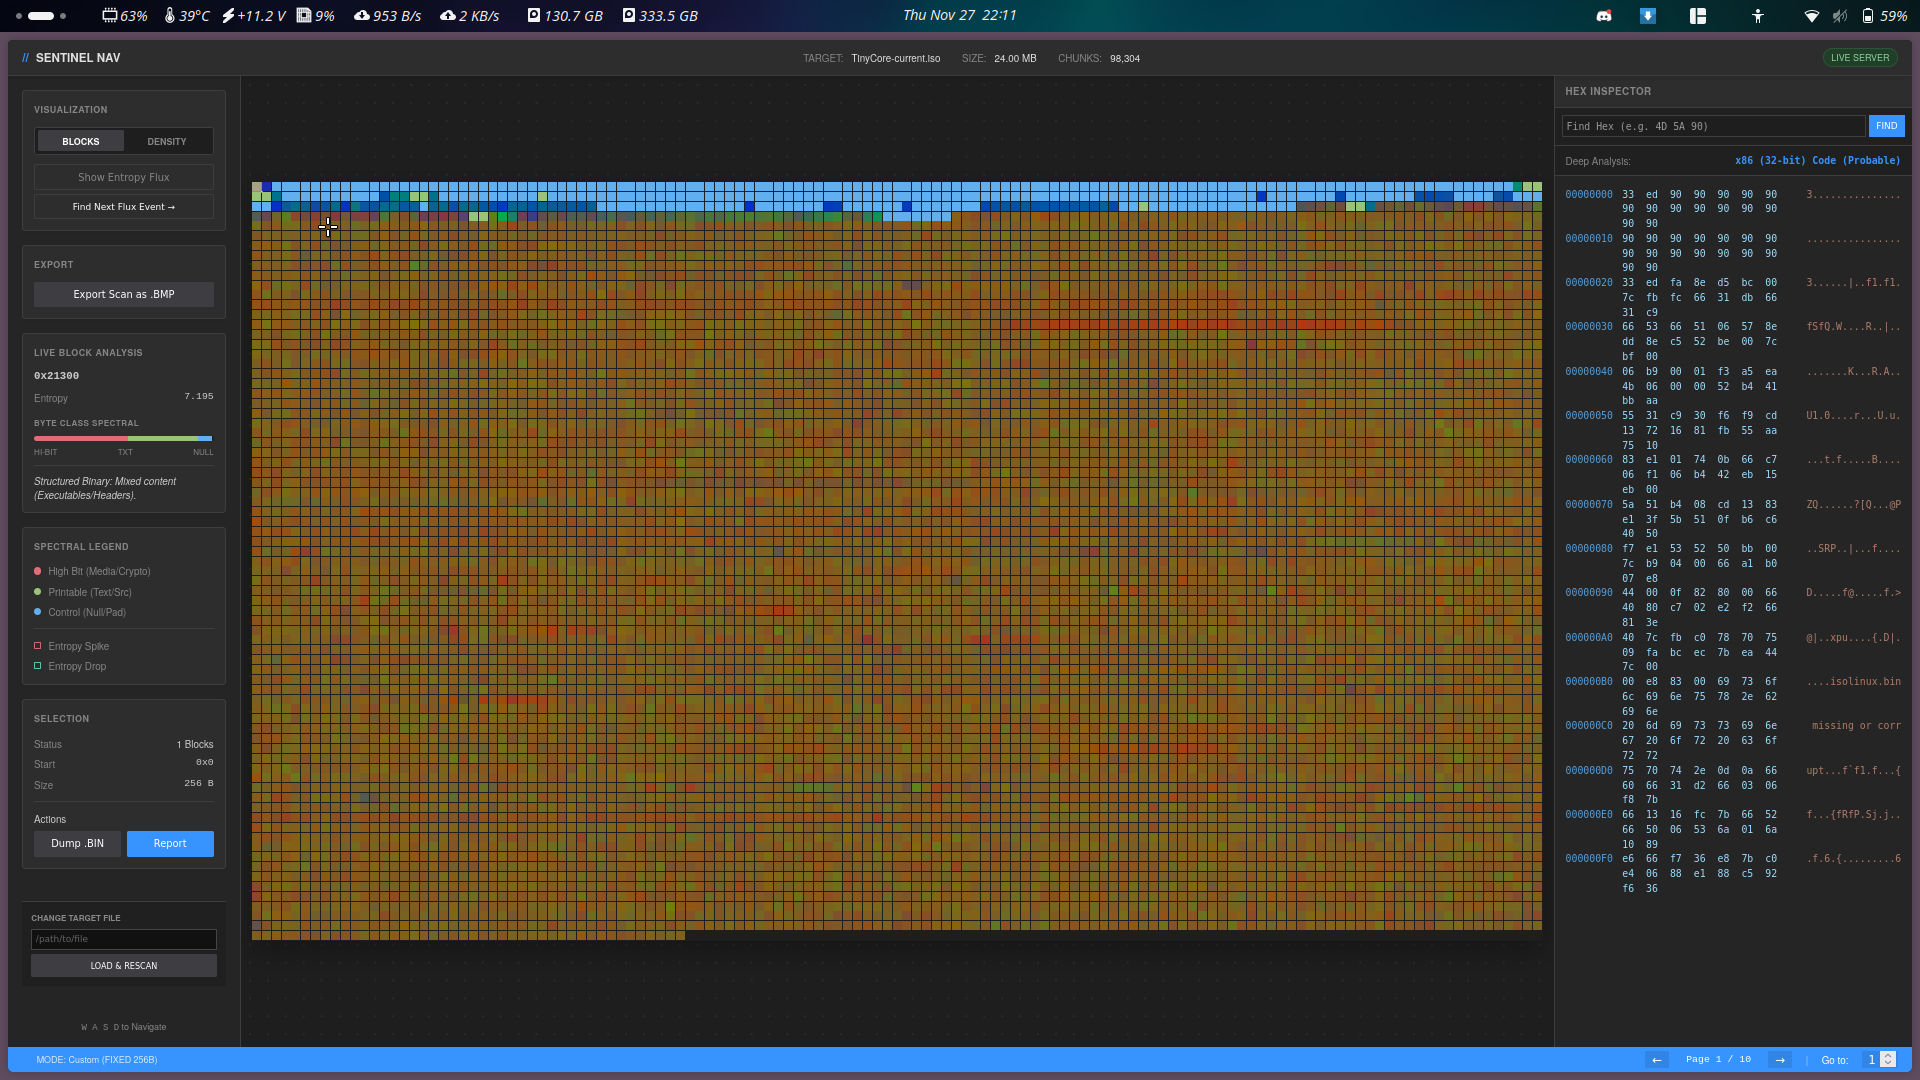 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.