
rastrea2r
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
digital-forensicsforensicsincident-response+6
rastrea2r/rastrea2rCollecting & Hunting for IOCs with gusto and style
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
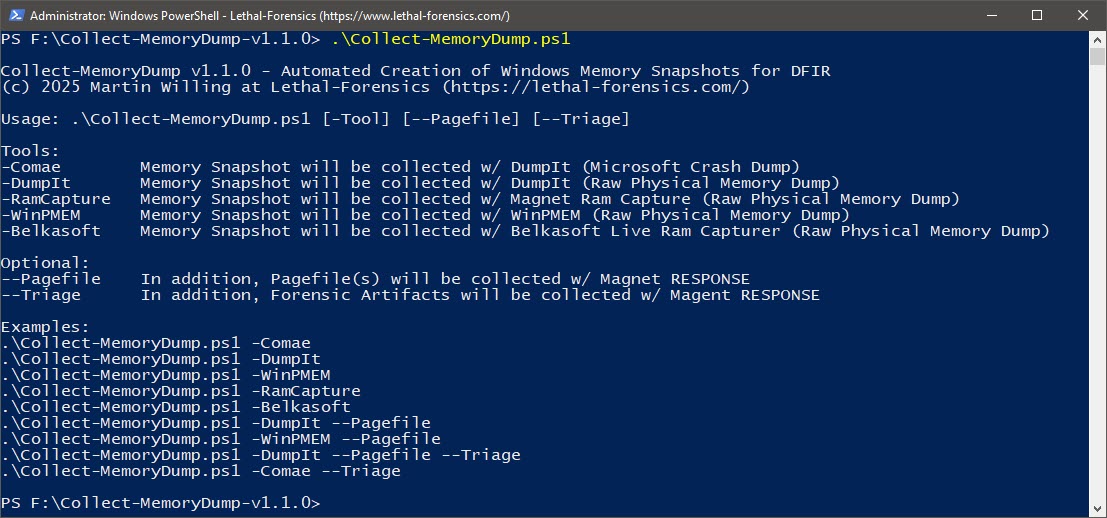 lethal-forensics/collect-memorydump
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
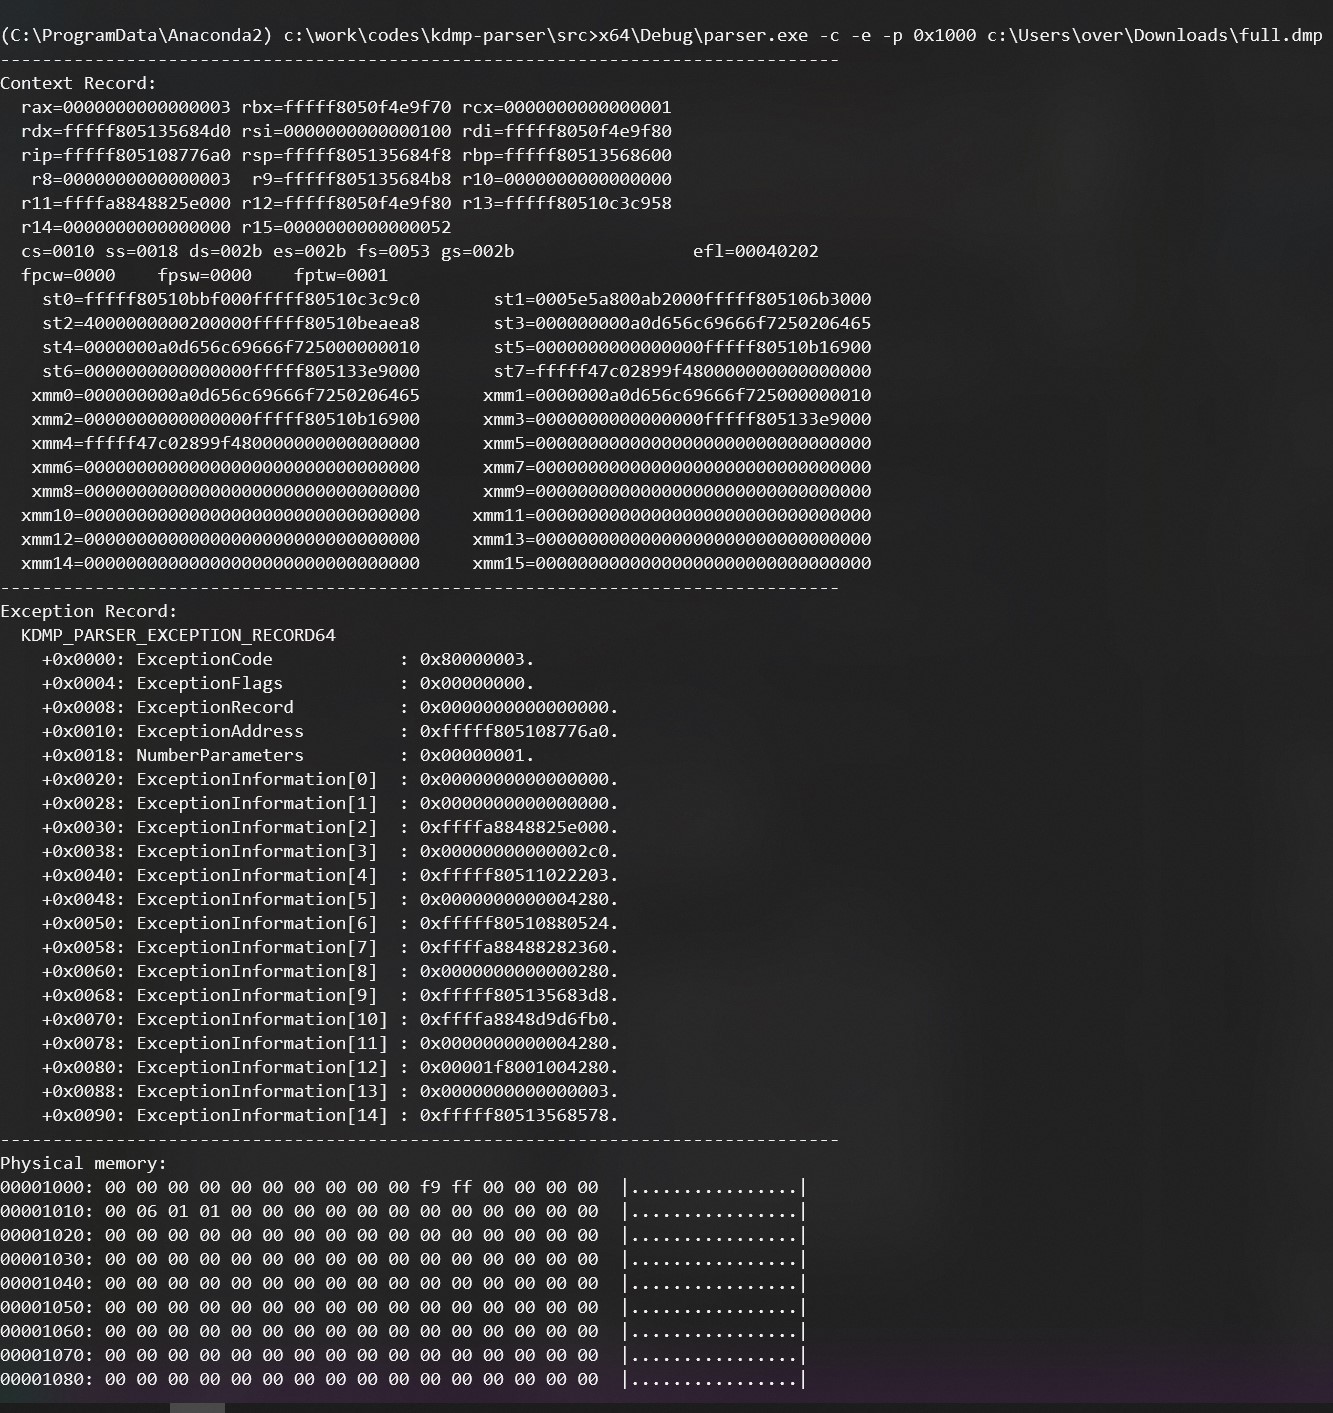 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
 bohops/rogueassemblyhunter
Rogue Assembly Hunter is a utility for discovering 'interesting' .NET CLR modules in running processes.
 ajmartel/irtriage
Incident Response Triage - Windows Evidence Collection for Forensic Analysis
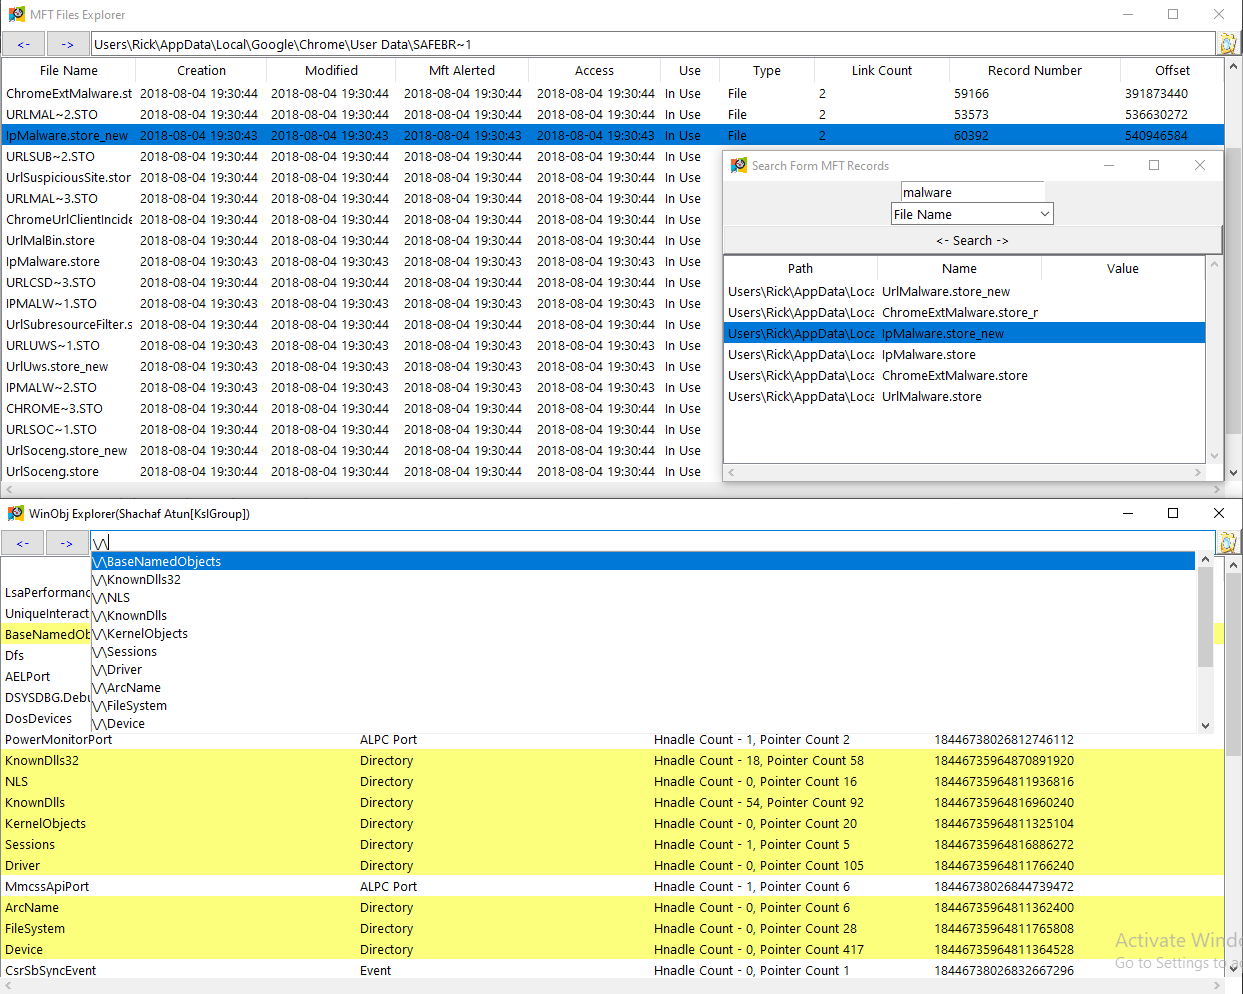 memoryforensics1/volexp
volatility explorer (volatility 2)
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 opensourcesec/cirtkit
Tools for the Computer Incident Response Team :computer:
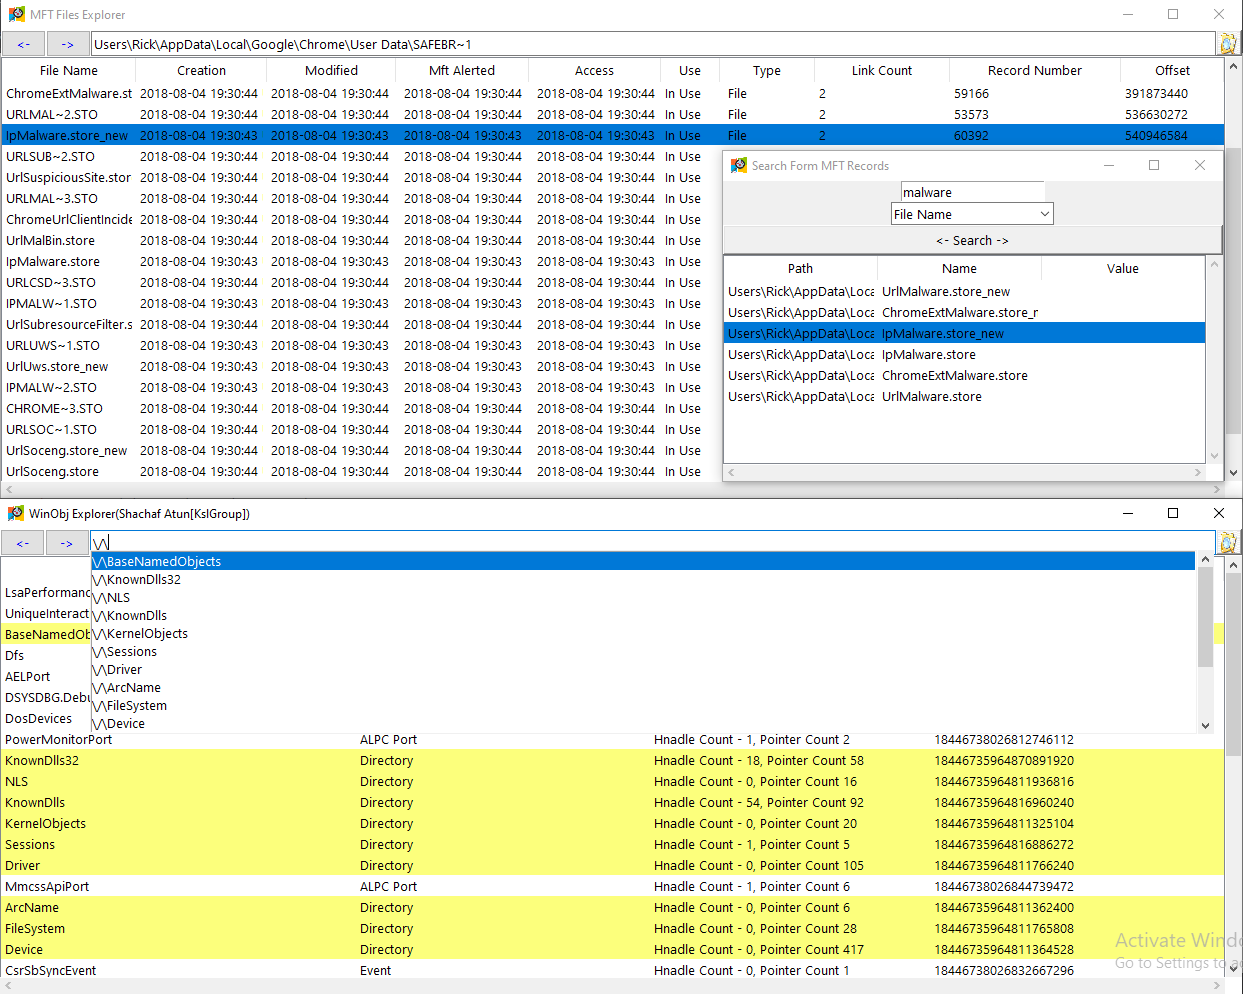 memoryforensics1/vol3xp
Volatility Explorer Suit (volatility 3)
 velocidex/linpmem
Linux kernel driver for physical memory acquisition, enabling read access to any physical address including reserved memory and memory holes, with…
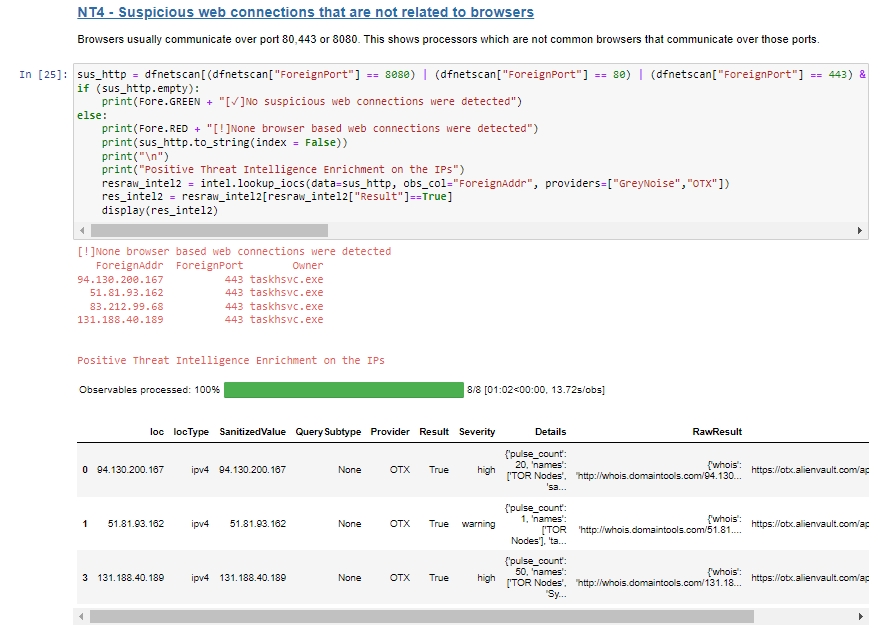 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 t-tani/yama-dev
Yet Another Memory Analyzer for malware detection
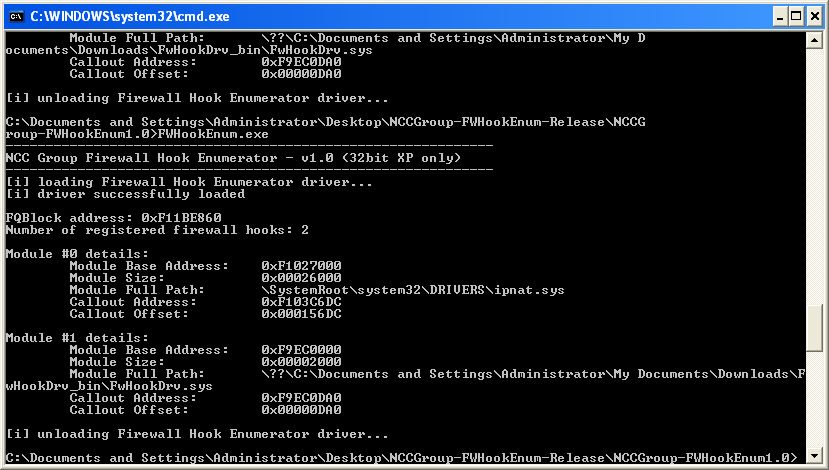 nccgroup/windowsfirewallhookdriverenumeration
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003