
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
124 results
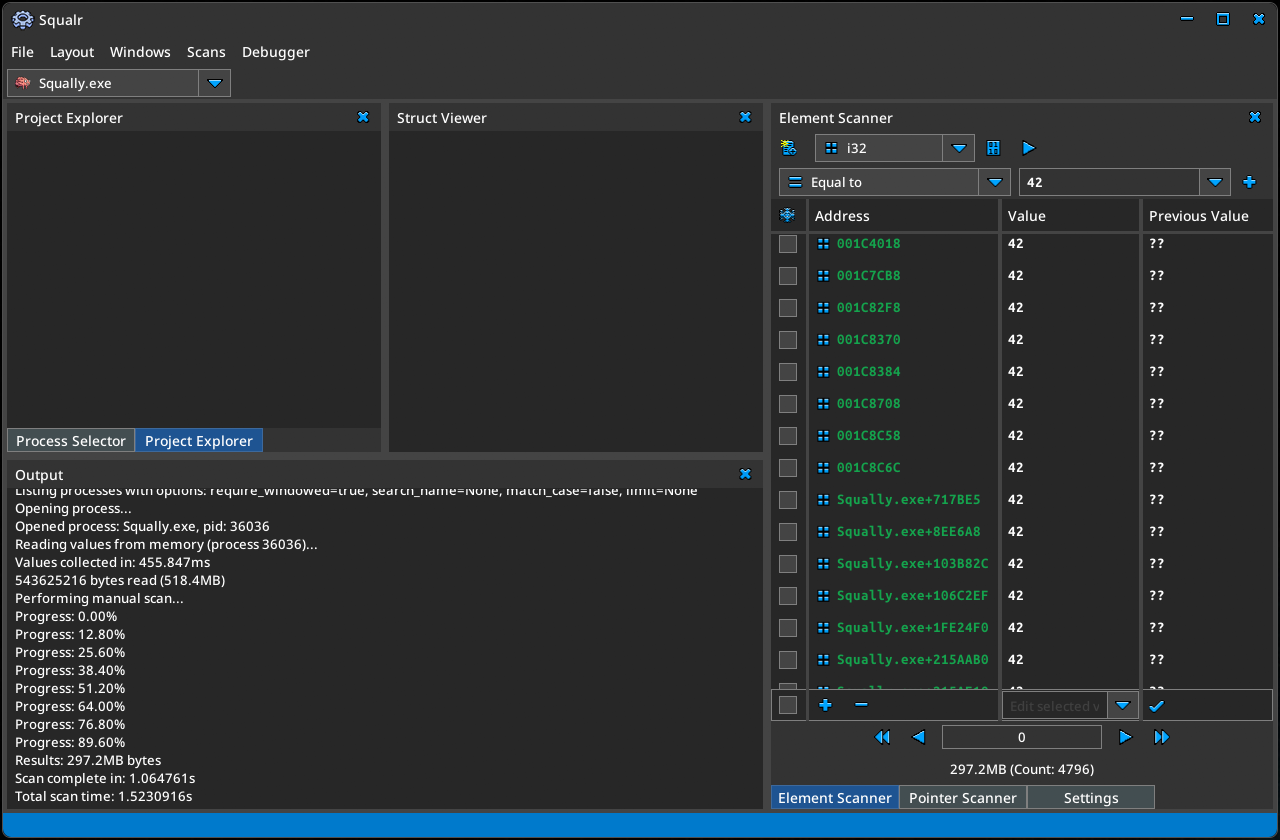
Squalr preview

Squalr

GitHubsqualr/squalr

A generic game/software hacking tool written from the ground up in Rust.
binary-analysisdebuggersdynamic-analysis-sandboxing+5
1874 months ago
KslKatzBof preview

KslKatzBof

GitHubprinciplecheck/kslkatzbof

Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
exploitationmemory-forensicspayload-development+4
911 month ago
KilledProcessCanary preview

KilledProcessCanary

GitHubnccgroup/killedprocesscanary

A canary designed to minimize the impact from certain Ransomware actors
anomaly-detectiondefensive-toolsdigital-forensics+2
1015 years ago
gpg_reaper preview

gpg_reaper

GitHubkacperszurek/gpg_reaper

GPG Reaper - Obtain/Steal/Restore GPG Private Keys from gpg-agent cache/memory
exploitationmemory-forensicspenetration-testing+1
968 years ago
proctools preview

proctools

GitHubmlcsec/proctools

Small toolkit for extracting information and dumping sensitive strings from Windows processes
digital-forensicsforensicsinformation-gathering+2
1162 years ago
IronPE preview

IronPE

GitHubiss4cf0ng/ironpe

Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
binary-analysisbinary-exploitationeducation+5
1247 months ago
memOptix preview

memOptix

GitHubblueteam0ps/memoptix

A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
digital-forensicsforensicsincident-response+2
983 years ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
cryptographydigital-forensicseducation+7
315 months ago
EtwLeakKernel preview

EtwLeakKernel

GitHubidov31/etwleakkernel

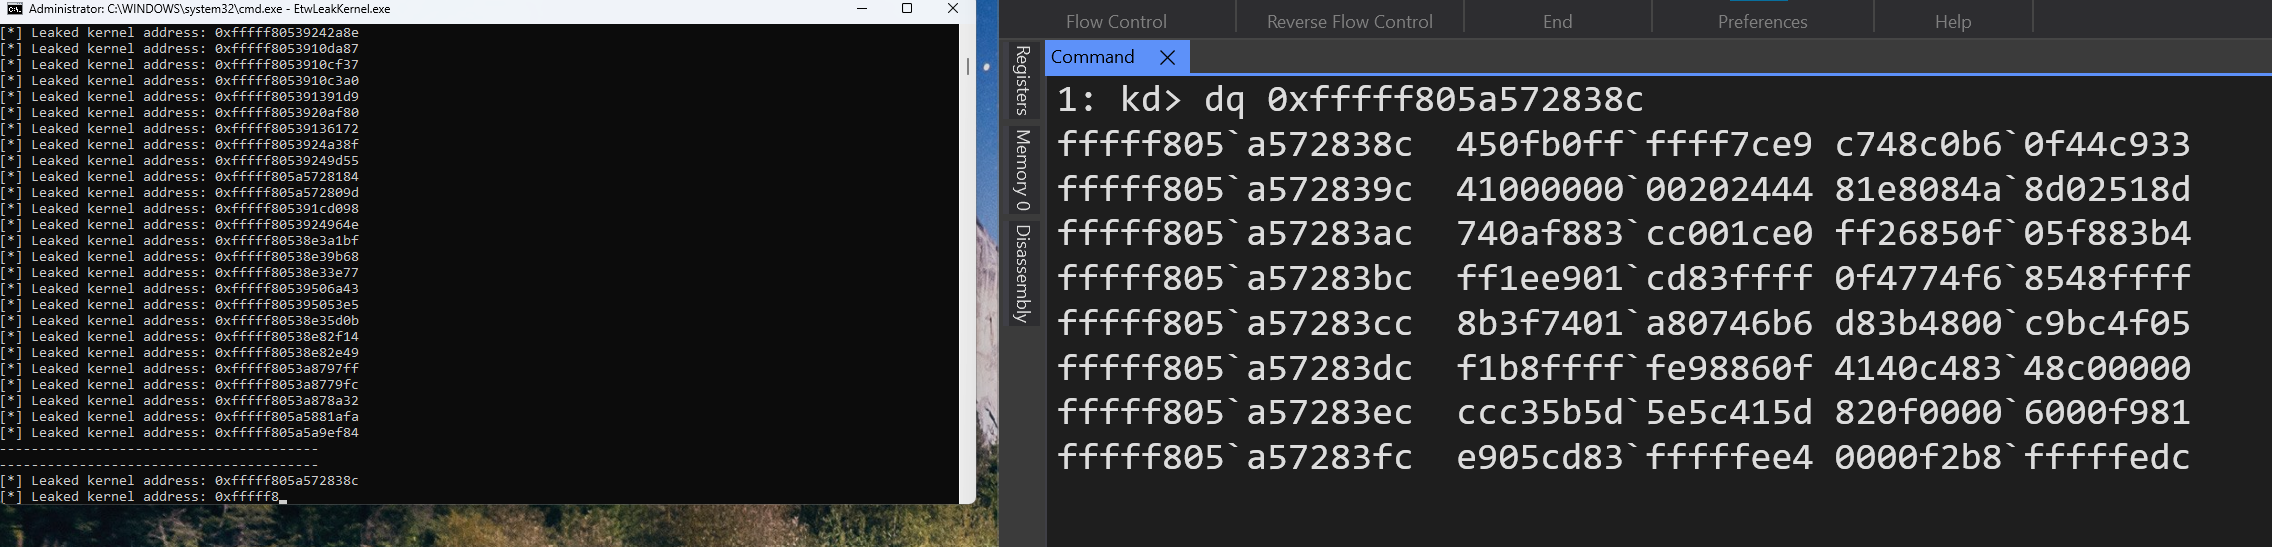
Leaking kernel addresses from ETW consumers. Requires Administrator privileges.
binary-exploitationexploitationinformation-gathering+2
9511 months ago
linux_screenshot_xwindows preview

linux_screenshot_xwindows

GitHubeurecom-s3/linux_screenshot_xwindows

Volatility plugin to extract X screenshots from a memory dump
digital-forensicsforensicsinformation-gathering+1
378 years ago
Nemesis preview

Nemesis

GitHubzypherion-technologies/nemesis

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.

defensive-toolsdynamic-analysis-sandboxingmalware-analysis+2
4112 days ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…

binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

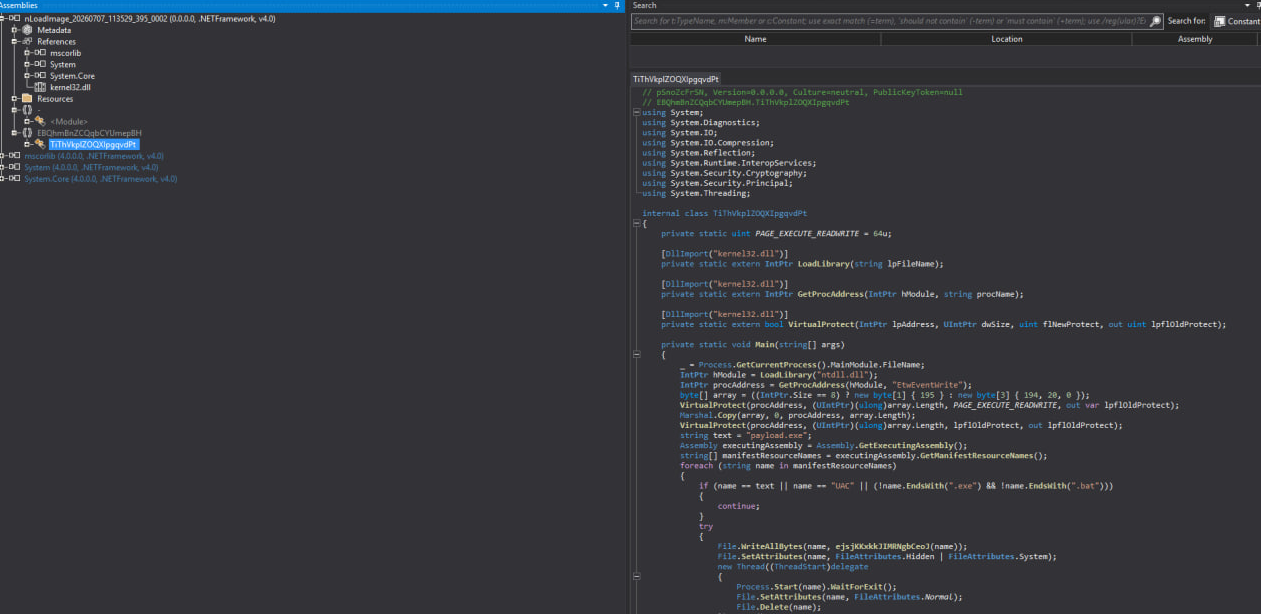
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
command-and-controlcryptographydigital-forensics+4
372 years ago
bw-dump preview

bw-dump

GitHubmarkuta/bw-dump

A proof-of-concept for (CVE-2023-38840) that extracts plaintext master passwords from a locked Bitwarden vault.

digital-forensicsexploitationforensics+4
422 years ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
binary-analysiscontainer-escapedata-recovery+7
122 months ago
watchTowr-vs-Netscaler-CVE-2026-8451 preview

watchTowr-vs-Netscaler-CVE-2026-8451

GitHubwatchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451

Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…
exploitationinformation-gatheringmemory-forensics+3
133 months ago
CVE-2025-7771-Vulnerability-Exploration preview

CVE-2025-7771-Vulnerability-Exploration

GitHubd4rkks/cve-2025-7771-vulnerability-exploration

Escalating privilege in the system from unsigned driver using throttlestop vulnerability
binary-exploitationeducationexploitation+4
156 months ago
CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter preview

CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter

GitHubsneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.

binary-exploitationexploitationmemory-forensics+3
51 month ago
Previous1234567Next