

libmempool
 nccgroup/libmempool
Heap analysis tooling for mempool
binary-analysisdebuggersembedded-systems-security+3
nccgroup/libmempoolHeap analysis tooling for mempool
 pwndorei/cve-2024-22532
Proof-of-concept exploit for CVE-2024-22532: heap-based buffer overflow in XnView Classic 2.51.5 and NConvert 7.163 via crafted .xwd file, enabling…
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
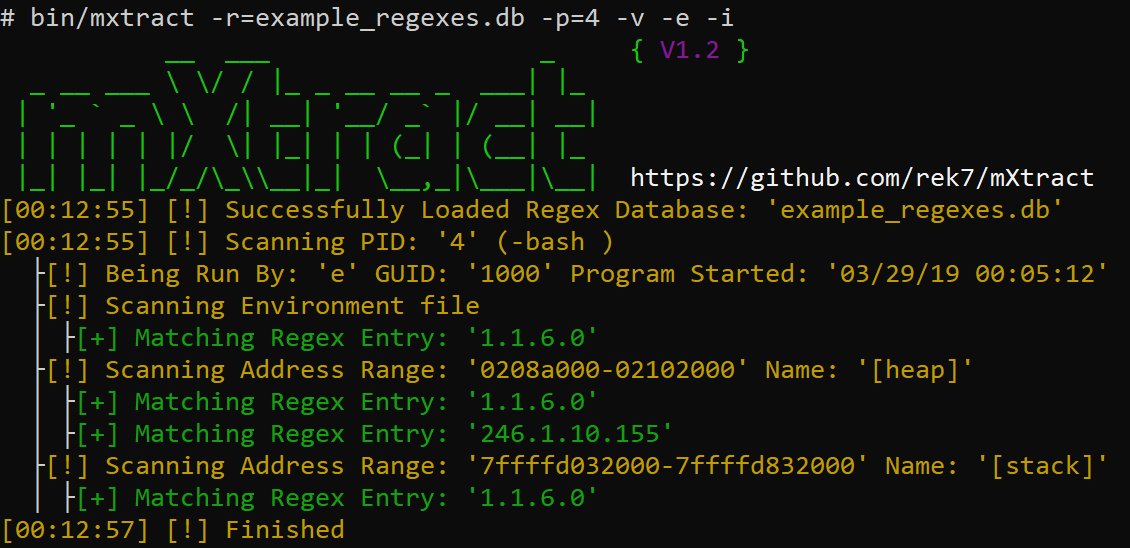 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
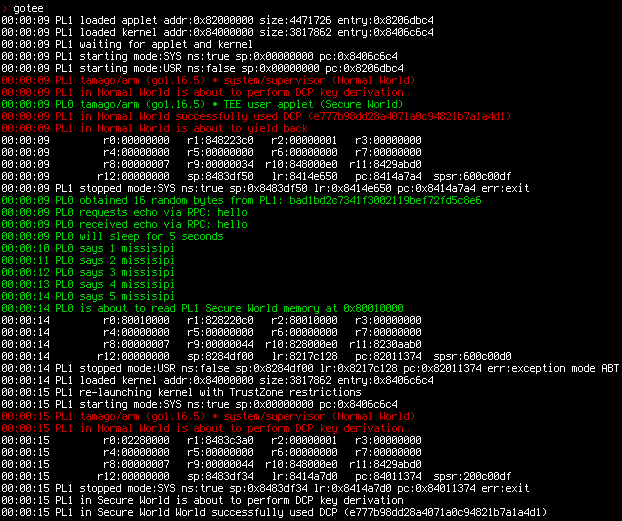 usbarmory/gotee-example
GoTEE - example application
 the-maxu/cve-2025-24201-webkit-vulnerability-detector-poc-
CVE-2025-24201 WebKit Vulnerability Detector (PoC)
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

 pray3r/cve-2015-8088
Crash PoC