

IPED
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k
sepinf-inc/ipedIPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
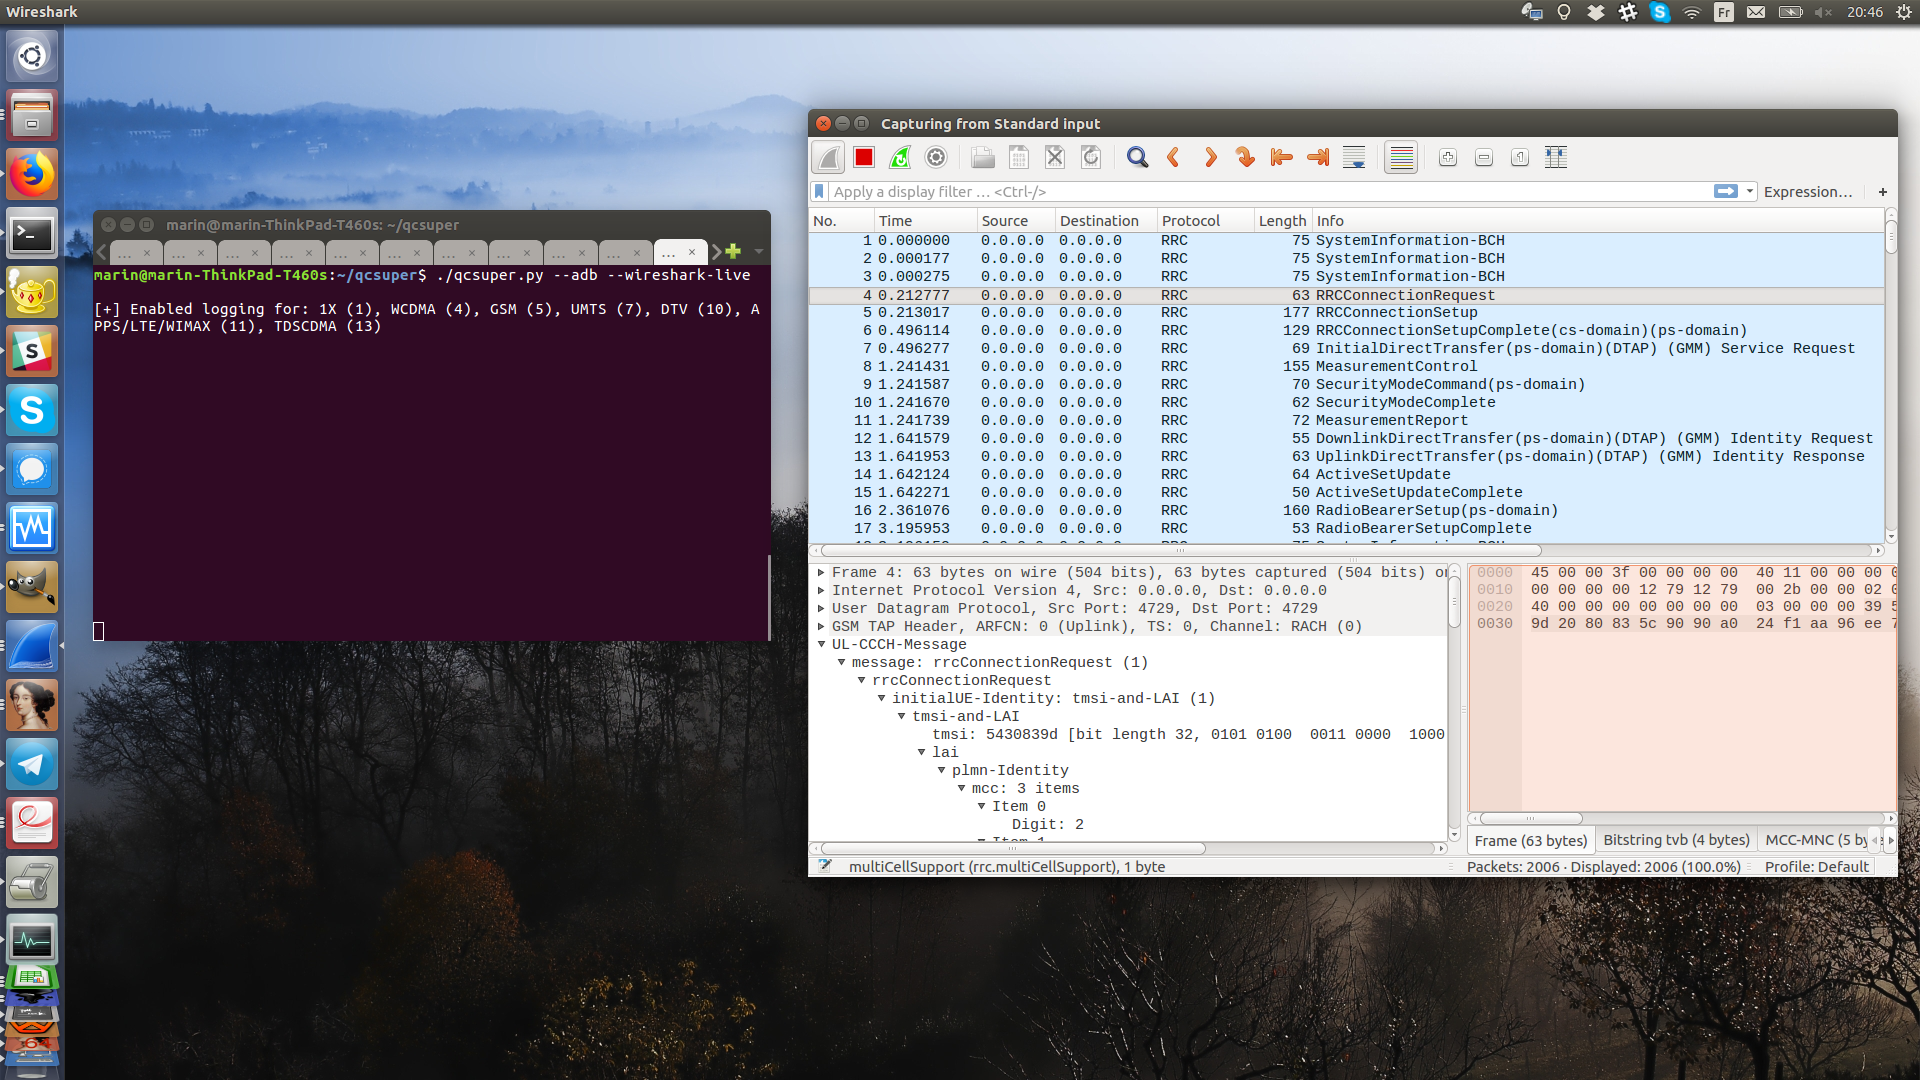 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
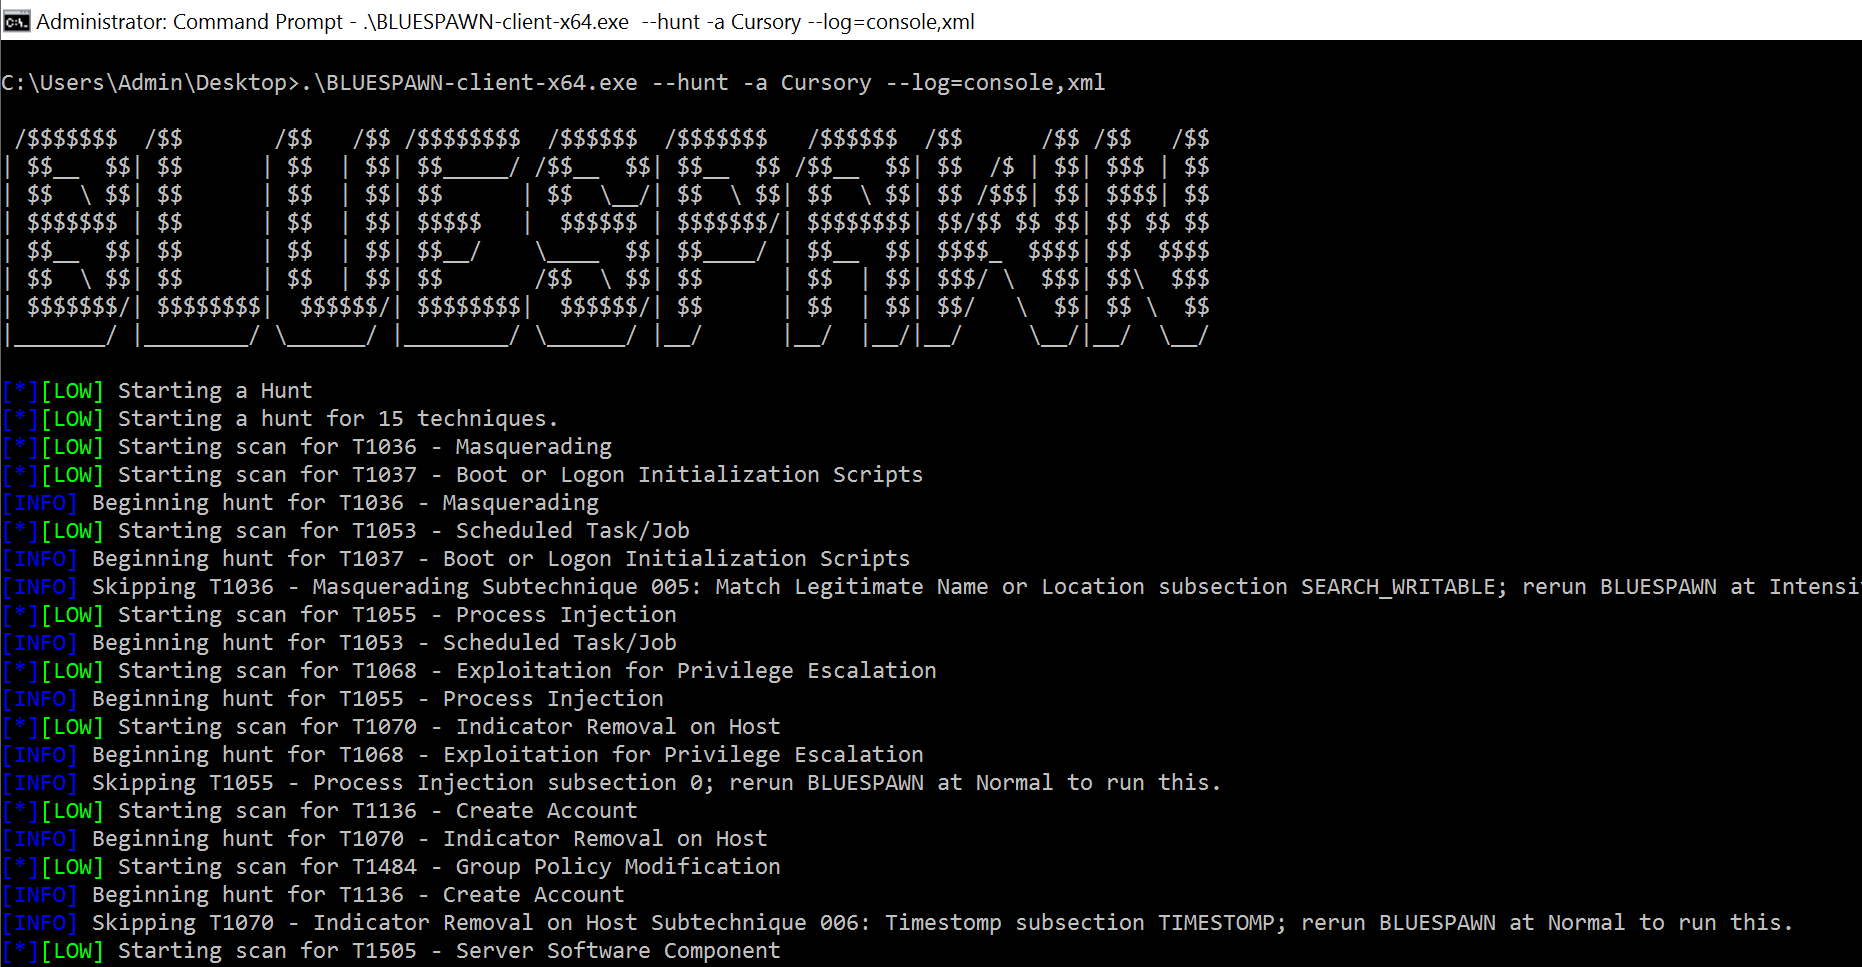 ion28/bluespawn
An Active Defense and EDR software to empower Blue Teams