

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
10.9k
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
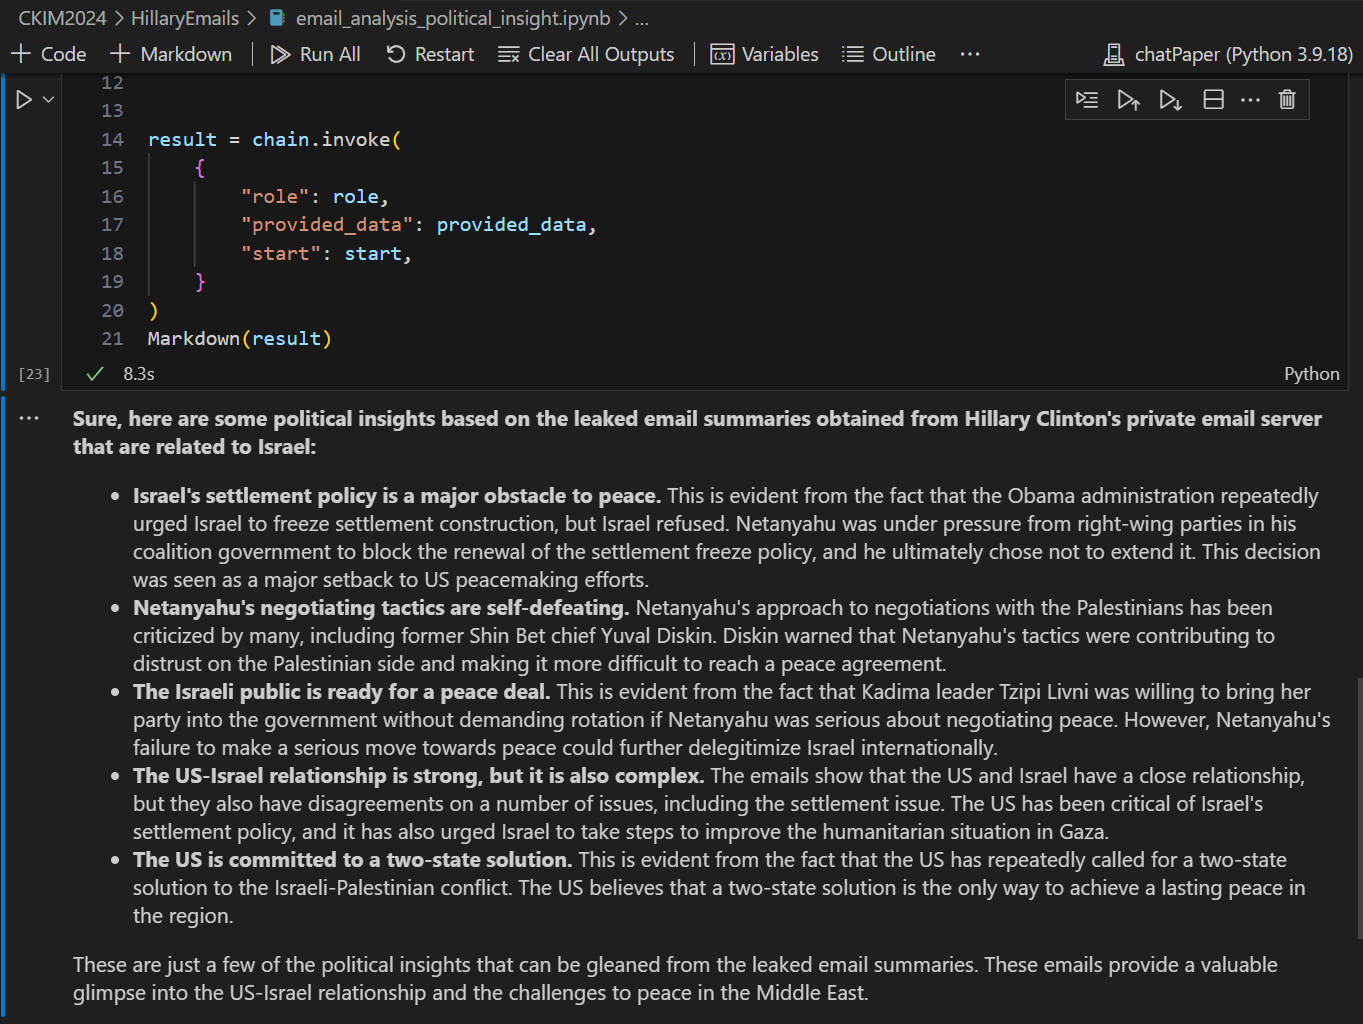 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
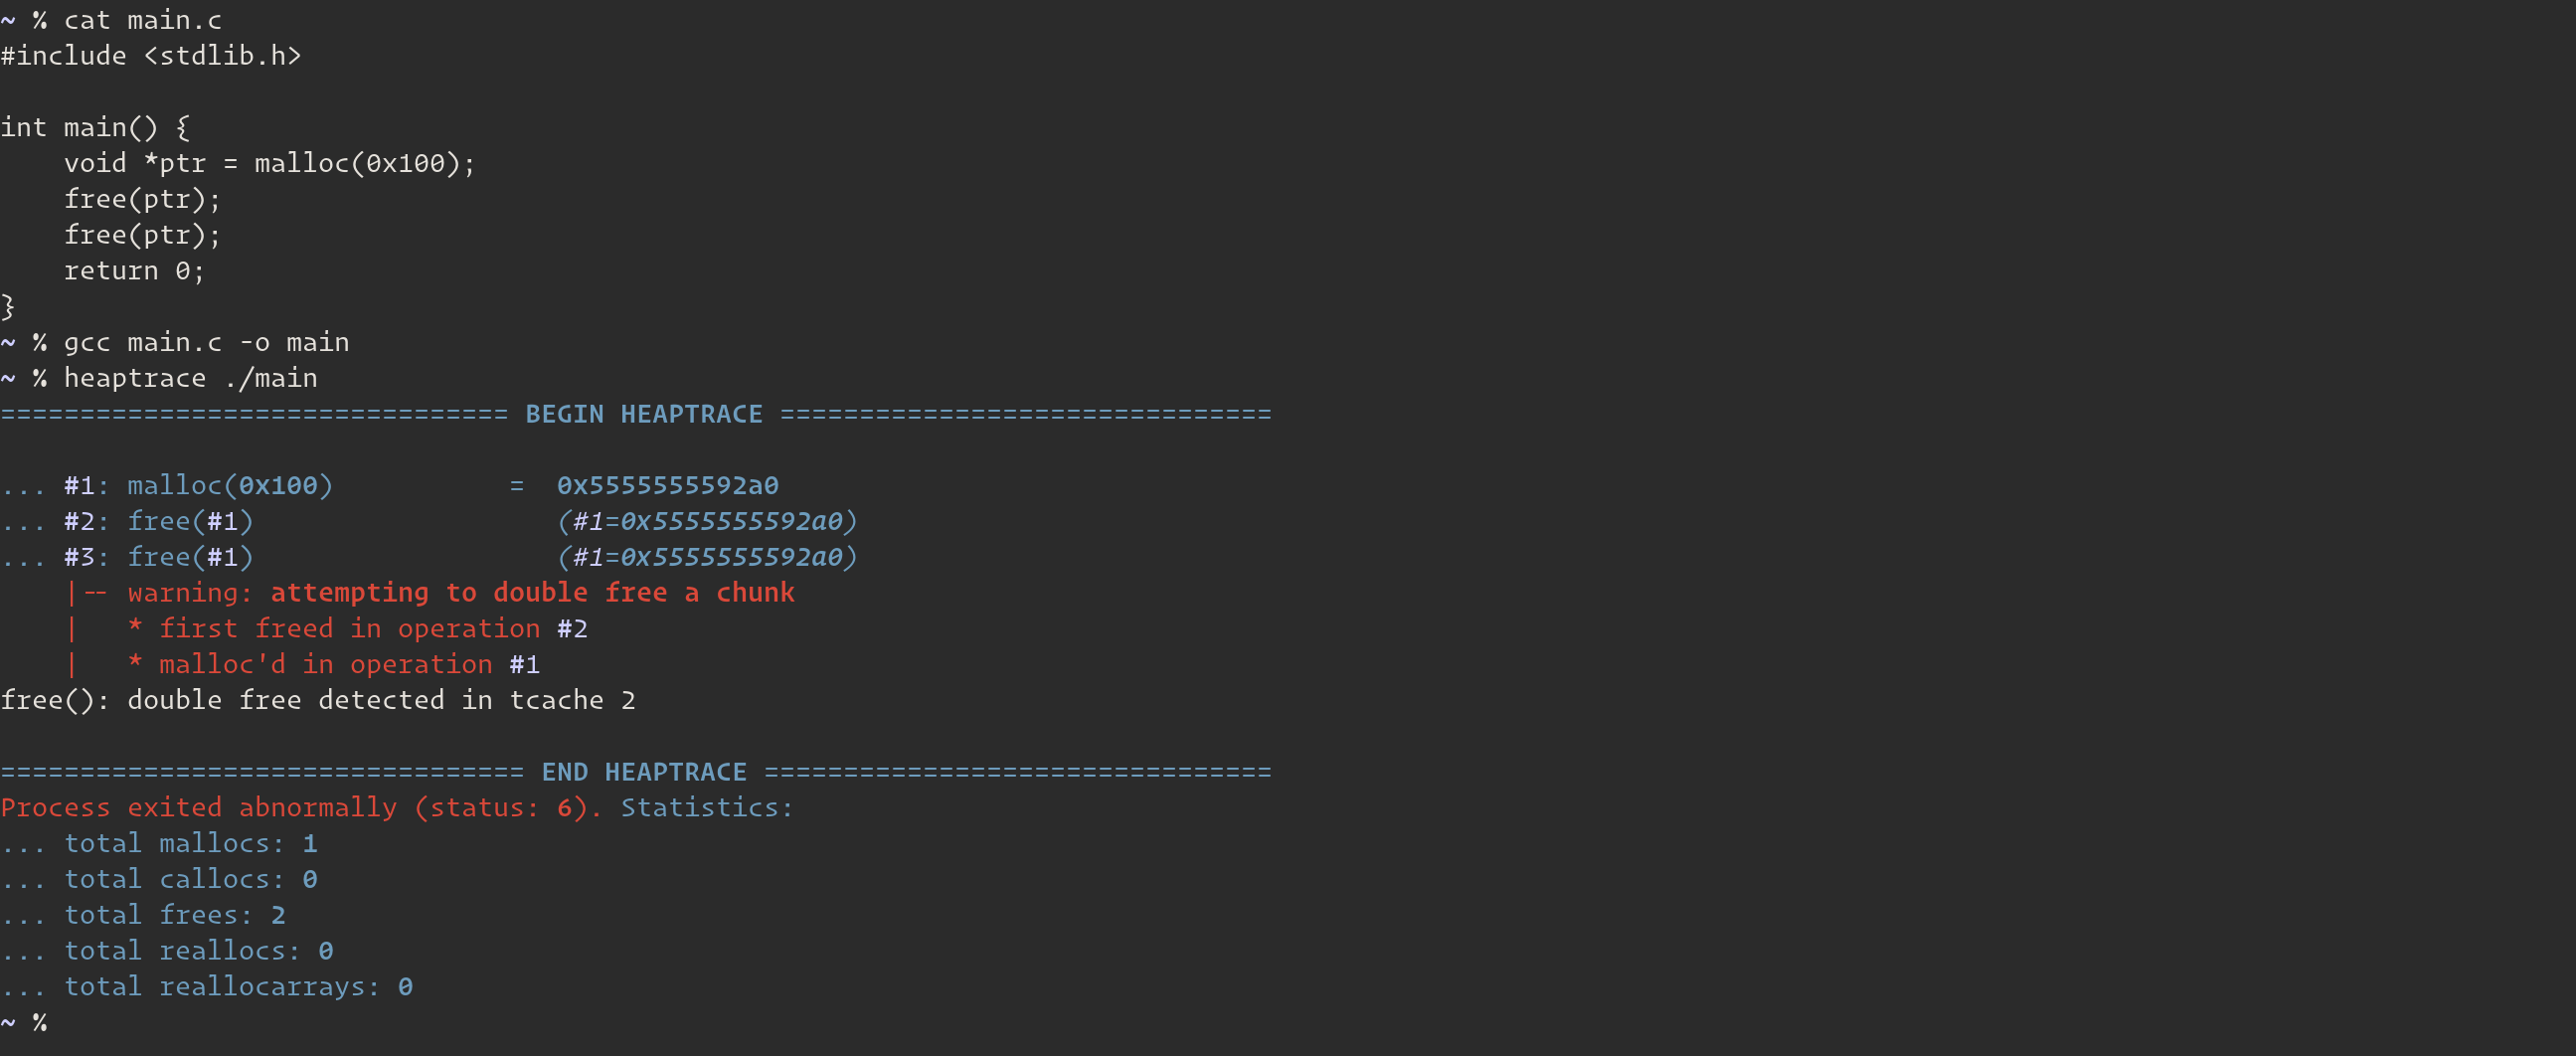 arinerron/heaptrace
helps visualize heap operations for pwn and debugging
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
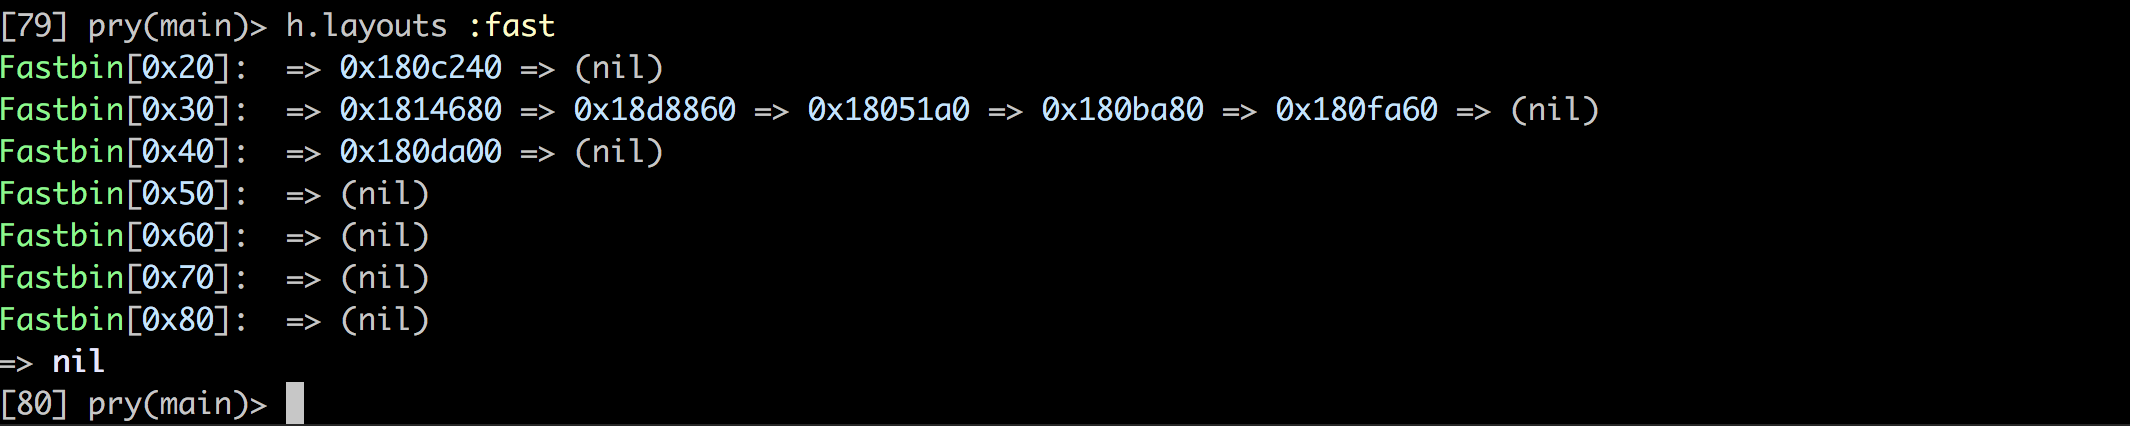 david942j/heapinfo
An interactive memory info for pwning / exploiting
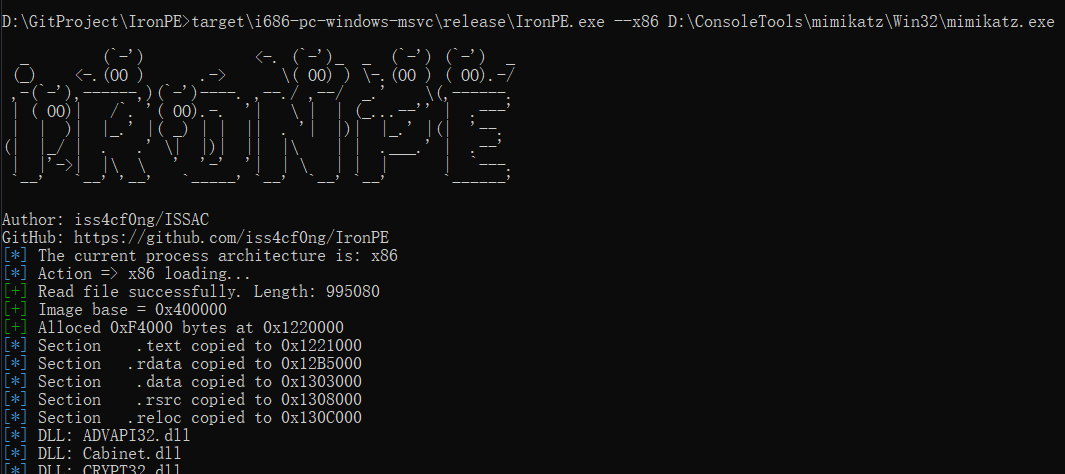 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 tin-z/cve-2025-27363
Integer overflow in FreeType software, which also affects Chrome
 flankerhqd/cve-2015-6620-poc
POC for CVE-2015-6620, AMessage unmarshal arbitrary write
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 android-rooting-tools/libmsm_vfe_read_exploit
CVE-2014-4321 exploit
 kagancapar/cve-2026-5201
CVE-2026-5201: Heap-based buffer overflow in gdk-pixbuf JPEG loader (CWE-122, CVSS 7.5)
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 baba01hacker666/cve-2026-23111
Linux Kernel nf_tables Use-After-Free (CVE-2026-23111) — LPE PoC