
ltm
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
agent-hellboy/ltmltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 gmikisilva/cve-2024-33901-proofofconcept
Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
 hunters-sec/cve-2025-31200
IOS audio buffer overflow CVE-2025-31200 POC

 furkankayapinar/cve-2025-14847-mongobleed-exploit
CVE-2025-14847 MongoBleed - MongoDB Memory Leak Vulnerability PoC
 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
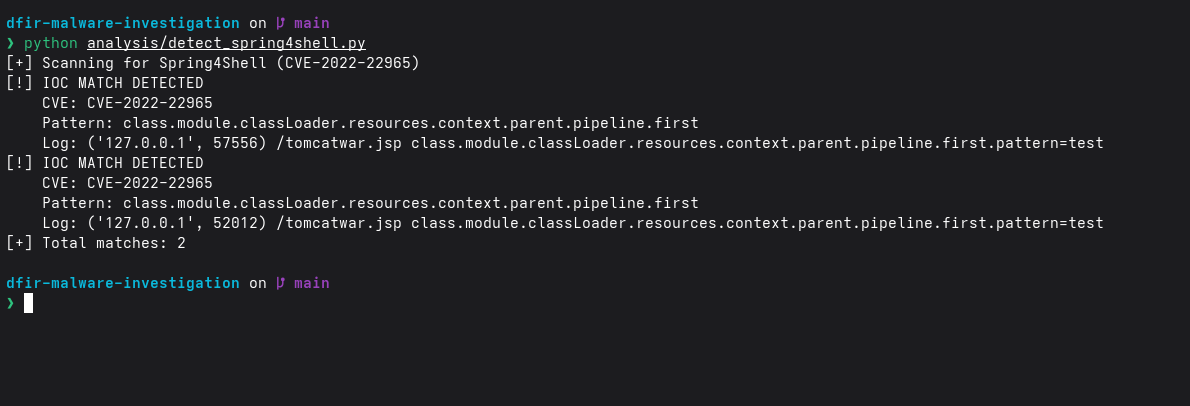 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 soteria-research/cve-2015-4843-type-confusion-phrack
Demonstrates type confusion and heap overflow exploits for CVE-2015-4843 in Java, with demos for aarch64 and Morello, highlighting CHERI capability…
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 denandz/lpc_sniffer_tpm
A low pin count sniffer for ICEStick - targeting TPM chips
 packtpublishing/learning-linux-binary-analysis
Learning Linux Binary Analysis, published by Packt
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 bytehackr/cve-2022-0853
Demonstrates a memory leak in JBoss client when using UserTransaction repeatedly, with a PoC and analysis for CVE-2022-0853.
 satheesh575555/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.