
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
369 results
CVE-2018-19321 preview

CVE-2018-19321

GitHubnanabingies/cve-2018-19321

CVE-2018-19321

binary-exploitationexploitationhardware-security+3
2
3 years ago
CVE-2014-1773 preview

CVE-2014-1773

GitHubday6reak/cve-2014-1773

Technical analysis of CVE-2014-1773, a heap corruption vulnerability in Internet Explorer's MSHTML engine, with detailed crash callstack,…

binary-exploitationdebuggersexploitation+3
11 years ago
CVE-2022-21971-Windows-Runtime-RCE preview

CVE-2022-21971-Windows-Runtime-RCE

GitHubtufanturhan/cve-2022-21971-windows-runtime-rce

Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…

binary-exploitationdebuggersexploitation+3
24 years ago
CVE-2022-21971 preview
Archived

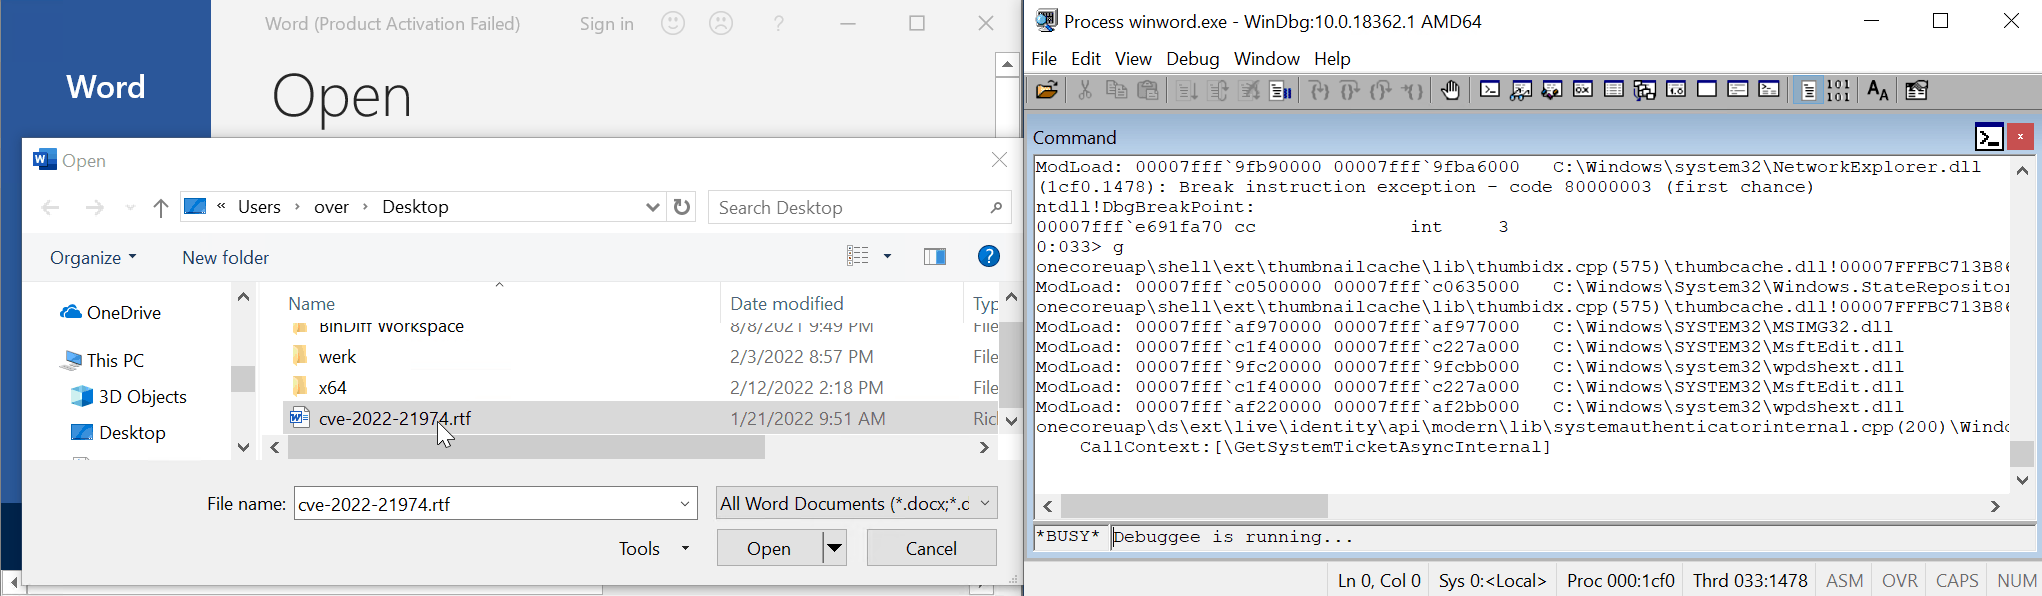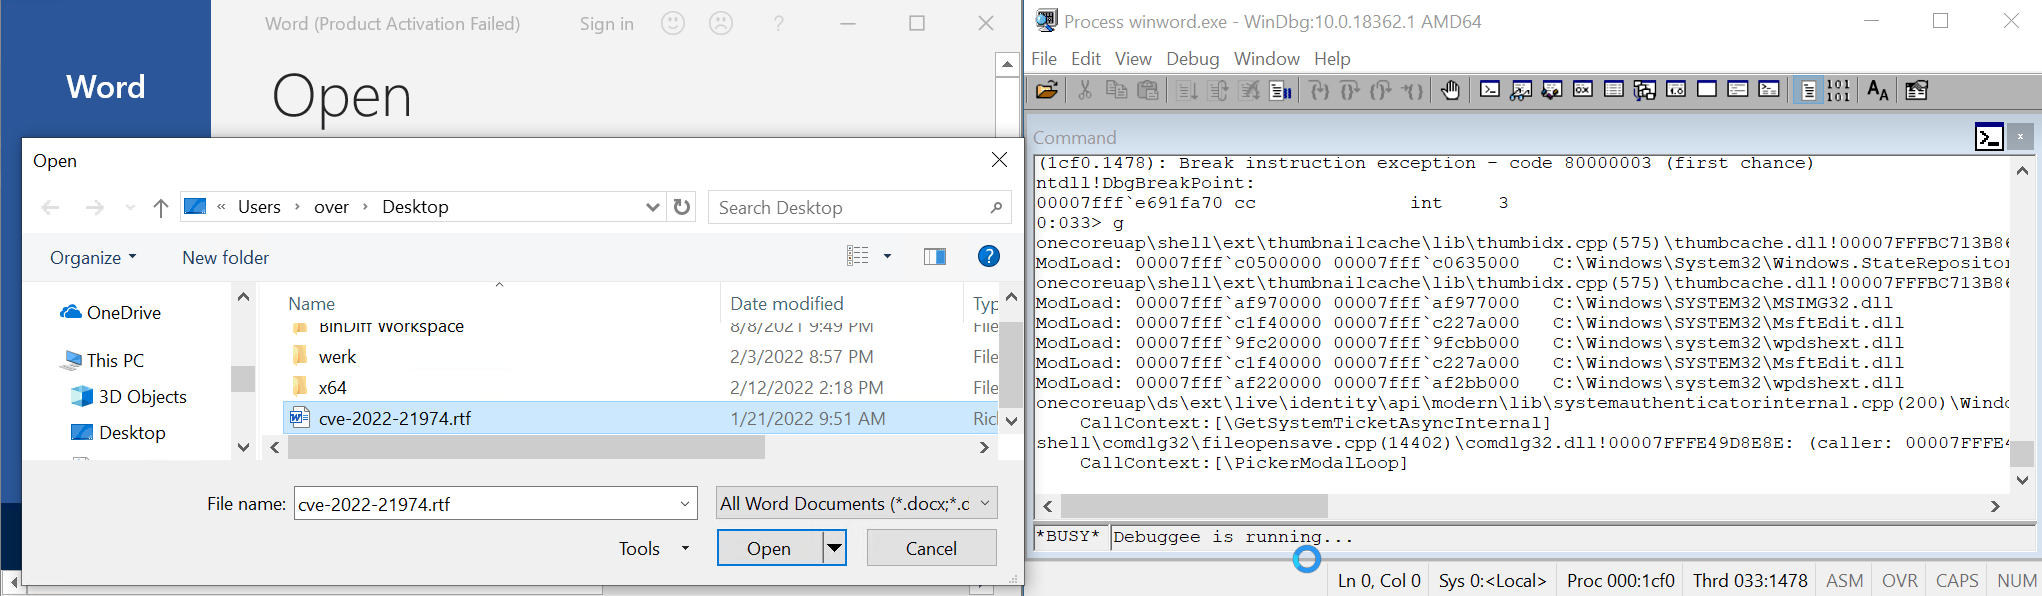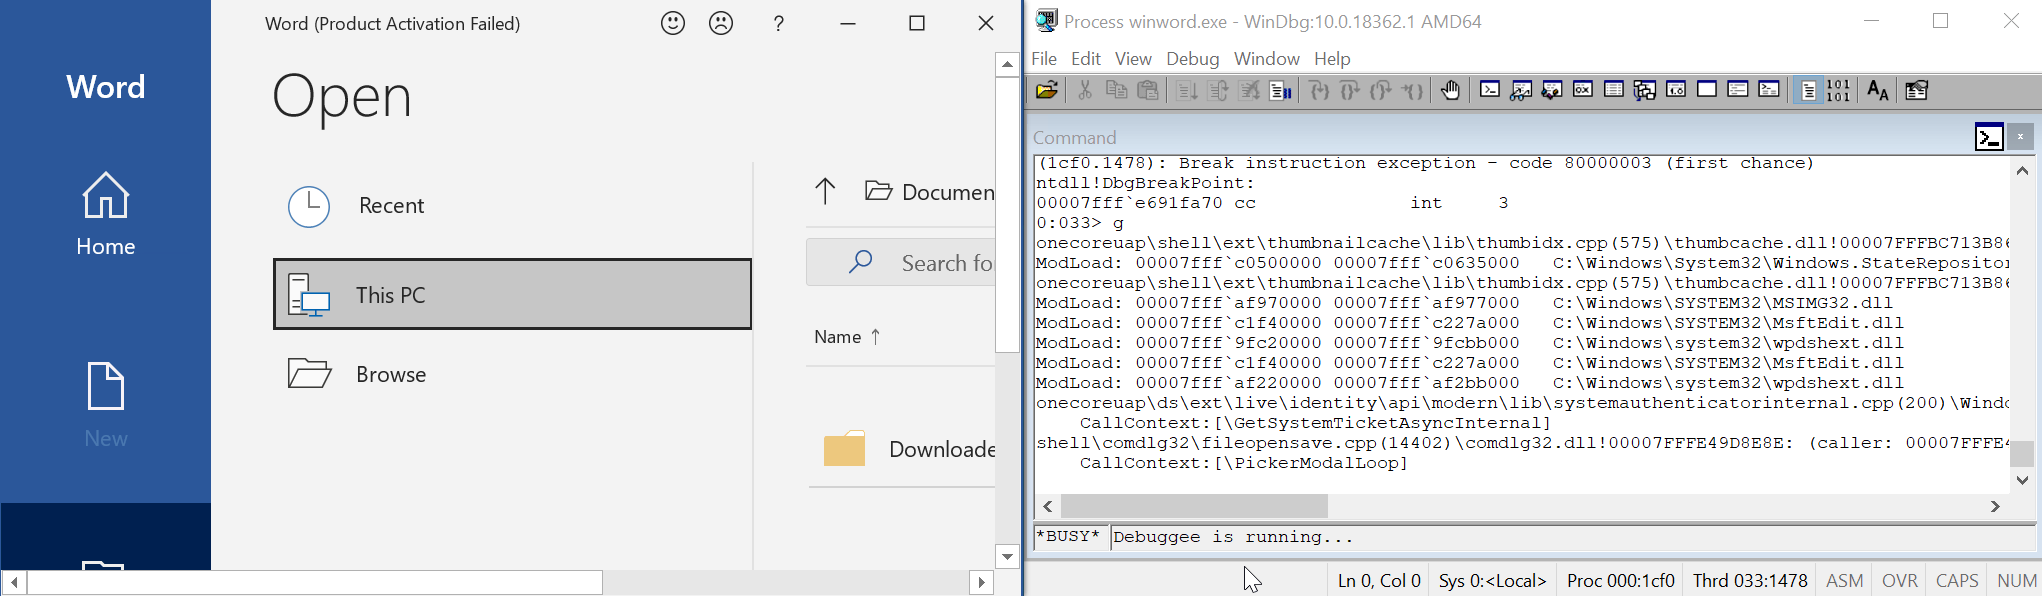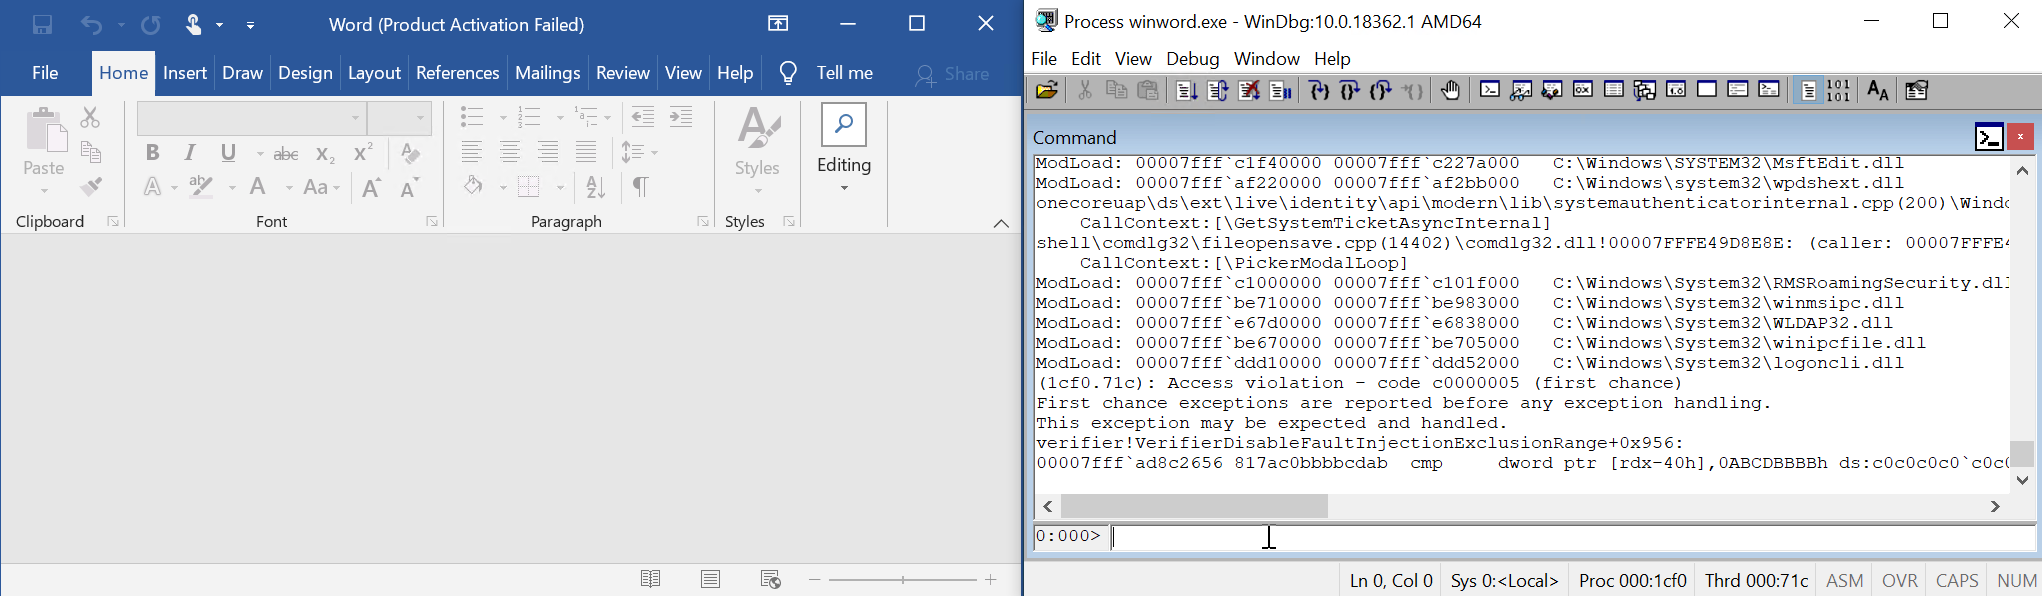
CVE-2022-21971

GitHub0vercl0k/cve-2022-21971

PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"
binary-exploitationdebuggersexploitation+3
3024 years ago
CVE-2022-21974 preview
Archived

CVE-2022-21974

GitHub0vercl0k/cve-2022-21974

PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"

binary-exploitationdebuggersexploitation+3
574 years ago
TrickDump preview

TrickDump

GitHubricardojoserf/trickdump

Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
memory-forensicspost-exploitationred-teaming
60229 days ago
apk-medit preview

apk-medit

GitHubsterrasec/apk-medit

memory search and patch tool on debuggable apk without root & ndk
android-securitybinary-analysismemory-forensics+2
4343 months ago
ipa-medit preview

ipa-medit

GitHubsterrasec/ipa-medit

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.

binary-analysisios-securitymemory-forensics+3
2091 year ago
KslKatzBof preview

KslKatzBof

GitHubprinciplecheck/kslkatzbof

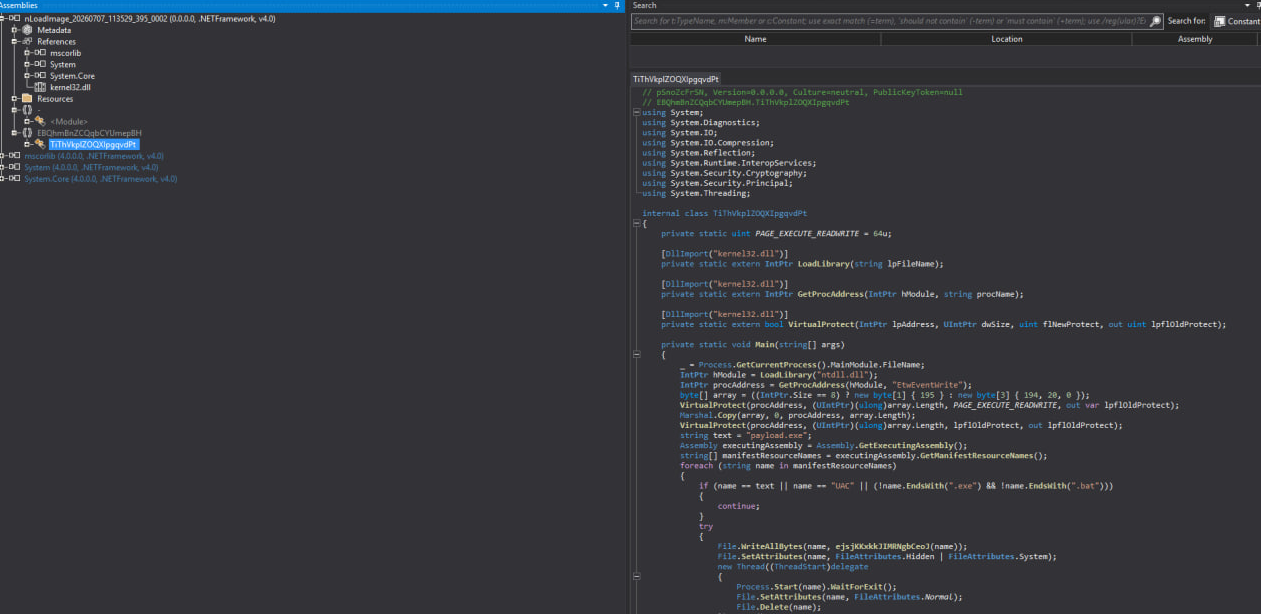
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
exploitationmemory-forensicspayload-development+4
8912 days ago
Nemesis preview

Nemesis

GitHubzypherion-technologies/nemesis

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
defensive-toolsdynamic-analysis-sandboxingmalware-analysis+2
412 months ago
page_table_walk preview

page_table_walk

GitHubjazho76/page_table_walk

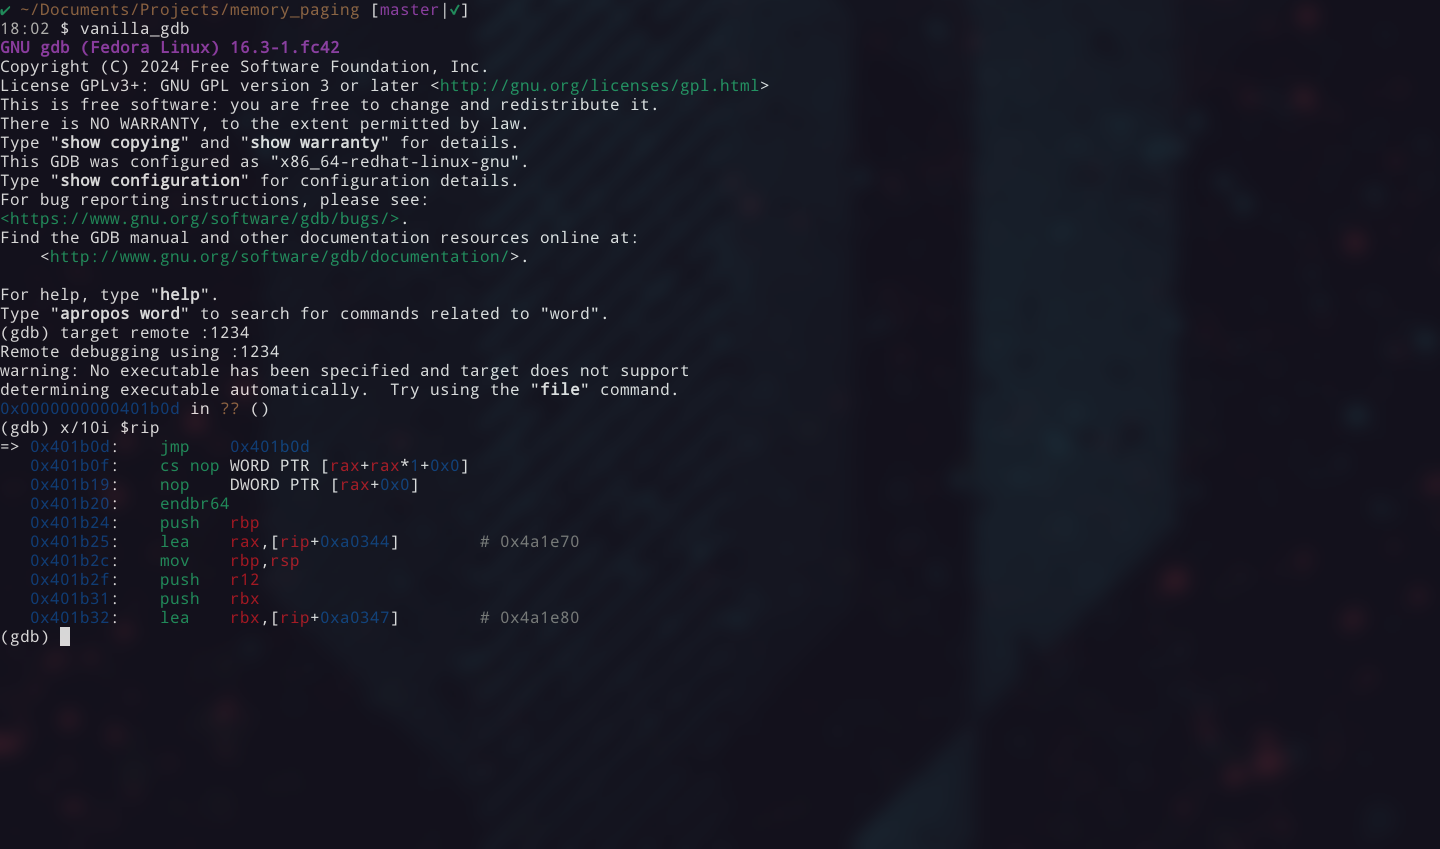
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
binary-analysisctfdebuggers+4
286 months ago
WebKit-CVE-2016-4622 preview

WebKit-CVE-2016-4622

GitHubhdbreaker/webkit-cve-2016-4622

Deep-dive analysis and exploitation walkthrough of CVE-2016-4622, a WebKit JavaScriptCore memory disclosure vulnerability via Array.slice TOCTOU race…
binary-exploitationeducationexploitation+4
231 year ago
Advanced-Loader-Reverse-Engineering preview

Advanced-Loader-Reverse-Engineering

GitHubkaandemir993/advanced-loader-reverse-engineering

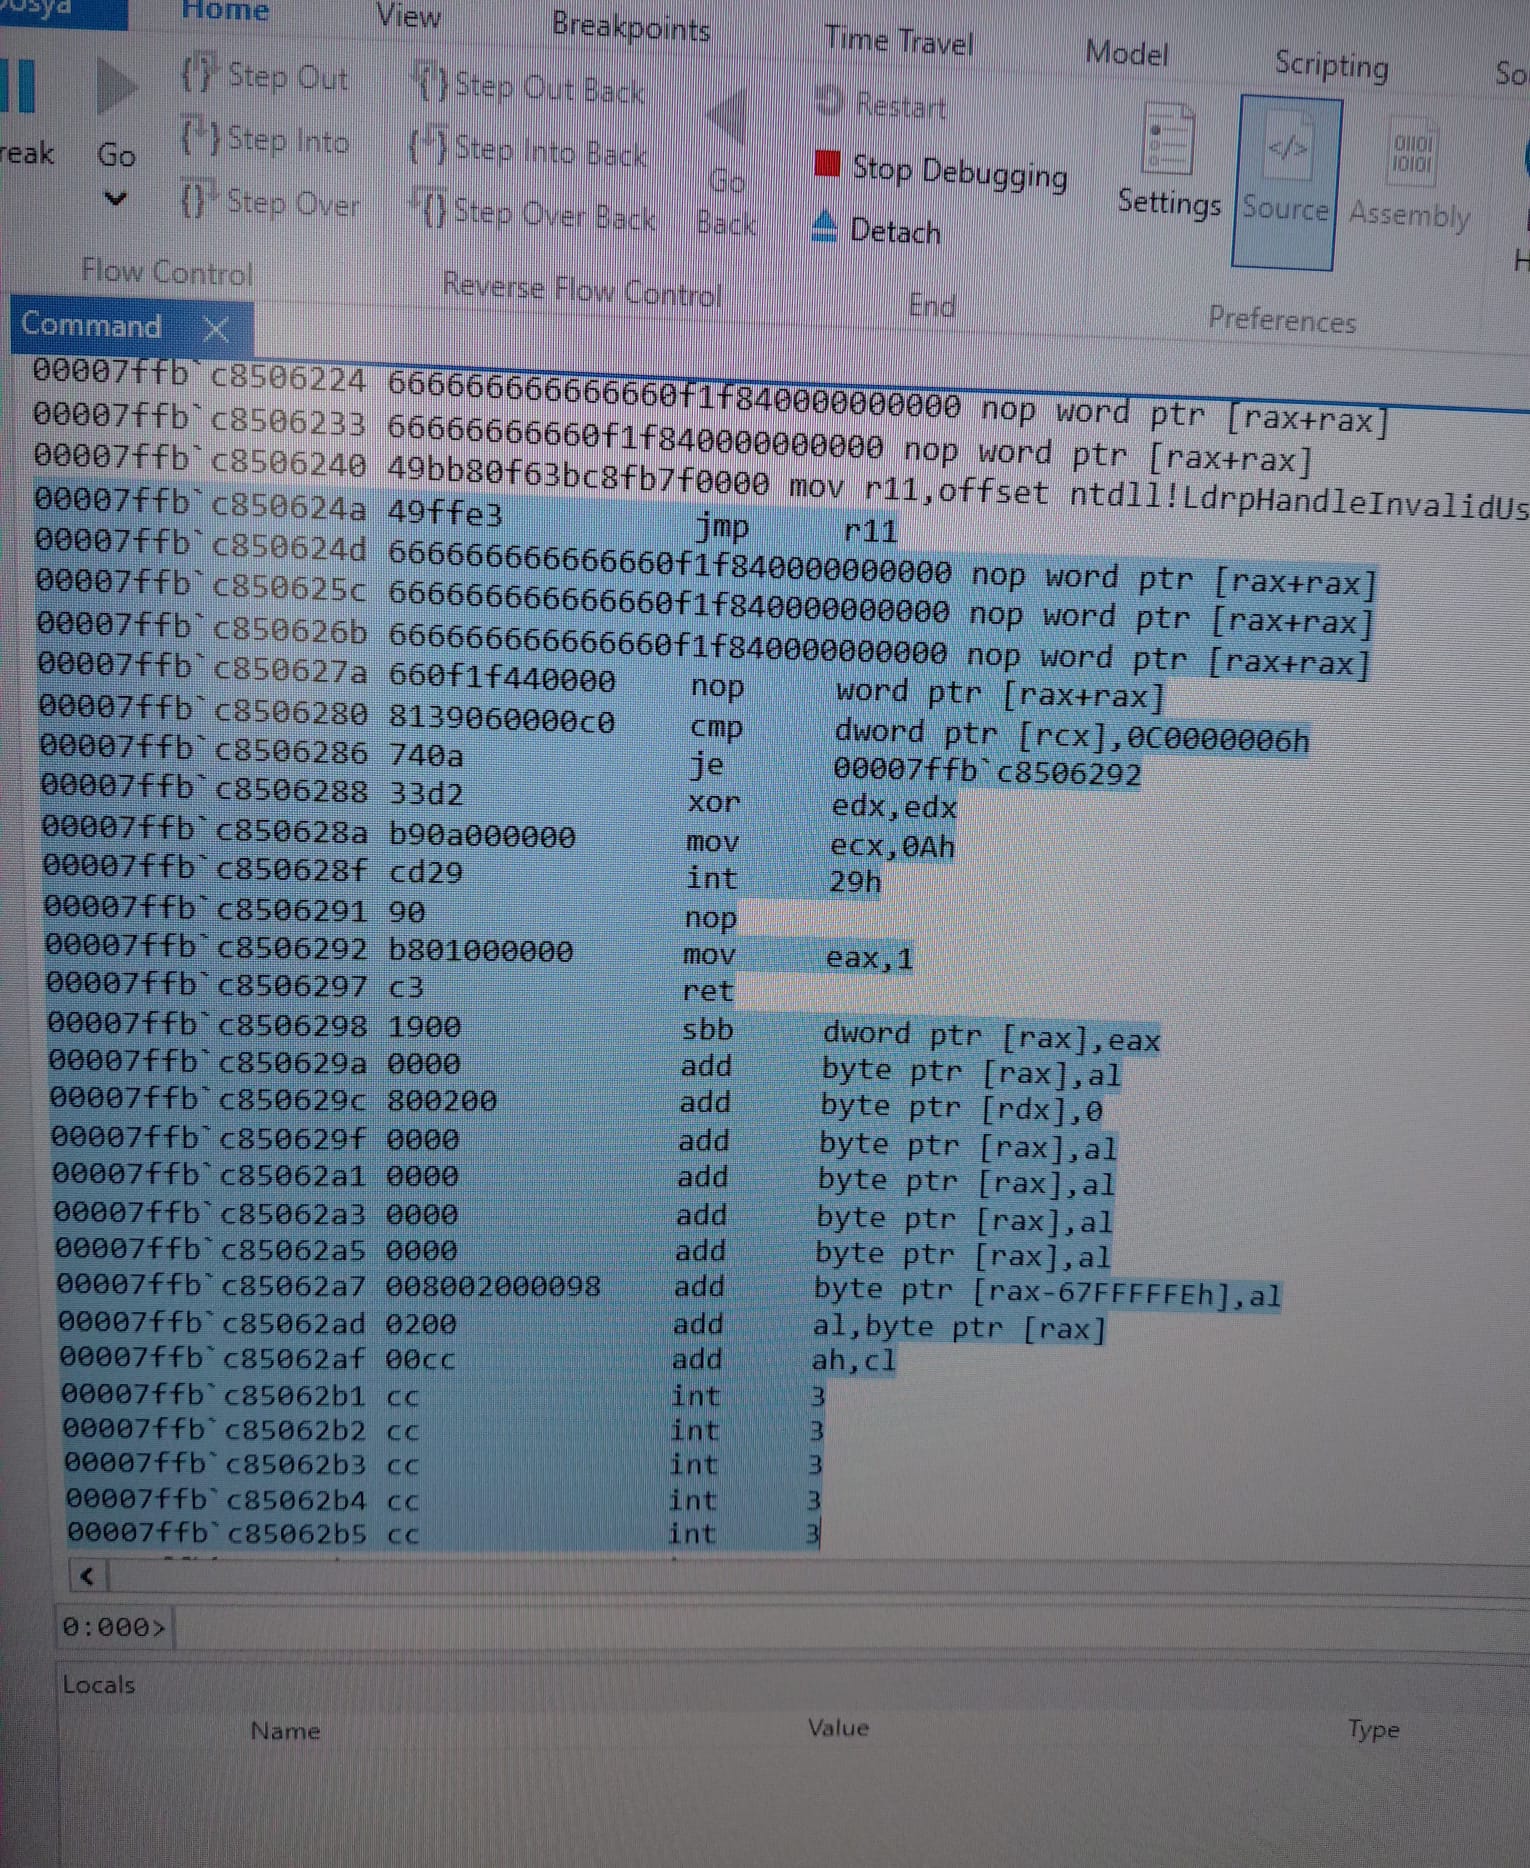
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
binary-analysiscode-analysiseducation+8
142 months ago
GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC preview

GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC

GitHubchainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc

Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.

binary-exploitationeducationexploitation+5
121 year ago
NORM-EDR preview

NORM-EDR

GitHubamberchalia/norm-edr

Experimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…
binary-analysisdefensive-toolseducation+4
116 months ago
CVE-2019-2215 preview

CVE-2019-2215

GitHubatorninja/cve-2019-2215

PoC and analysis of CVE-2019-2215, a use-after-free in Android Binder, with kernel instrumentation and exploit tuning for affected Samsung devices.
android-securitybinary-exploitationexploitation+2
46 years ago
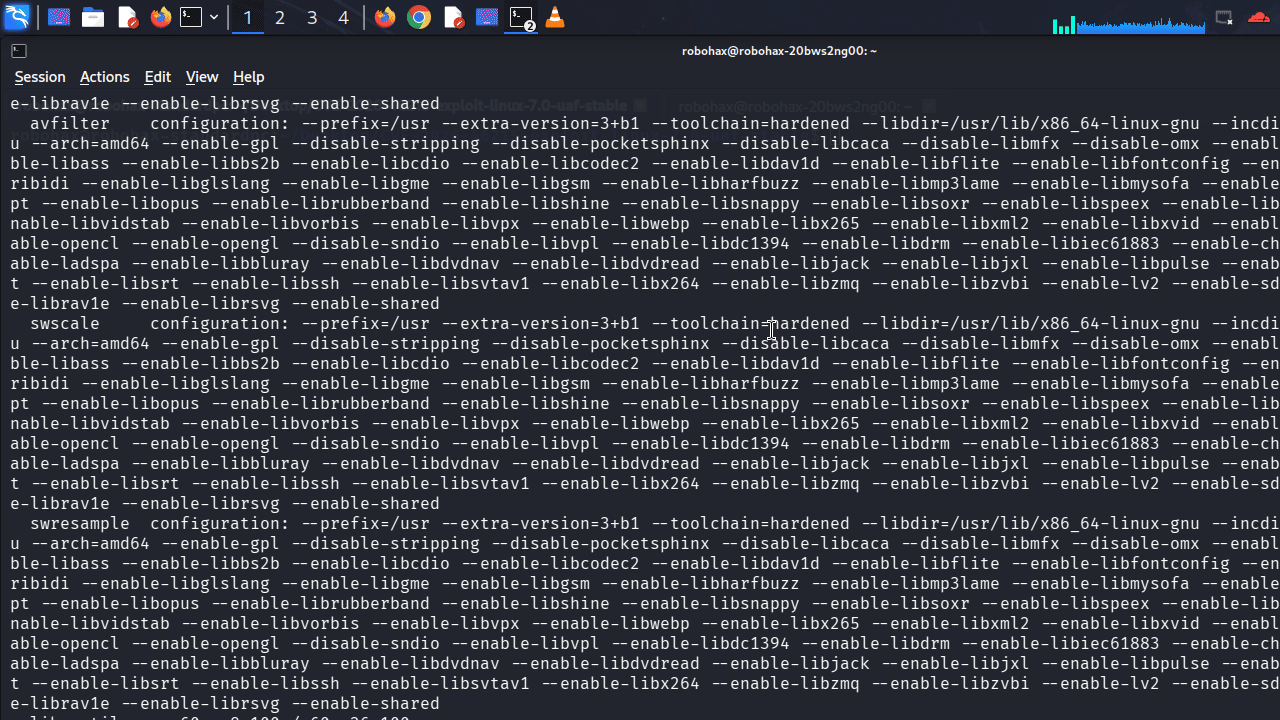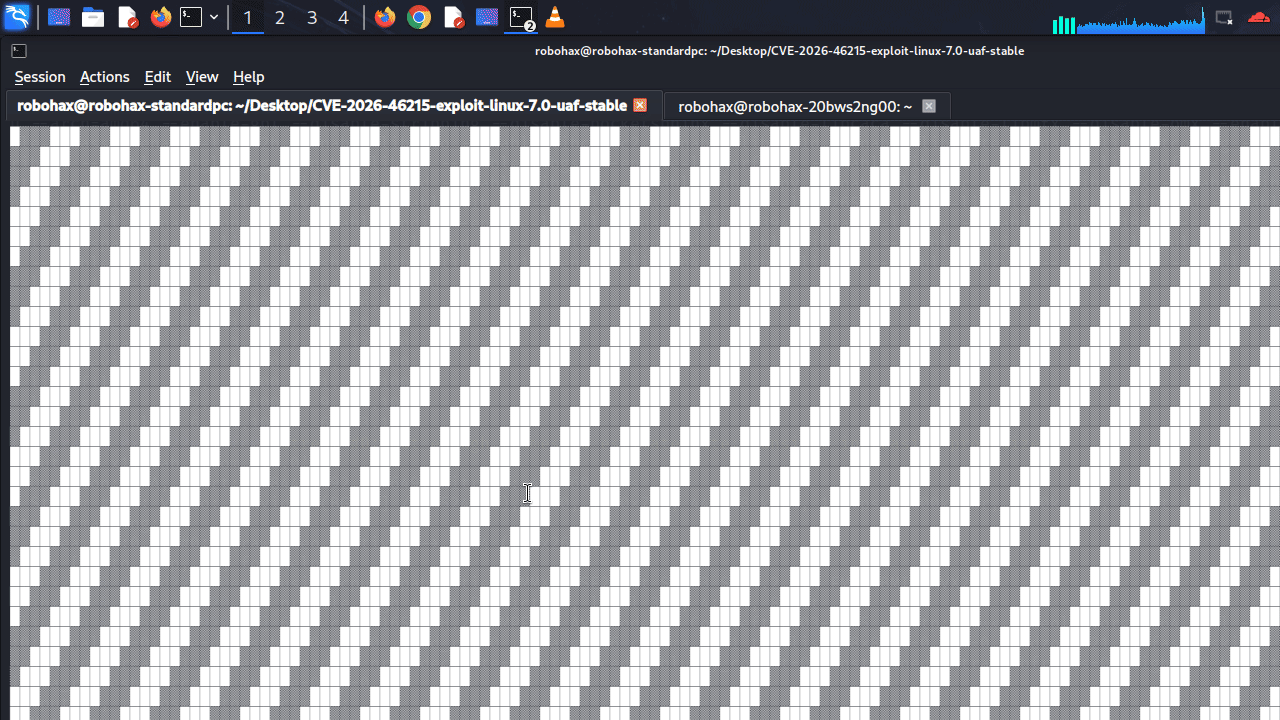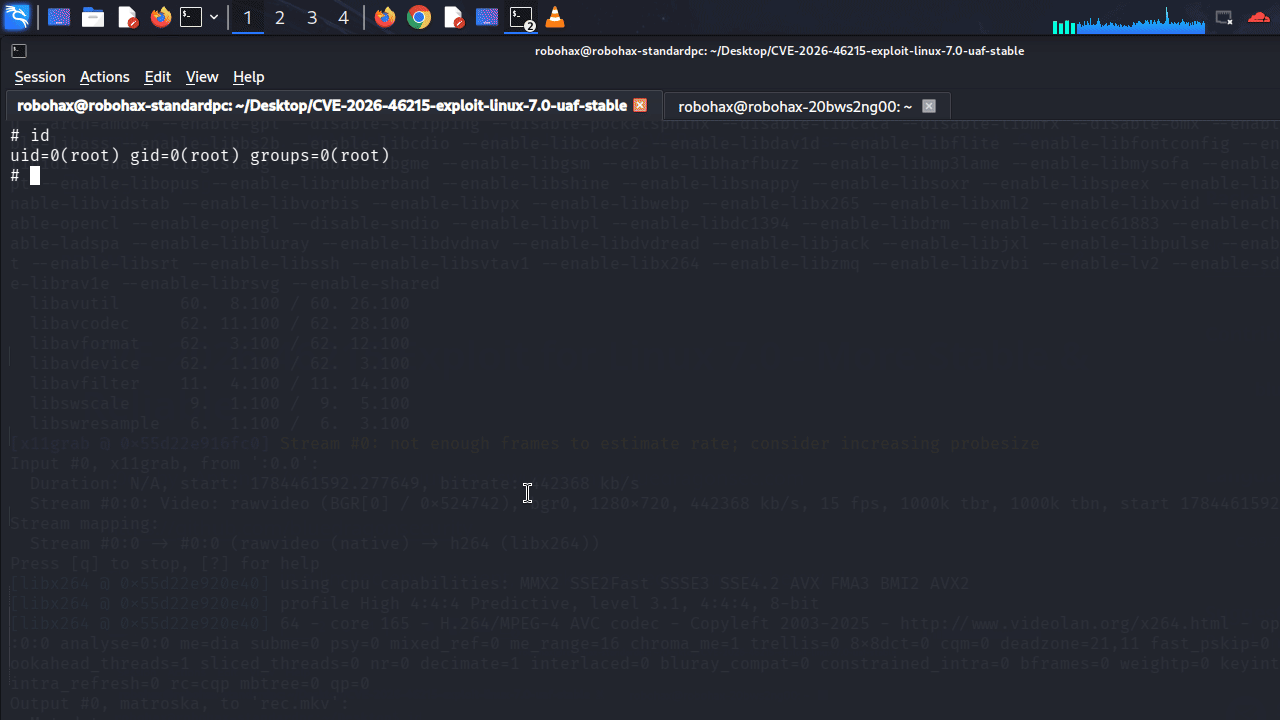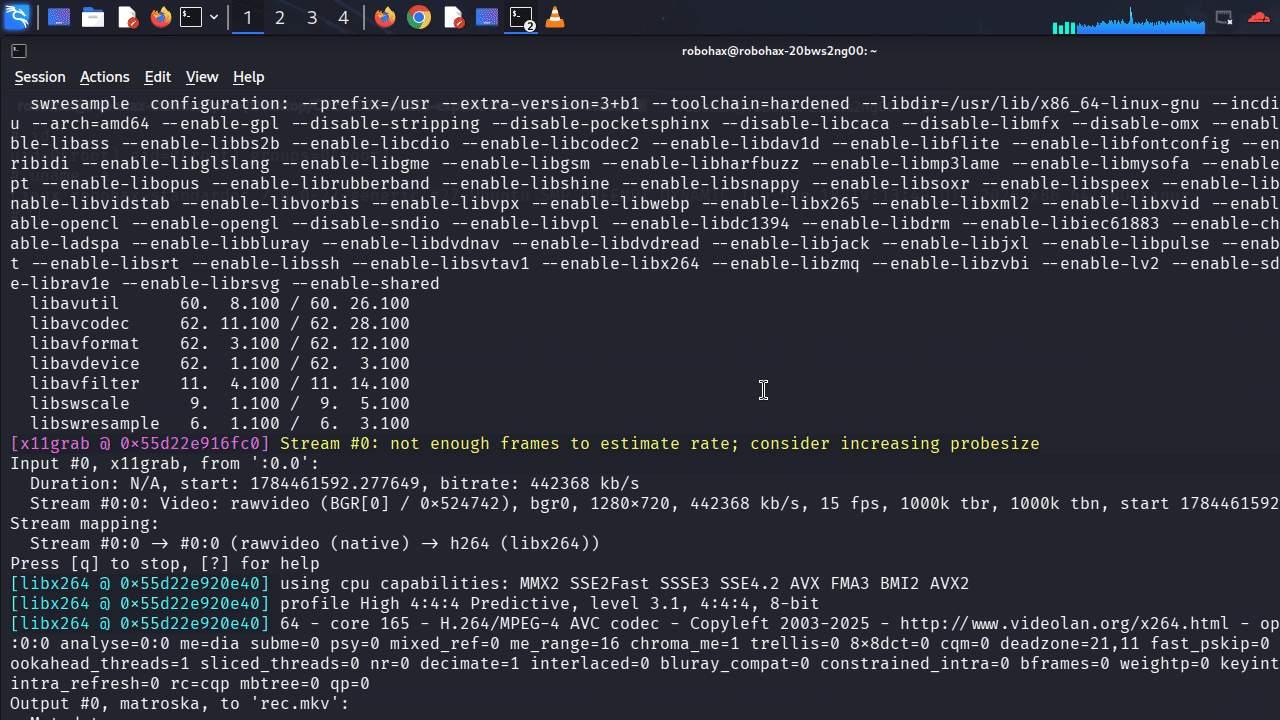
CVE-2026-46215-exploit-linux-7.0-uaf-stable preview

CVE-2026-46215-exploit-linux-7.0-uaf-stable

GitHubbluedragonsecurity/cve-2026-46215-exploit-linux-7.0-uaf-stable

CVE-2026-46215 DRM GEM UAF Exploit for Linux 7.0 - The first working PoC for linux kernel 7 use after free- by Antonius (sw0rdm4n, w1sdom, ev1lut10n)

binary-exploitationexploitationmemory-forensics+2
51 month ago
ImageMagick-CVE-2017-15277 preview

ImageMagick-CVE-2017-15277

GitHubhexrom/imagemagick-cve-2017-15277

Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.

binary-analysisexploitationfuzzing+2
56 years ago
Previous1…131415…21Next