
CVE-2026-2005
 var77/cve-2026-2005
PoC for CVE-2026-2005
binary-exploitationdatabase-securityeducation+4
274 months ago
var77/cve-2026-2005PoC for CVE-2026-2005
 encrypter15/cve-2025-30400
Educational Python model demonstrating a Use-After-Free (UAF) privilege escalation vulnerability inspired by CVE-2025-30400 in Windows DWM. Simulates…
 jordelmir/elysium-vanguard-sentinel-audit
The official Sentinel Edition v7.11 - Hypervisor Detection & Kernel Memory Audit Suite for Honor Magic V2. Investigating CVE-2025-38352 and EL2 RKP…
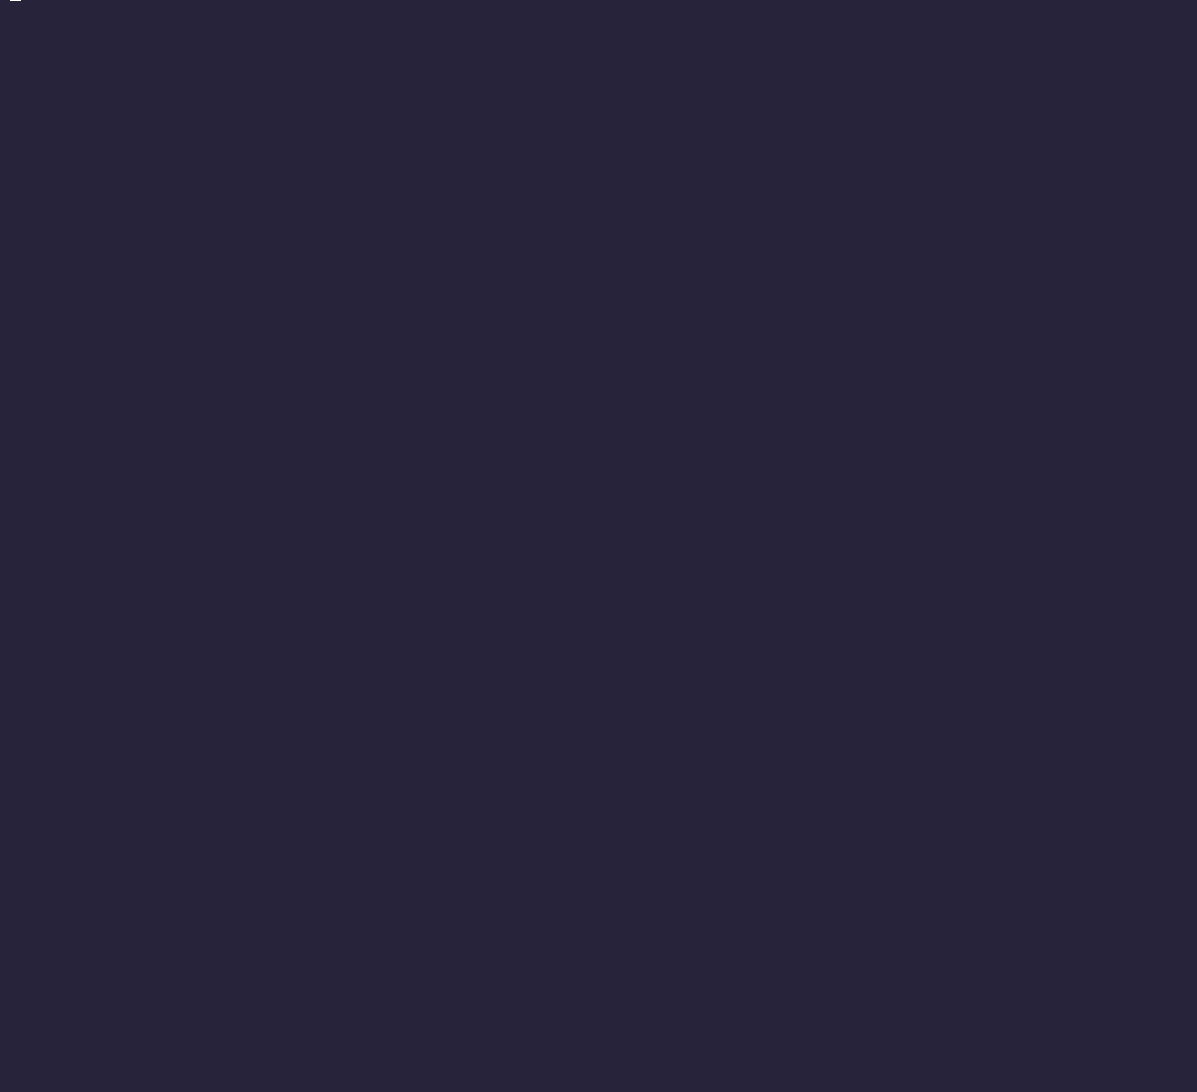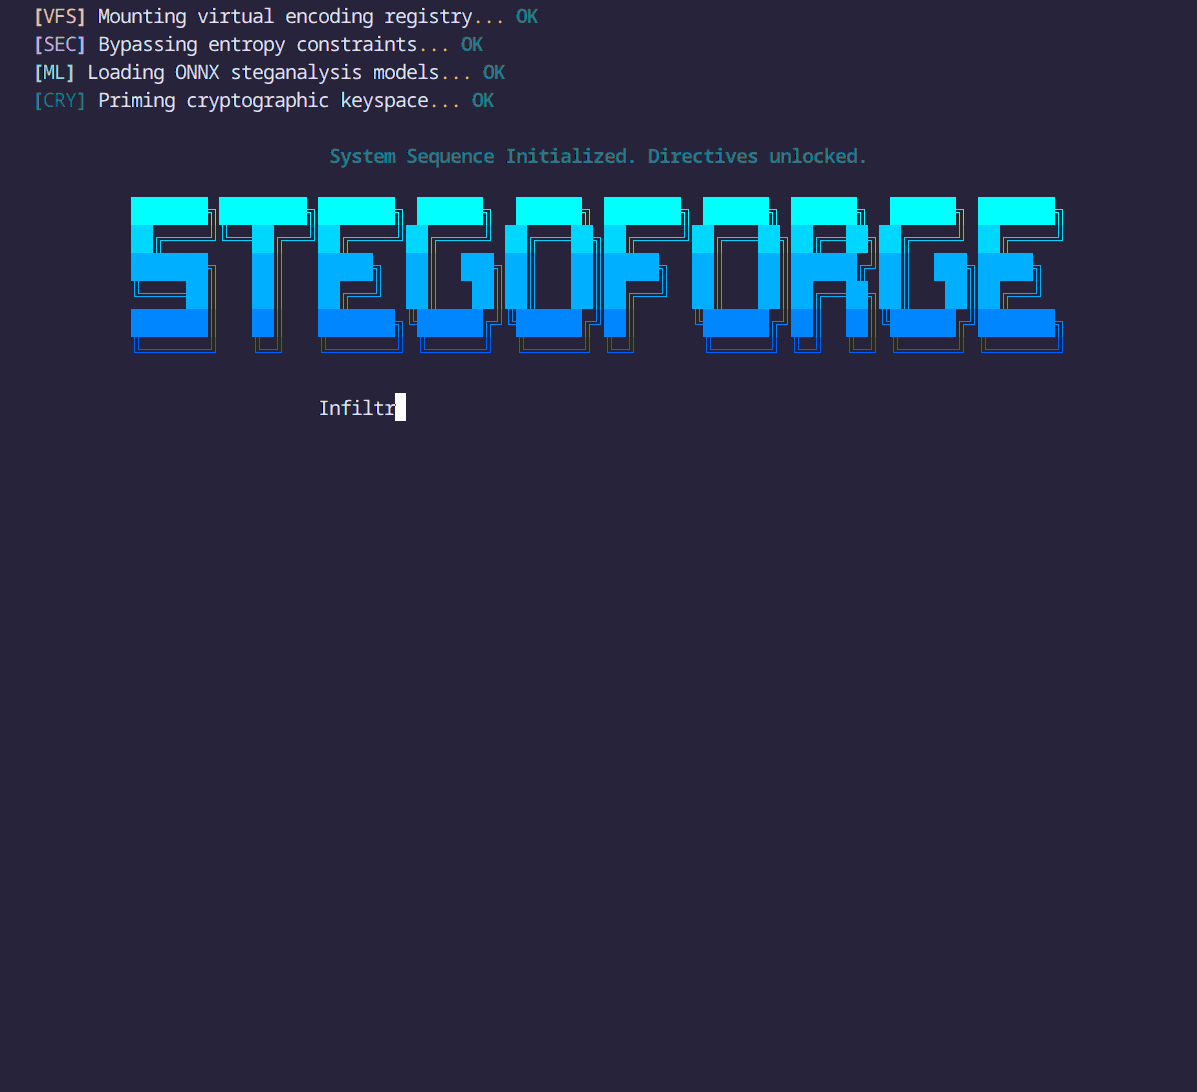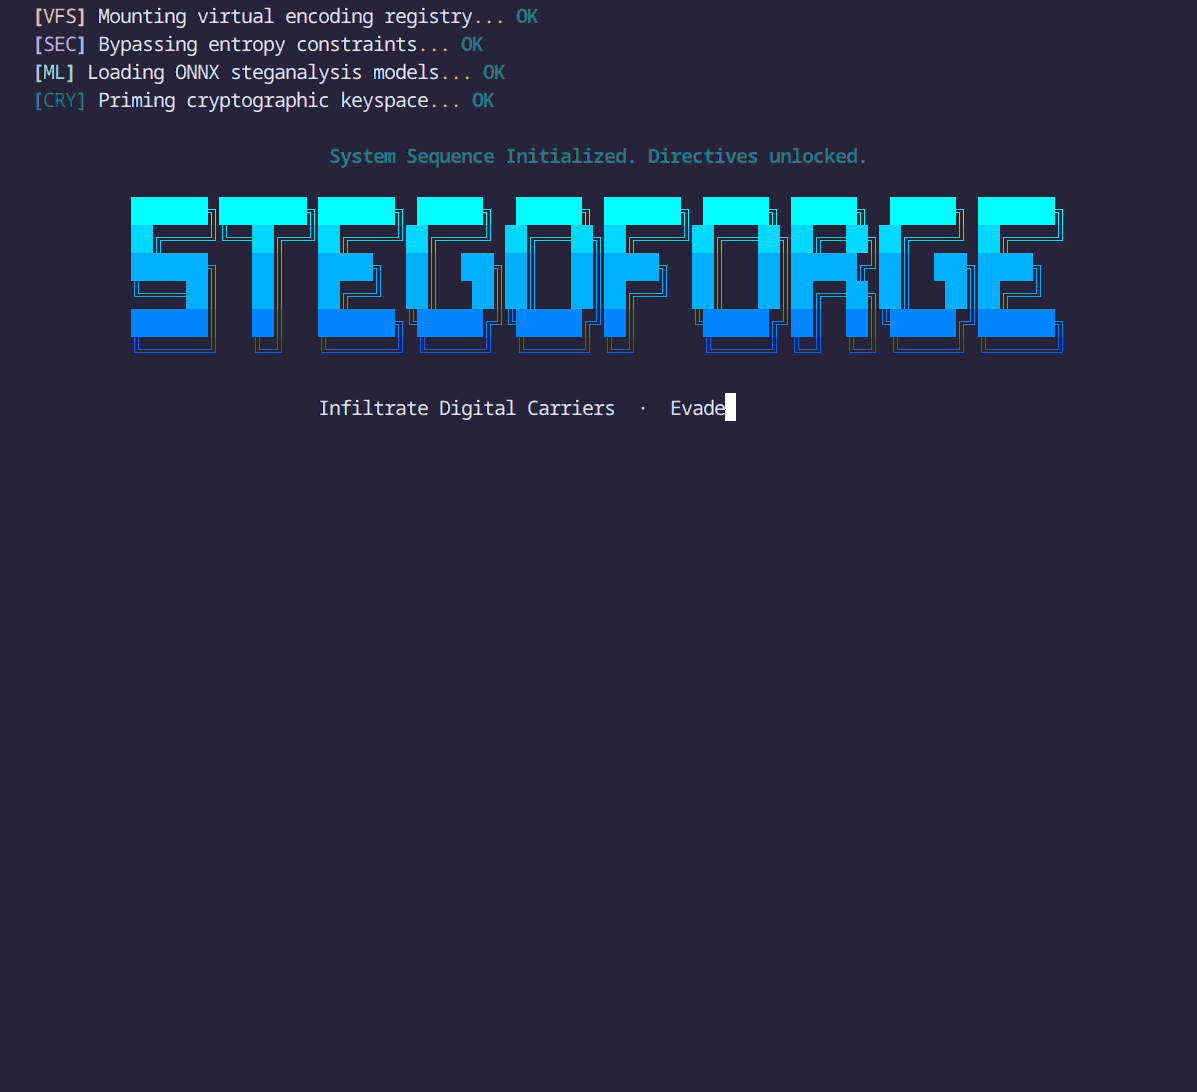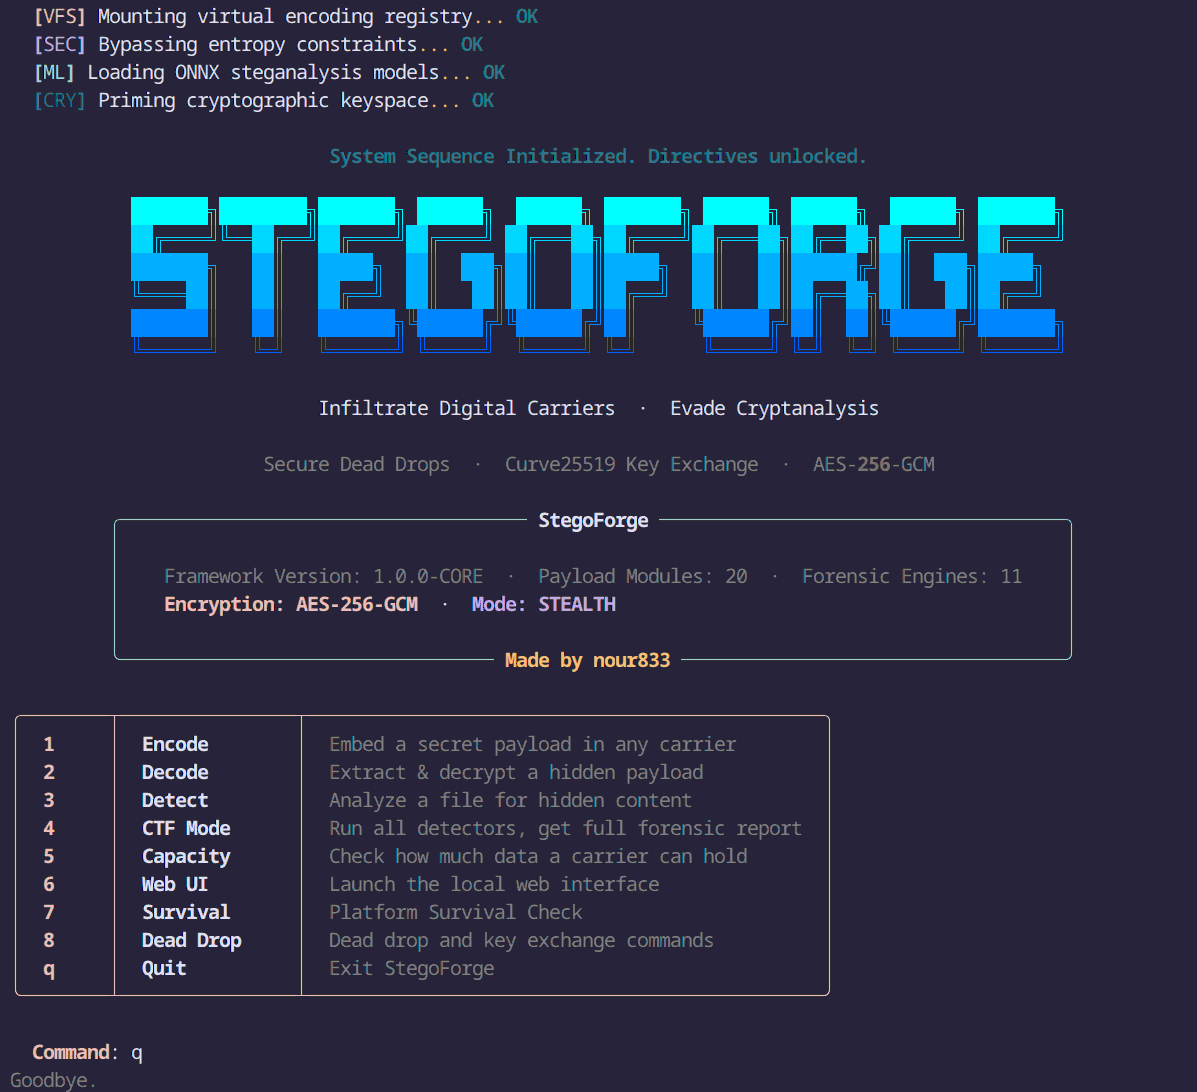 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
 0xcyberstan/cve-2026-46215-poc
Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…
 argp/cve-2011-3026-firefox
Example of exploiting CVE-2011-3026 on Firefox (Linux/x86)
 maherazzouzi/cve-2024-26817-amdkfd
Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
 0neday/multi_path
CVE-2018-4241: XNU kernel heap overflow due to bad bounds checking in MPTCP for iOS 11 - 11.3.1released by Ian Beer
 ox1111/cve-2022-32932
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 tamirzb/cve-2017-13253
PoC code for CVE-2017-13253
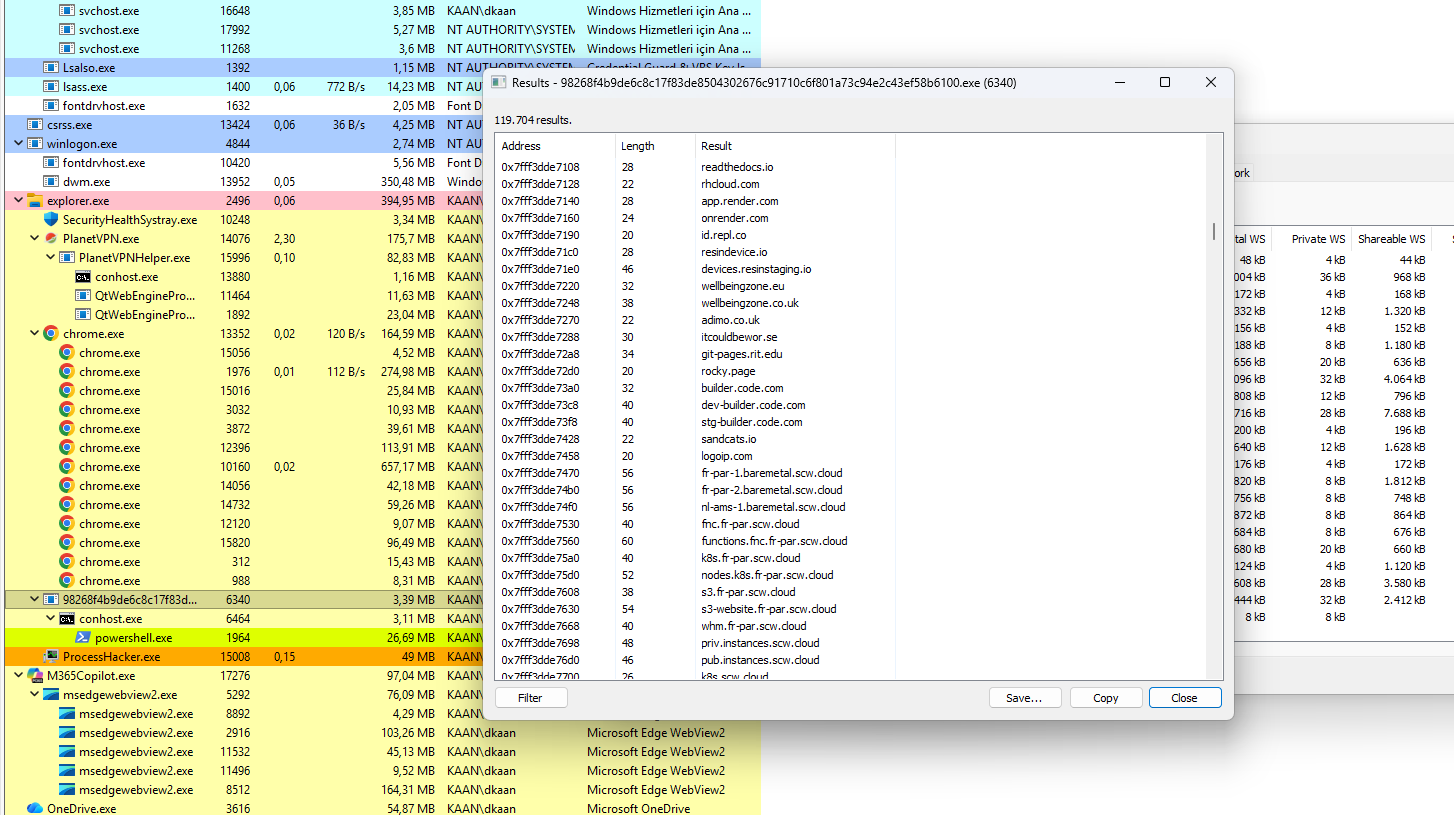 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…