Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
ghidra preview

ghidra

GitHubnationalsecurityagency/ghidra

Ghidra is a software reverse engineering (SRE) framework

ai-assisted-reversingandroid-securitybinary-analysis+17
80.7k
5 days ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.7k7 days ago
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.7k9 days ago
GoTEE-example preview

GoTEE-example

GitHubusbarmory/gotee-example

GoTEE - example application
debuggersembedded-systems-securityhardware-security+2
1711 days ago
CVE-2026-50416-writeup-and-poc preview

CVE-2026-50416-writeup-and-poc

GitHubkarollooool/cve-2026-50416-writeup-and-poc

CVE-2026-50416: Windows 11 KASLR bypass
binary-analysisctfeducation+7
471 month ago
libheif-cve-2026-50142 preview

libheif-cve-2026-50142

GitHubmuhammedhussein17/libheif-cve-2026-50142

CVE-2026-50142 — Heap allocation vulnerability in libheif HEIF sequence parser
binary-analysiseducationexploitation+3
4 months ago
PSI_BOF preview

PSI_BOF

GitHubwhokilleddb/psi_bof

A BOF designed to inspect processes memory and addresses
binary-analysisdebuggersmemory-forensics+4
415 months ago
NORM-EDR preview

NORM-EDR

GitHubamberchalia/norm-edr

Experimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…
binary-analysisdefensive-toolseducation+4
117 months ago
full-poc-CVE-2025_21298 preview

full-poc-CVE-2025_21298

GitHubfy-poc/full-poc-cve-2025_21298

Complete analysis of CVE-2025-21298, a double free vulnerability related to ole32 library in windows.
binary-exploitationeducationexploitation+3
11 year ago
libunwind_CVE-2015-3239_After preview

libunwind_CVE-2015-3239_After

GitHubrenukaselvar/libunwind_cve-2015-3239_after

Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.

binary-analysisdebuggersexploitation+3
1 year ago
libunwind_CVE-2015-3239 preview

libunwind_CVE-2015-3239

GitHubrenukaselvar/libunwind_cve-2015-3239

C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…

binary-analysisdebuggersexploitation+3
1 year ago
Malware-analysis-and-Reverse-engineering preview

Malware-analysis-and-Reverse-engineering

GitHubdump-guy/malware-analysis-and-reverse-engineering

Some of my publicly available Malware analysis and Reverse engineering.
binary-analysisctfcurated-resources+8
9632 years ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
3242 years ago
ReClass.NET preview

ReClass.NET

GitHubreclassnet/reclass.net

More than a ReClass port to the .NET platform.

binary-analysiscode-analysisdebuggers+4
2.2k3 years ago
DMA-ProcessDumper preview

DMA-ProcessDumper

GitHubgmh5225/dma-processdumper

Simple Process Dumper using DMA over a PCIe FPGA device
data-exfiltrationforensicshardware-hacking+3
4 years ago
dismember preview

dismember

GitHubliamg/dismember

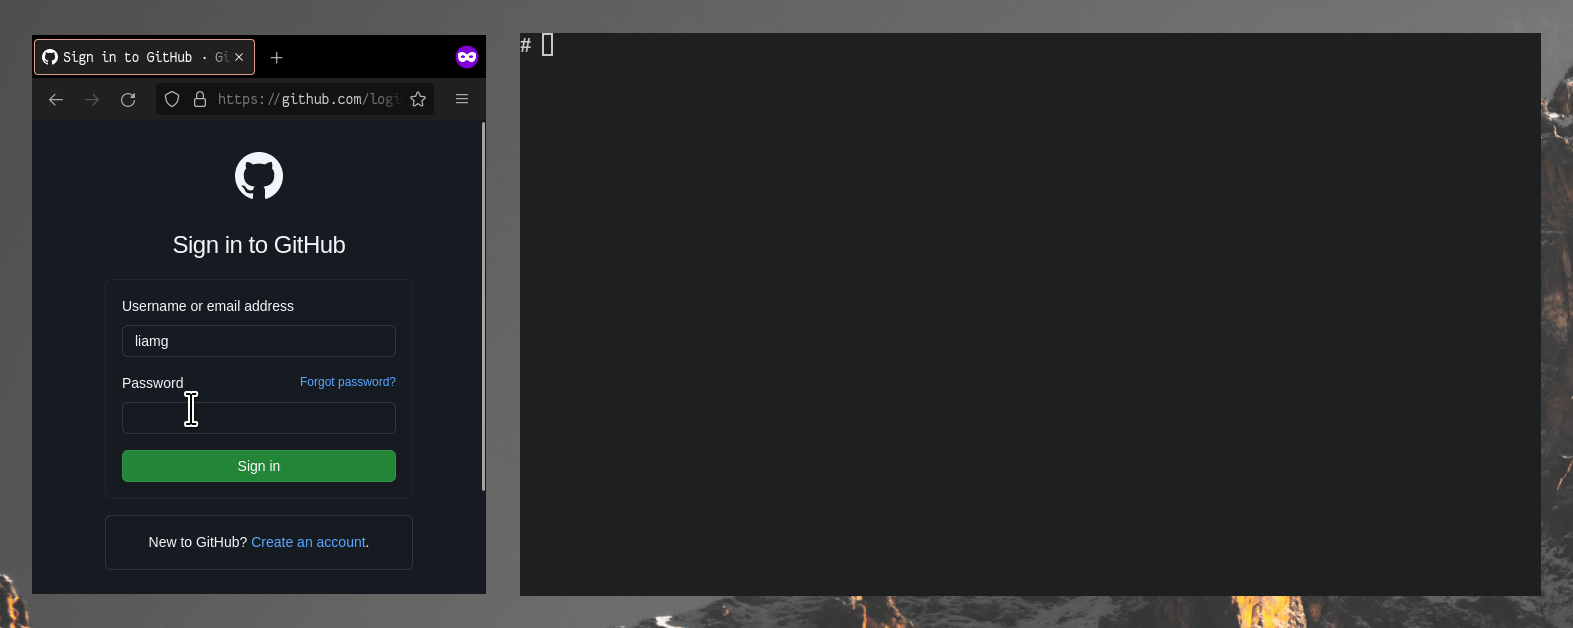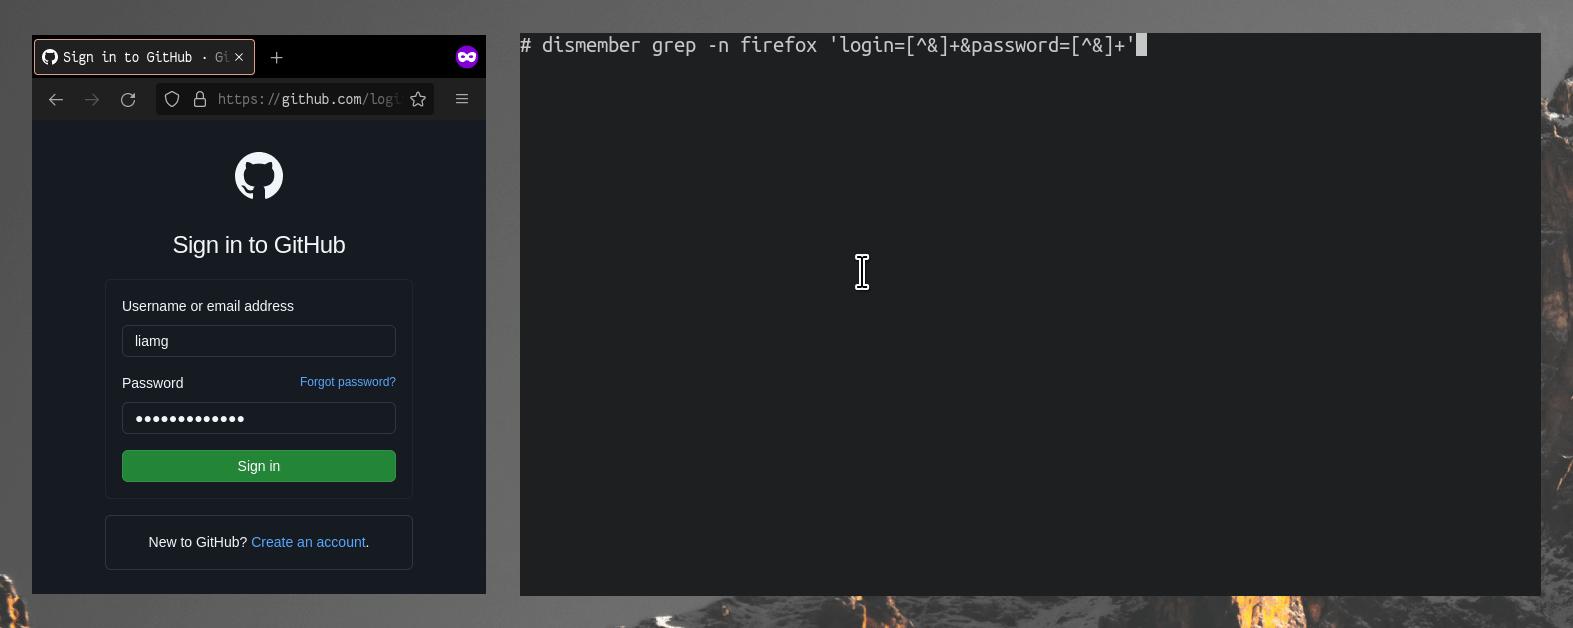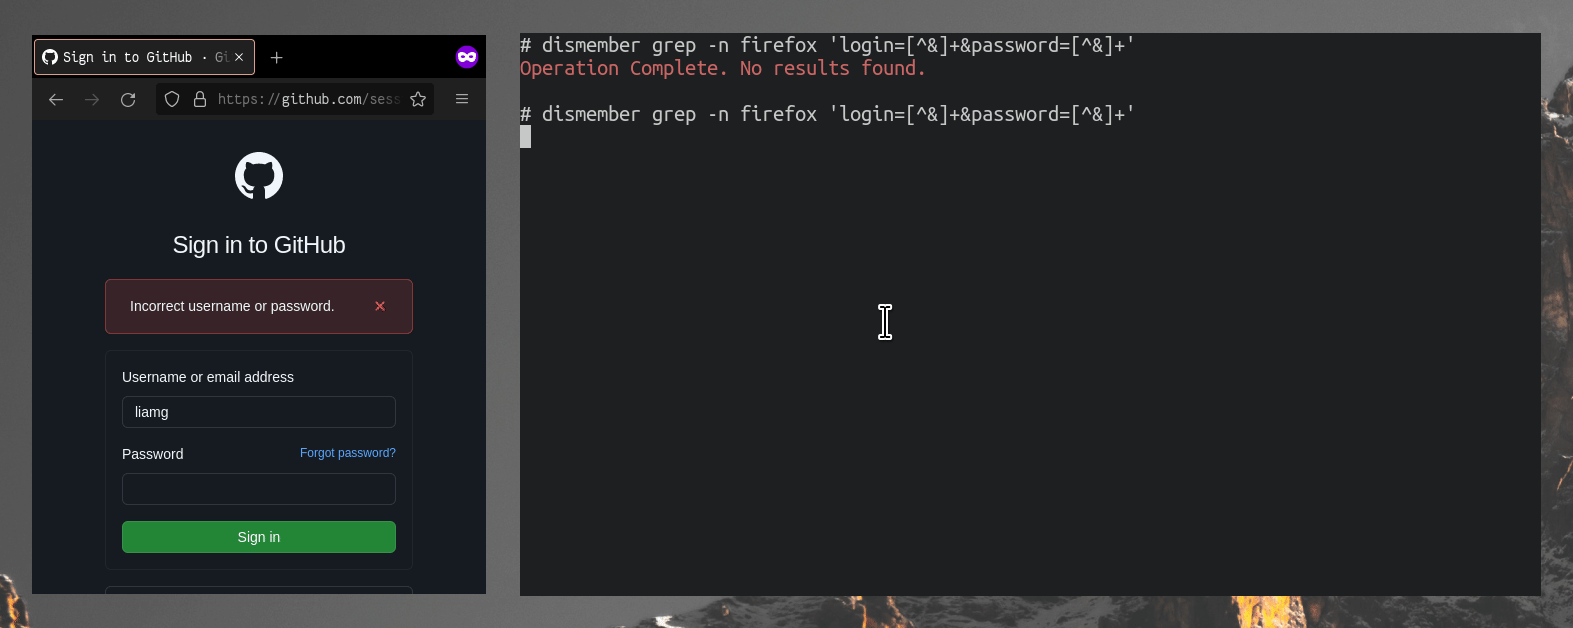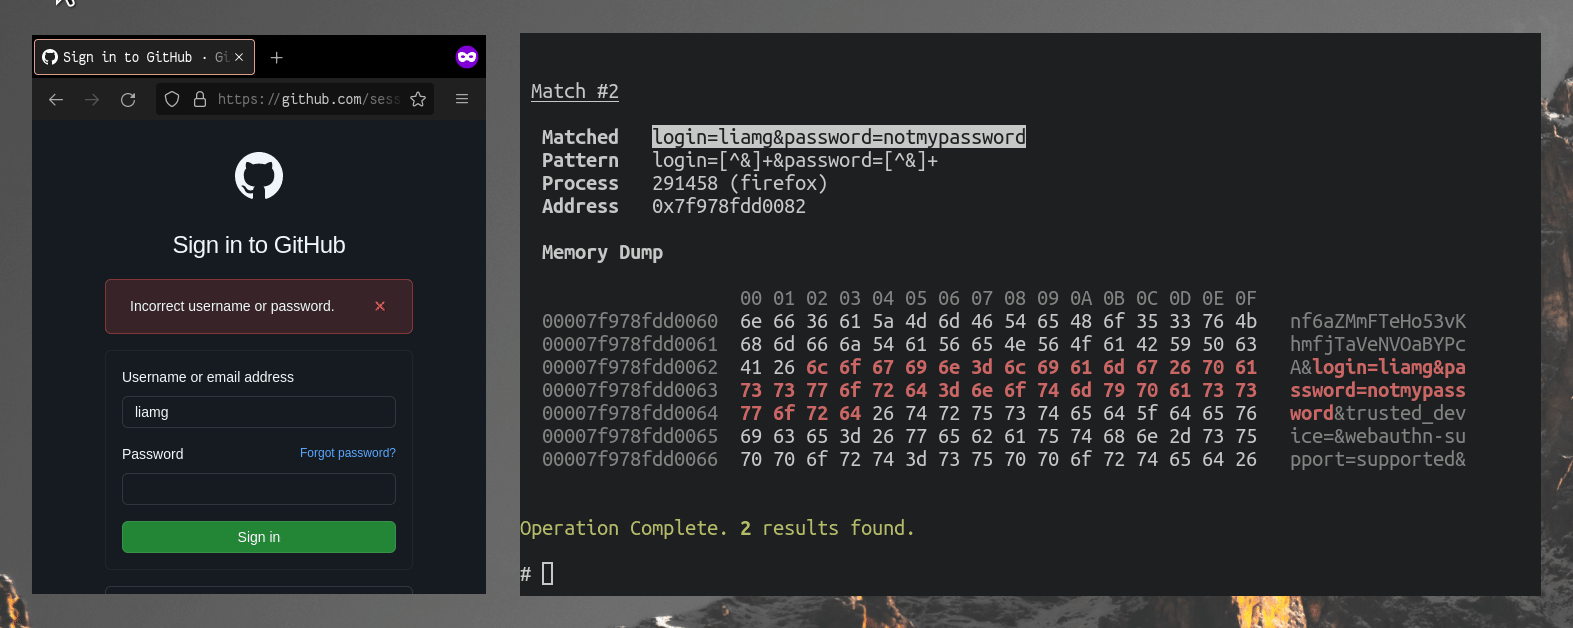
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
ctfforensicsinformation-gathering+2
6744 years ago
rekall preview
Archived

rekall

GitHubgoogle/rekall

Rekall Memory Forensic Framework

digital-forensicsforensicsincident-response+3
2.0k5 years ago
gsscred-move-uaf preview

gsscred-move-uaf

GitHubbazad/gsscred-move-uaf

CVE-2018-4343: Proof-of-concept for a use-after-free in the GSSCred daemon on macOS and iOS.

binary-exploitationexploitationios-security+2
78 years ago
Previous12Next