

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
164 results
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
24.9k16h 9m ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 day ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .

binary-analysisdebuggerseducation+3
2222 days ago
pwndbg preview

pwndbg

GitHubpwndbg/pwndbg

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
11.0k2 days ago
RootMyVivo-Exploit preview

RootMyVivo-Exploit

GitHubzenyxx-xd/rootmyvivo-exploit

GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.

android-securitybinary-exploitationexploitation+5
12 days ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k2 days ago
ghidra preview

ghidra

GitHubnationalsecurityagency/ghidra

Ghidra is a software reverse engineering (SRE) framework

ai-assisted-reversingandroid-securitybinary-analysis+17
80.5k4 days ago
CVE-2026-43805-PoC preview

CVE-2026-43805-PoC

GitHubtls456/cve-2026-43805-poc

CVE-2026-43805 IOKit IODMACommand race analysis and proof of concept
binary-analysisexploitationios-security+5
6 days ago
umbra preview

umbra

GitHubymsniper/umbra

External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…

exploitationmemory-forensicsred-teaming+1
168 days ago
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
embedded-systems-securitymemory-forensicsmobile-forensics+4
1.7k8 days ago
honor-6.12.38-43499-research preview

honor-6.12.38-43499-research

GitHubpyyyc/honor-6.12.38-43499-research

Research repository documenting exploitation attempts of CVE-2026-43499 futex UAF on Honor YLP-W00 kernel 6.12.38, including PoC sources, kernel…
android-securitybinary-exploitationexploitation+5
10 days ago
cve-2023-6931-pipa preview

cve-2023-6931-pipa

GitHubyutori-natsu/cve-2023-6931-pipa

Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
android-securitybinary-exploitationexploitation+6
11 days ago
streambox-cve-2026-28618 preview

streambox-cve-2026-28618

GitHubraafatabualazm/streambox-cve-2026-28618

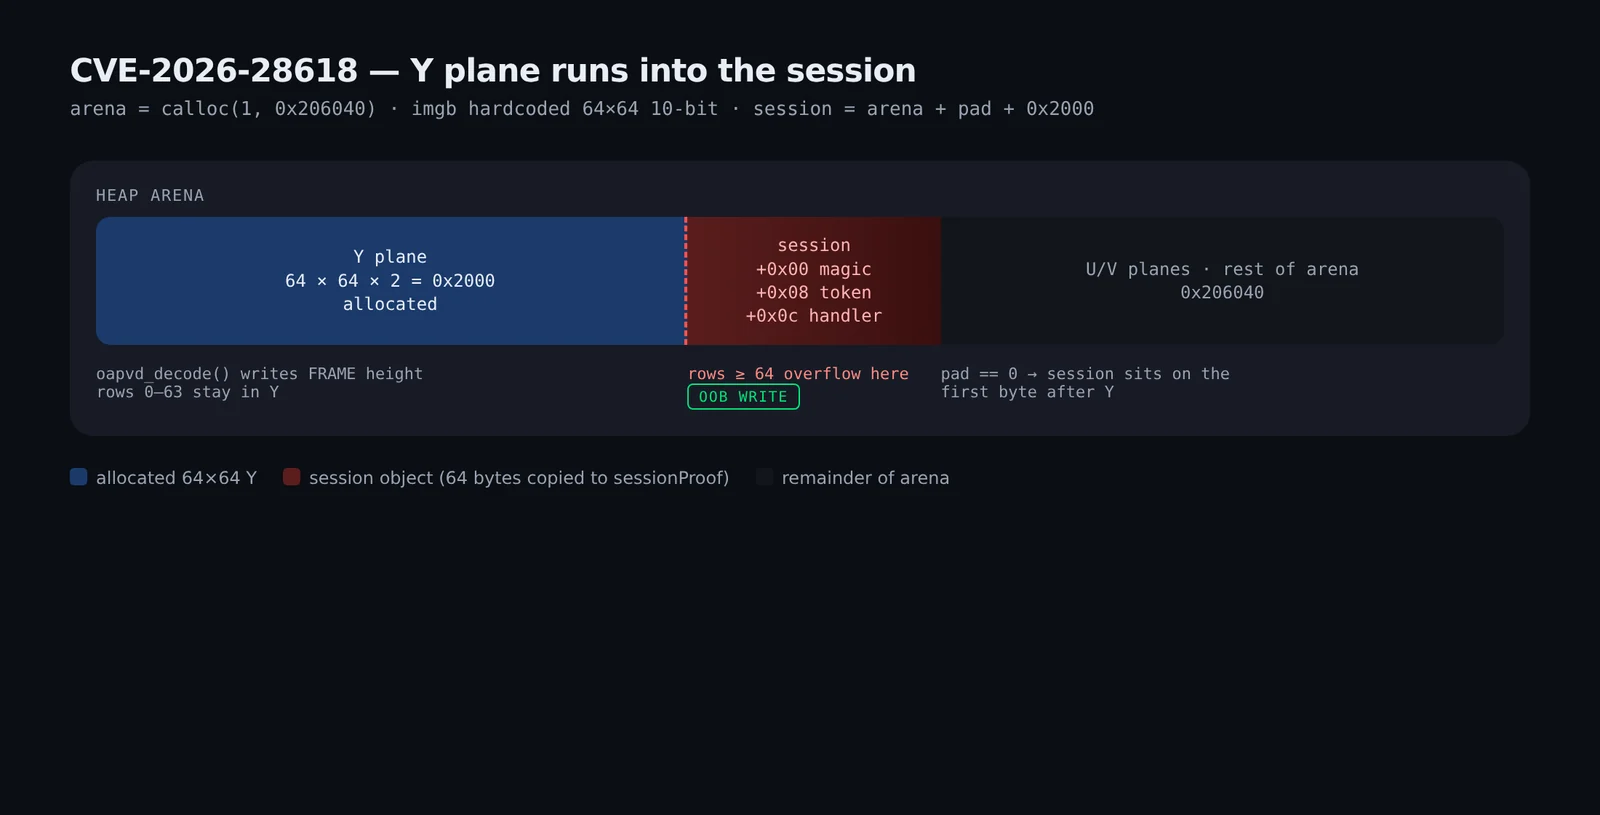
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
android-securitybinary-exploitationeducation+6
12 days ago
CVE-2026-28609-matroska-pcm-oob preview

CVE-2026-28609-matroska-pcm-oob

GitHubdevrodt2/cve-2026-28609-matroska-pcm-oob

Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
android-securitybinary-exploitationexploitation+5
612 days ago
apk-medit preview

apk-medit

GitHubsterrasec/apk-medit

memory search and patch tool on debuggable apk without root & ndk
android-securitybinary-analysismemory-forensics+2
43413 days ago
ghostlock-pfem10 preview

ghostlock-pfem10

GitHubimeiplus/ghostlock-pfem10

GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering
android-securitybinary-exploitationexploitation+6
16 days ago
PPPoEject preview

PPPoEject

GitHubmanizada/pppoeject

Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
binary-exploitationexploitationmemory-forensics+4
816 days ago
zenfone9-root preview

zenfone9-root

GitHubramenfast/zenfone9-root

Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.

android-securitybinary-exploitationexploitation+7
316 days ago
Previous12…10Next