


 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
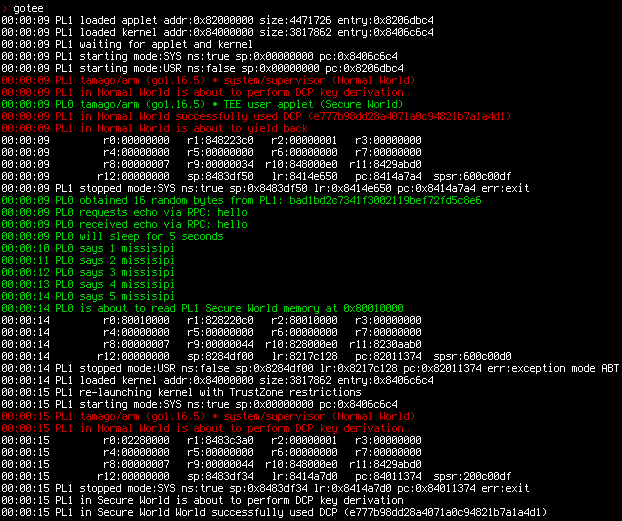 usbarmory/gotee-example
GoTEE - example application
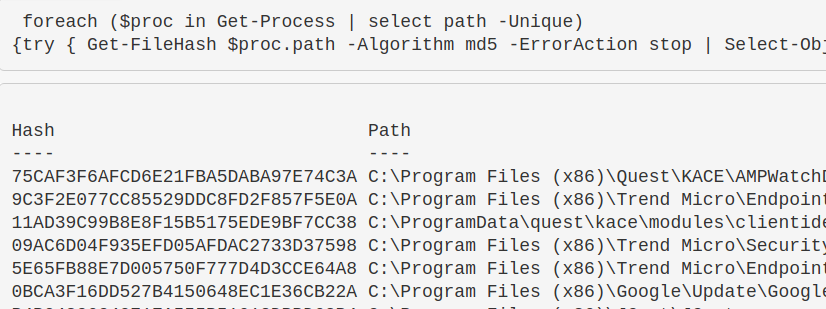 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 antisurveillanceagency/shadownet
ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
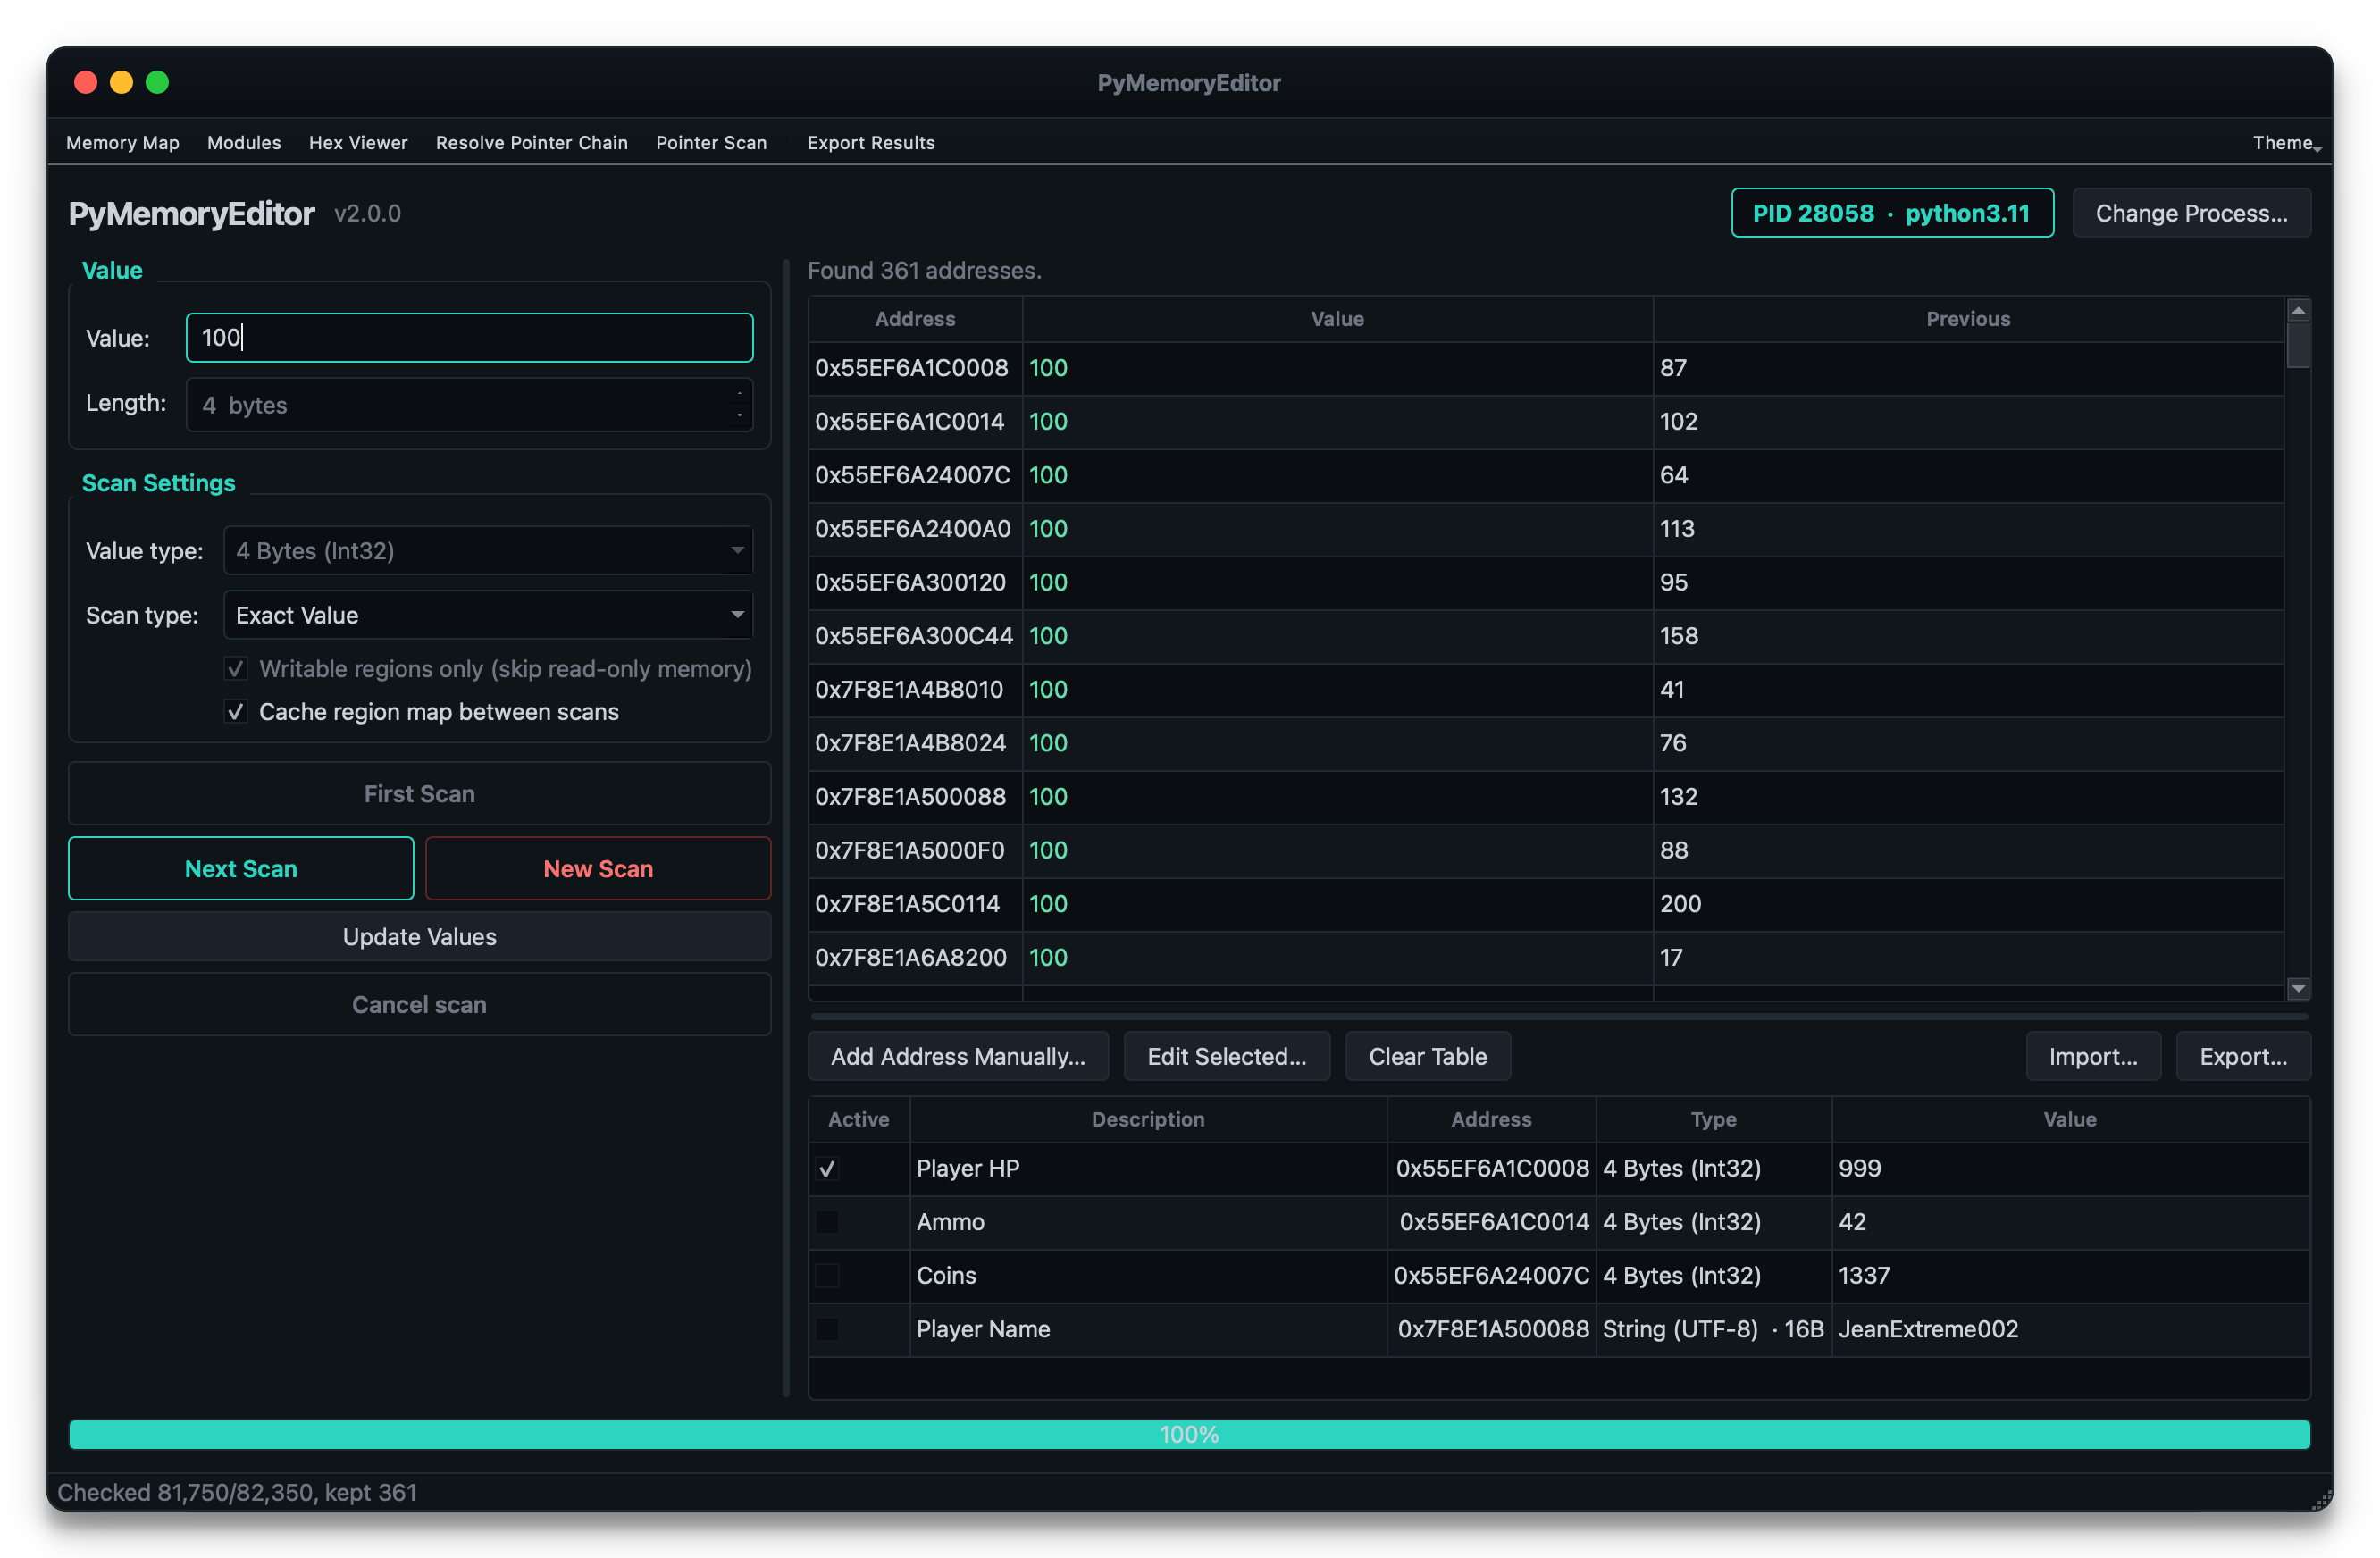 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 sneakynachos/cve-2026-84118-who-labeled-the-crit-as-a-high
Proof-of-concept for CVE-2026-84118, a SpiderMonkey GC use-after-free leading to out-of-bounds read/write and potential code execution. Includes…
 lsinus/cachemeifyoucan
SLUBStick exploitation of CVE-2022-2588. Converting a DF into a cross-cache arbitrary memory R/W primitive through PTE manipulation.
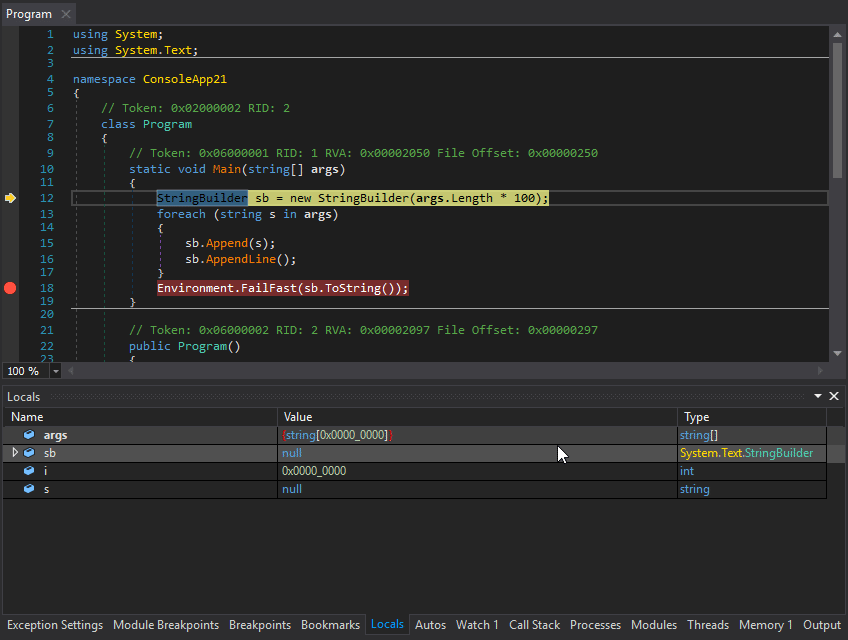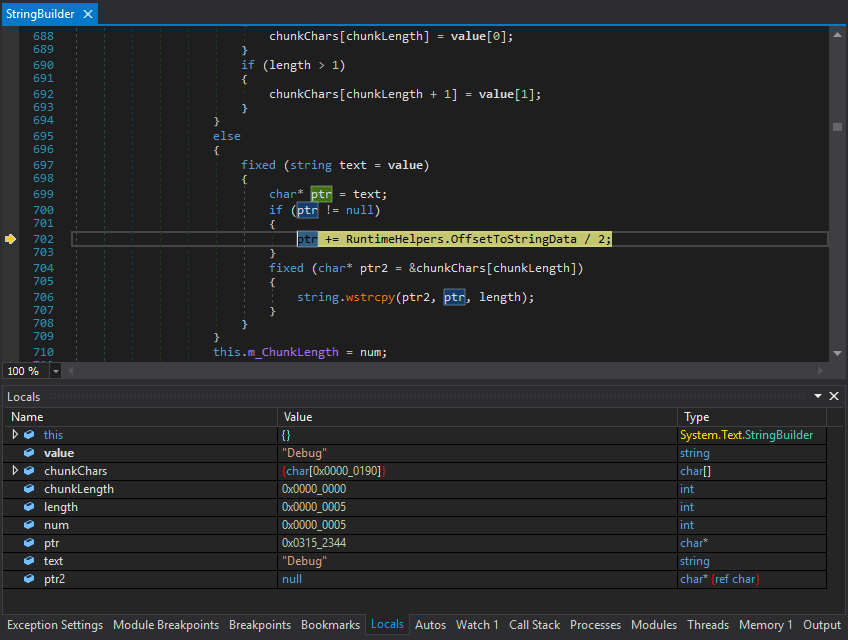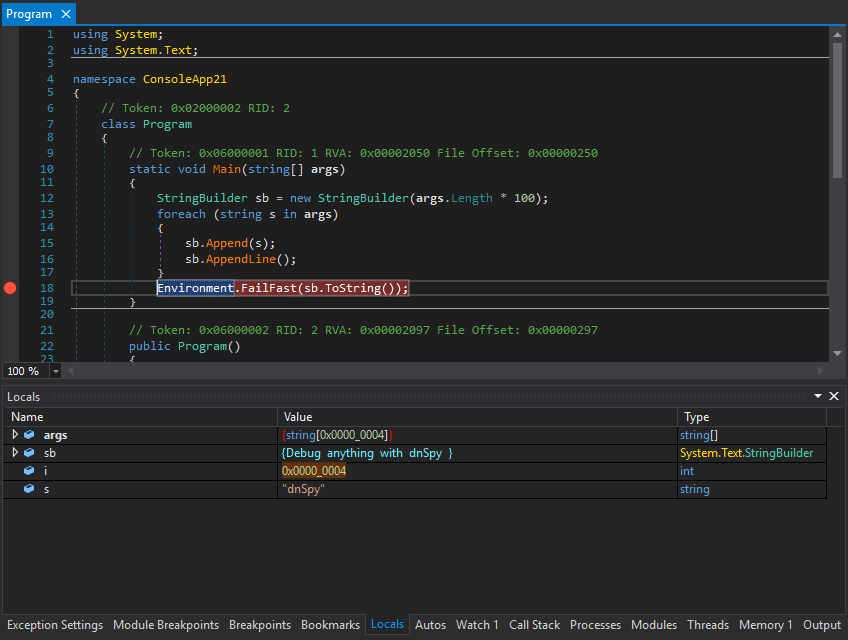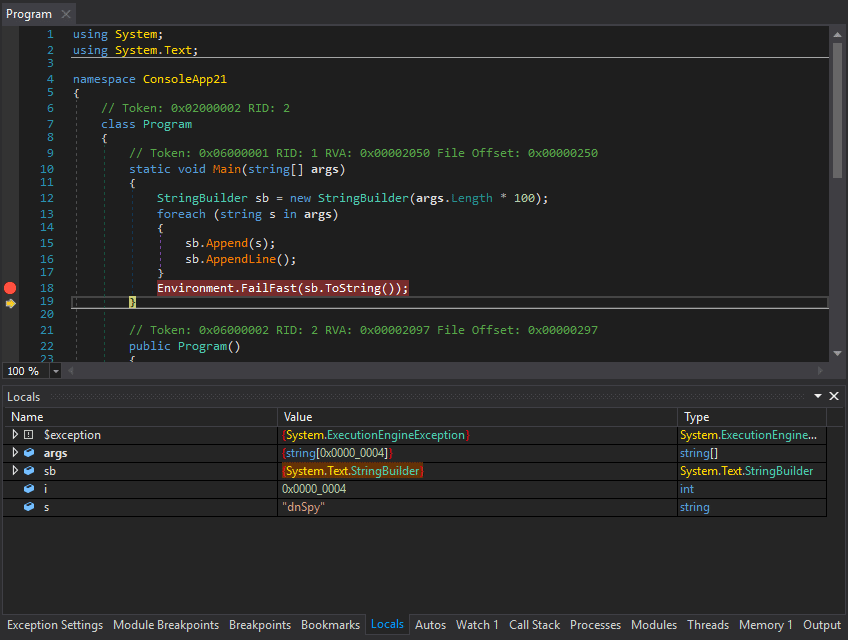 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 awnumar/memguard
Software sandbox for storage of sensitive information in memory.
 saereya/cve-2025-14847---mongobleed
Go proof-of-concept exploit for CVE-2025-14847 (MongoBleed), a MongoDB memory disclosure vulnerability. Crafts malformed BSON documents to leak…
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…