

MemGuard
 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
defensive-toolsdigital-forensicsincident-response+4
prox0959/memguardZero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
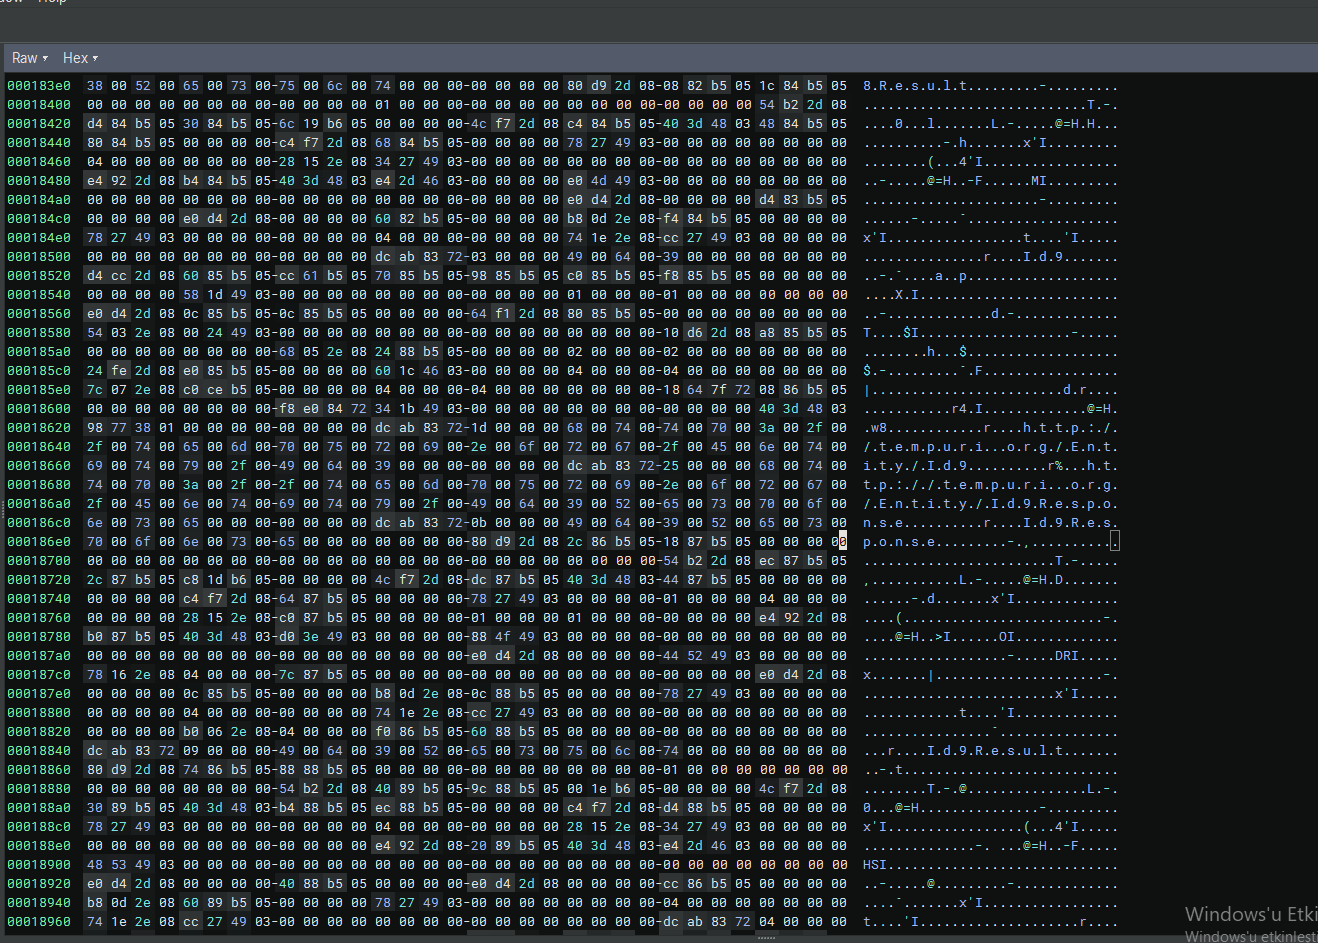 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 ngtuonghung/cve-2022-27666
Heap buffer overflow exploit for CVE-2022-27666 in Linux kernel IPsec ESP6 implementation. Includes kernel build, debug setup with GDB stub, and…
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
 nikaiw/vmkatz
Extract Windows credentials directly from VM memory snapshots and virtual disks
 skelsec/pypykatz
Mimikatz implementation in pure Python
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 rshipp/awesome-malware-analysis
Defund the Police.
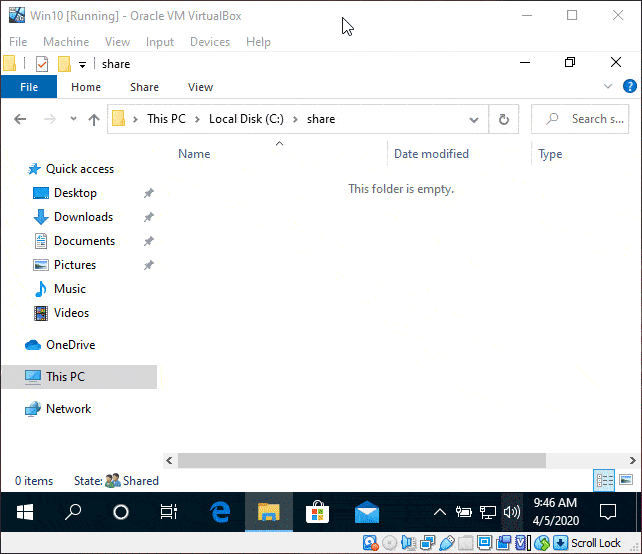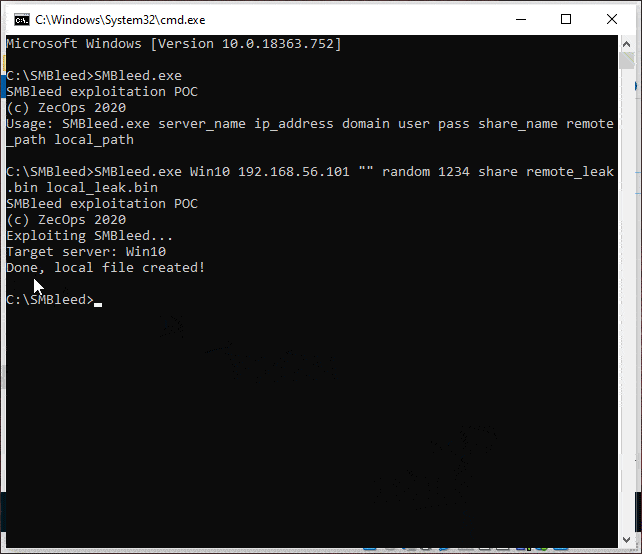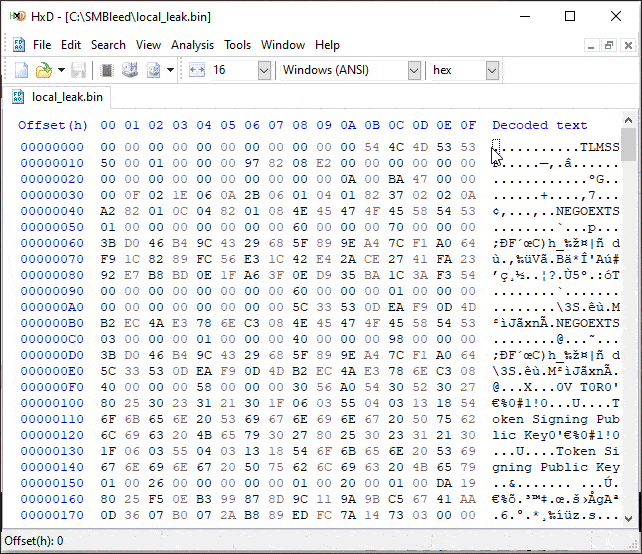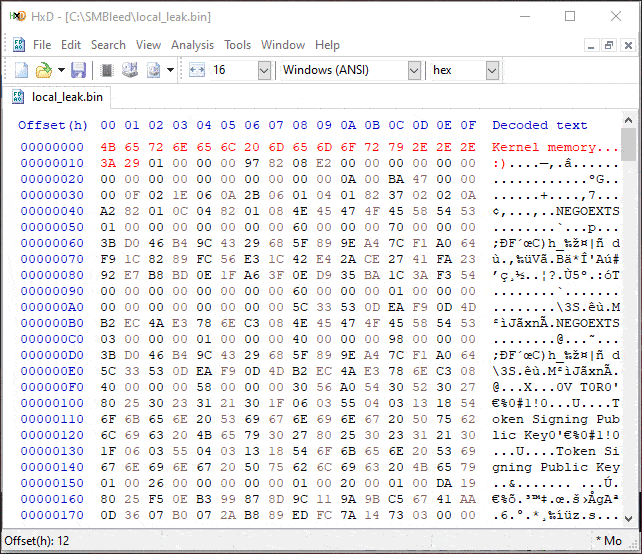 jamf/cve-2020-1206-poc
CVE-2020-1206 Uninitialized Kernel Memory Read POC