

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
253 results
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset

ai-assisted-reversingandroid-securitybinary-analysis+16
24.9k7h 37m ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.6k1 day ago
ShadowNet preview

ShadowNet

GitHubantisurveillanceagency/shadownet

ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…

anti-botdigital-forensicsforensics+9
241 day ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k2 days ago
cve-2026-43687 preview

cve-2026-43687

GitHubjvidhan/cve-2026-43687

Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…
binary-analysiseducationexploitation+4
2 days ago
CVE_2025_24257----NOT-MINE preview

CVE_2025_24257----NOT-MINE

GitHublearningdisordercapital35/cve_2025_24257----not-mine

Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
binary-exploitationexploitationmemory-forensics+2
2 days ago
VectorFreed preview

VectorFreed

GitHubrafabd1/vectorfreed

Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
binary-exploitationexploitationinformation-gathering+4
82 days ago
GoTEE-example preview

GoTEE-example

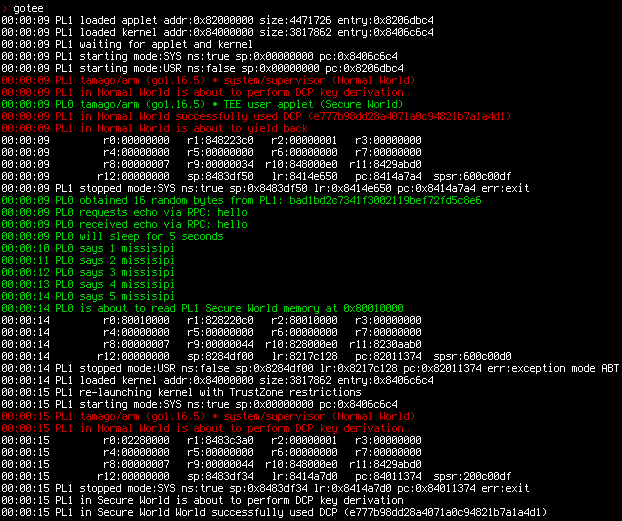
GitHubusbarmory/gotee-example

GoTEE - example application
debuggersembedded-systems-securityhardware-security+2
173 days ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

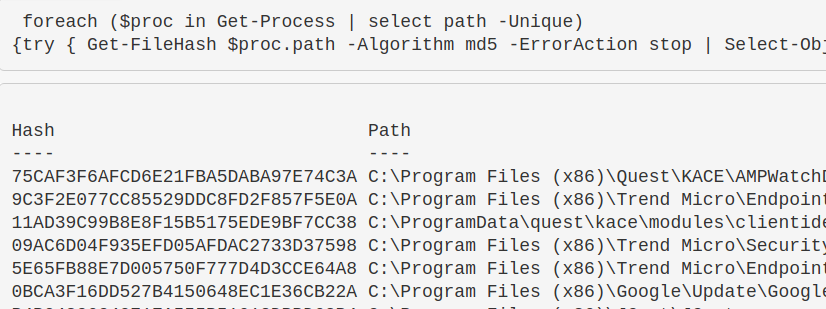
You didn't think I'd go and leave the blue team out, right?
curated-resourcesdigital-forensicseducation+5
1.8k4 days ago
CAPEv2 preview

CAPEv2

GitHubkevoreilly/capev2

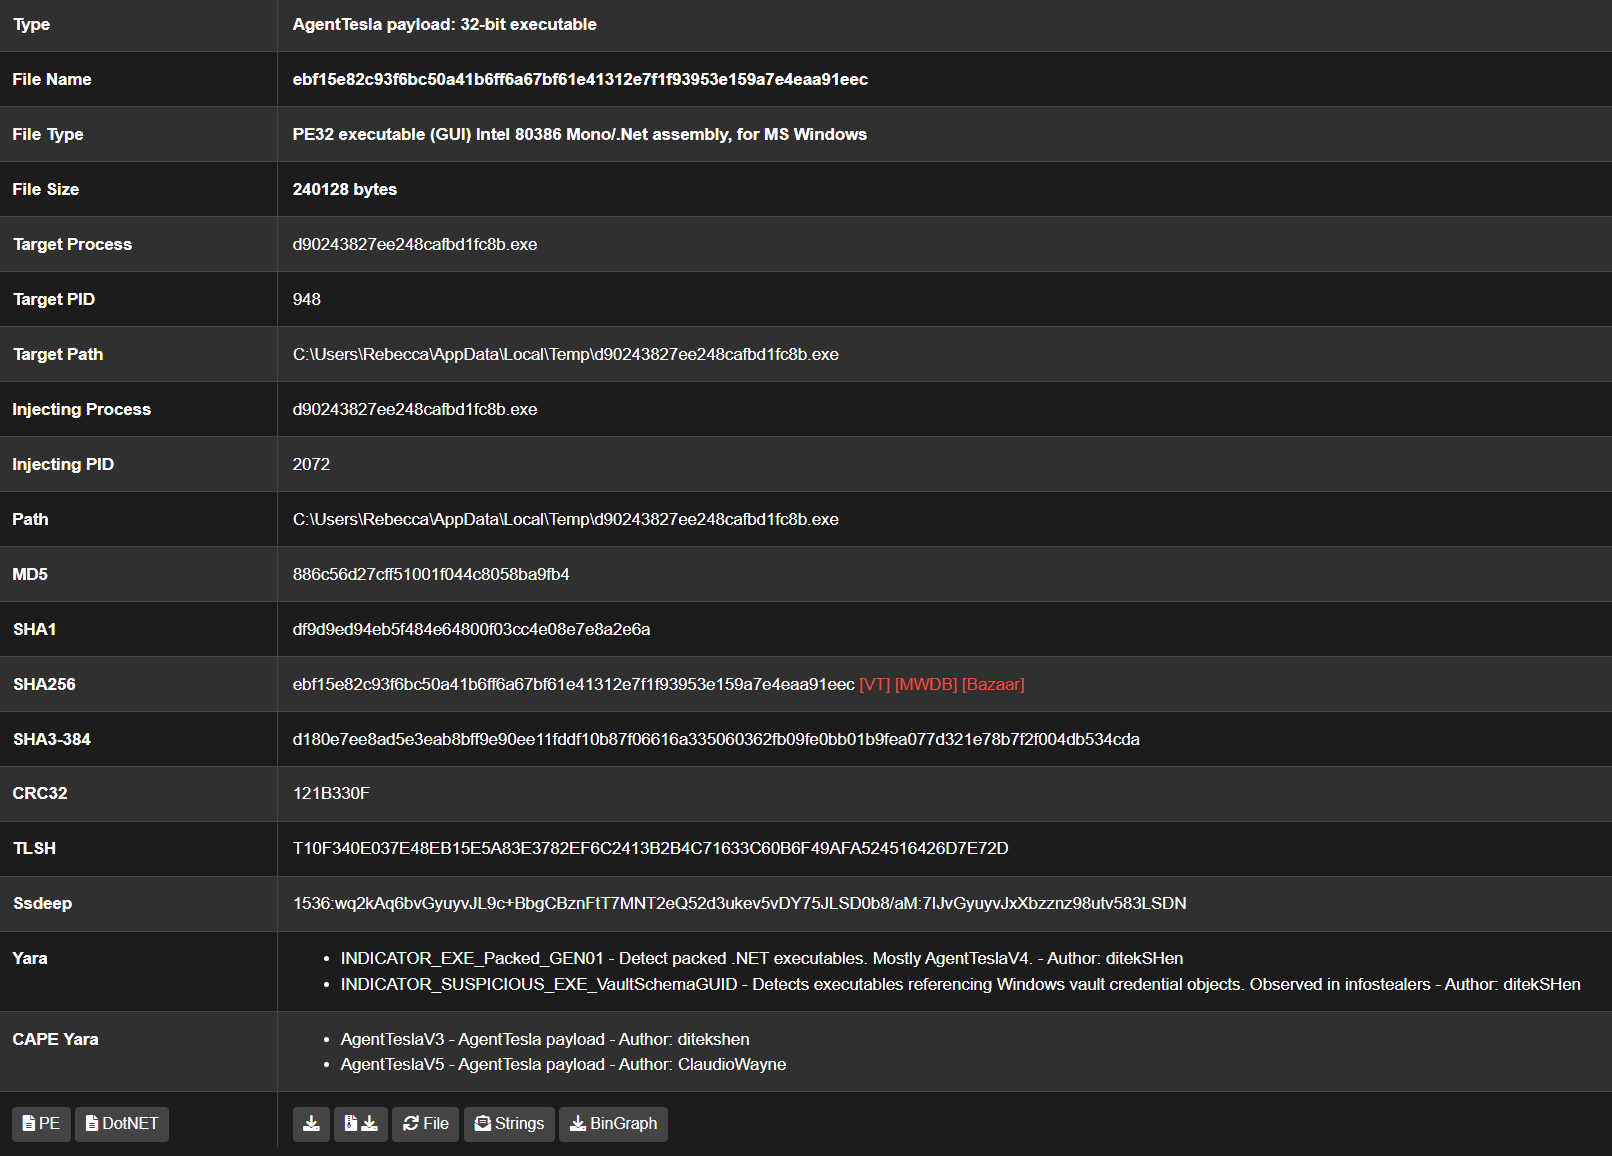
Malware Configuration And Payload Extraction

debuggersdynamic-analysis-sandboxingeducation+6
3.5k4 days ago
OnTheEdge preview

OnTheEdge

GitHubjssngc/ontheedge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…

command-and-controldata-exfiltrationmalware-analysis+4
94 days ago
CVE-2026-28609-matroska-pcm-oob preview

CVE-2026-28609-matroska-pcm-oob

GitHubdevrodt2/cve-2026-28609-matroska-pcm-oob

Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
android-securitybinary-exploitationexploitation+5
66 days ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
5936 days ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.4k9 days ago
objection preview

objection

GitHubsensepost/objection

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
android-securitydynamic-analysis-sandboxingexploitation+9
9.4k10 days ago
ios.CVE-2026-84616-84607 preview

ios.CVE-2026-84616-84607

GitHubping-2o/ios.cve-2026-84616-84607

research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
binary-analysiseducationexploitation+6
1111 days ago
ghost-hoock preview

ghost-hoock

GitHubdeaurity/ghost-hoock

GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
android-securitybinary-exploitationexploitation+6
111 days ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k12 days ago
Previous12…15Next