velociraptor
 velocidex/velociraptor
Digging Deeper....
data-recoverydefensive-toolsdigital-forensics+8
4.3k
velocidex/velociraptorDigging Deeper....
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
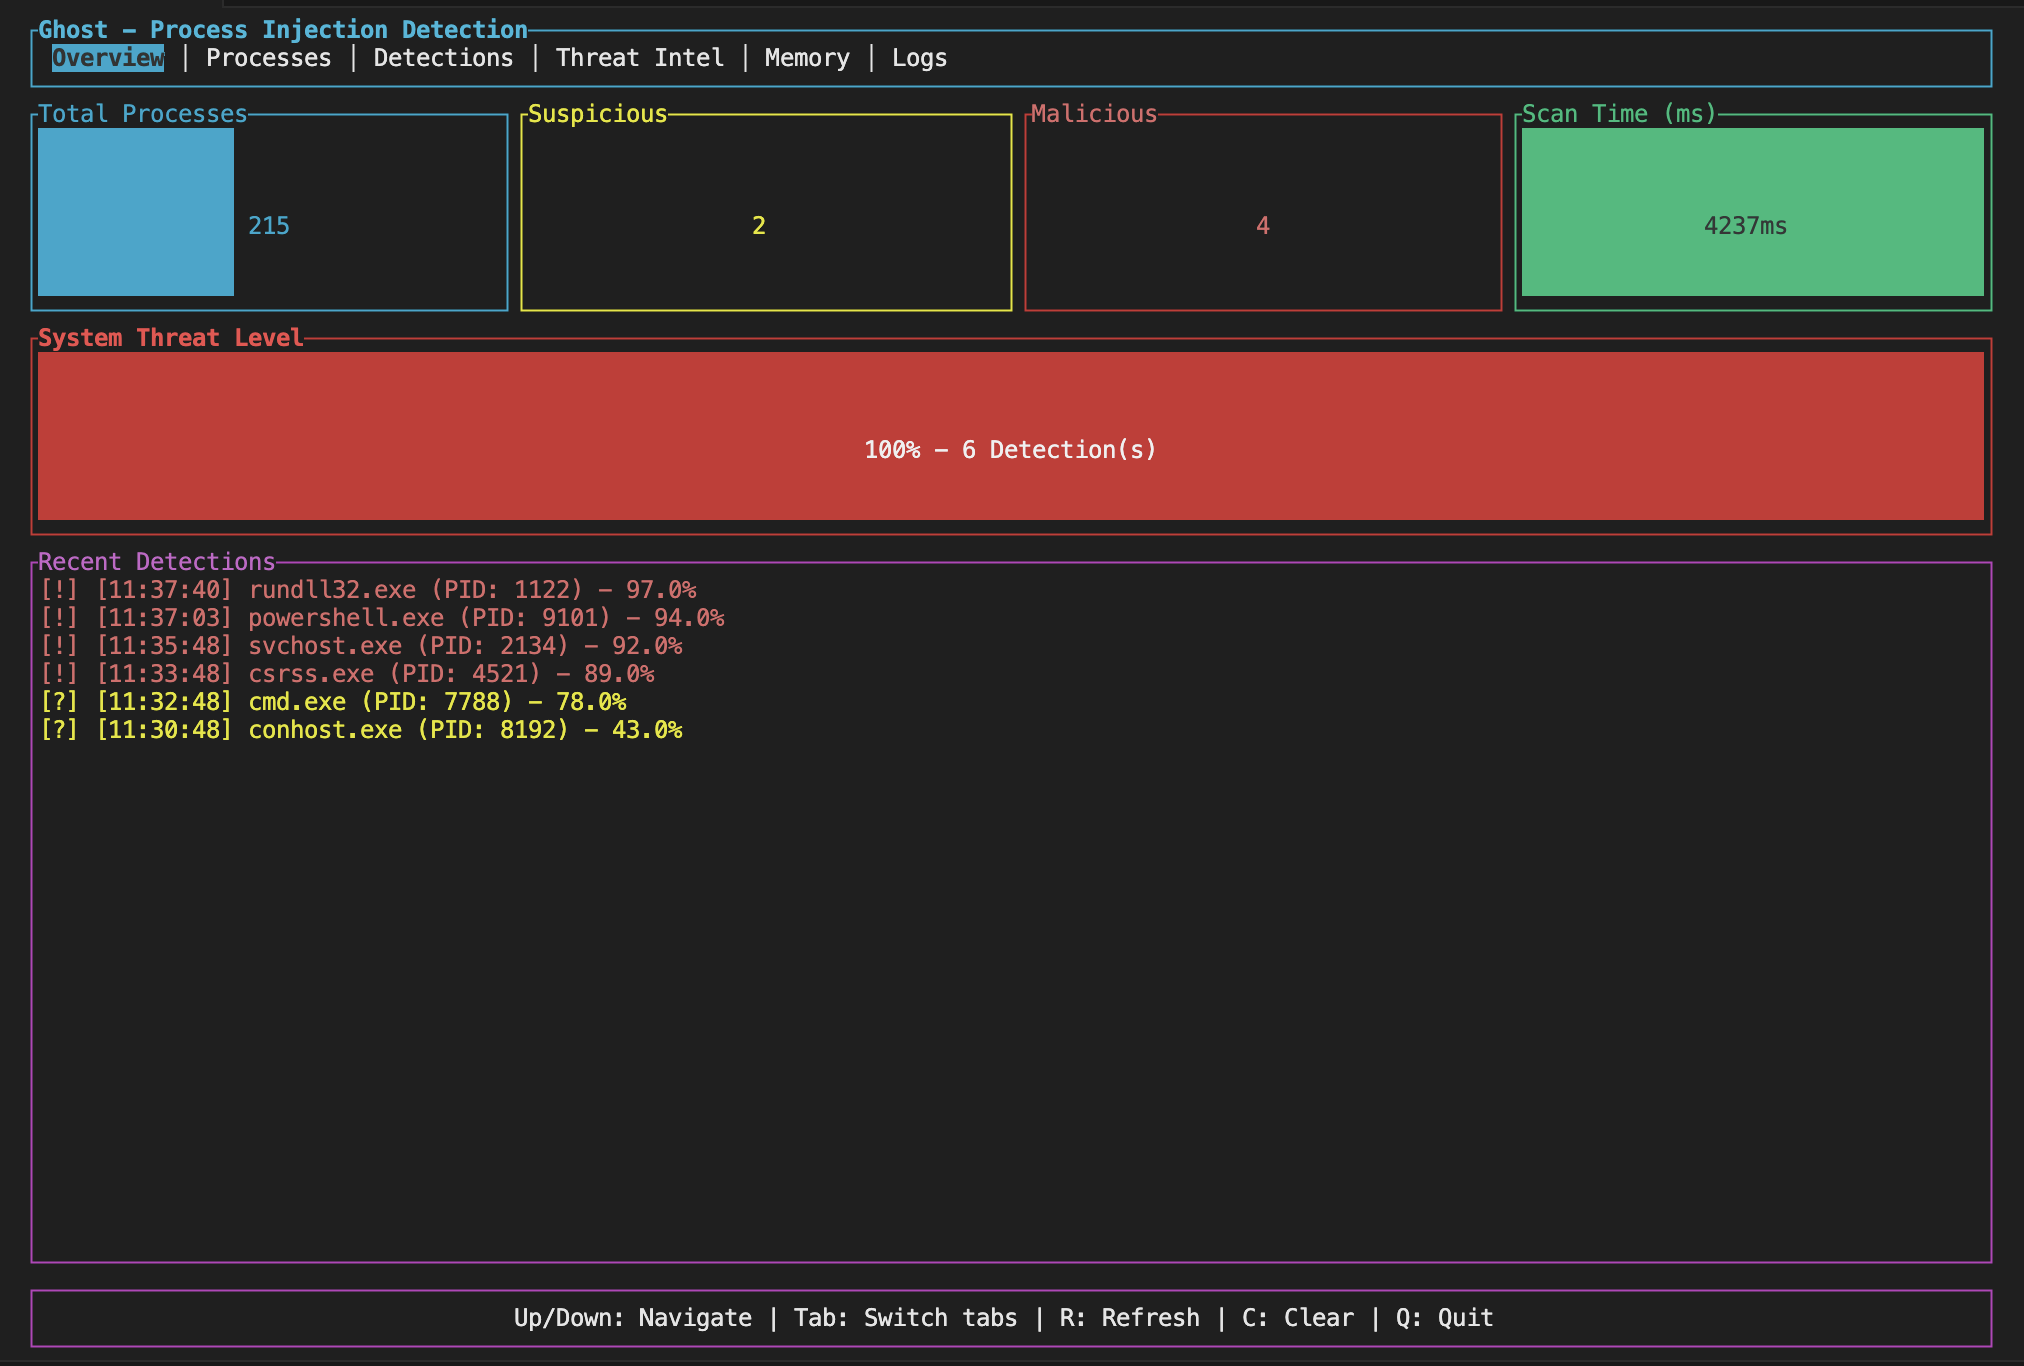 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
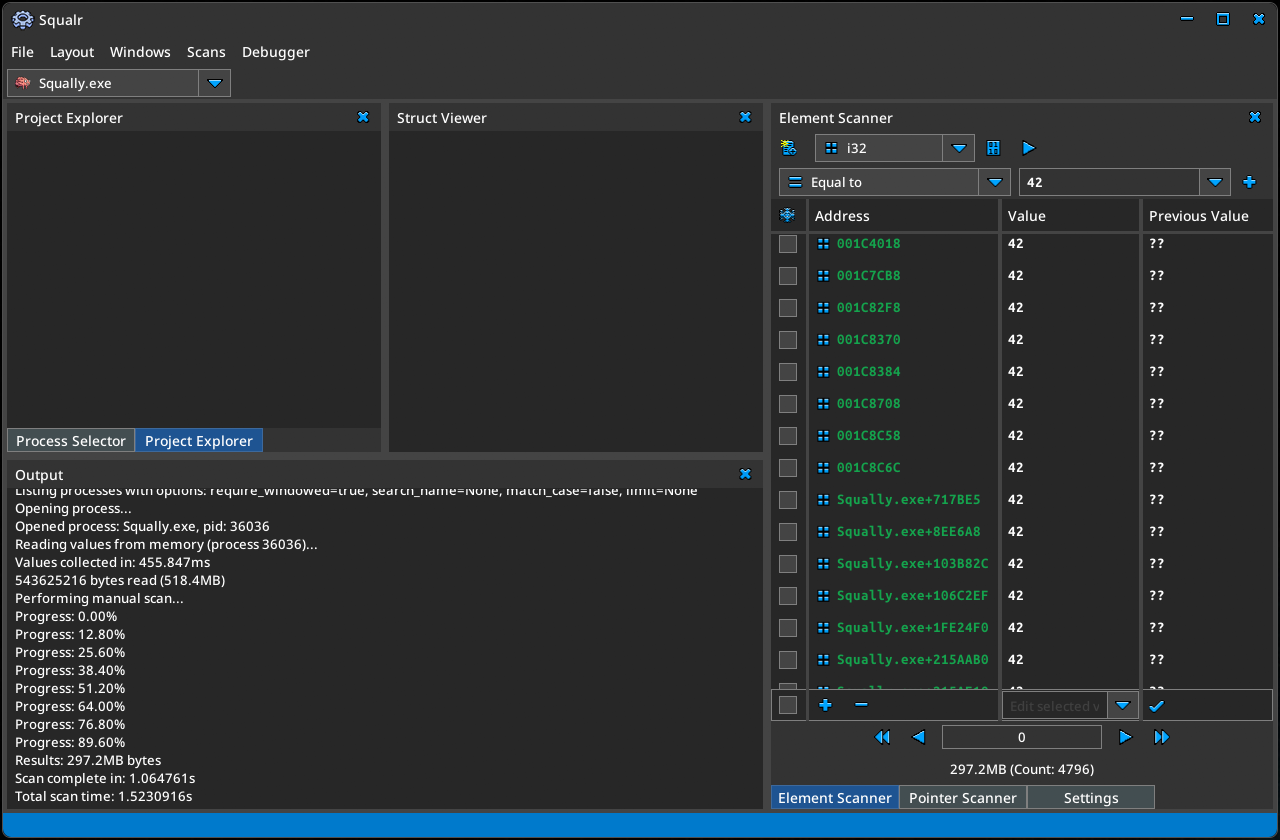 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
 velocidex/winpmem
The multi-platform memory acquisition tool.
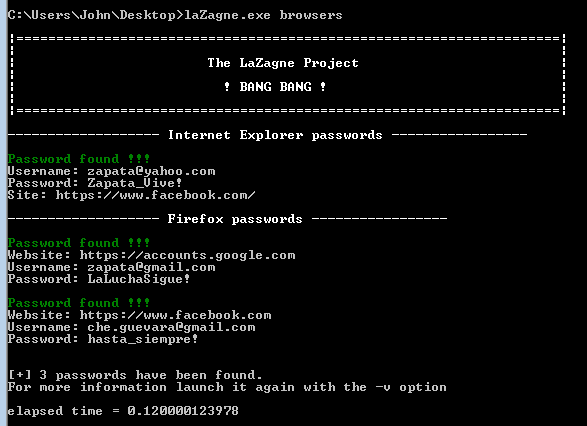 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
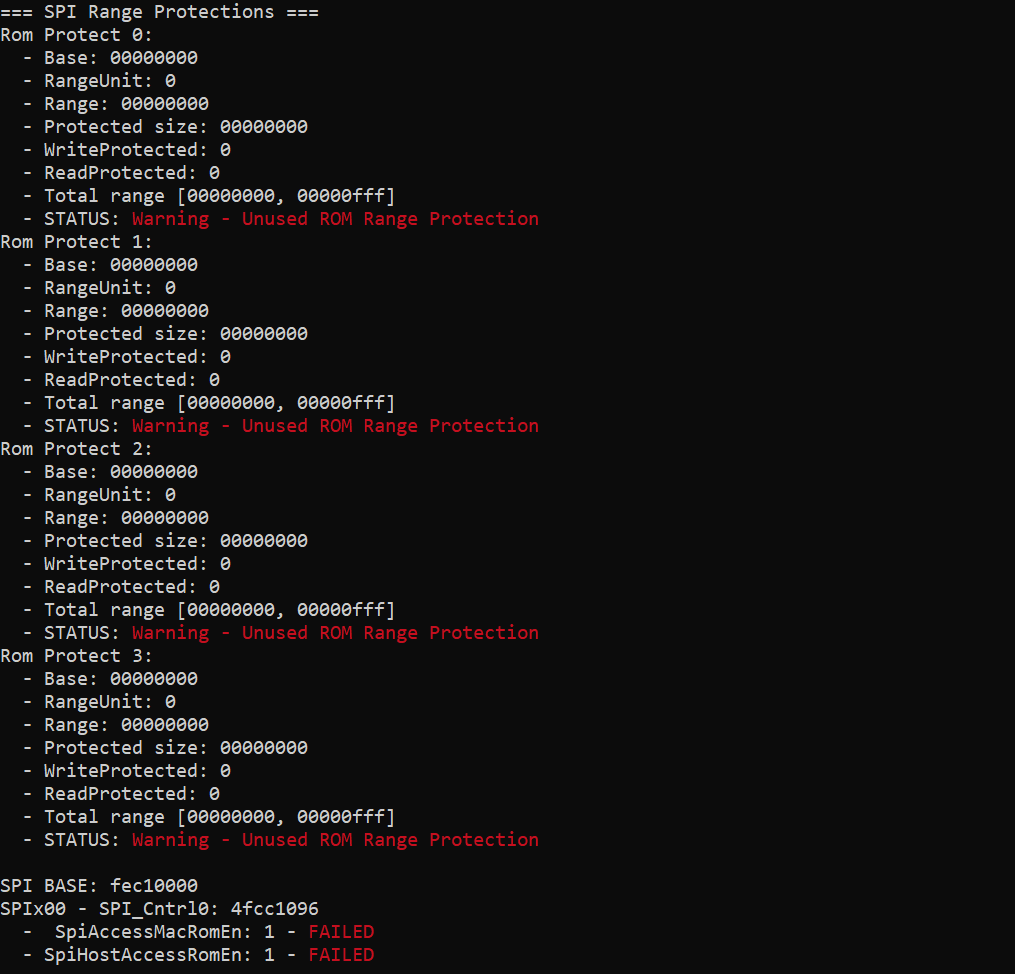 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 fortra/nanodump
The swiss army knife of LSASS dumping
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…