

frida-medit
 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
gmh5225/frida-meditCross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 nccgroup/memaddressanalysis
Research project related to memory address analysis
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
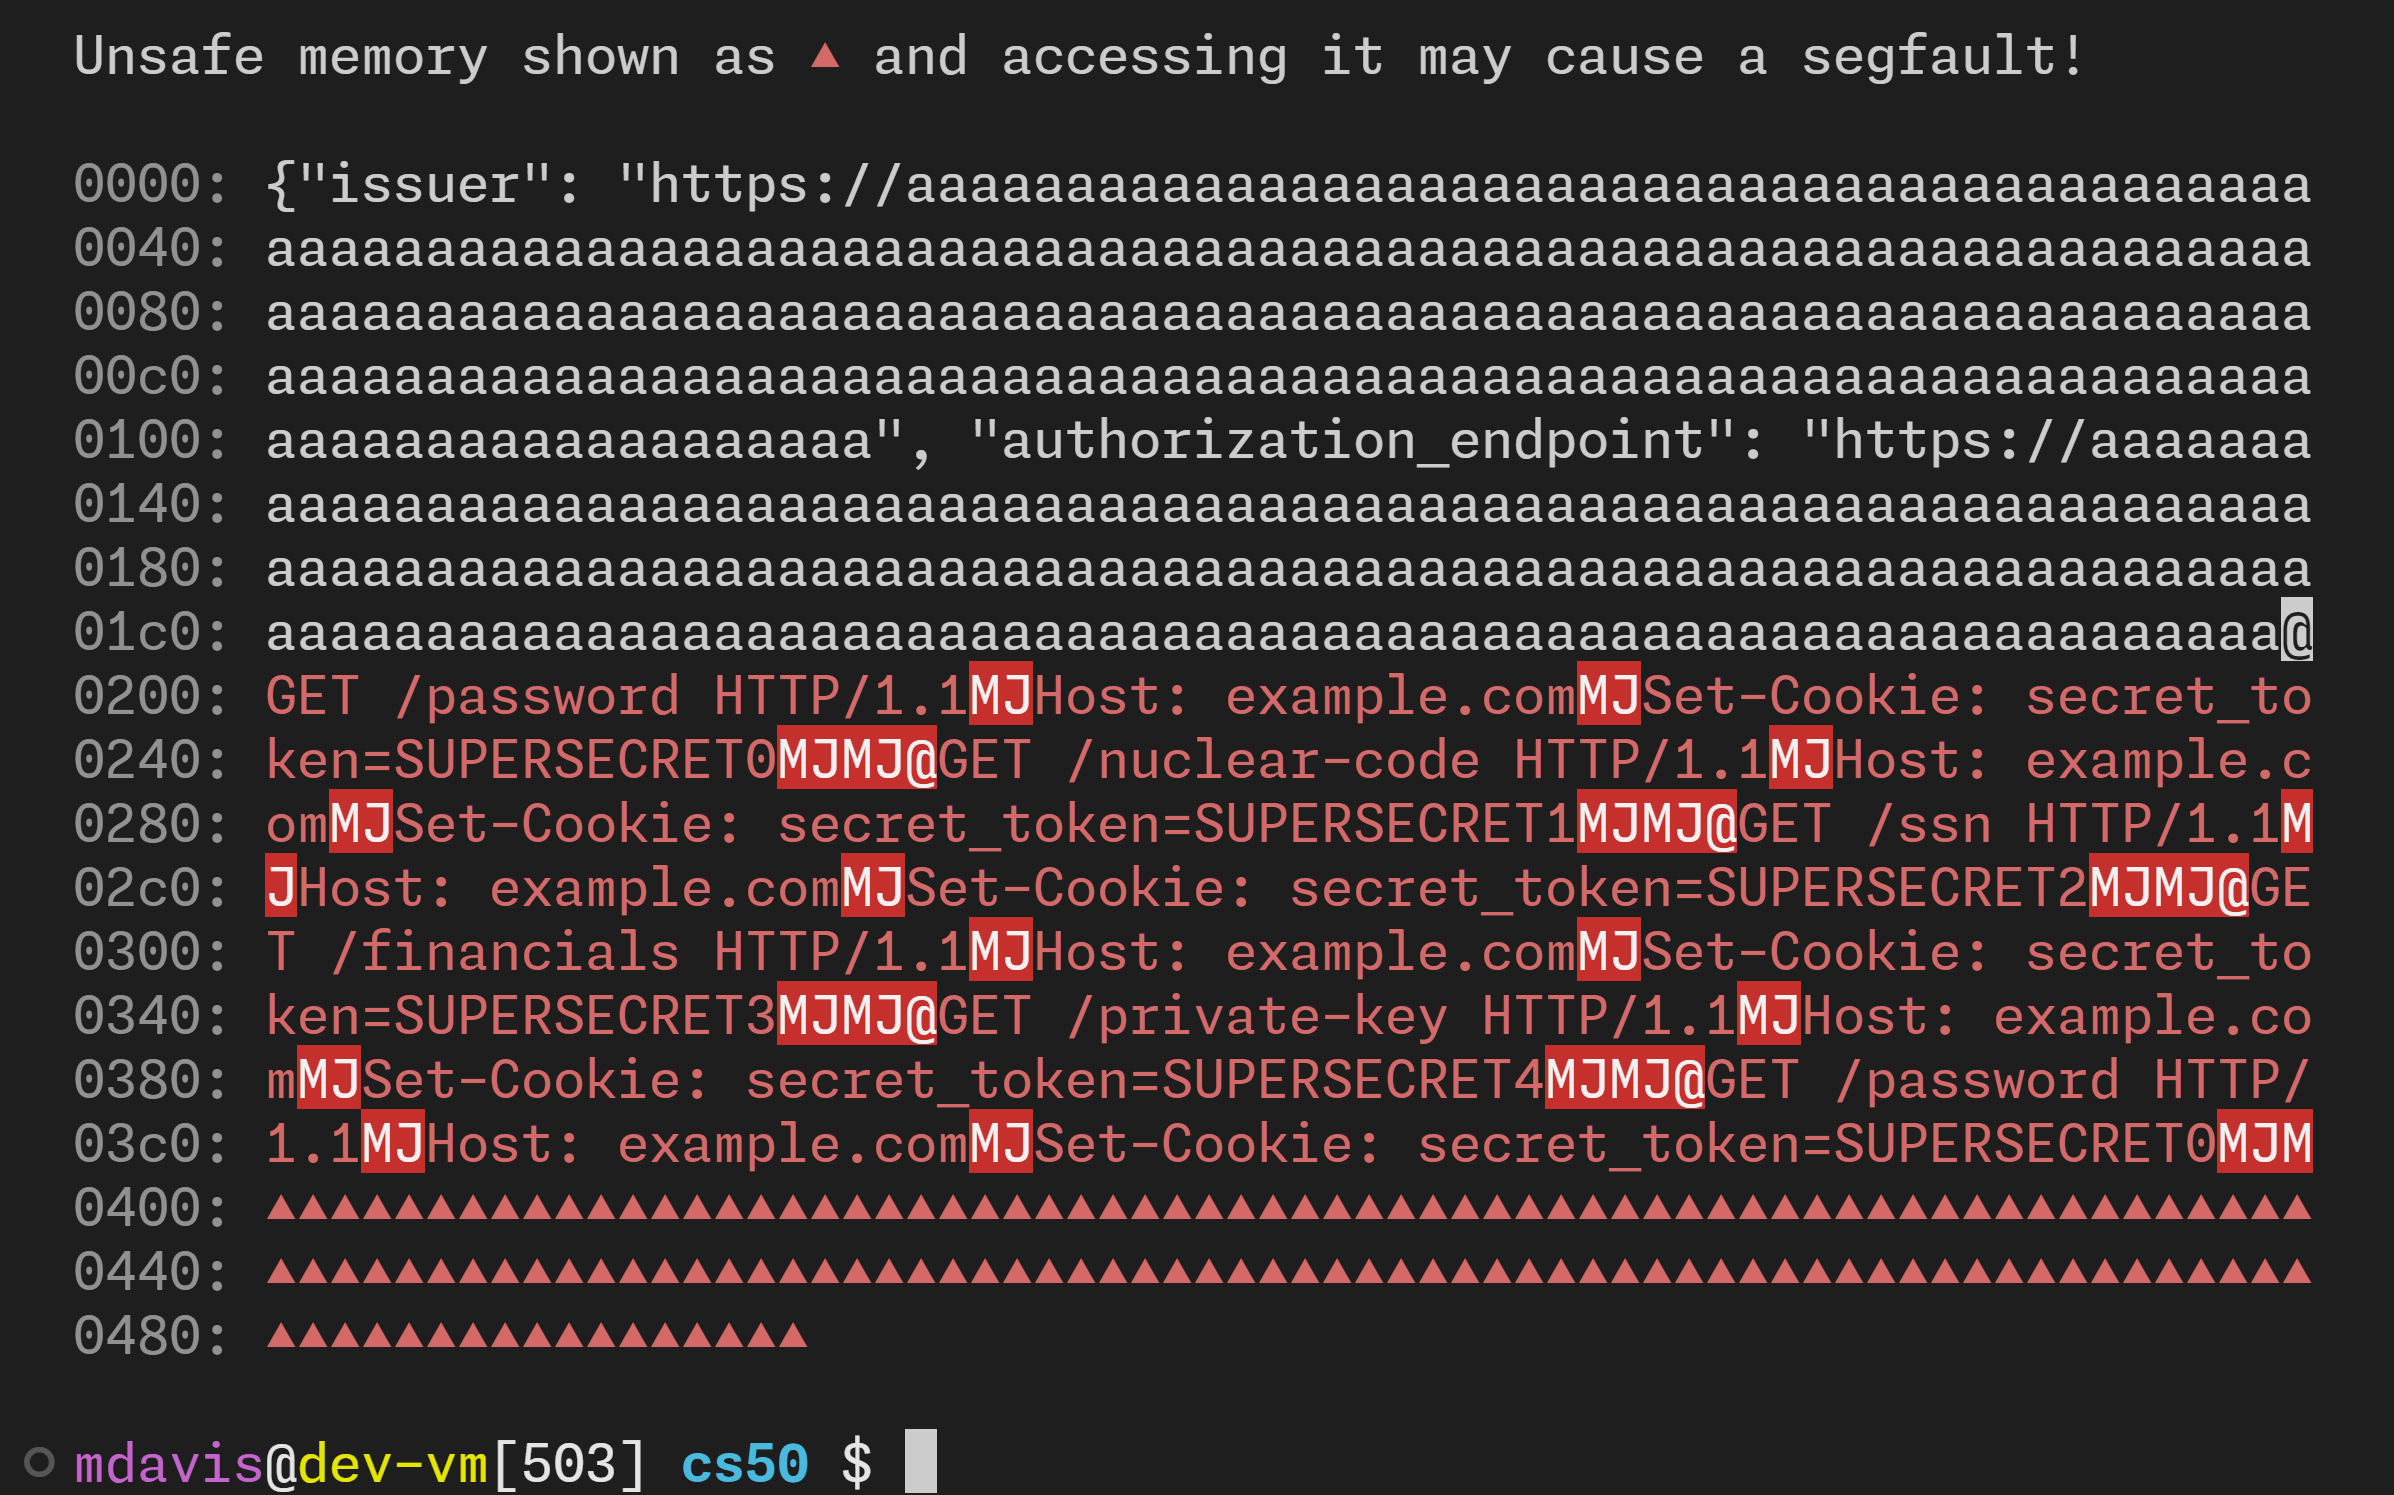 morganwdavis/overread
Simulates CVE-2023-4966 Citrix Bleed overread bug
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 springsec/cve-2022-22620
Webkit (Safari) - Exploit
 jajangjaman/cve-2021-41160
FreeRDP is a free implementation of the Remote Desktop Protocol (RDP), released under the Apache license. In affected versions a malicious server…
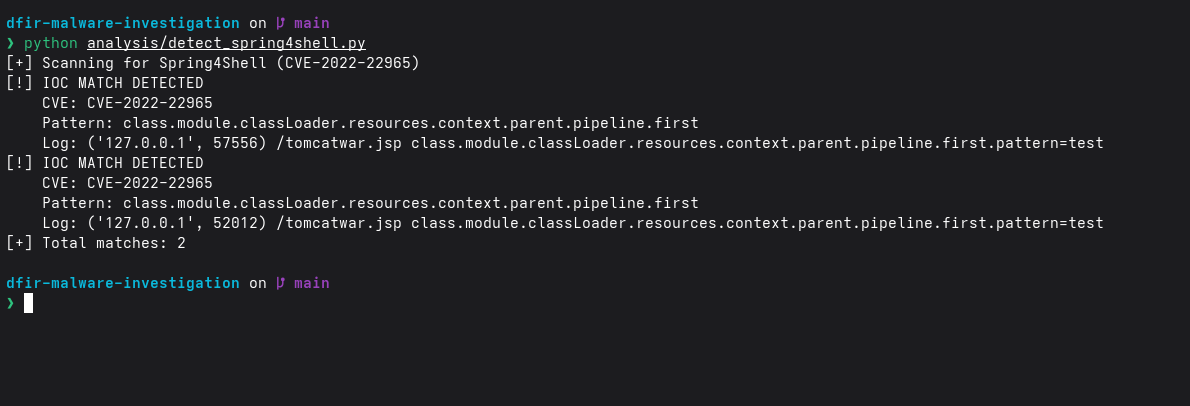 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 jas502n/cve-2018-17182
Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
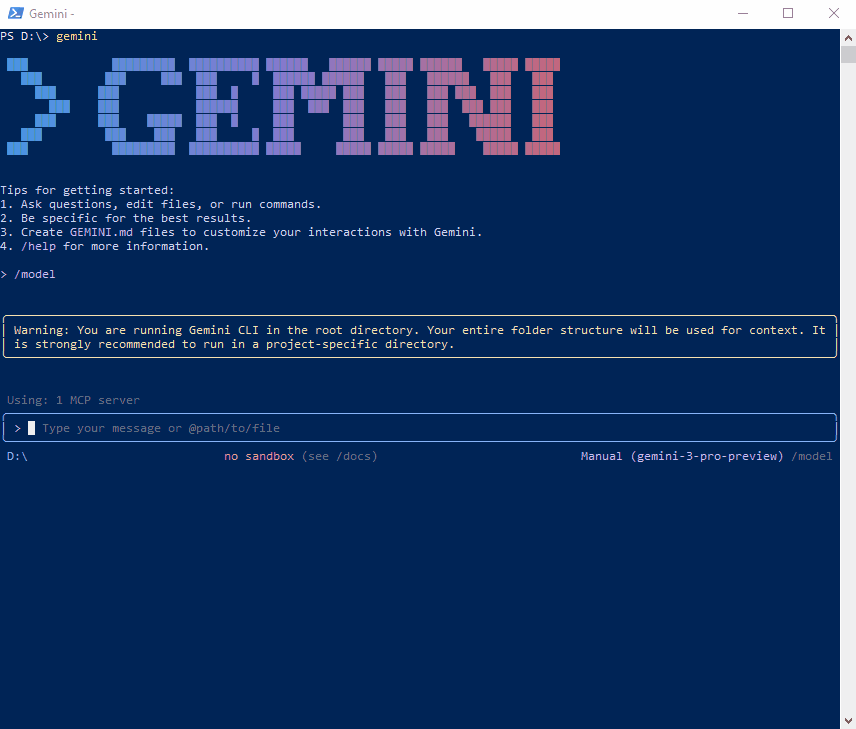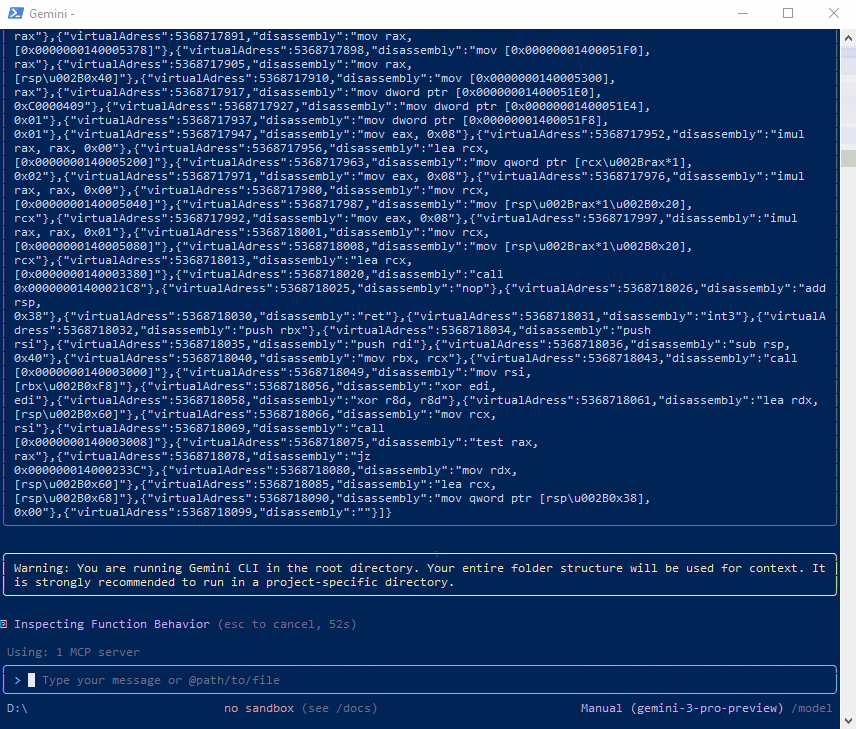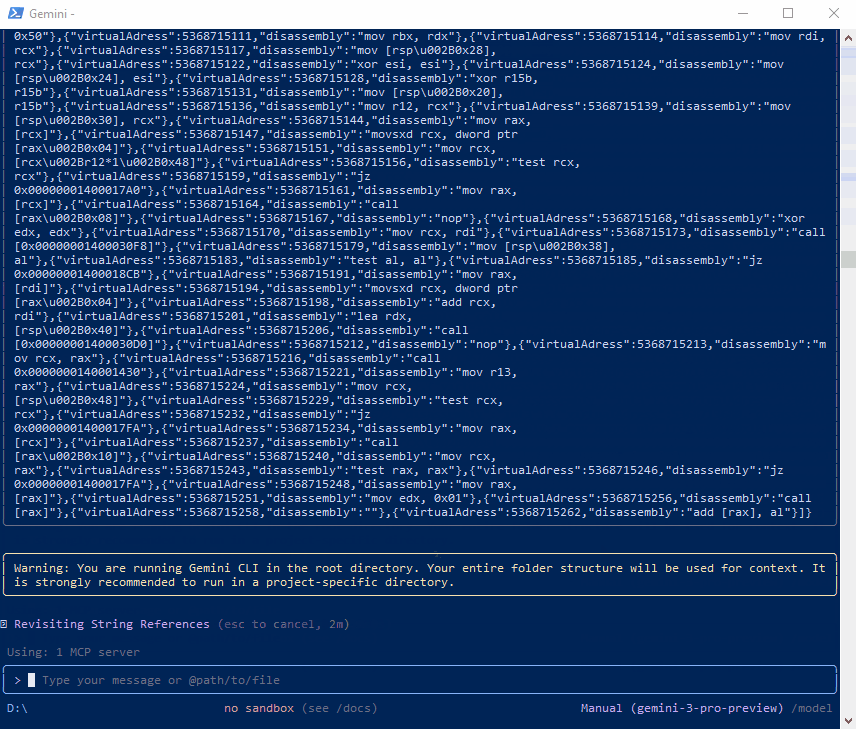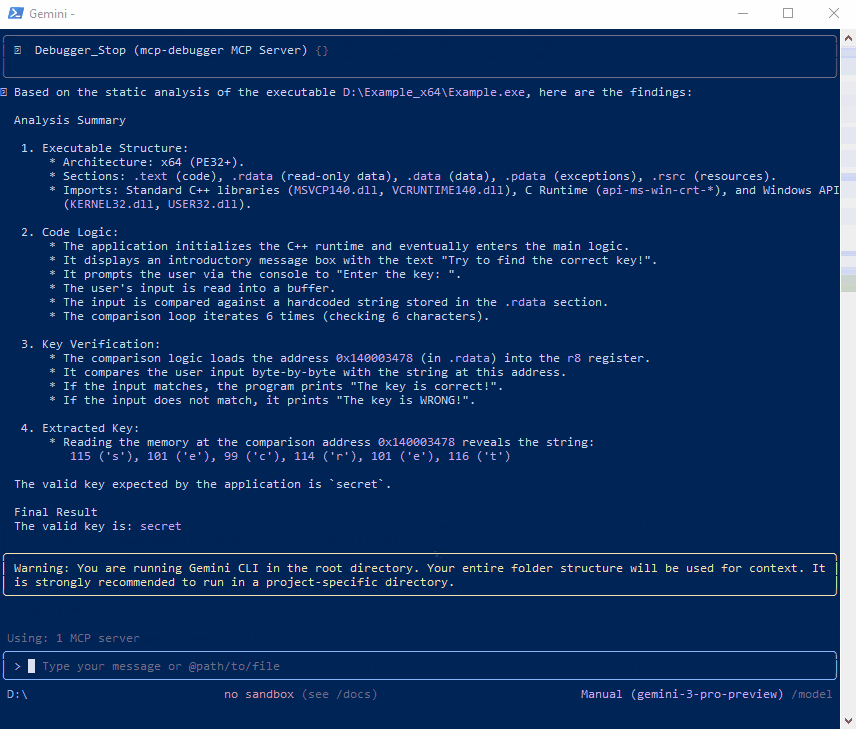 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 amberchalia/norm-edr
Experimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…
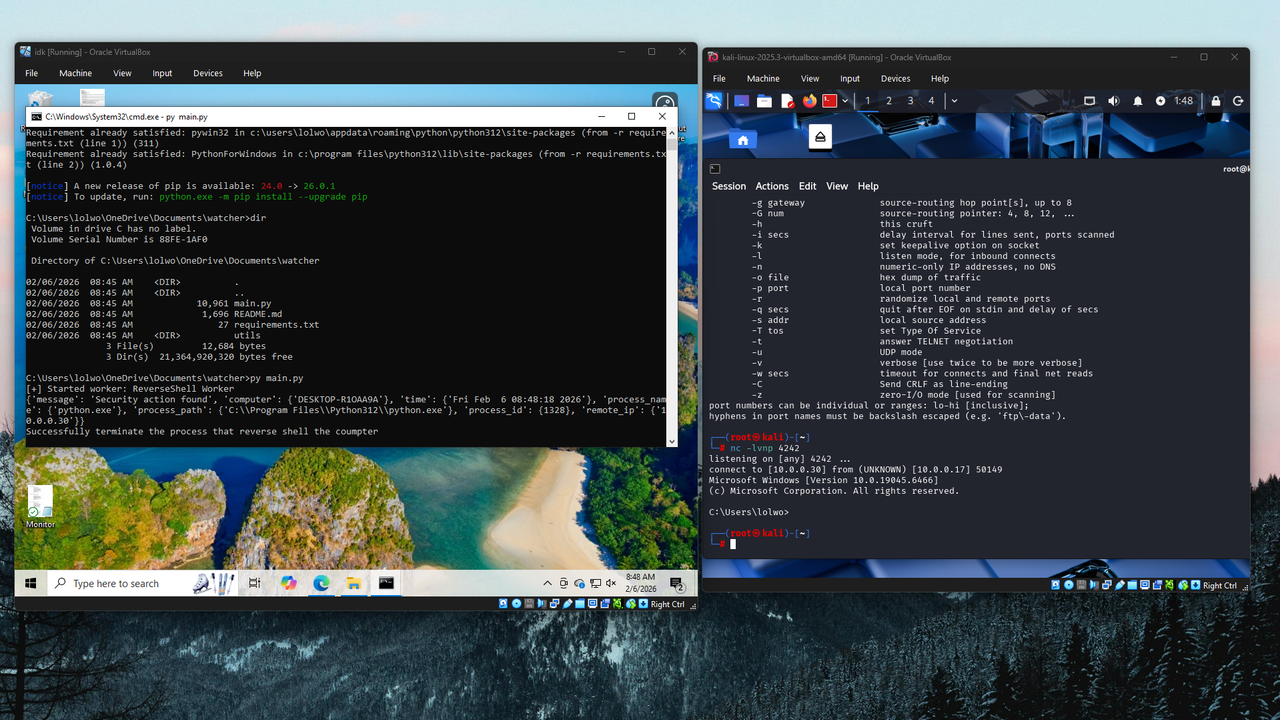 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 artemcyberlab/project-field-analysis-and-memory-leak-demonstration
The objective of this project was to assess a remote host for the Heartbleed vulnerability (CVE-2014-0160), verify its presence, and exploit it to…
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…