
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
46 results
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
179
5 days ago
volatility-plugins preview

volatility-plugins

GitHubwithsecurelabs/volatility-plugins

Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
digital-forensicsforensicsincident-response+2
117 years ago
dotnet-gargoyle preview

dotnet-gargoyle

GitHubwithsecurelabs/dotnet-gargoyle

A spiritual .NET equivalent to the Gargoyle memory scanning evasion technique
malware-analysismemory-forensicsred-teaming
527 years ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
memory-carving-scripts preview

memory-carving-scripts

GitHubwithsecurelabs/memory-carving-scripts

Scripts for extracting useful information from infected memory dumps
digital-forensicsforensicsincident-response+2
108 years ago
community preview

community

GitHubvolatilityfoundation/community

Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…
digital-forensicsmalware-analysismemory-forensics
3775 years ago
libpeconv preview

libpeconv

GitHubhasherezade/libpeconv

Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
binary-analysismalware-analysismemory-forensics+4
1.4k5 months ago
TickTock preview

TickTock

GitHubwithsecurelabs/ticktock

Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…

defensive-toolsmalware-analysismemory-forensics
1143 years ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2672 years ago
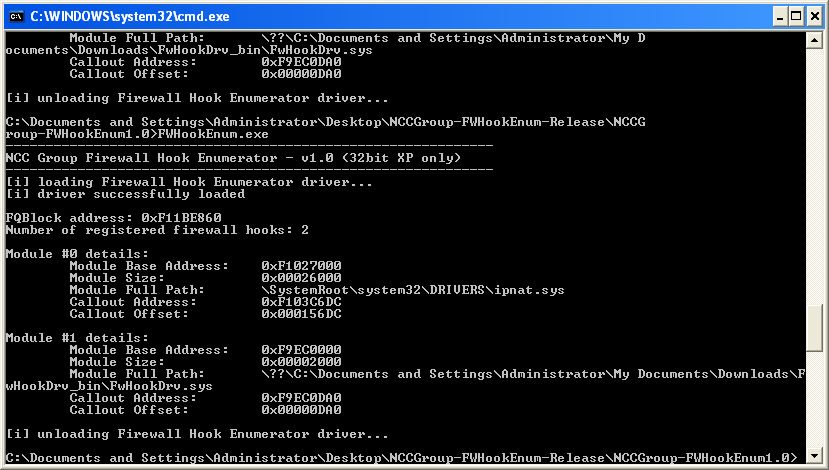
WindowsFirewallHookDriverEnumeration preview

WindowsFirewallHookDriverEnumeration

GitHubnccgroup/windowsfirewallhookdriverenumeration

Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
digital-forensicsforensicsincident-response+2
2111 years ago
Memory-analysis preview

Memory-analysis

GitHubbedazzlinghex/memory-analysis

Contains tools to perform malware and forensic analysis in Memory

digital-forensicsforensicsincident-response+3
48 years ago
wmi-static-spoofer preview

wmi-static-spoofer

GitHubalex3434/wmi-static-spoofer

Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
exploitationhardware-hackinghardware-iot-security+4
5157 years ago
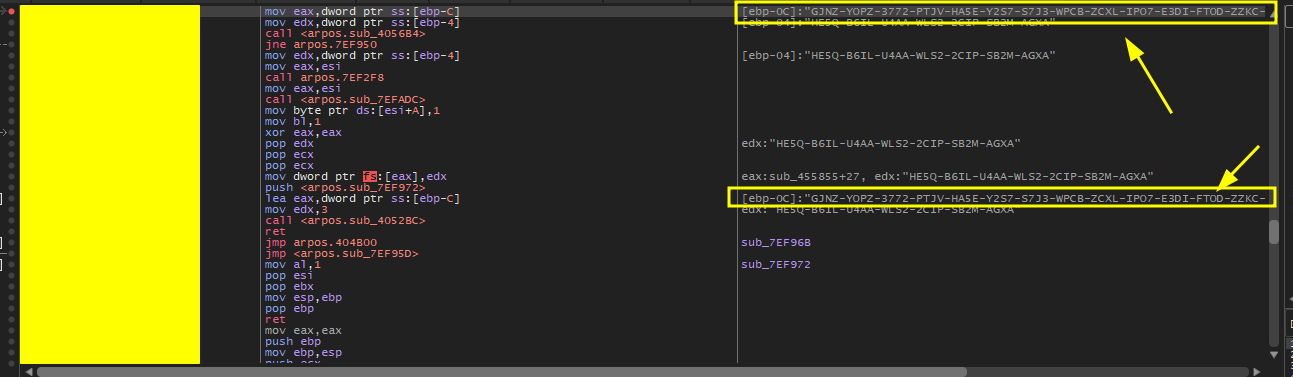
CVE-2025-65320 preview

CVE-2025-65320

GitHubyonathanpy/cve-2025-65320

CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…

binary-analysisdebuggersexploitation+3
26 months ago
CVE-2025-27363 preview

CVE-2025-27363

GitHubtin-z/cve-2025-27363

Integer overflow in FreeType software, which also affects Chrome

binary-exploitationeducationexploitation+3
312 months ago
pwndbg preview

pwndbg

GitHubpwndbg/pwndbg

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
10.9k1 day ago
GhostTrace preview

GhostTrace

GitHubdevzinh/ghosttrace

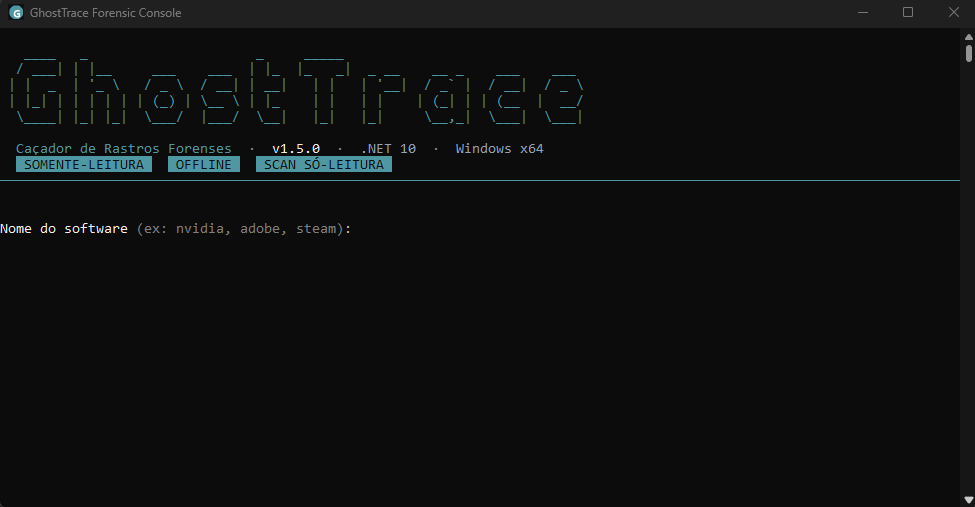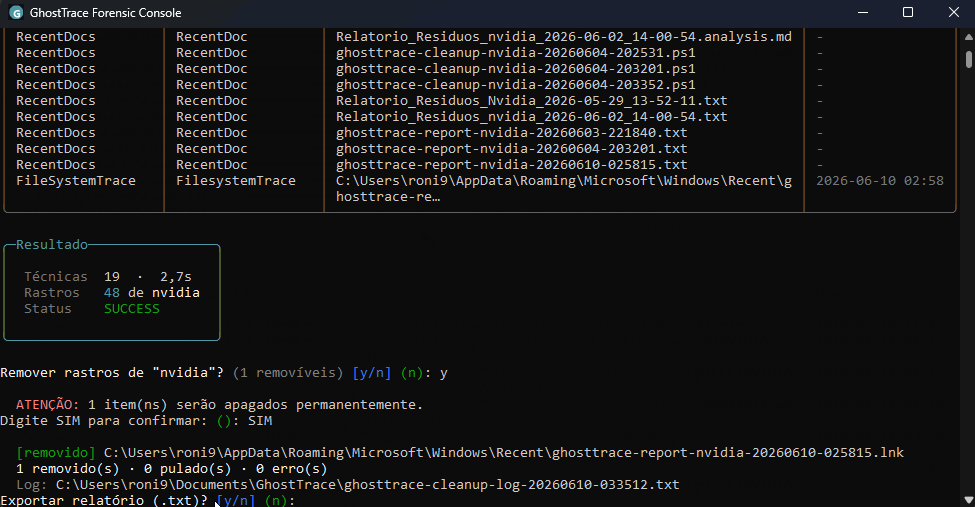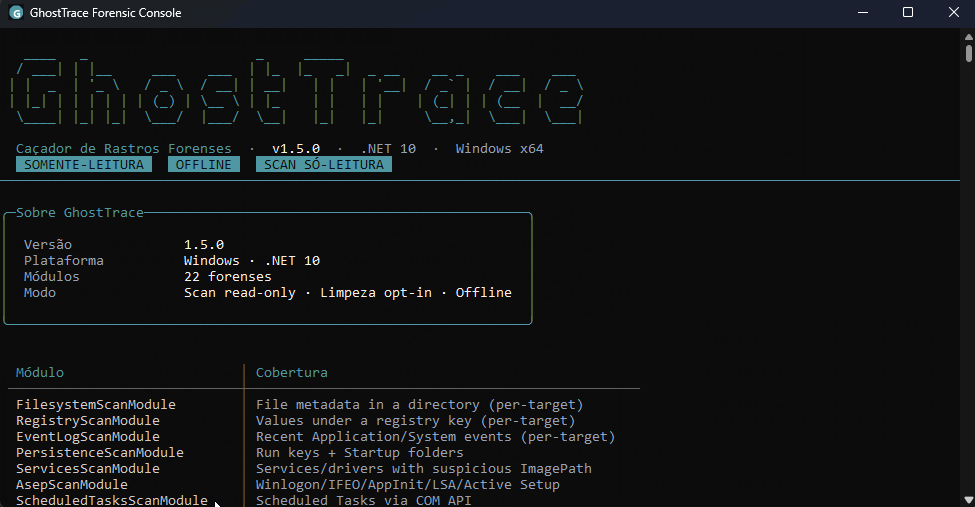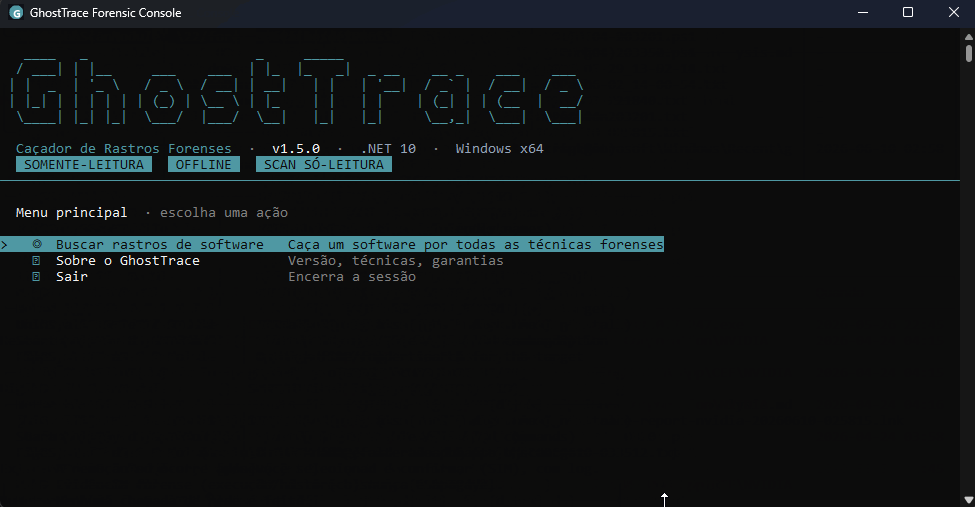
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…

digital-forensicsforensicsincident-response+3
1 month ago
NTDLL-Unhook preview

NTDLL-Unhook

GitHubhwbp/ntdll-unhook

proper ntdll .text section unhooking via native api. unlike other unhookers this doesnt leave 2 ntdlls loaded. x86/x64/wow64 supported.

malware-analysismemory-forensicspenetration-testing+2
569 months ago
Embarcadero-Workaround preview

Embarcadero-Workaround

GitHubhelpsystems/embarcadero-workaround

This is a workaround for CVE-2014-0993 and CVE-2014-0994 that patches on memory without the need to recompile your vulnerable software. This is not…

binary-analysisdefensive-toolsexploitation+3
111 years ago
Previous123Next