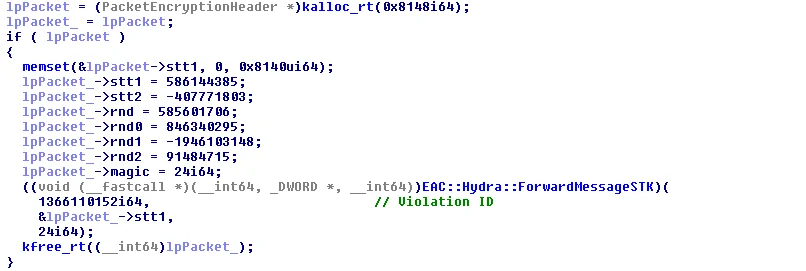
EAC-Kernel-Packet-Fucker

Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…

Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…

Windows Analysis and Research Toolkit

Main repository to pull all NCC Group Cisco ASA-related tool projects.


Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.

A Runtime Crypter in C for Linux ELF binaries.

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

SALT - SLUB ALlocator Tracer for the Linux kernel

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

Tool to make in memory man in the middle

All reasonably stable tools

Utility to find AES keys in running processes