Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

Tool for extracting information from newly spawned processes

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…

Dynamic unpacker based on PE-sieve

A python script developed to process Windows memory images based on triage type.

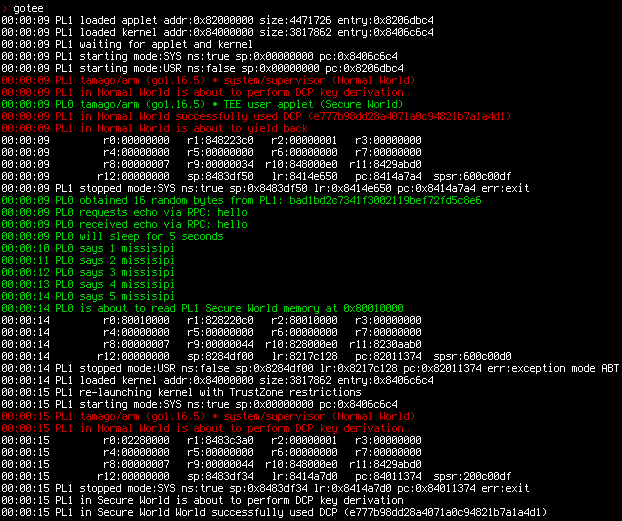
GoTEE - example application

Dump cookies and credentials directly from Chrome/Edge process memory

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

Heap analysis tooling for mempool

A Generic Windows Memory Scraping Tool

Windows kernel exploit for CVE-2020-17057 using palette objects with dangling data pointers, targeting type isolation bypass for privilege escalation.

7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

Proof-of-concept exploit for CVE-2024-22532: heap-based buffer overflow in XnView Classic 2.51.5 and NConvert 7.163 via crafted .xwd file, enabling…

Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…

Vulnerability Found on Squid Proxy.

Technical documentation and analysis of CVE-2022-30292, a heap-based buffer overflow in Squirrel 3.2 leading to denial of service, sandbox escape,…

PoC for CVE-2026-2005