CVE-2026-109618-exploit

[PHP2Shell] Golang exploit for CVE-2026-109618 / CVE-2026-109619: Unauthenticated RCE in PHP 5.4–8.5.11 via OOM corruption + session.upload_progress…

[PHP2Shell] Golang exploit for CVE-2026-109618 / CVE-2026-109619: Unauthenticated RCE in PHP 5.4–8.5.11 via OOM corruption + session.upload_progress…

A public release of the Steal My Bitcoin challenge

PHP 8.4.26 - Critical - Remote - OOM longjmp - CVE-2026-109618 PHP2Shell. Unauth chunked multipart hits memory_limit before app code on Apache…

PHP 8.5.11 - Critical - Remote - UAF - CVE-2026-109619 PHP2Shell. Same-worker fatal backtrace then INI diagnostic on Apache mod_php. Lab vs 8.5.12.…

Proof-of-concept exploit for PHP session.upload_progress pre-auth RCE (PHP2Shell), with heap/ASLR leak, per-build offset profiles, and an all-in-one…

Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environments.…

Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

CVE-2026-109618/109619 — 5 RCE chains + detection rules (Suricata, Sigma, ModSecurity). PHP session.upload_progress pre-auth exploit research.

CVE-2026-109618/109619 — PHP session.upload_progress pre-auth RCE. Exploit research: remote ASLR chain, PoC & patch analysis.

A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.

ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…

Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain

Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.

Proof-of-concept exploit for CVE-2021-21017, an Adobe Reader type confusion leading to out-of-bounds read and heap overflow, with technical analysis…

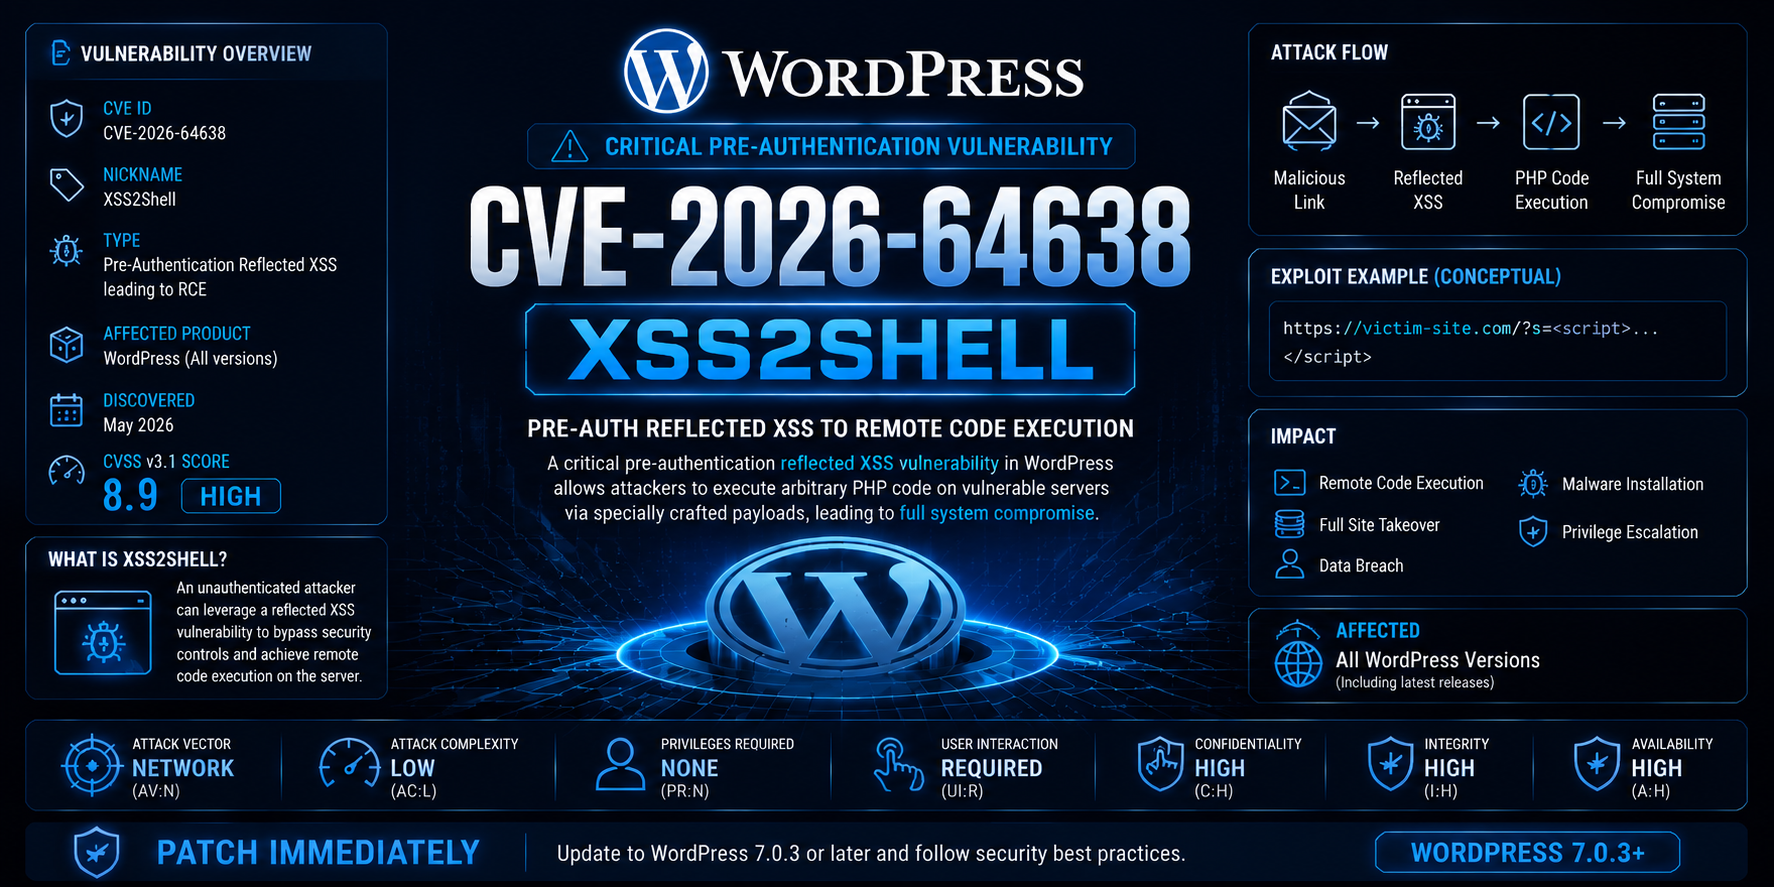
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…

Toy scripts for playing with WinDbg JS API