

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
50.1k2 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

 devianntsec/cve-2021-4034
Master's thesis research on CVE-2021-4034 (PwnKit) local privilege escalation. Multi-payload Python exploit with 7 modes including interactive shell,…
 thalium/icebox
Virtual Machine Introspection, Tracing & Debugging
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
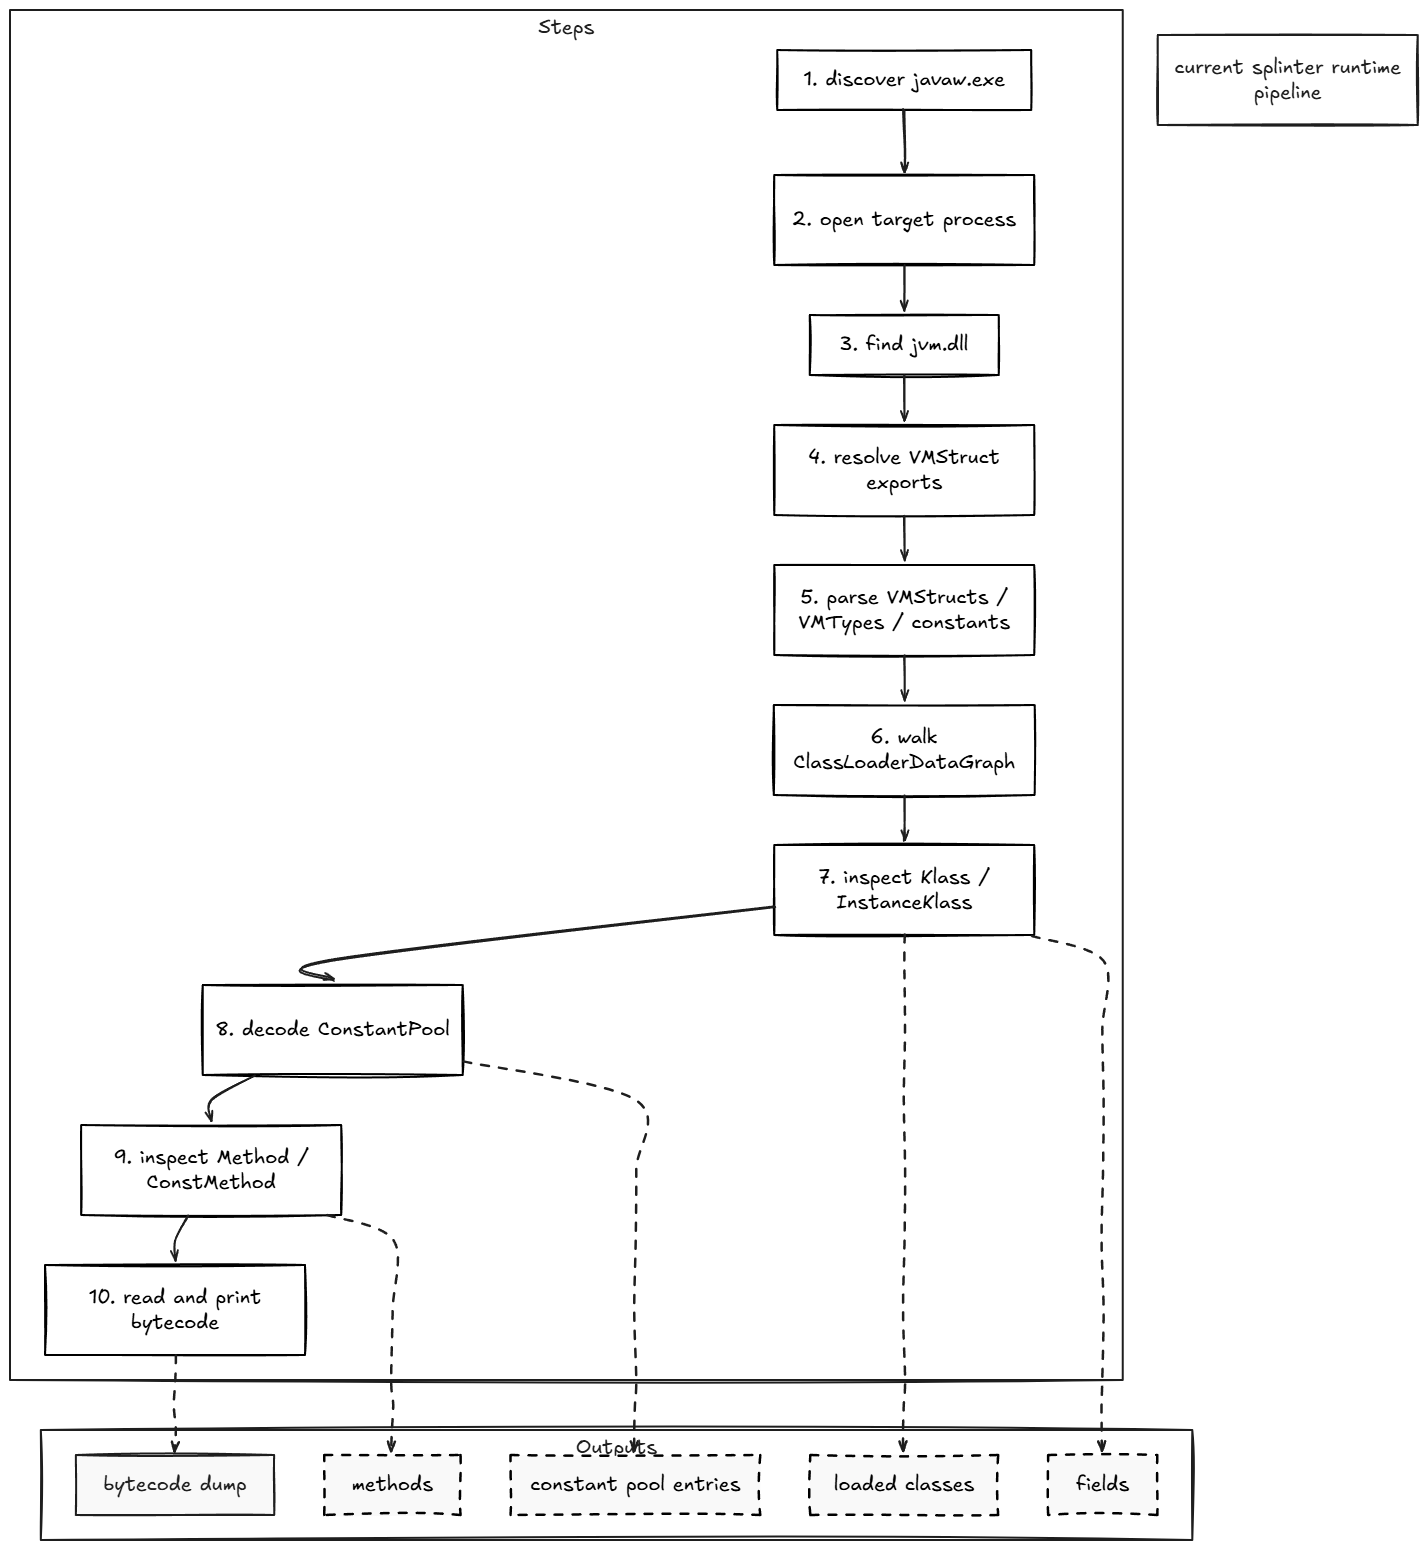 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 4d4j/cormem-read-poc
This tool demonstrates CVE-2026-38194, a vulnerability in Teledyne Digital Imaging Sapera Memory Manager (v9.0.0.0 and below). The CORMEM.SYS kernel…
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
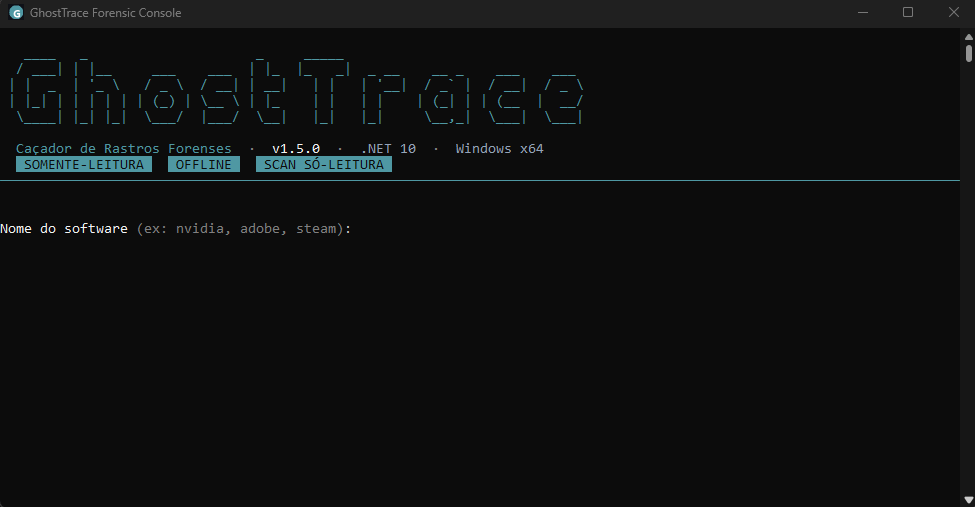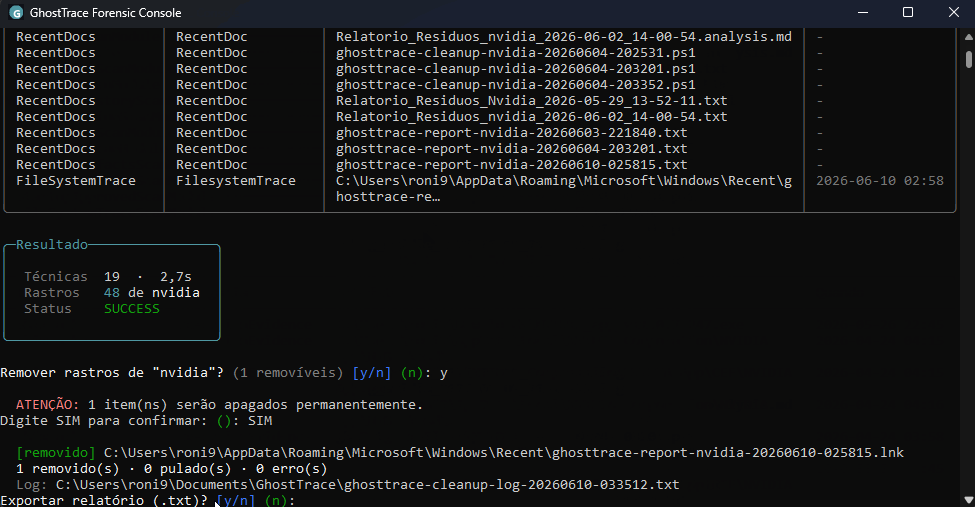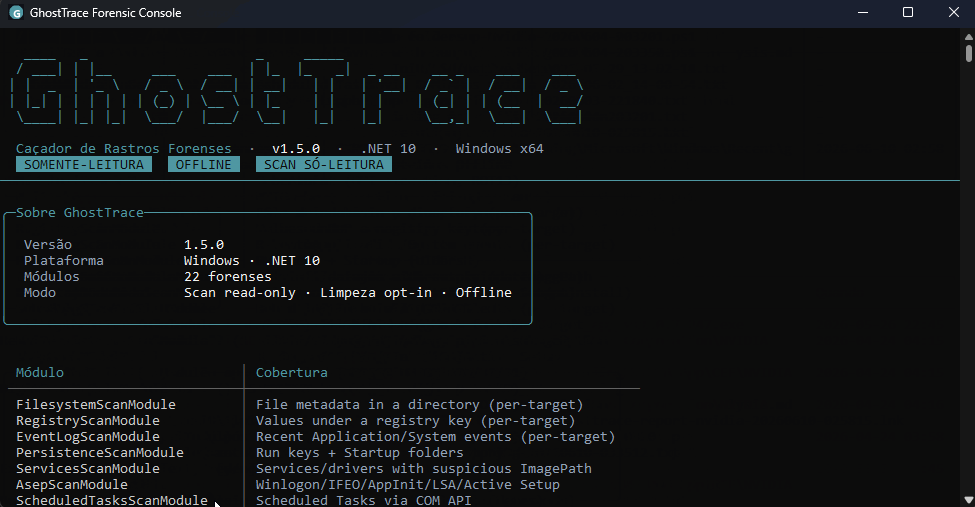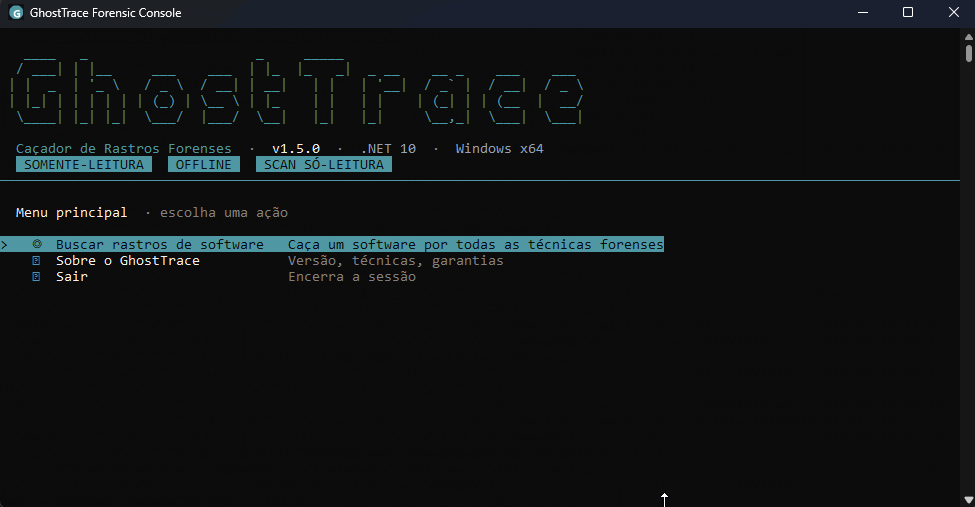 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 rainbowdynamix/ghostkatz
Dump LSASS via physical memory read primitives in vulnerable kernel drivers
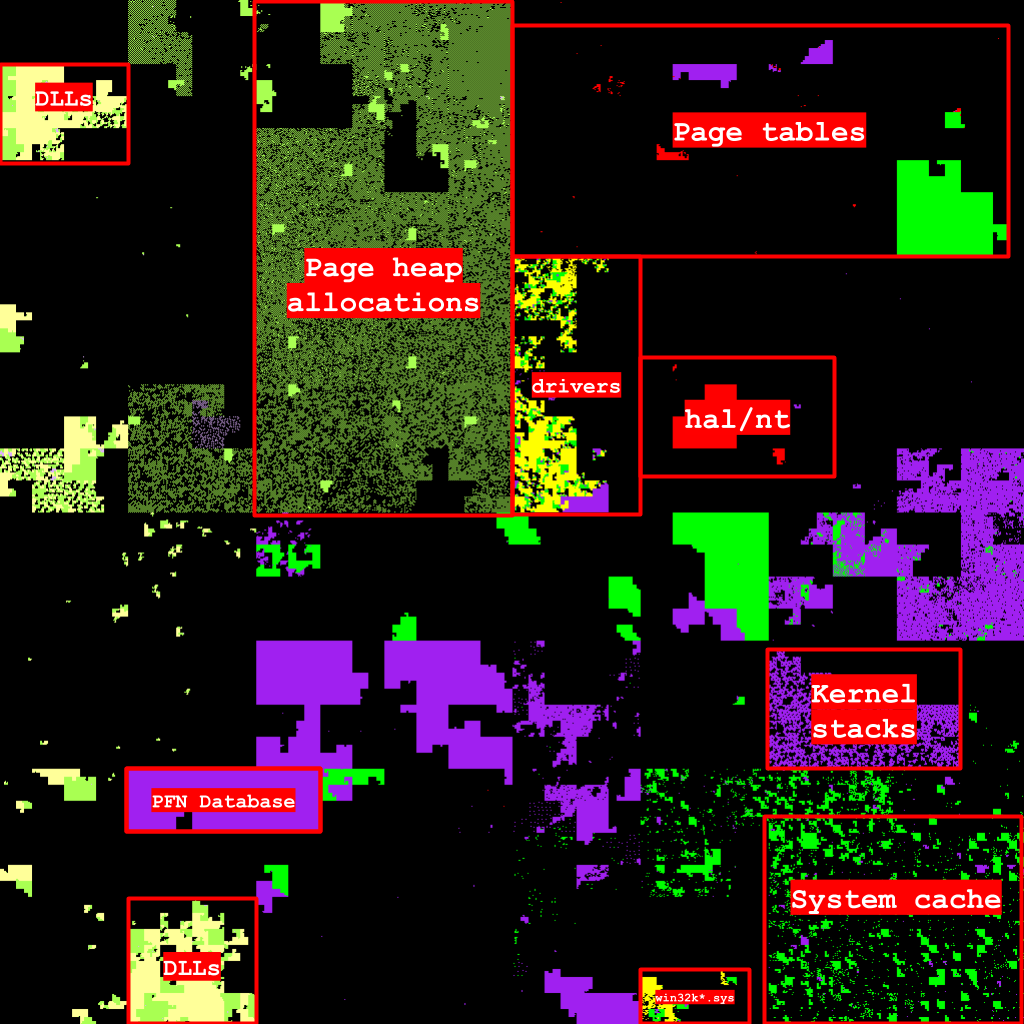 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.
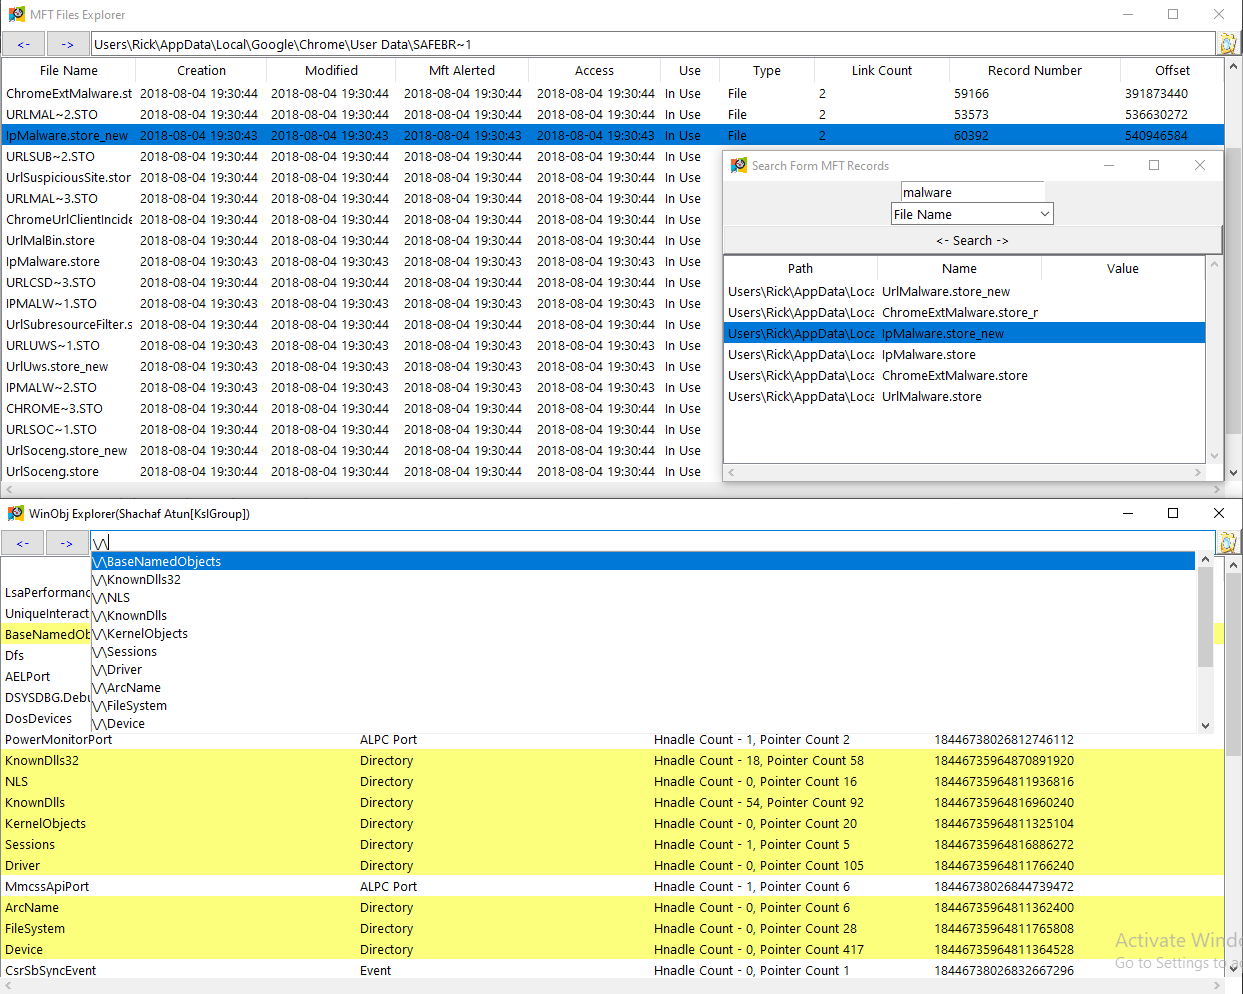 memoryforensics1/volexp
volatility explorer (volatility 2)
 gmh5225/lithium-kernel
Windows kernel-mode driver with user-mode client exposing IOCTL-based physical and virtual memory read/write, page table walking, pattern scanning,…
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
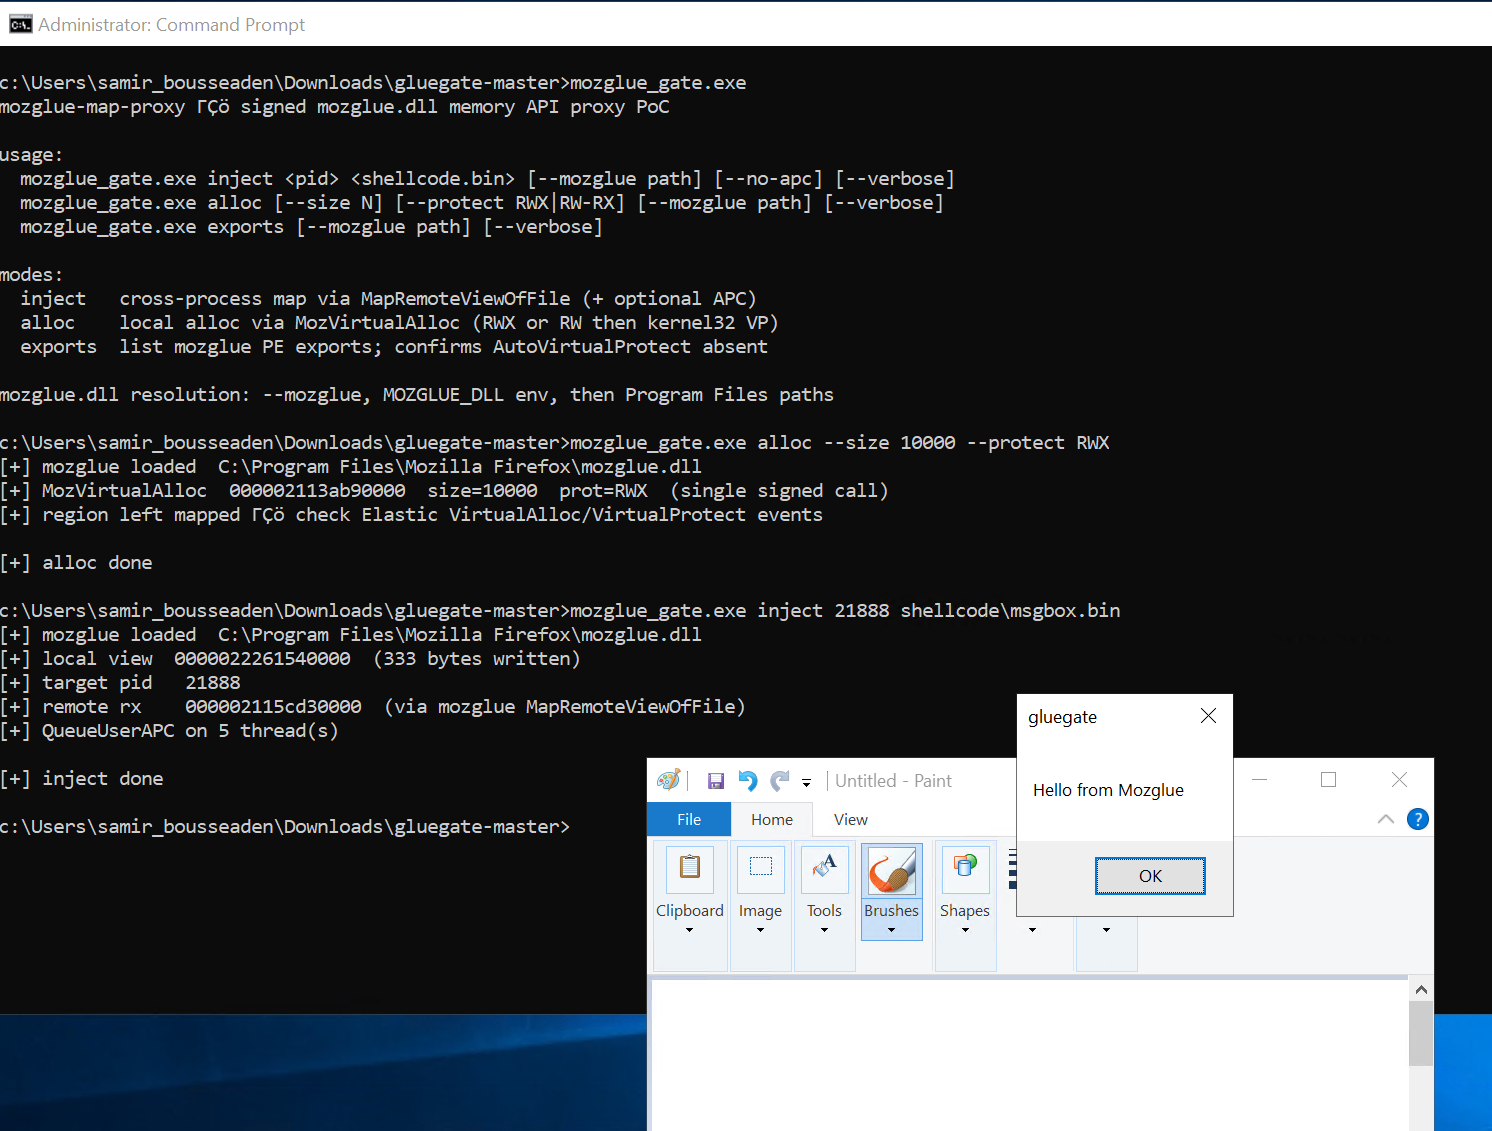 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
 0xcyberstan/cve-2026-46215-poc
Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…
 seemoo-lab/dtrace-memaccess_cve-2020-27949
Proof-of-concept exploit for CVE-2020-27949, demonstrating arbitrary memory read/write in macOS processes via DTrace fasttrap ioctl without elevated…
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass