

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.1k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

 zodiacon/alltools
All reasonably stable tools
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 rshipp/awesome-malware-analysis
Defund the Police.
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
 antisurveillanceagency/shadownet
ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…

 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 var77/cve-2026-2005
PoC for CVE-2026-2005
 gabriellandau/edrsandblast-godfault
EDRSandblast-GodFault
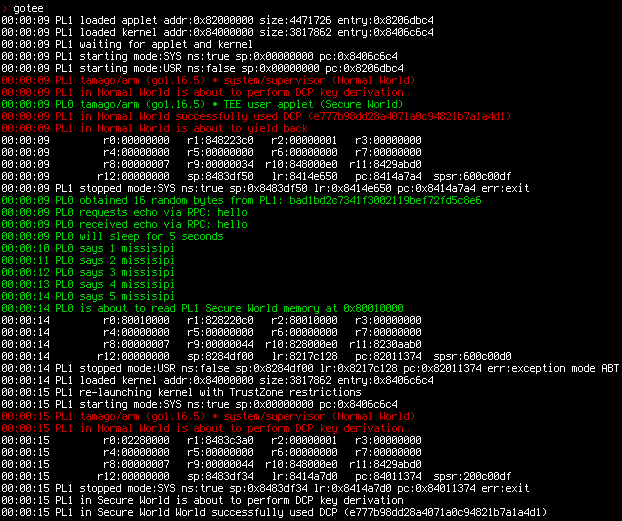 usbarmory/gotee-example
GoTEE - example application
 krish-foren6/cve-2026-31431-report-copy-fail-vulnerability-
Detailed analysis of the Copy Fail vulnerability (CVE-2026-31431) in the Linux kernel, including memory corruption mechanism, privilege escalation…