


 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
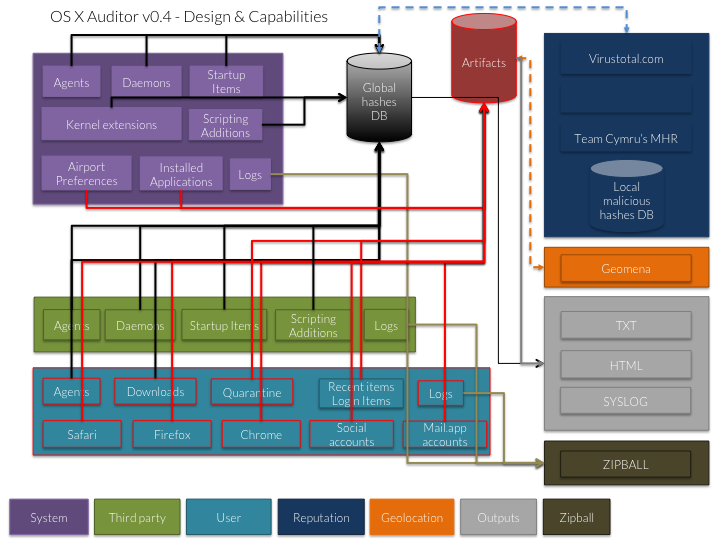 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 fboldewin/atmmalscan
Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys