
salt
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
binary-analysisdebuggerseducation+2
paolomonti42/saltSALT - SLUB ALlocator Tracer for the Linux kernel
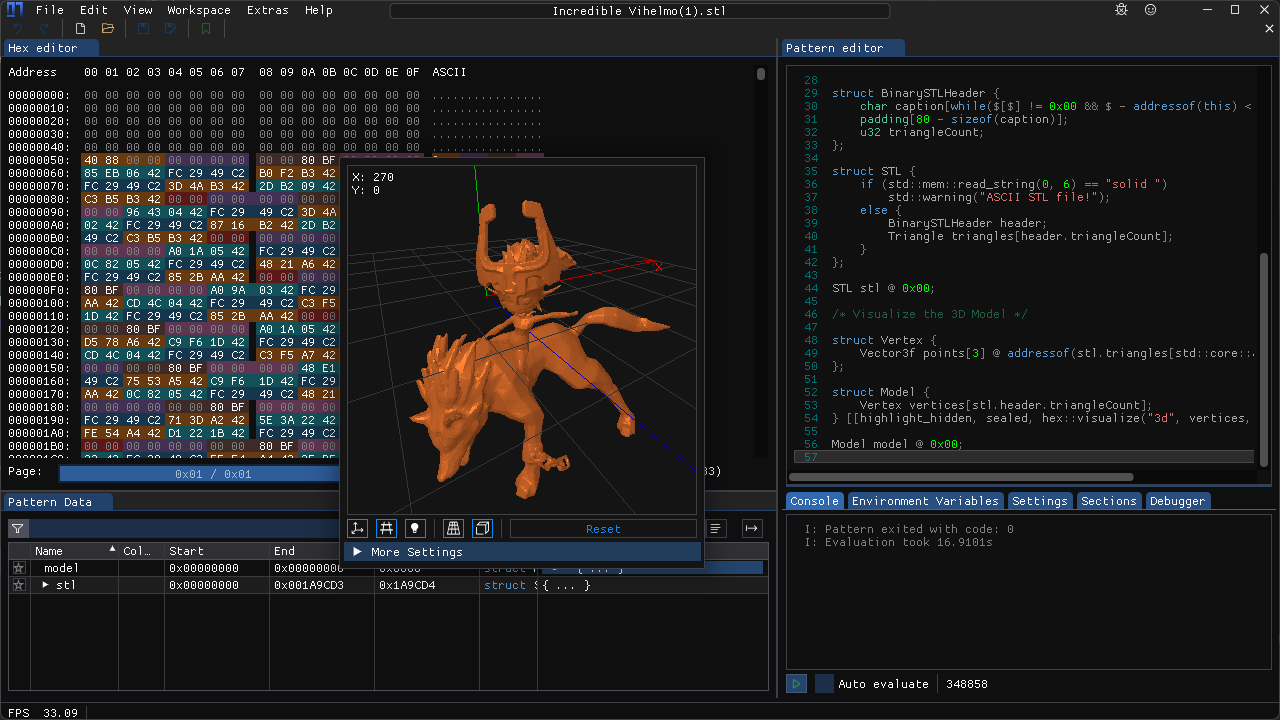 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 zodiacon/alltools
All reasonably stable tools
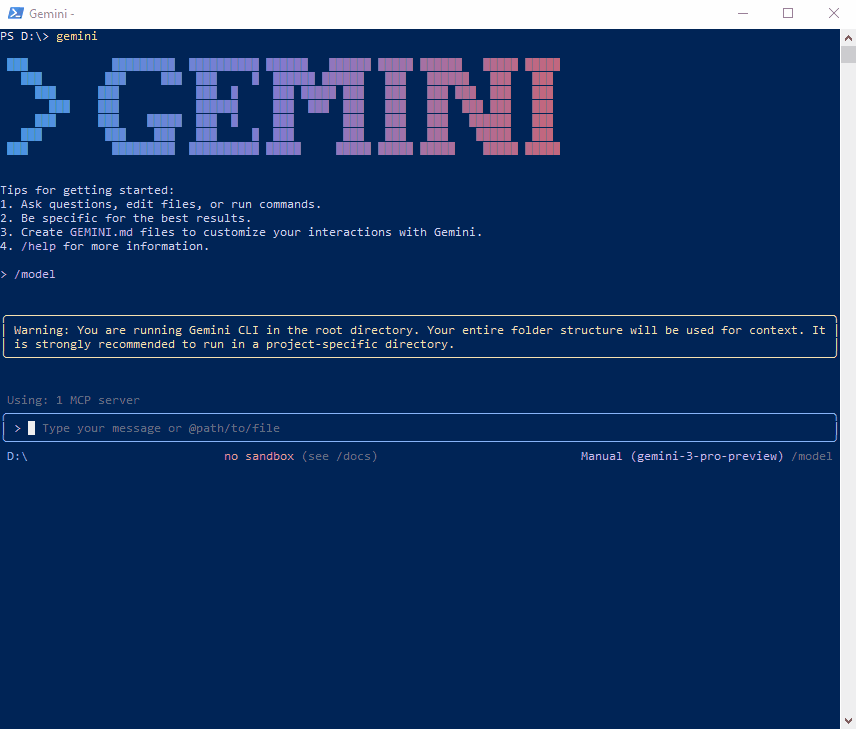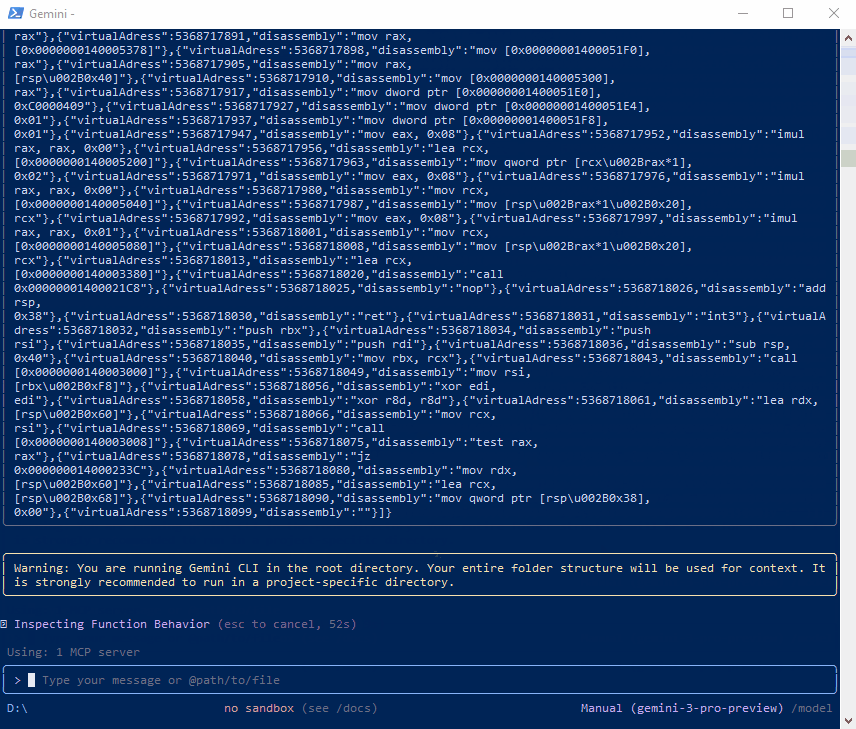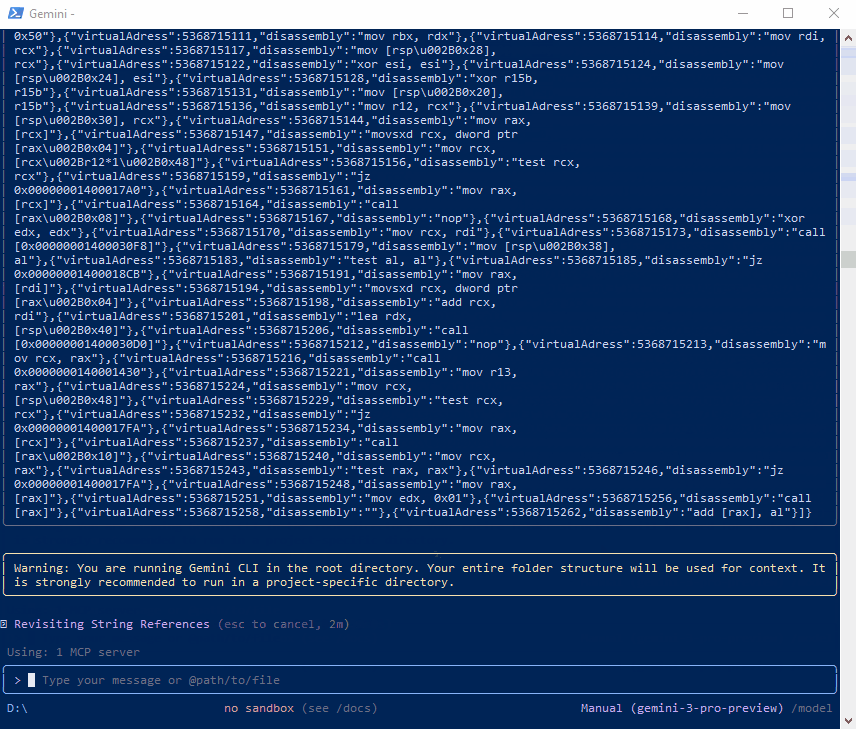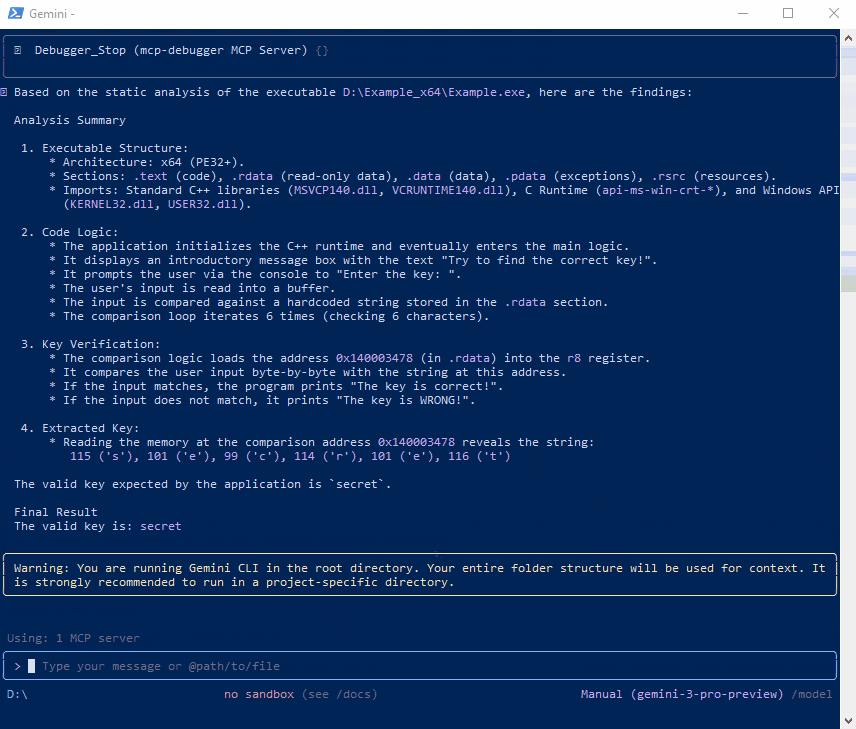 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 pinksawtooth/how_to_become_a_malware_analyst
Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
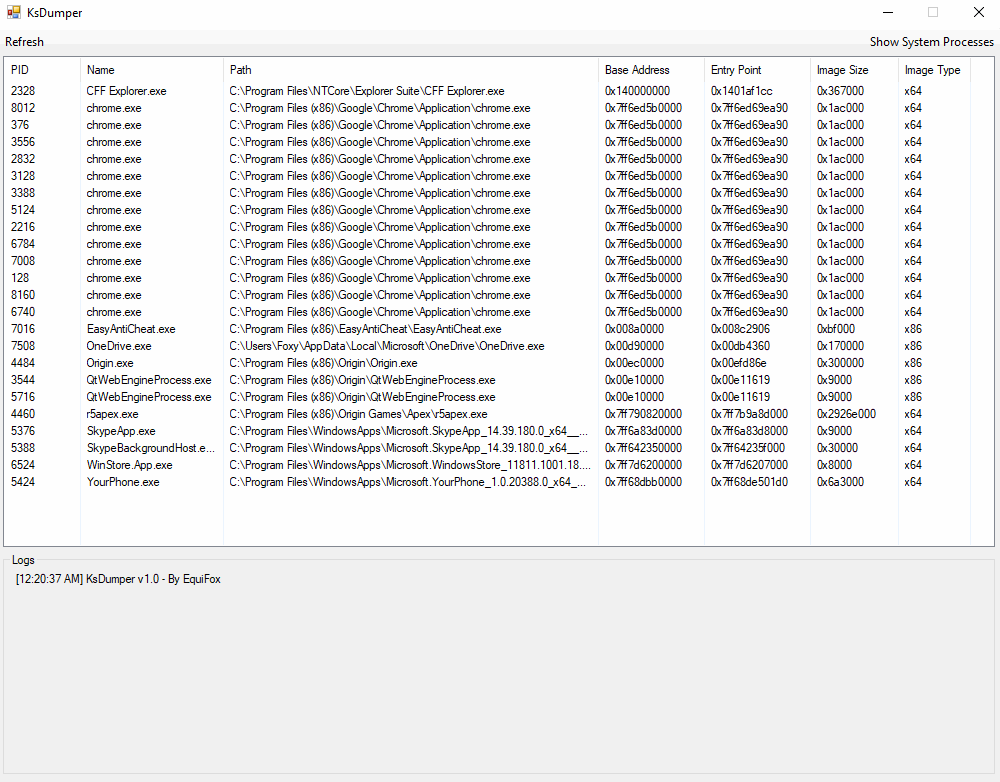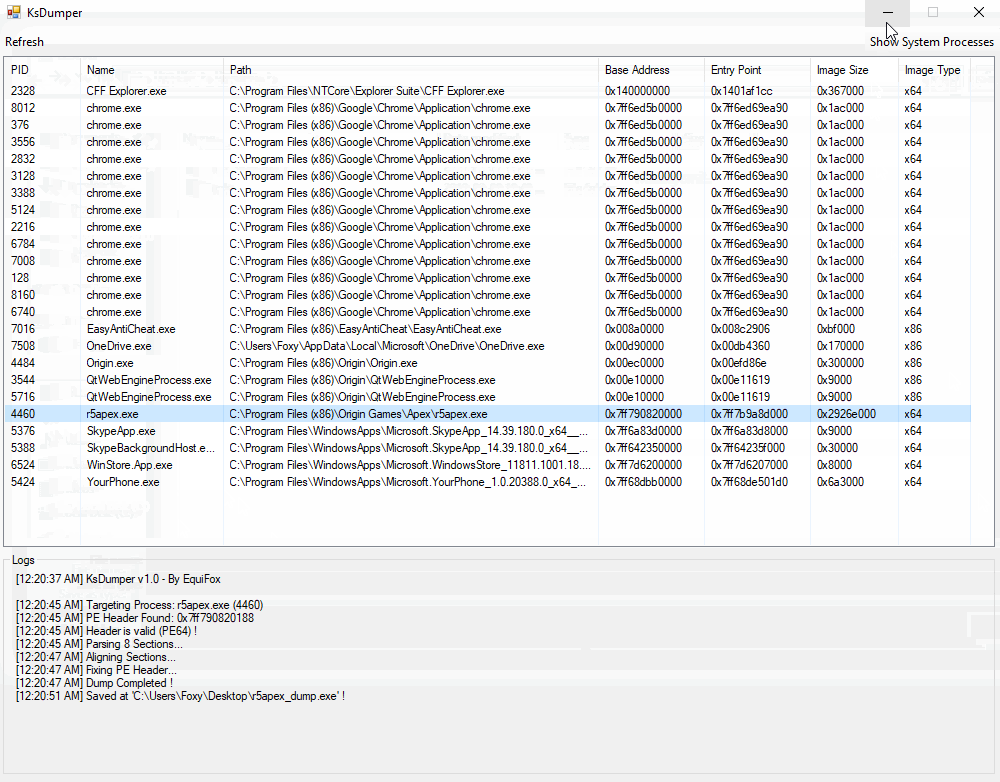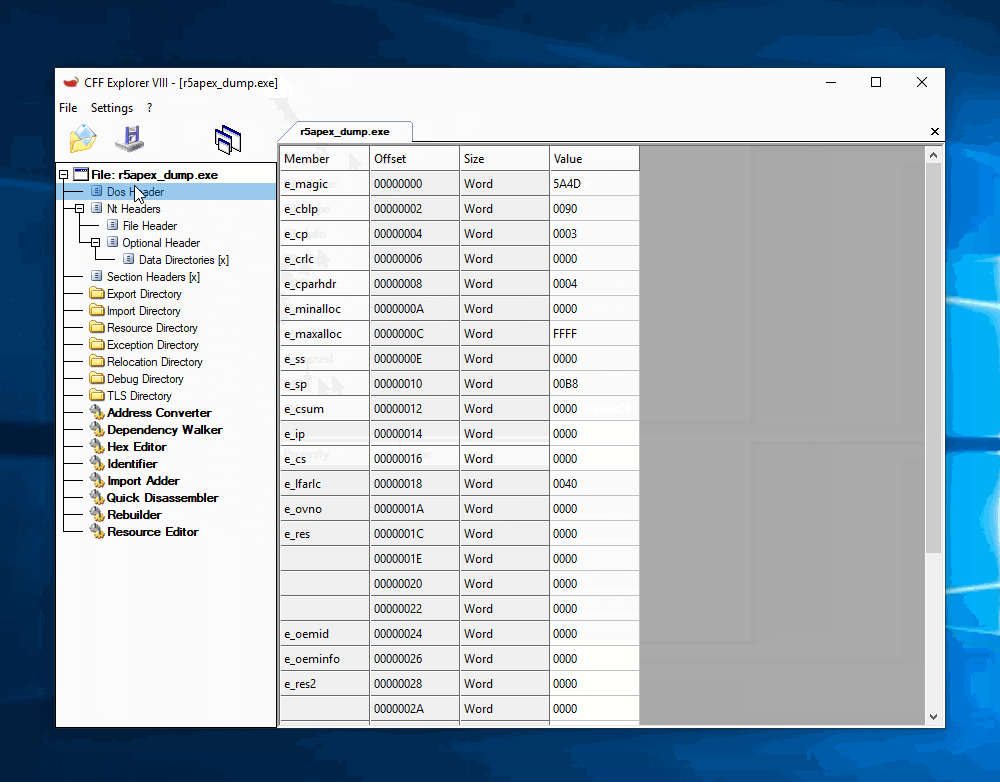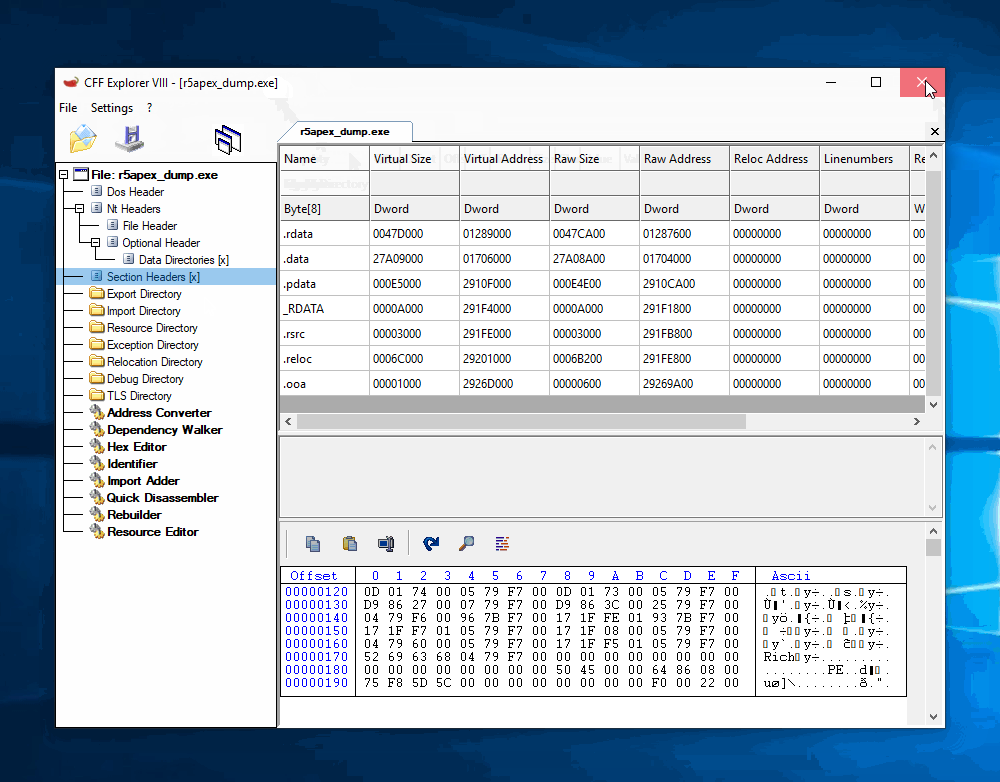 equifox/ksdumper
Dumping processes using the power of kernel space !
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
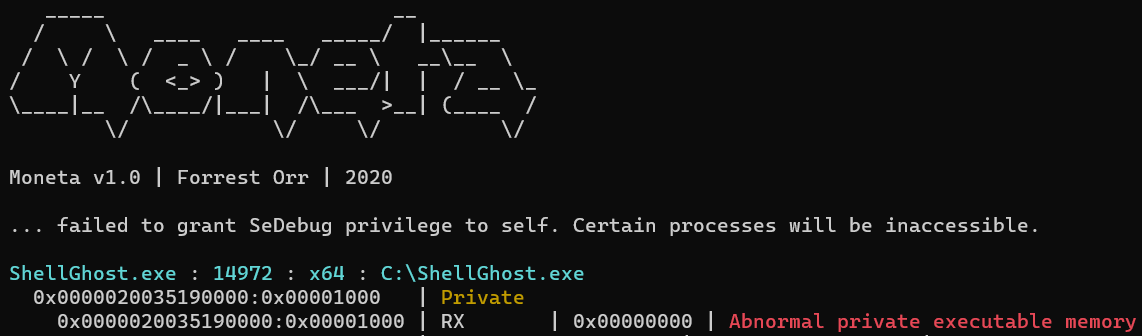 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 thiasap/oppo-pgem10-ghostlock
OPPO Find X6 Pro GhostLock (CVE-2026-43499) exploit adaptation
 volatilityfoundation/volatility
An advanced memory forensics framework
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
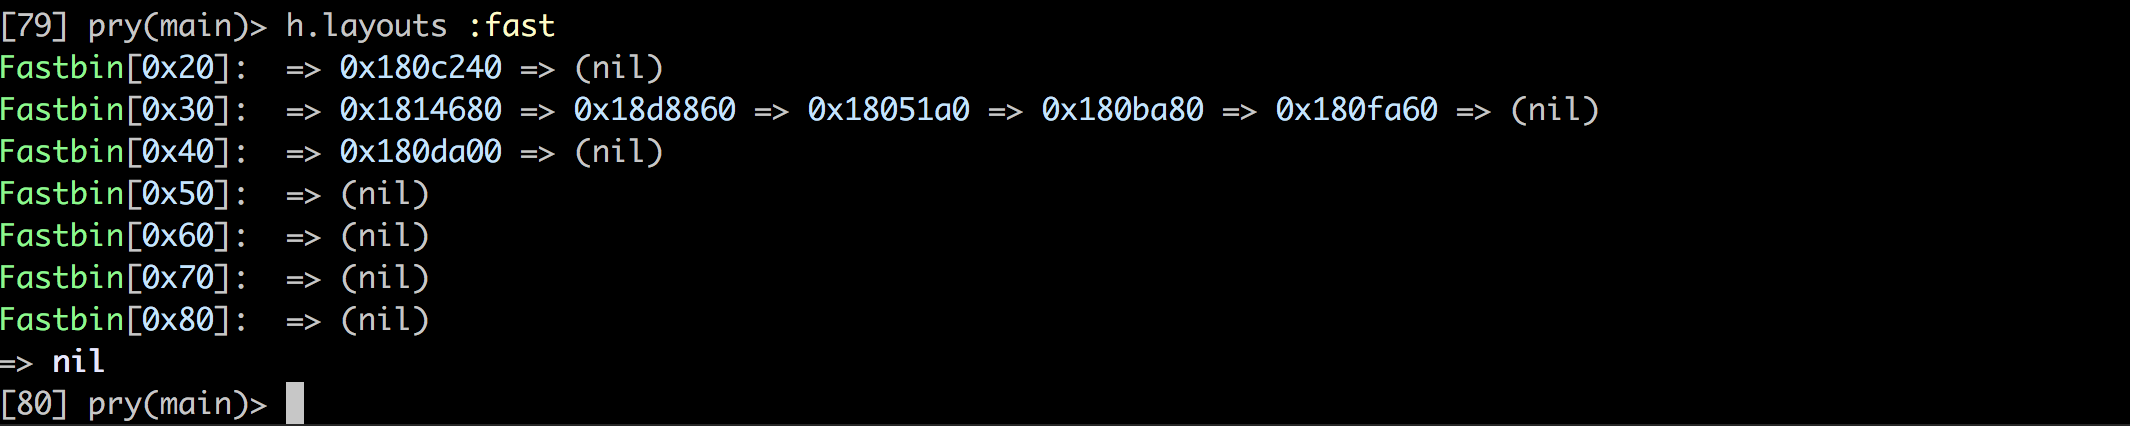 david942j/heapinfo
An interactive memory info for pwning / exploiting
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 abhinavagarwal07/gdcm-security-poc
Private end-to-end sanitizer reproduction package for six GDCM findings