Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
59 results
php2shell-bypass-aslr-exp preview

php2shell-bypass-aslr-exp

GitHub9bie/php2shell-bypass-aslr-exp

Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…

binary-exploitationexploitationmemory-forensics+4
1.5k
10 days ago
php-cve-2026-10961x-lab-poc preview

php-cve-2026-10961x-lab-poc

GitHubdinosn/php-cve-2026-10961x-lab-poc

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

binary-exploitationexploitationfuzzing+7
1144 days ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

digital-forensicsdisk-forensicsforensics+5
906 months ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1202 years ago
LiME preview

LiME

GitHubjtsylve/lime

Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.

digital-forensicsforensicsincident-response+2
2.1k7 months ago
samsung_tizen_tv_root preview

samsung_tizen_tv_root

GitHubcommit-regrets/samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

binary-exploitationembedded-systems-securityexploitation+8
156 days ago
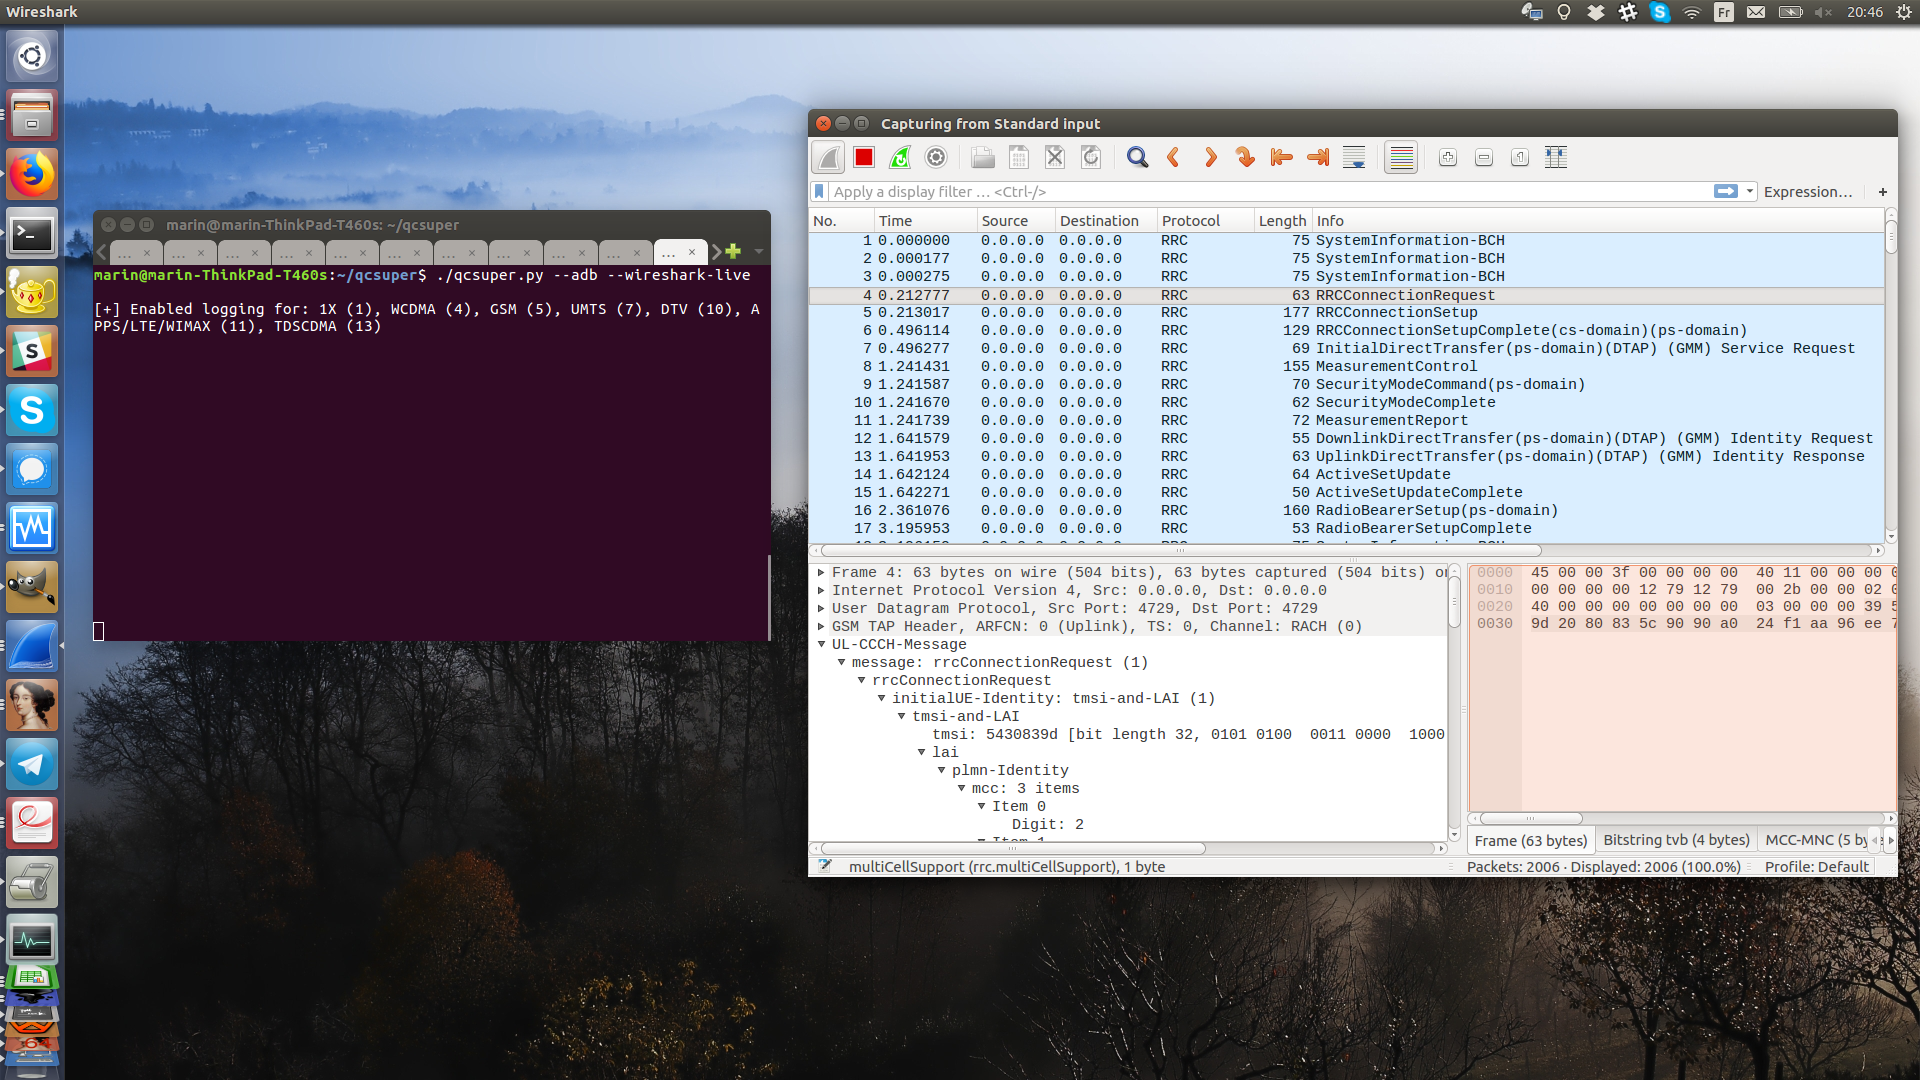
QCSuper preview

QCSuper

GitHubp1sec/qcsuper

QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.

embedded-systems-securitymemory-forensicsmobile-forensics+4
1.6k14 days ago
pcileech preview

pcileech

GitHubufrisk/pcileech

Direct Memory Access (DMA) Attack Software

digital-forensicsexploitationhardware-security+7
7.9k28 days ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

digital-forensicsforensicsincident-response+3
1.4k1 month ago
CVE-2026-23111 preview

CVE-2026-23111

GitHub0xblackash/cve-2026-23111

CVE-2026-23111

binary-exploitationexploitationmemory-forensics+2
54 months ago
dumpscan preview
Archived

dumpscan

GitHubdaddycocoaman/dumpscan

Finding secrets in kernel and user memory

cryptographydigital-forensicsencryption-decryption-tools+4
1183 years ago
CVE-2023-32784-kdbxpassdmp preview

CVE-2023-32784-kdbxpassdmp

GitHubamperclock/cve-2023-32784-kdbxpassdmp

Retrieves the master password from Keepass memory dump, using a hint of bruteforce.

digital-forensicsexploitationforensics+3
5 months ago
nanodump preview

nanodump

GitHubfortra/nanodump

The swiss army knife of LSASS dumping

exploitationmemory-forensicspayload-development+4
2.1k2 years ago
Platbox preview

Platbox

GitHubioactive/platbox

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…

binary-analysisfirmware-analysisfuzzing+3
2211 year ago
aes-finder preview

aes-finder

GitHubmmozeiko/aes-finder

Utility to find AES keys in running processes

binary-analysiscryptographyencryption-decryption-tools+2
1.1k9 years ago
umbra preview

umbra

GitHubymsniper/umbra

External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…

exploitationmemory-forensicsred-teaming+1
1828 days ago
PPPoEject preview

PPPoEject

GitHubmanizada/pppoeject

Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.

binary-exploitationexploitationmemory-forensics+4
71 month ago
libunwind_CVE-2015-3239 preview

libunwind_CVE-2015-3239

GitHubrenukaselvar/libunwind_cve-2015-3239

C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…

binary-analysisdebuggersexploitation+3
1 year ago
Previous1234Next