systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.4k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 darthton/blackbone
Windows memory hacking library
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 zodiacon/alltools
All reasonably stable tools
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
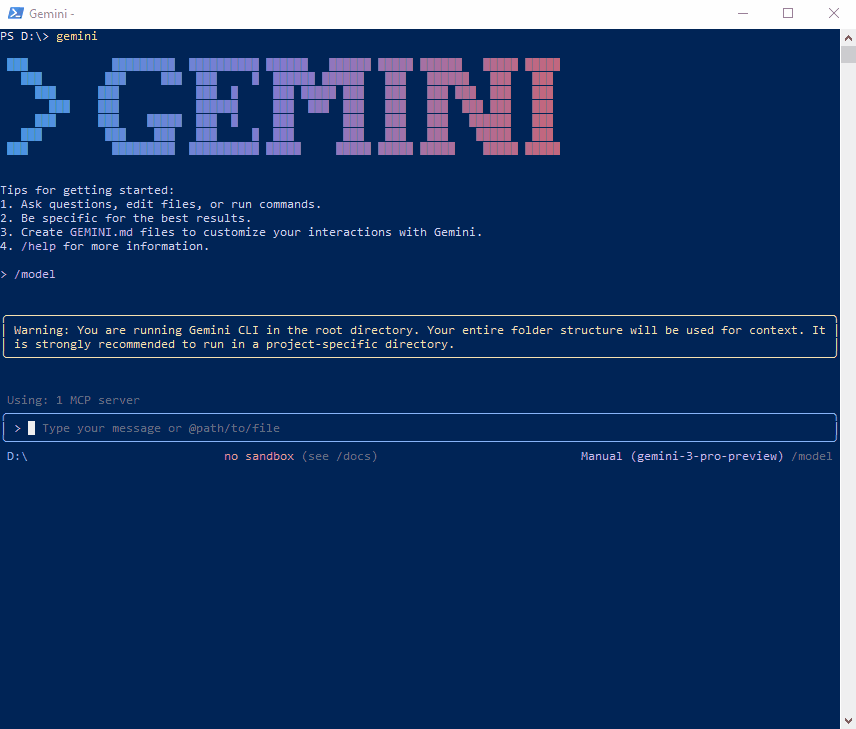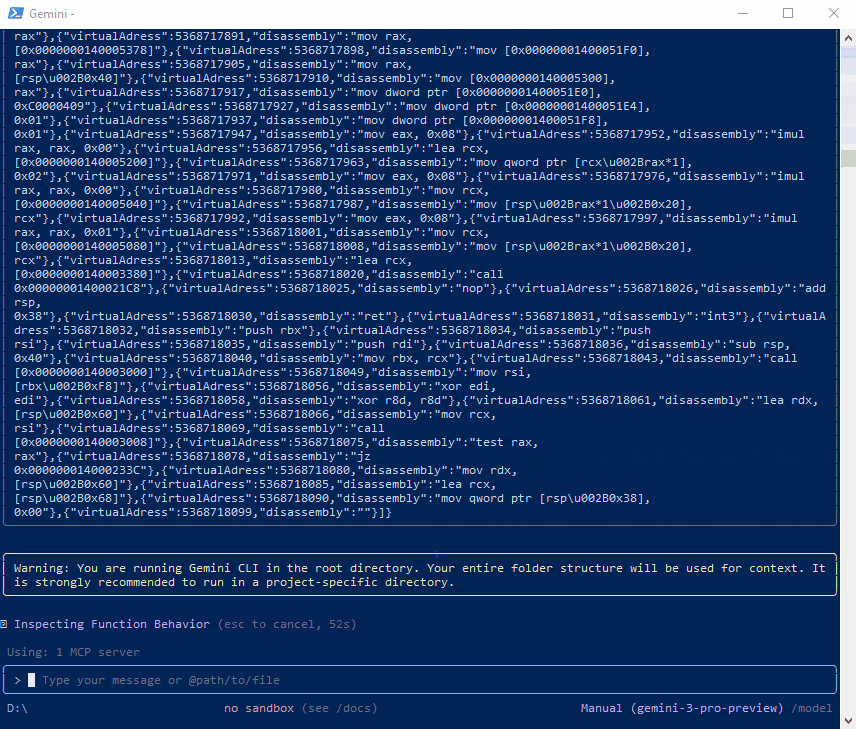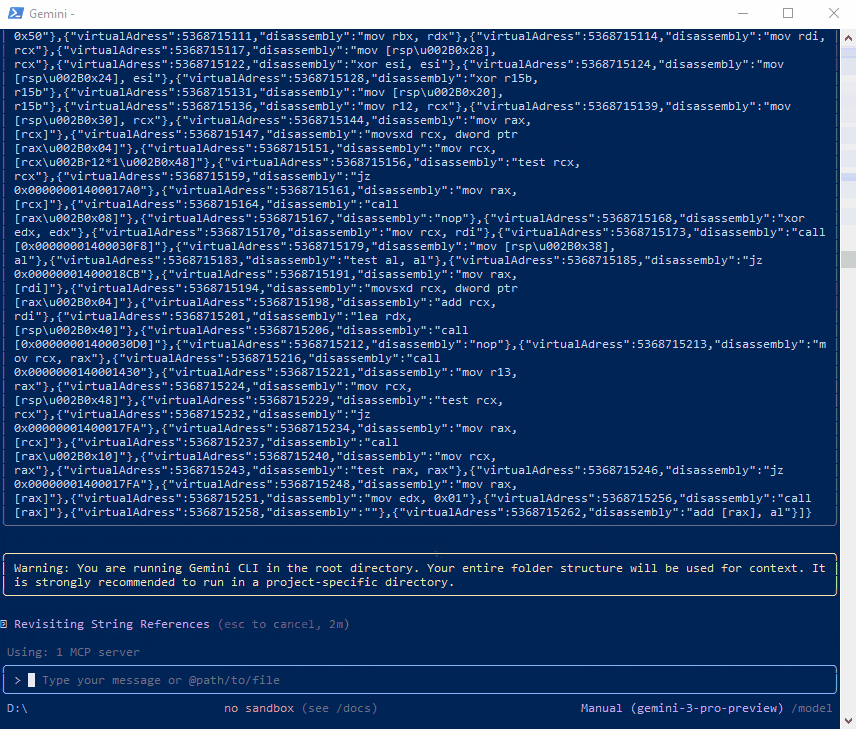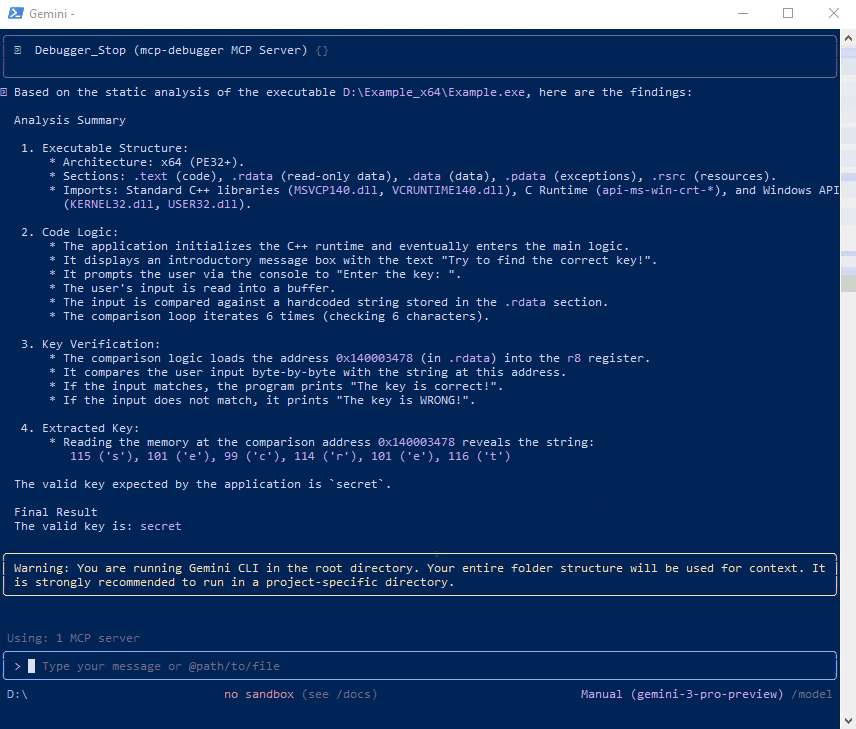 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
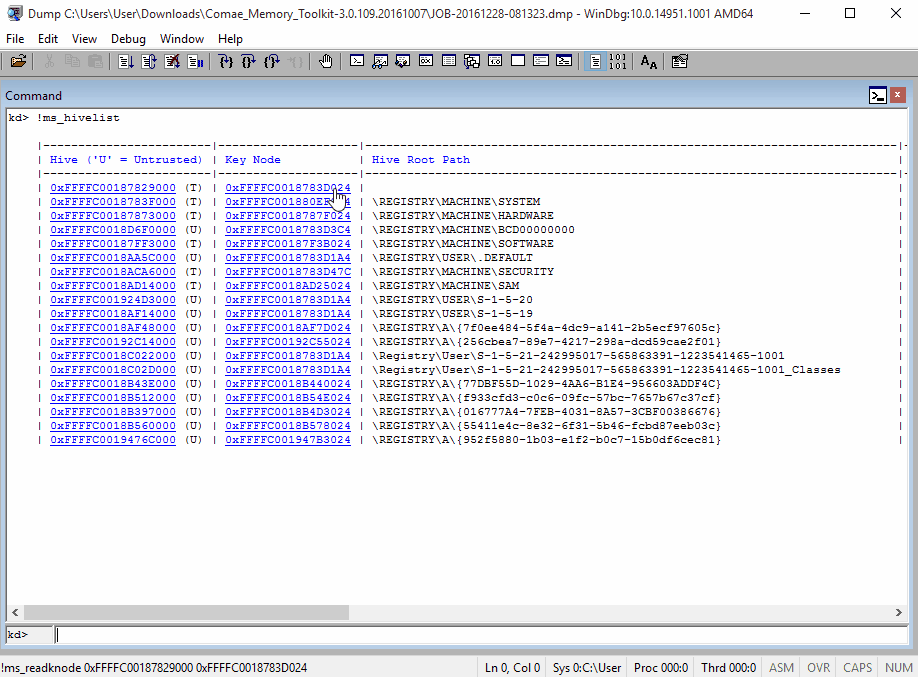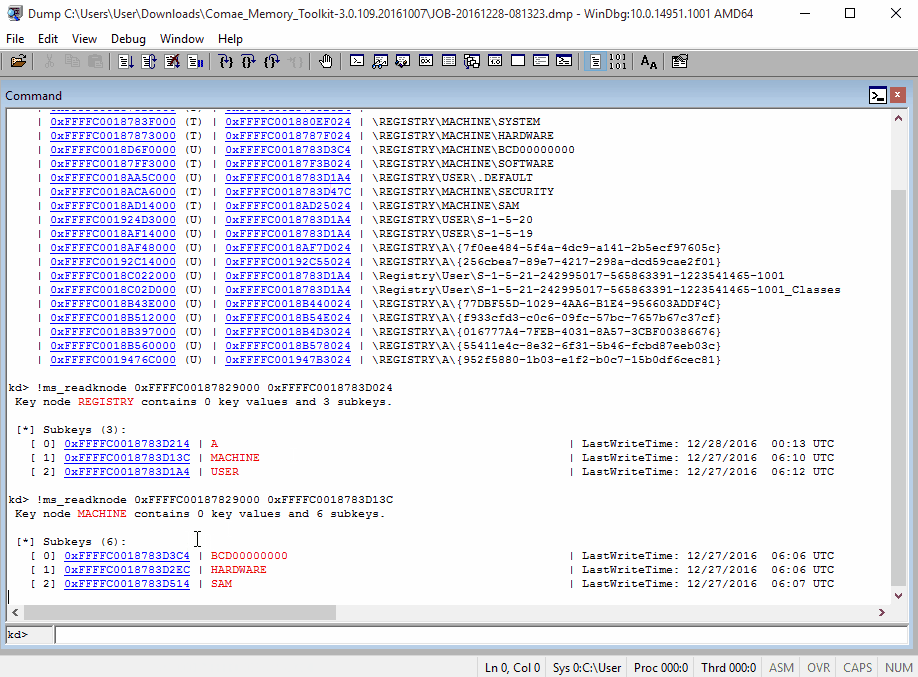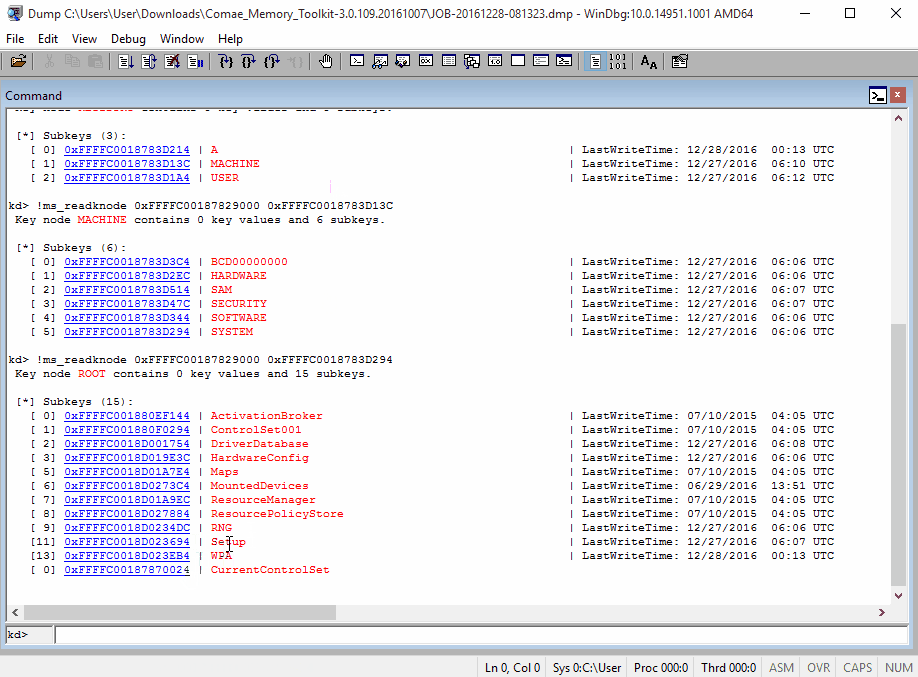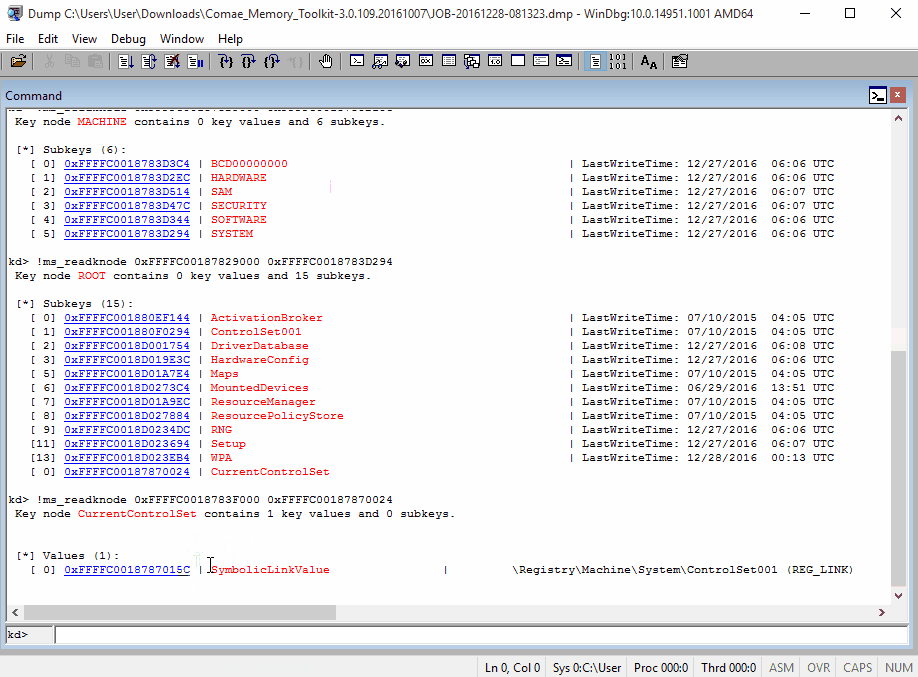 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
 cecio/xenoboxx
Hardware Sandbox Toolkit
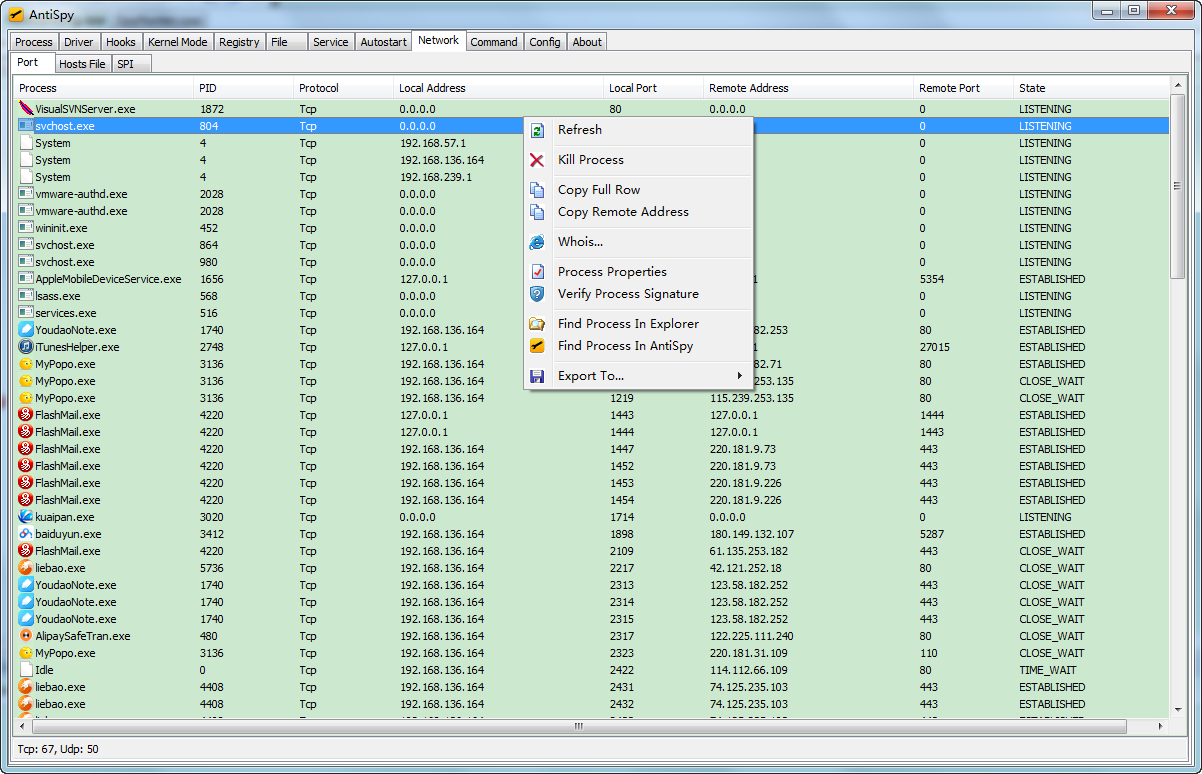 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.