Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
168 results
php2shell-bypass-aslr-exp preview

php2shell-bypass-aslr-exp

GitHub9bie/php2shell-bypass-aslr-exp

Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…

binary-exploitationexploitationmemory-forensics+4
1.5k

6 days ago
ghostlock-cve-2026-43499-4.19-k40 preview

ghostlock-cve-2026-43499-4.19-k40

GitHubccp-p/ghostlock-cve-2026-43499-4.19-k40

Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.

android-securitybinary-exploitationexploitation+6
91 month ago
RootMyVivo-Exploit preview

RootMyVivo-Exploit

GitHubzenyxx-xd/rootmyvivo-exploit

GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.

android-securitybinary-exploitationexploitation+5
615 days ago
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset

ai-assisted-reversingandroid-securitybinary-analysis+16
25.2k20h 6m ago
ghidra preview

ghidra

GitHubnationalsecurityagency/ghidra

Ghidra is a software reverse engineering (SRE) framework

ai-assisted-reversingandroid-securitybinary-analysis+17
95.9k13h 3m ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…

binary-exploitationdebuggerseducation+7
52 months ago
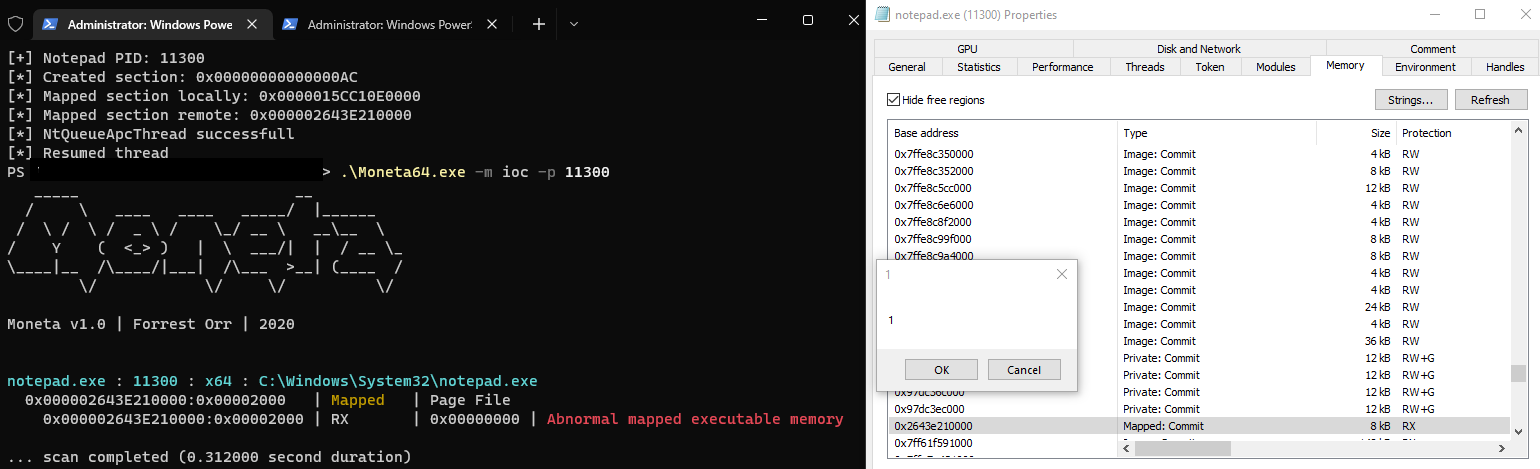
DeepSleep preview

DeepSleep

GitHubtheflink/deepsleep

A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC

exploitationmemory-forensicspayload-development+1
3744 years ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
8255 months ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k9 months ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

encryption-decryption-toolsforensicshash-analysis+8
11.1k1 year ago
oppo-ghostlock preview

oppo-ghostlock

GitHubpubglite55/oppo-ghostlock

OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation

android-securitybinary-exploitationeducation+7
6612h 9m ago
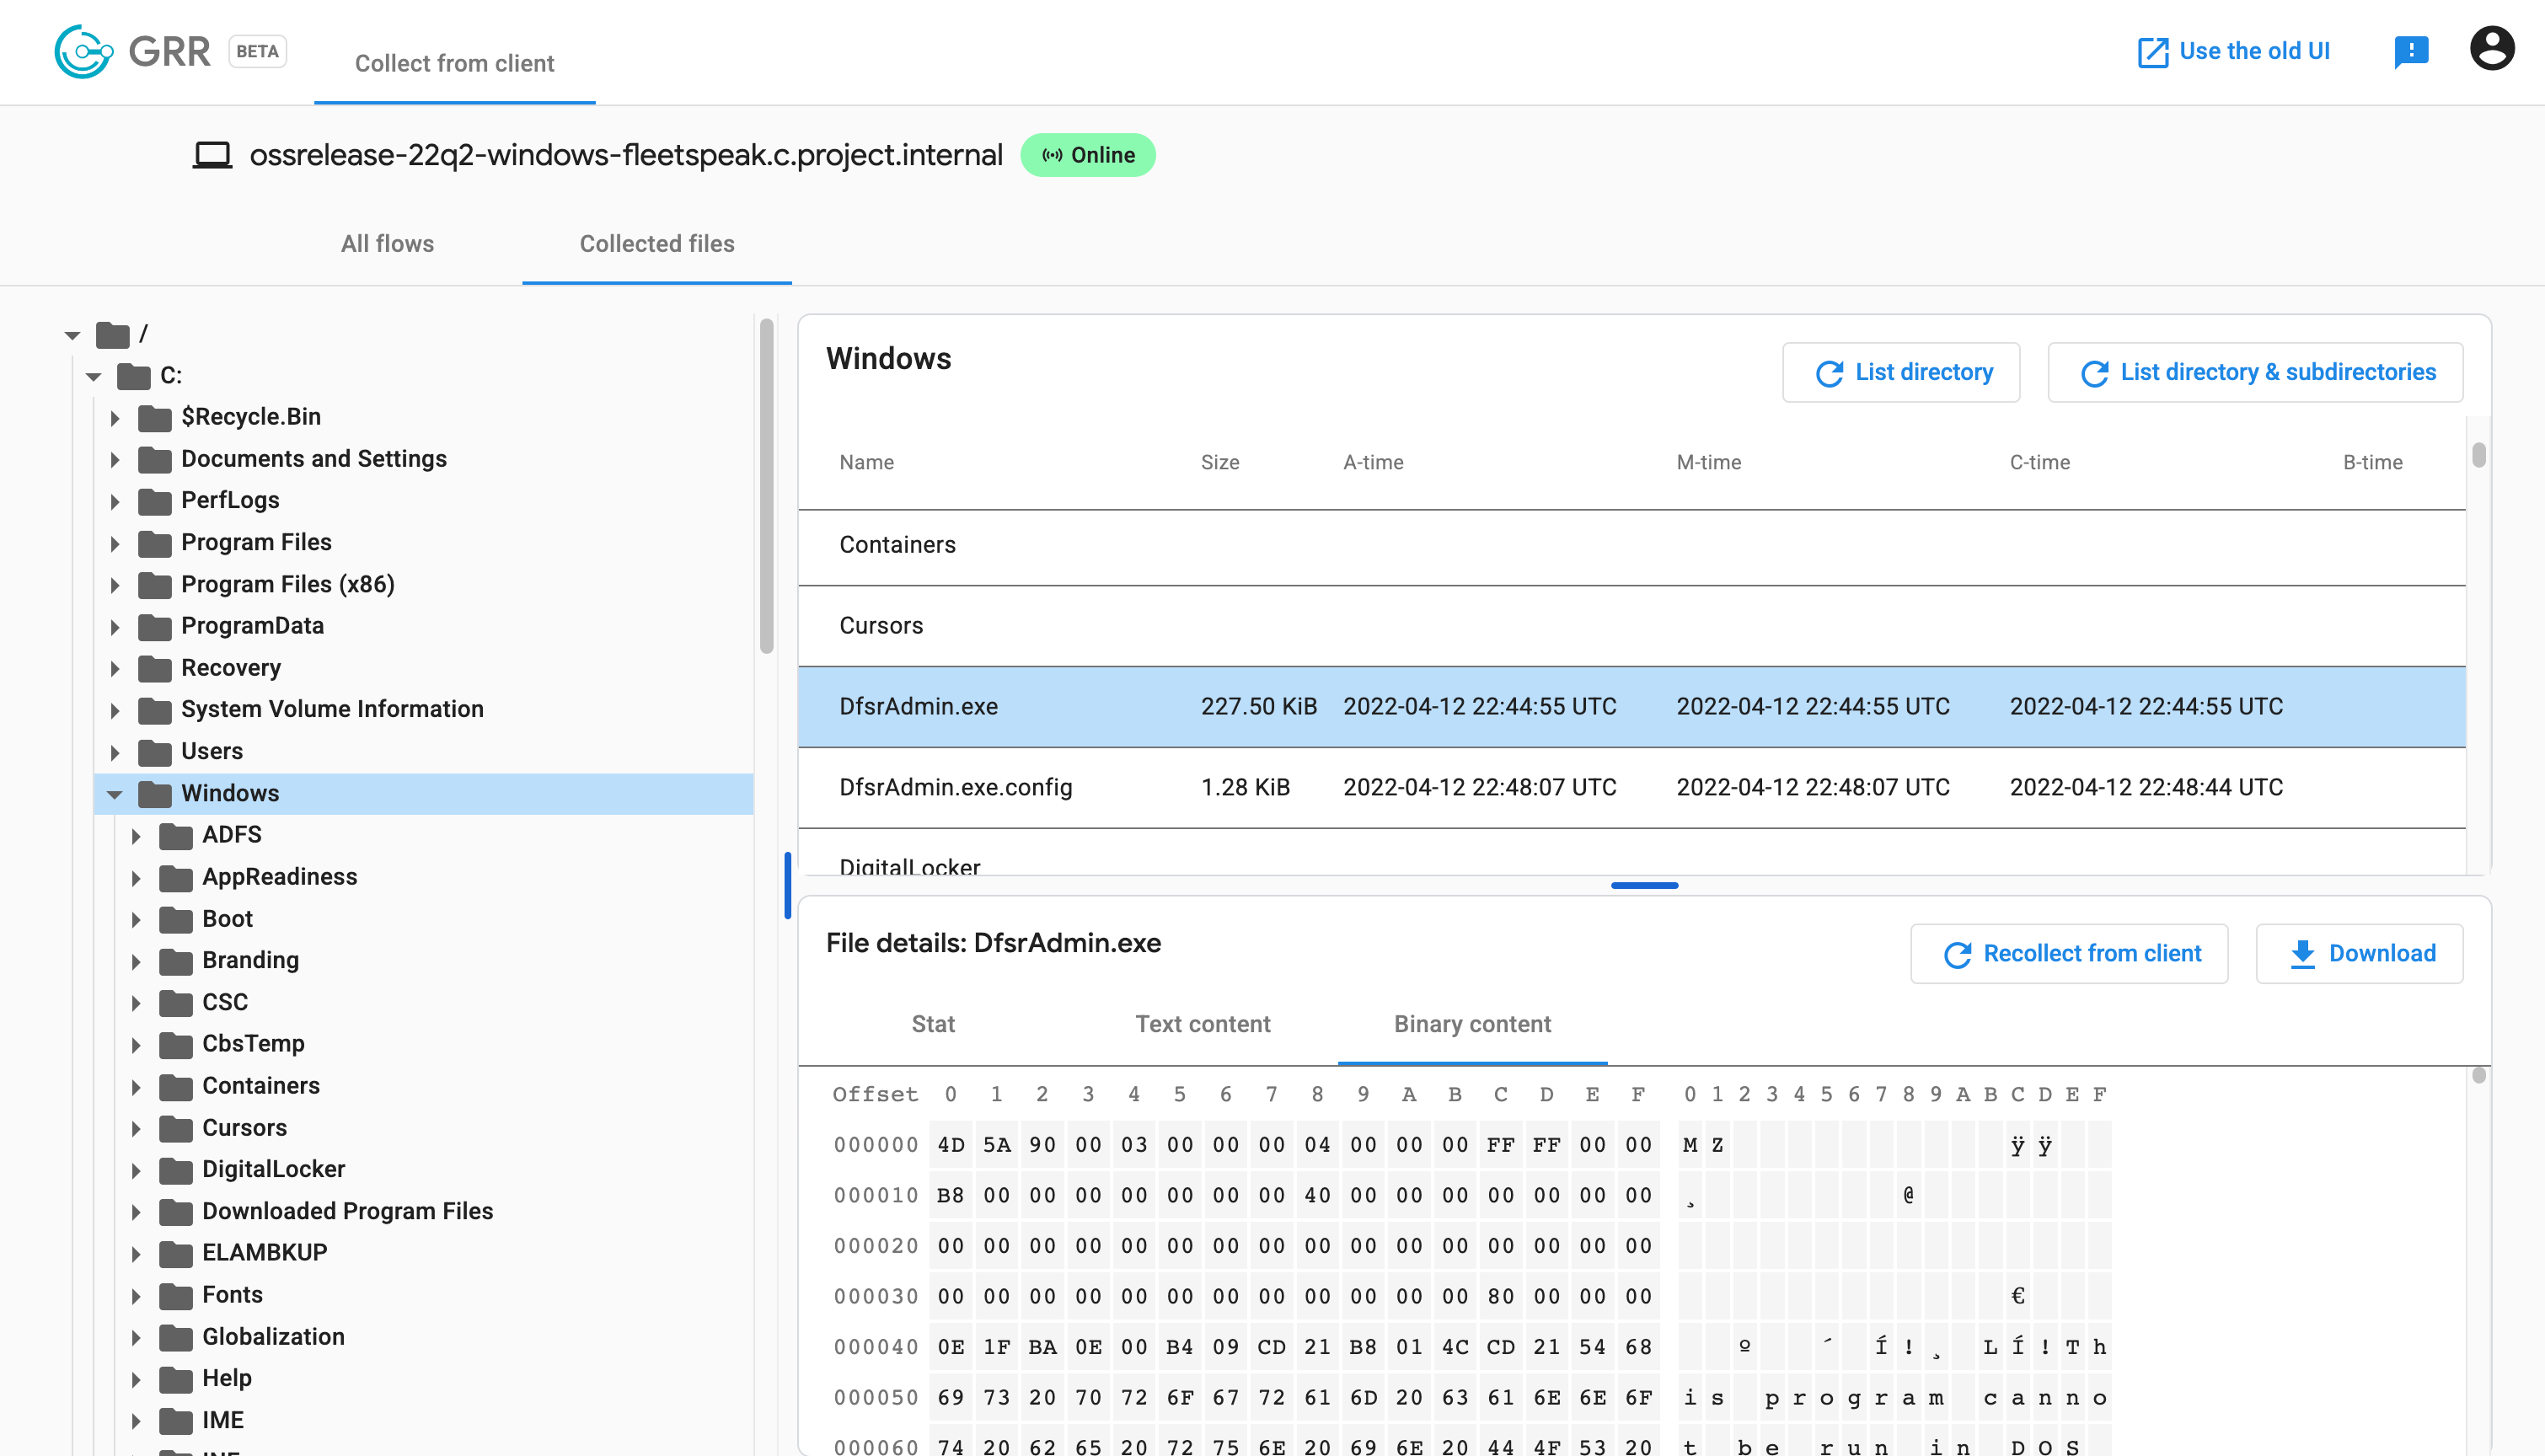
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k28 days ago
zenfone9-root preview

zenfone9-root

GitHubramenfast/zenfone9-root

Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.

android-securitybinary-exploitationexploitation+7
41 month ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.5k16 days ago
CVE-2026-43499-S26 preview

CVE-2026-43499-S26

GitHubsammyenigma/cve-2026-43499-s26

Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…

android-securitybinary-exploitationexploitation+8
2 months ago
objection preview

objection

GitHubsensepost/objection

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

android-securitydynamic-analysis-sandboxingexploitation+9
9.5k2 days ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.5k17 days ago
ios.CVE-2026-84616-84607 preview

ios.CVE-2026-84616-84607

GitHubping-2o/ios.cve-2026-84616-84607

research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607

binary-analysiseducationexploitation+6
101 month ago
Previous12…10Next