

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
9 results
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.6k4 years ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
exploitationmemory-forensicspayload-development+2
3.4k13 years ago
zirconium preview

zirconium

GitHubrobertmotr/zirconium

DLL-injectable internal game cheat for Plutonium BO2 zombies
exploitationmemory-forensicspenetration-testing+2
132 months ago
MappedImagesDetector preview

MappedImagesDetector

GitHubadem-hosni/mappedimagesdetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

anomaly-detectionbinary-analysisdefensive-tools+4
110 months ago
NativeMirror preview

NativeMirror

GitHubhabanada/nativemirror

Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.

binary-analysisdefensive-toolsdigital-forensics+4
57 days ago
WHFB-PinCapture preview

WHFB-PinCapture

GitHubivancabrera02/whfb-pincapture

Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…
debuggersinformation-gatheringmemory-forensics+5
614 days ago
VMInjector preview

VMInjector

GitHubhzphreak/vminjector

DLL Injection tool to unlock guest VMs
authentication-authorizationbinary-exploitationexploitation+4
23813 years ago
gluegate preview

gluegate

GitHubsbousseaden/gluegate

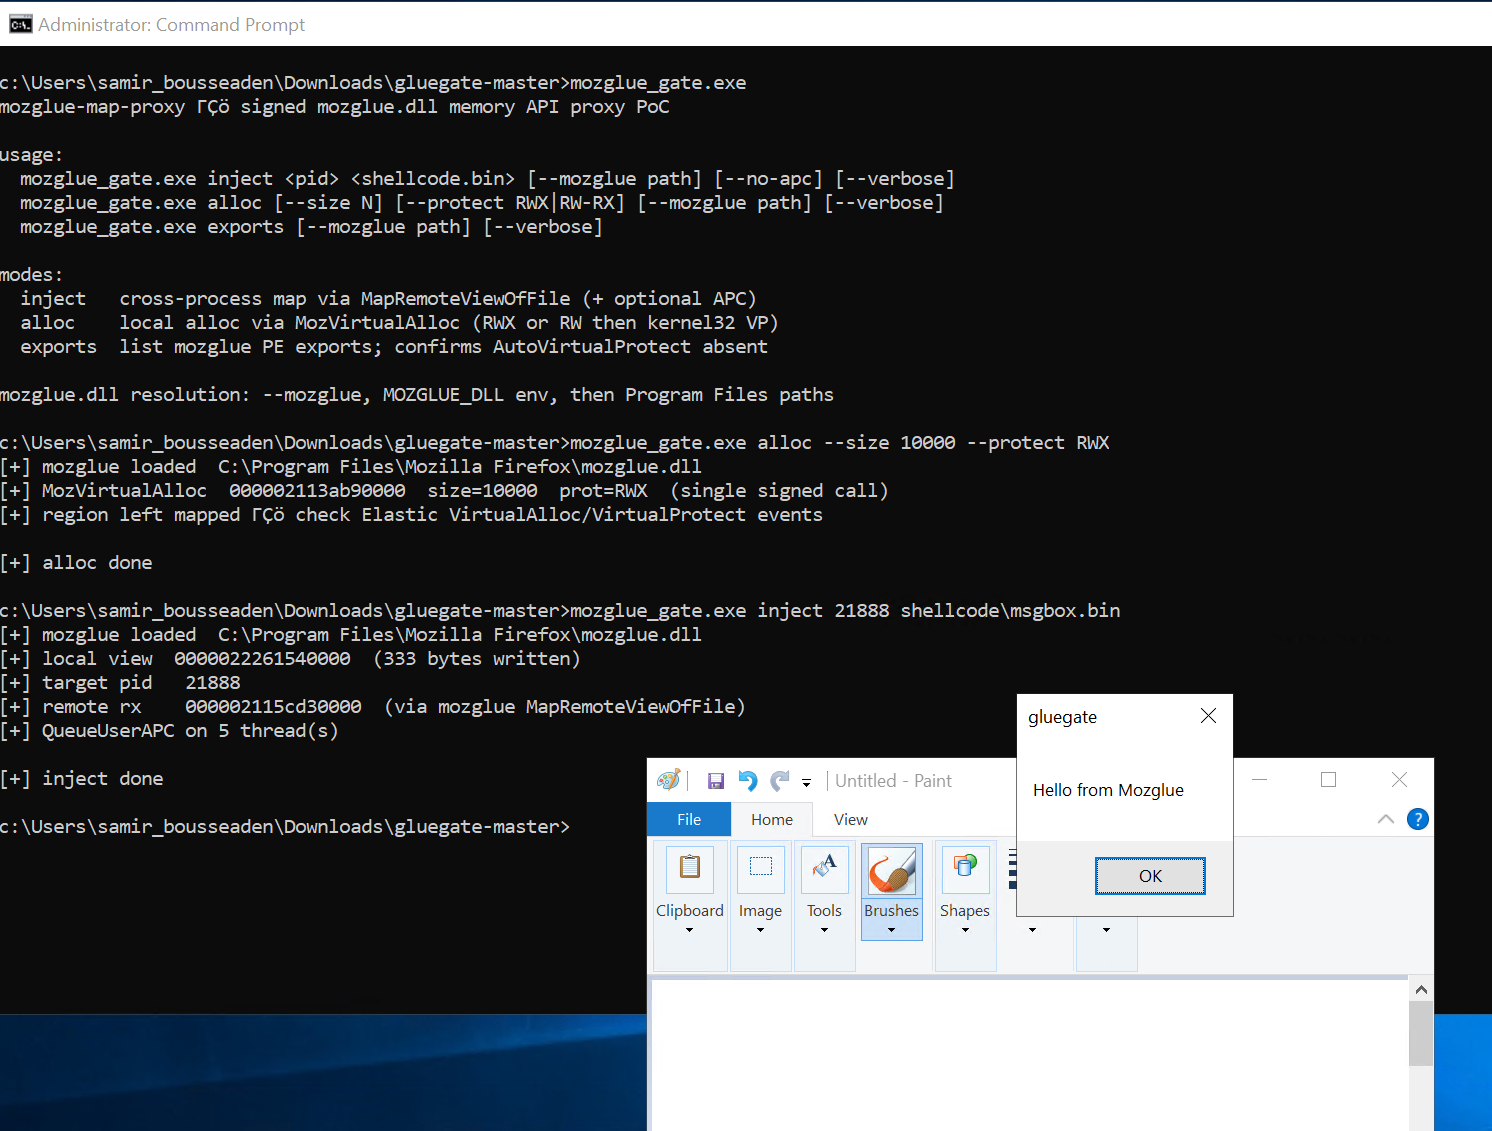
Memory API proxy via signed mozglue.dll
defensive-toolsids-ips-evasionmemory-forensics+2
414 months ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.

exploitationforensicsmalware-analysis+5
2292 years ago