

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
169 results
KernelFlirt preview

KernelFlirt

GitHubakatorich/kernelflirt

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…

ai-assisted-reversingai-securityanti-bot+9
53
5 months ago
ghostlock-cve-2026-43499-4.19-k40 preview

ghostlock-cve-2026-43499-4.19-k40

GitHubccp-p/ghostlock-cve-2026-43499-4.19-k40

Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.

android-securitybinary-exploitationexploitation+6
91 month ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.4k1 day ago
DFIR-Companion preview

DFIR-Companion

GitHubhasamba/dfir-companion

DFIR forensics companion server + capture extension

ai-securitydefensive-toolsdigital-forensics+9
352 days ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
52 months ago
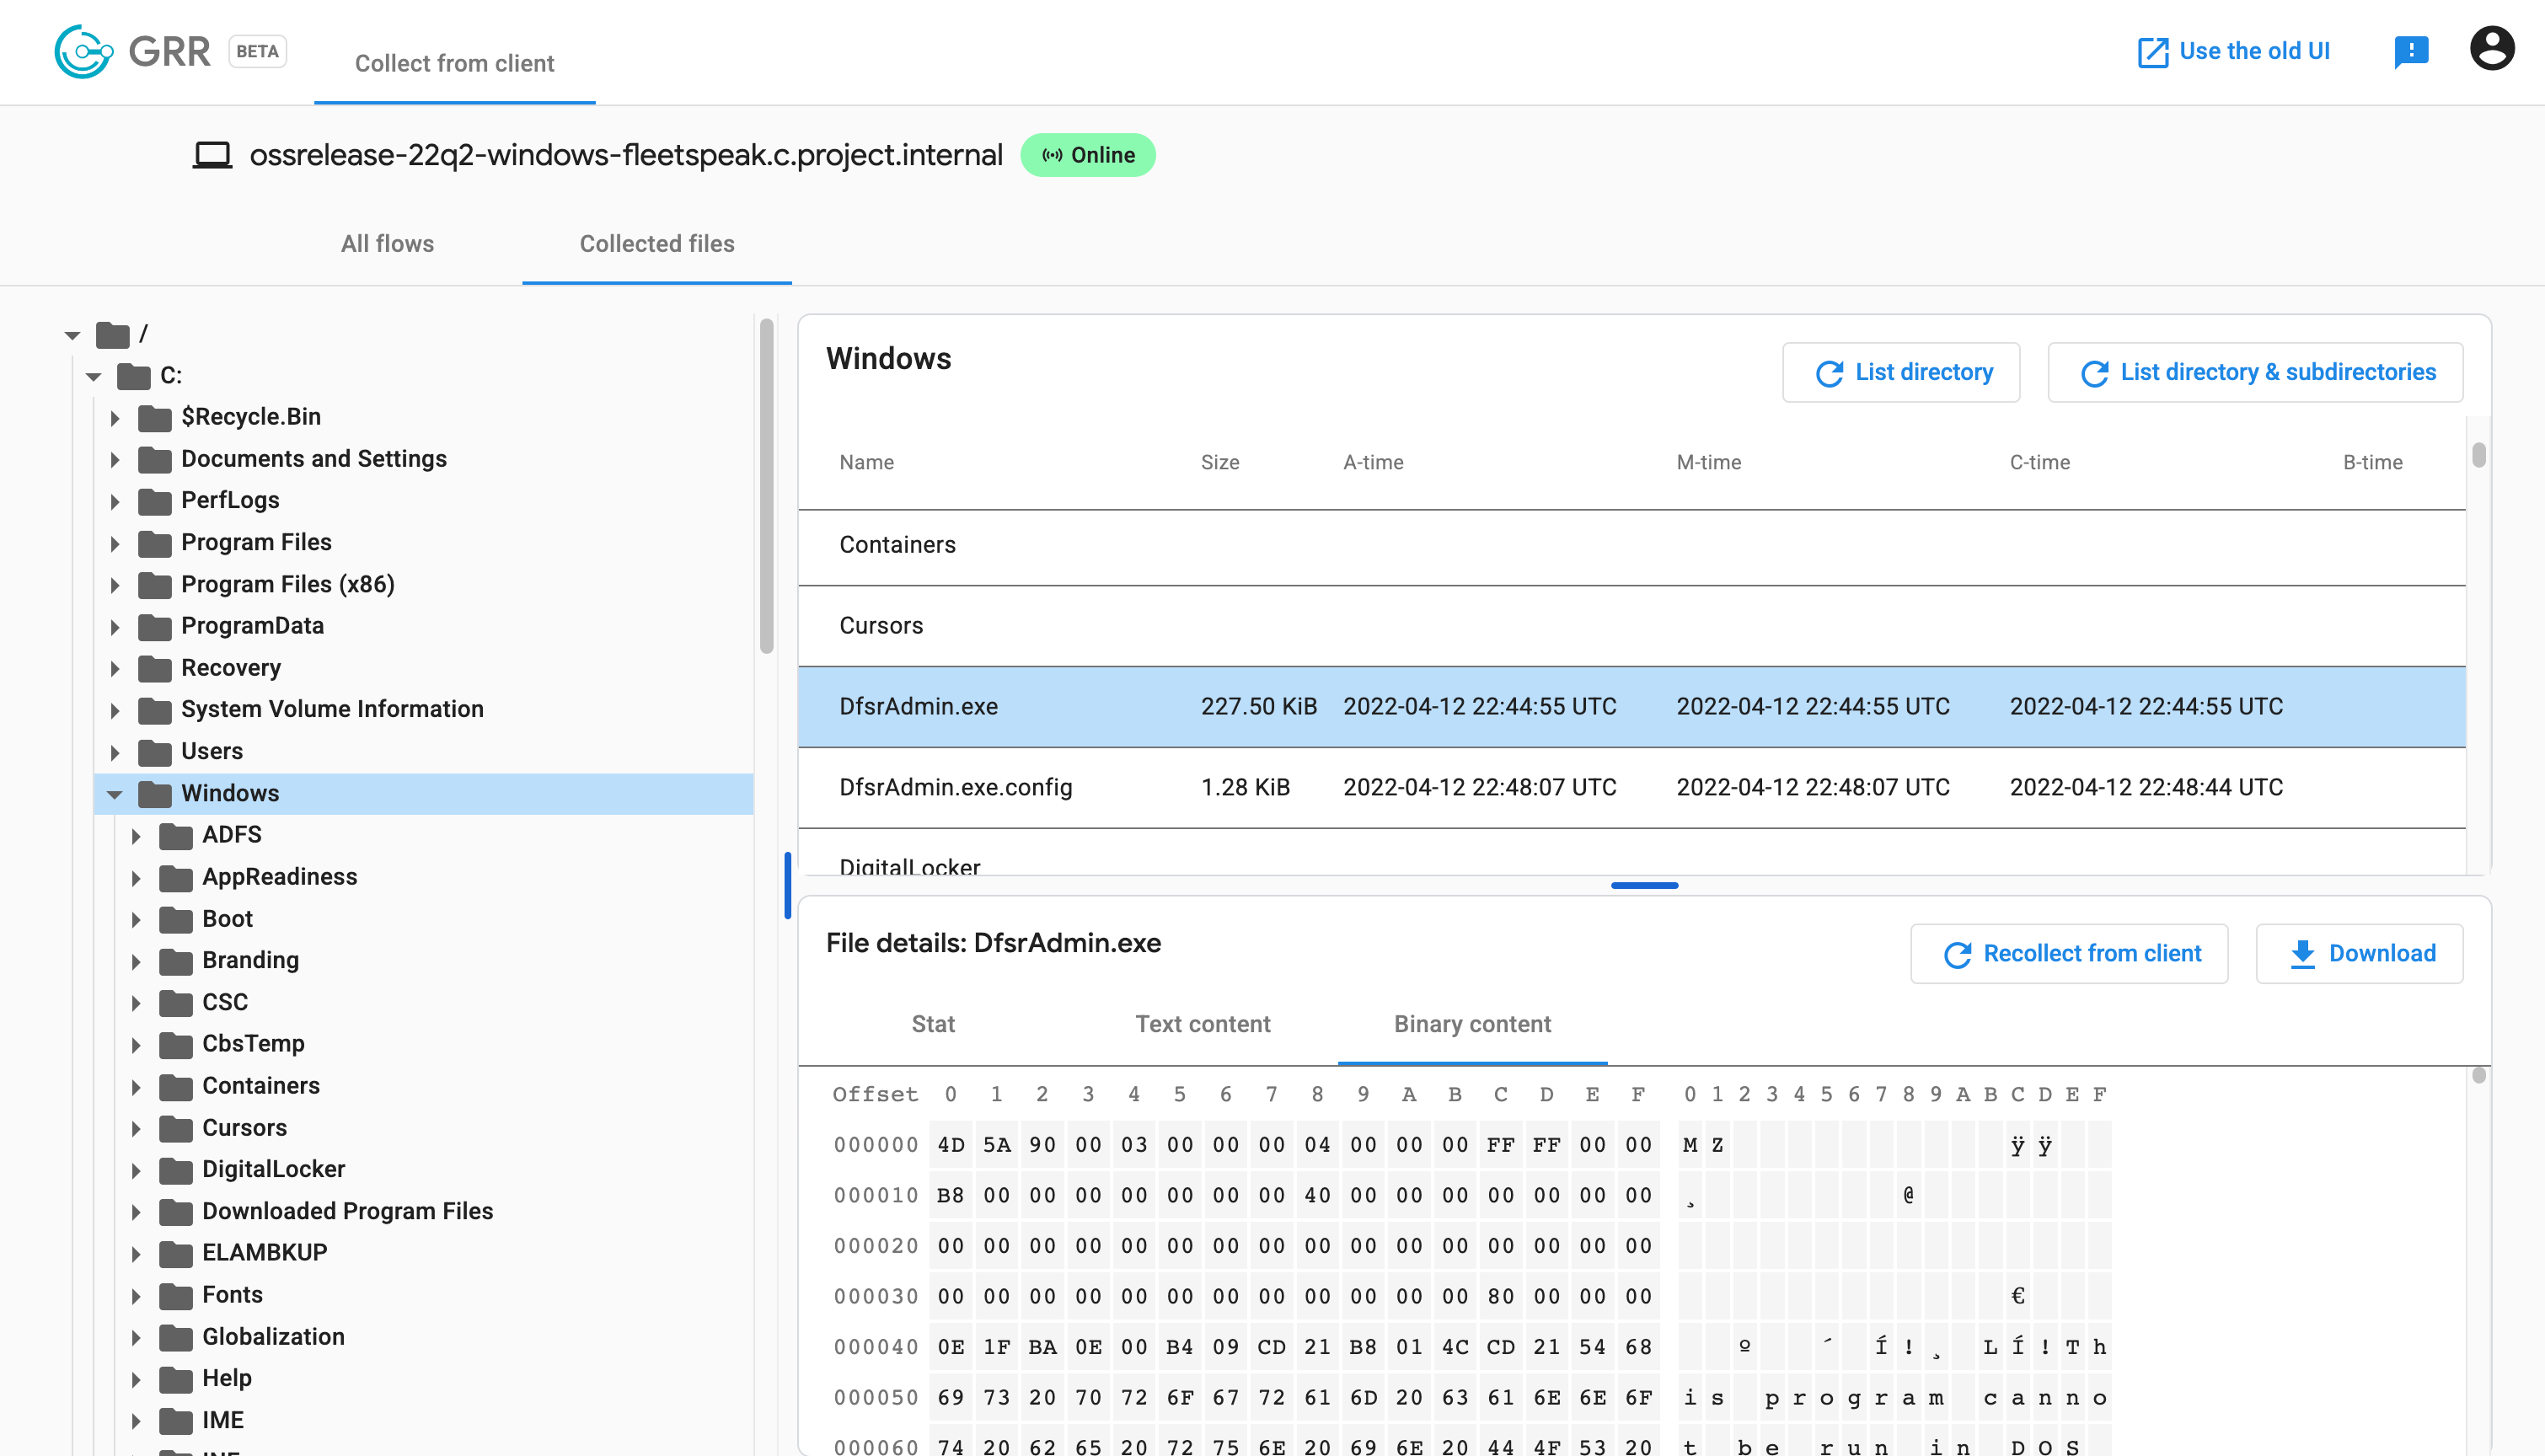
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

digital-forensicsdisk-forensicsforensics+4
5.1k29 days ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

curated-resourcesdigital-forensicsdisk-forensics+9
9.5k18 days ago
mcp-gamehacking preview

mcp-gamehacking

GitHub1llu50ry/mcp-gamehacking

MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…
ai-assisted-reversingbinary-analysiscurated-resources+6
4981 day ago
CVE-2026-74469 preview

CVE-2026-74469

GitHub0xblackash/cve-2026-74469

Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
binary-exploitationeducationexploitation+5
1 month ago
VectorFreed preview

VectorFreed

GitHubrafabd1/vectorfreed

Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
binary-exploitationexploitationinformation-gathering+4
2115 days ago
NativePe preview

NativePe

GitHubhabanada/nativepe

Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…

binary-analysisbinary-exploitationdynamic-analysis-sandboxing+5
191 month ago
how_to_become_a_malware_analyst preview

how_to_become_a_malware_analyst

GitHubpinksawtooth/how_to_become_a_malware_analyst

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…

binary-analysisctfcurated-resources+7
2841 month ago
CVE-2026-43499-S26 preview

CVE-2026-43499-S26

GitHubsammyenigma/cve-2026-43499-s26

Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
android-securitybinary-exploitationexploitation+8
2 months ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs

digital-forensicsforensicsioc-management+3
8582 years ago
awesome-malware-analysis preview

awesome-malware-analysis

GitHubrshipp/awesome-malware-analysis

Defund the Police.

curated-resourceseducationforensics+10
14.4k2 years ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
6661 month ago
OnTheEdge preview

OnTheEdge

GitHubjssngc/ontheedge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…

command-and-controldata-exfiltrationmalware-analysis+4
111 month ago
pwndbg preview

pwndbg

GitHubpwndbg/pwndbg

Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

ai-assisted-reversingbinary-analysisbinary-exploitation+12
11.1k2 days ago
Previous12…10Next