Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
msf_shellcode_analysis preview

msf_shellcode_analysis

GitHubyo-yo-yo-jbo/msf_shellcode_analysis

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
binary-analysiseducationmalware-analysis+3
292 months ago
REW-sploit preview

REW-sploit

GitHubrew-sploit/rew-sploit

Emulate and Dissect MSF and *other* attacks

bluetooth-securitydebuggersdefensive-tools+6
1442 years ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
3162 days ago
mkPIVM preview

mkPIVM

GitHubd7ead/mkpivm

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.

exploitationmalware-analysispayload-generation+3
3881 month ago
InflativeLoading preview

InflativeLoading

GitHubsenzee1984/inflativeloading

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

binary-exploitationexploitationmalware-analysis+3
3242 years ago
Lucky-Spark preview

Lucky-Spark

GitHubschich/lucky-spark

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.

binary-analysiscommand-and-controlexploitation+6
632 months ago
SHGenOb preview

SHGenOb

GitHuboldboy21/shgenob

Python based tool for generating Shellcode from PIC C
binary-analysiseducationencryption-decryption-tools+5
4311 months ago
artifacts-kit preview

artifacts-kit

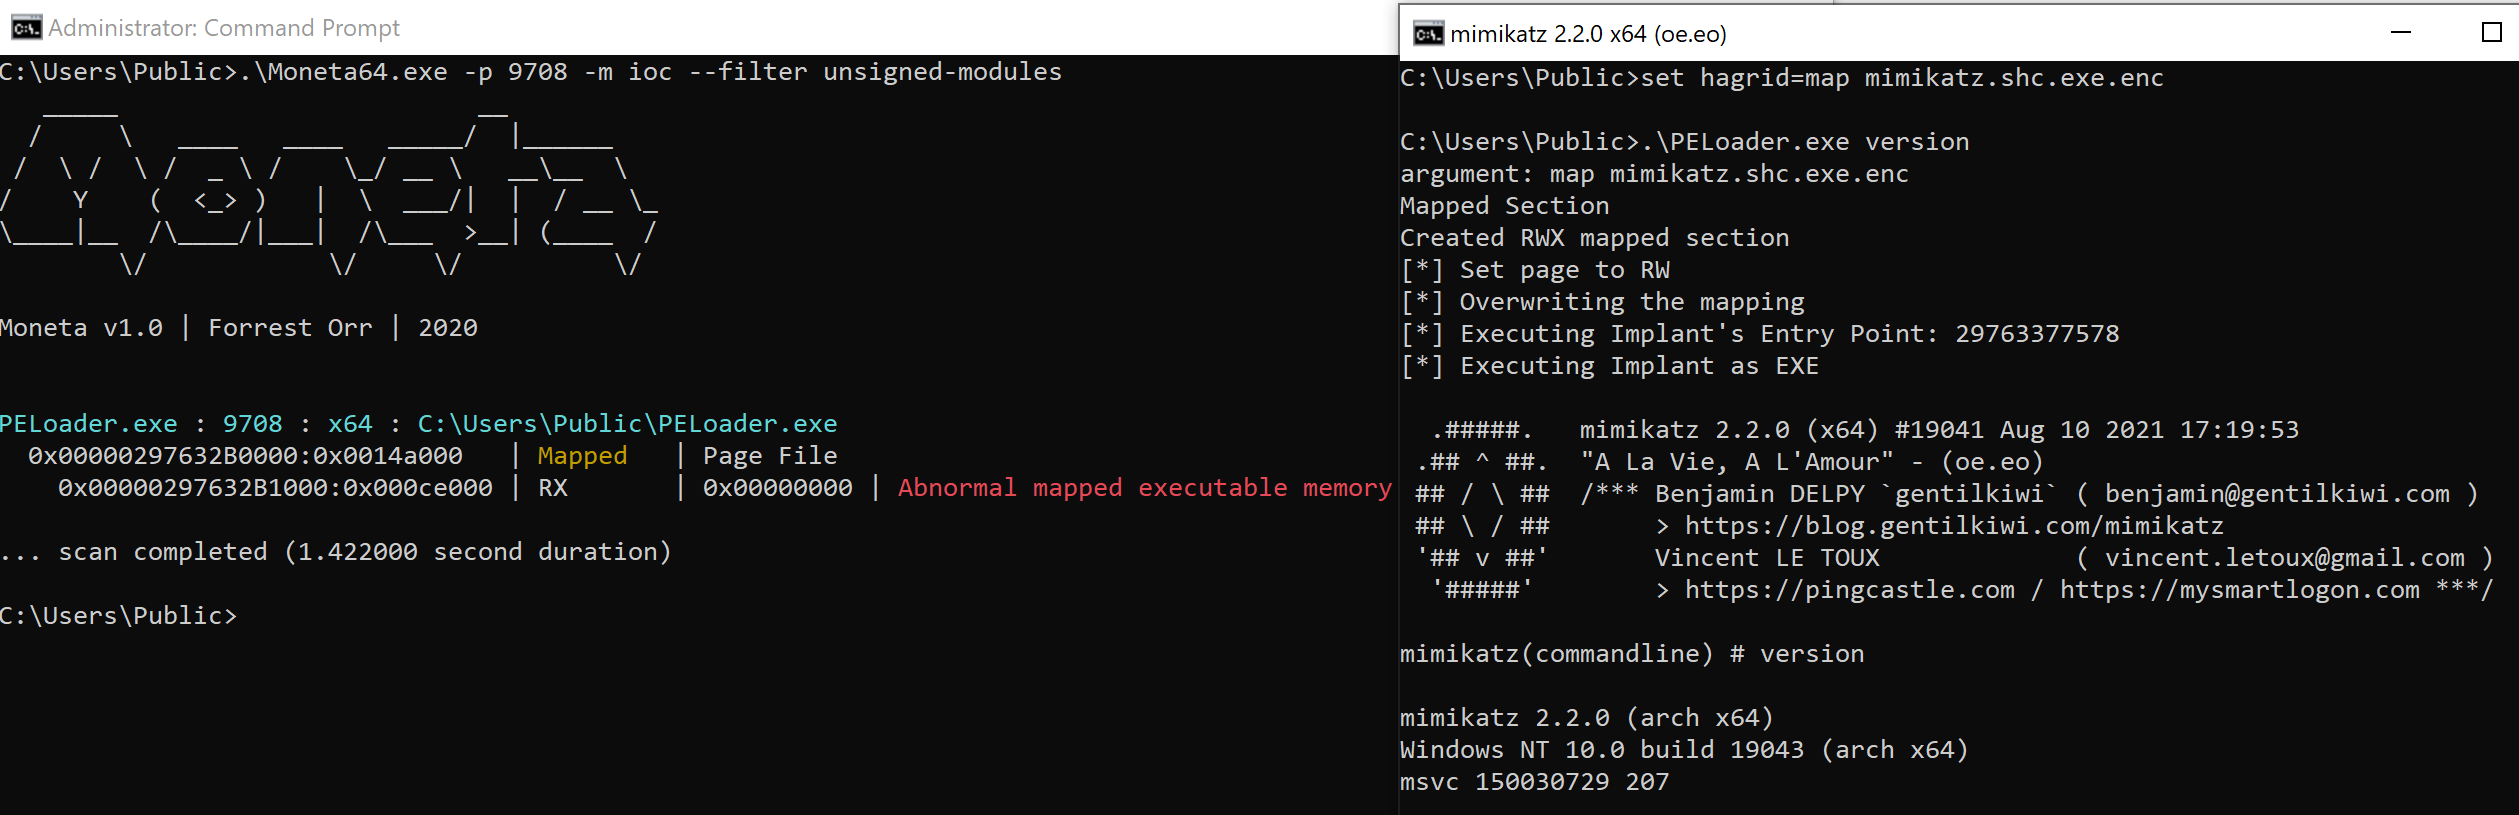
GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
2282 years ago
Supernova preview

Supernova

GitHubnickvourd/supernova

Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
encryption-decryption-toolsexploit-frameworksmalware-analysis+3
1.0k2 months ago
the-backdoor-factory preview

the-backdoor-factory

GitHubsecretsquirrel/the-backdoor-factory

Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors

binary-exploitationexploitationmalware-analysis+6
3.4k2 years ago
EternalBlueC preview

EternalBlueC

GitHubbhassani/eternalbluec

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
binary-exploitationeducationexploitation+7
6181 month ago
PELoader preview

PELoader

GitHubhagrid29/peloader

PE loader with various shellcode injection techniques
binary-analysisexploitationmalware-analysis+4
4603 years ago
KittyStager preview

KittyStager

GitHubenelg52/kittystager

KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
command-and-controleducationencryption-decryption-tools+6
2263 years ago
ExecIT preview

ExecIT

GitHubflorylsk/execit

Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2292 years ago
doublepulsar-usermode-injector preview

doublepulsar-usermode-injector

GitHubwithsecurelabs/doublepulsar-usermode-injector

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
exploitationmalware-analysispayload-development+2
1239 years ago
NOW preview

NOW

GitHubnirvanaon/now

NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.

cryptographyctfeducation+5
933 months ago
Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis preview

Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis

GitHubkaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

binary-analysiscommand-and-controldata-exfiltration+7
15 days ago