Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
Simple-Polymorphic-Engine-SPE32 preview

Simple-Polymorphic-Engine-SPE32

GitHubpelock/simple-polymorphic-engine-spe32

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

encryption-decryption-toolsmalware-analysisreverse-engineering+1
158
3 years ago
m3 preview

m3

GitHubthisislibra/m3

A simple and scalable Android bot emulation framework, as presented at Black Hat Europe 2021's Arsenal, as well as atHack 2021's Arsenal

android-securityeducationmalware-analysis+1
294 years ago
SSMA preview

SSMA

GitHubsecrary/ssma

SSMA - Simple Static Malware Analyzer [This project is not maintained anymore by me]

forensicsmalware-analysisstatic-analysis+1
4146 years ago
ioc-finder preview

ioc-finder

GitHubfhightower/ioc-finder

Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…

ioc-managementmalware-analysisthreat-intelligence+1
1845 days ago
spyre preview

spyre

GitHubspyre-project/spyre

simple YARA-based IOC scanner

forensicsincident-responseioc-management+1
1816 months ago
KittyStager preview

KittyStager

GitHubenelg52/kittystager

KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…

command-and-controleducationencryption-decryption-tools+6
2263 years ago
maldrolyzer preview

maldrolyzer

GitHubmaldroid/maldrolyzer

Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)

android-securitycommand-and-controlinformation-gathering+3
11211 years ago
ConTroll_Remote_Access_Trojan preview

ConTroll_Remote_Access_Trojan

GitHublithium876/controll_remote_access_trojan

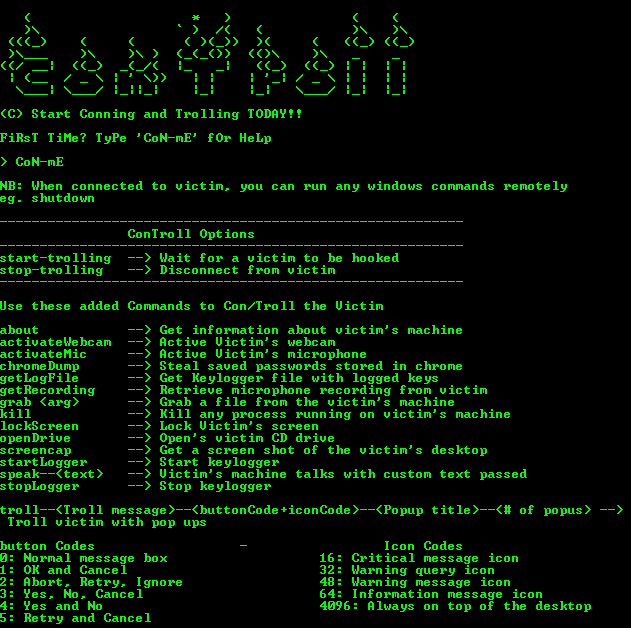
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.

command-and-controleducationinformation-gathering+7
1048 years ago
DDEtect preview

DDEtect

GitHubaserper/ddetect

Simple DDE object detector

malware-analysisstatic-analysisvulnerability-analysis
568 years ago
MalScan preview

MalScan

GitHubice3man543/malscan

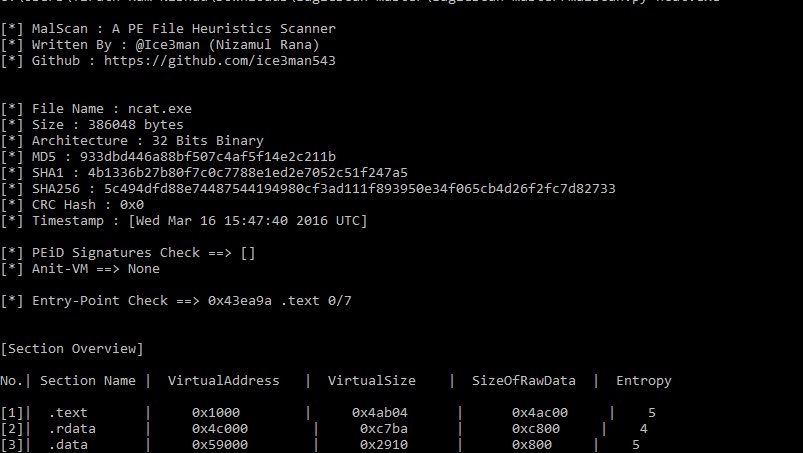
A Simple PE File Heuristics Scanners

malware-analysisstatic-analysisvulnerability-analysis
528 years ago
fuckshell preview

fuckshell

GitHubjofpin/fuckshell

Simple Webshell Scanner

information-gatheringmalware-analysispenetration-testing+2
5611 years ago
KoodousFinder preview

KoodousFinder

GitHubhuntdownproject/koodousfinder

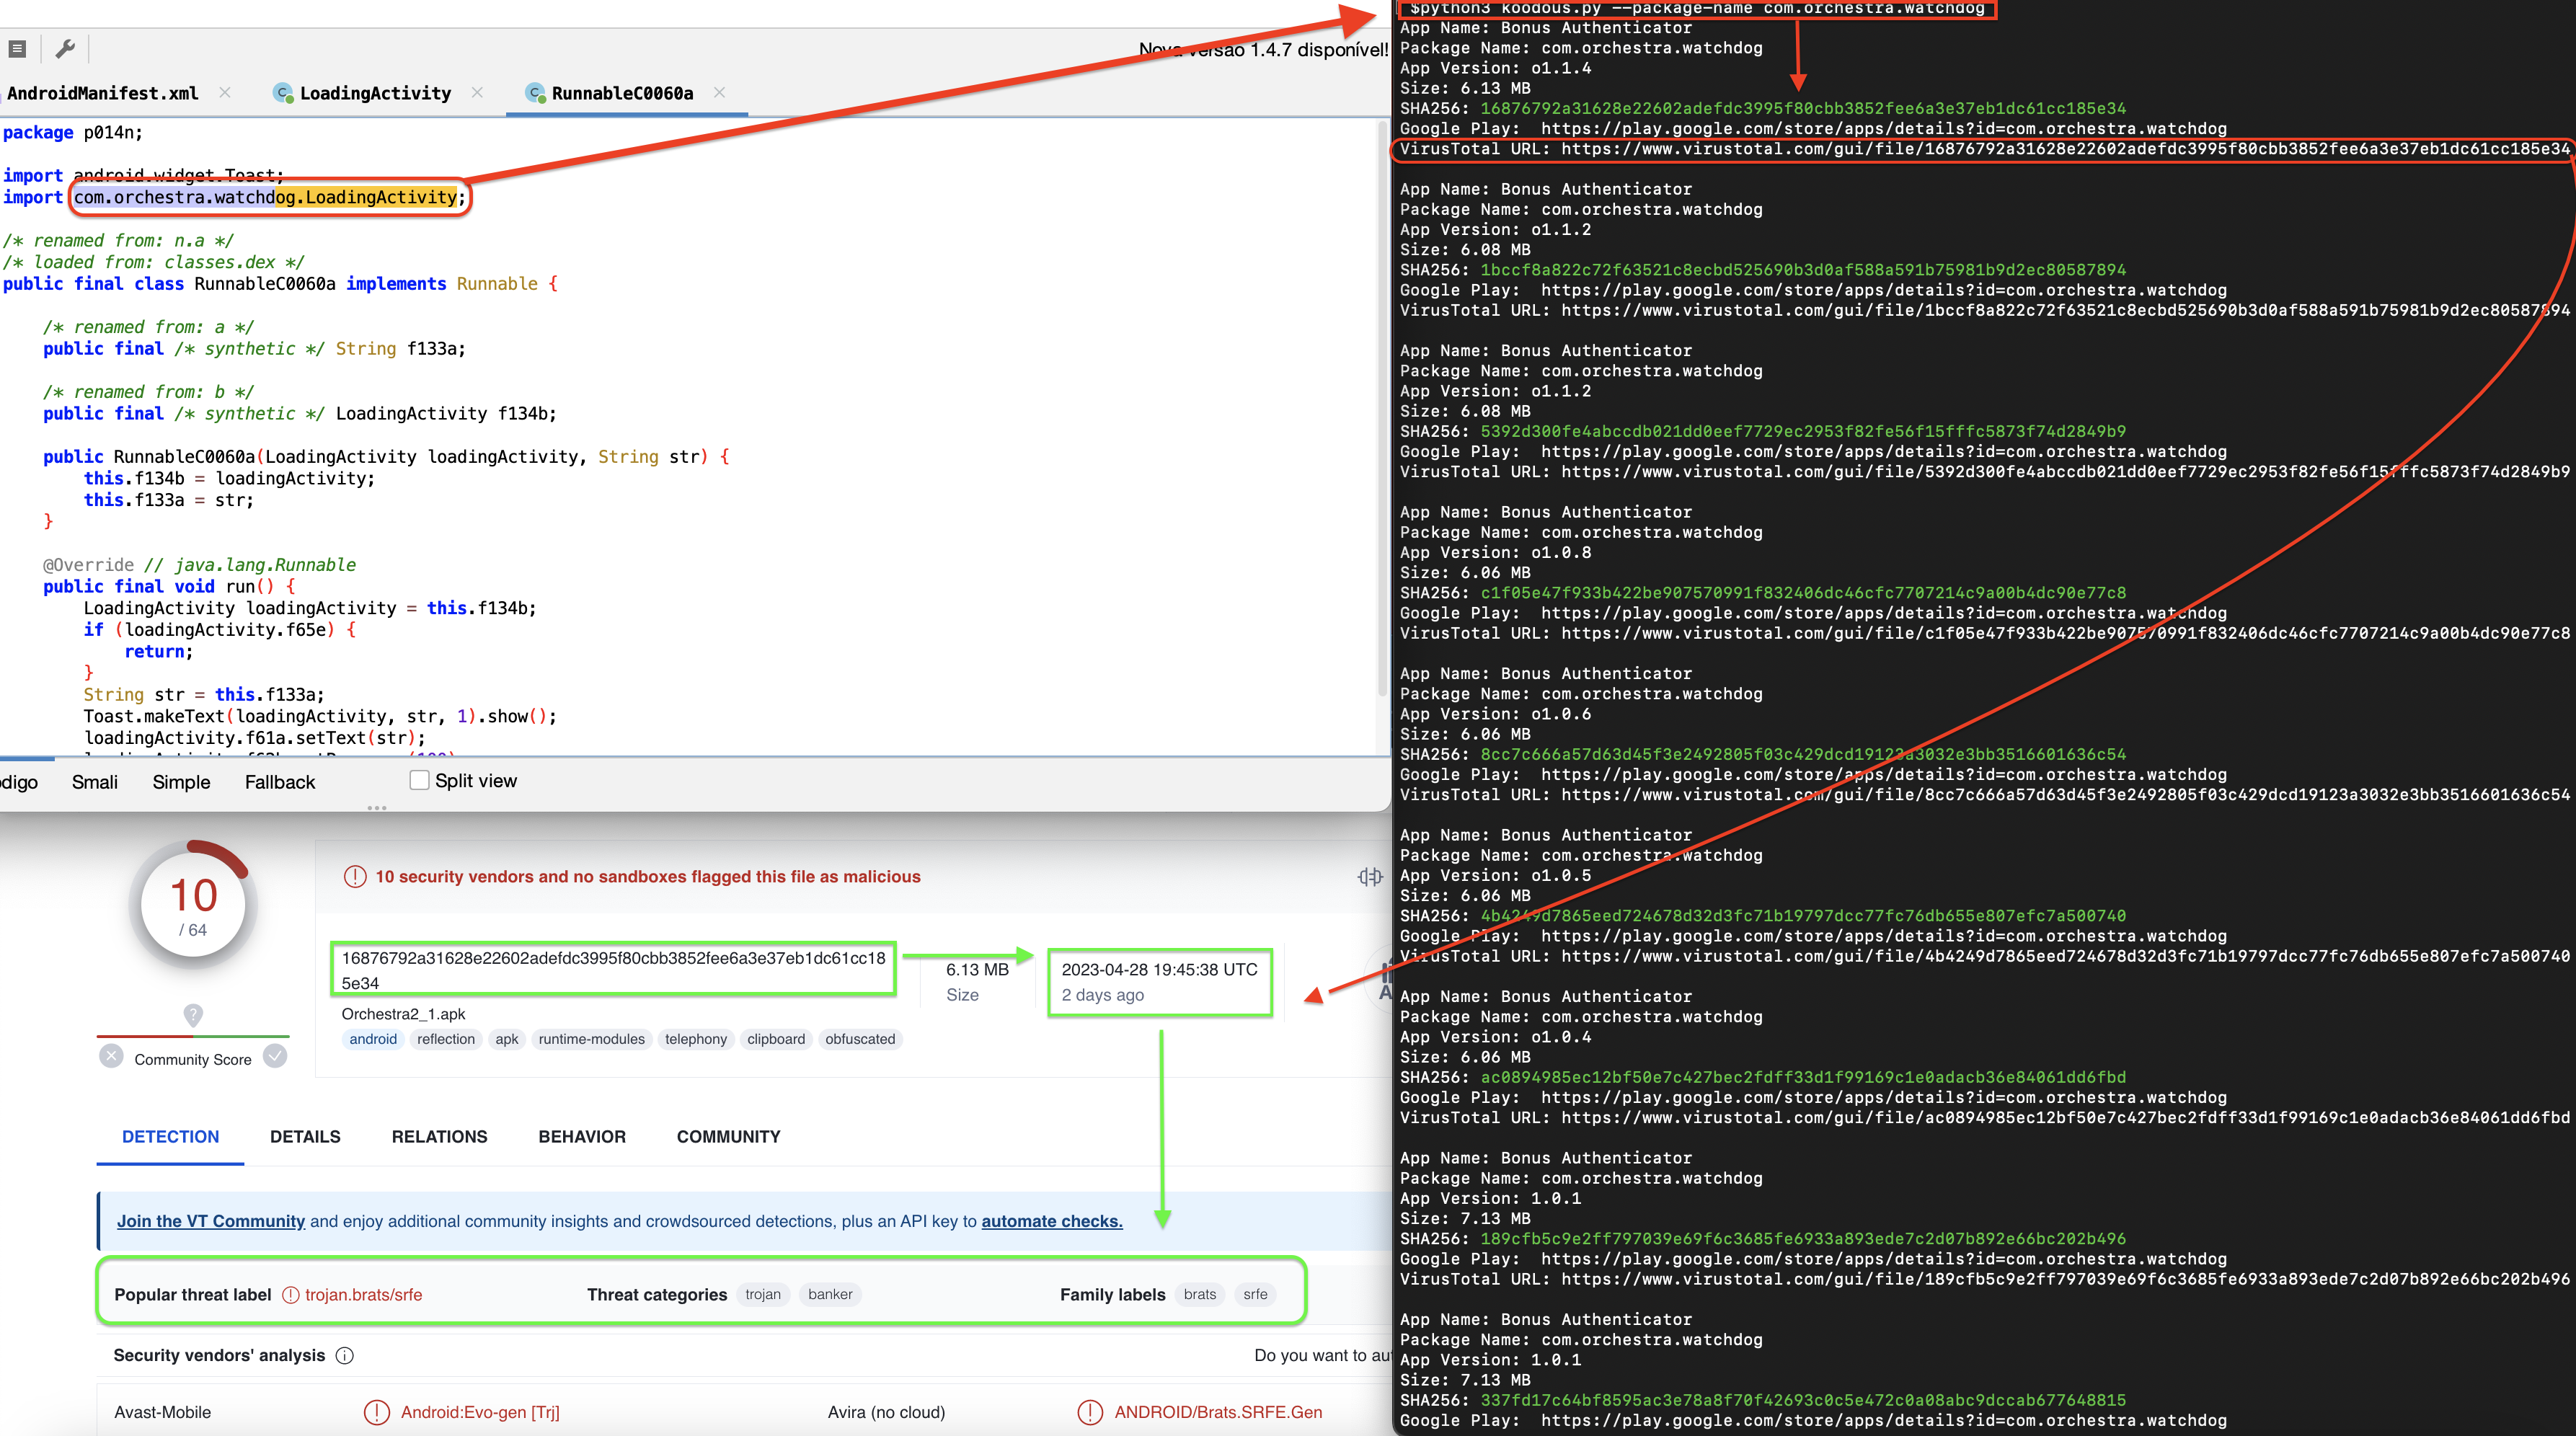
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities

android-securitymalware-analysisosint+2
892 years ago
pyobfuscate preview

pyobfuscate

GitHubmachine1337/pyobfuscate

A simple and efficent script to obfuscate python payloads to make it completely FUD

exploitationmalware-analysispayload-development+2
392 years ago
adwind-decryptor preview

adwind-decryptor

GitHubmhelwig/adwind-decryptor

Simple decrypter for Java AdWind, jRAT, jBifrost trojan

binary-analysisdigital-forensicsencryption-decryption-tools+3
179 years ago
deobf-Arxan-Deob-C preview

deobf-Arxan-Deob-C

GitHubgmh5225/deobf-arxan-deob-c

Simple C program to quickly deobfuscate windows executables protected with Arxan.

binary-analysisdefensive-toolsmalware-analysis+1
153 years ago
sc2elf preview

sc2elf

GitHubdump-guy/sc2elf

Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF

binary-analysismalware-analysisreverse-engineering+1
103 years ago
CVE-2025-7771 preview

CVE-2025-7771

GitHubxm0kht4r/cve-2025-7771

A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…

binary-exploitationmalware-analysispost-exploitation+3
108 months ago
batchfuscate preview

batchfuscate

GitHubhellwound/batchfuscate

A simple script to obfuscate batch(bat) code easily

malware-analysispayload-generation
43 years ago
Previous123Next