
ALPC-Enumerator
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
digital-forensicsinformation-gatheringmalware-analysis+4
31
talha-nazeef-ahmed/alpc-enumeratorA Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 elevenpaths/neto
Neto | A tool to analyse browser extensions
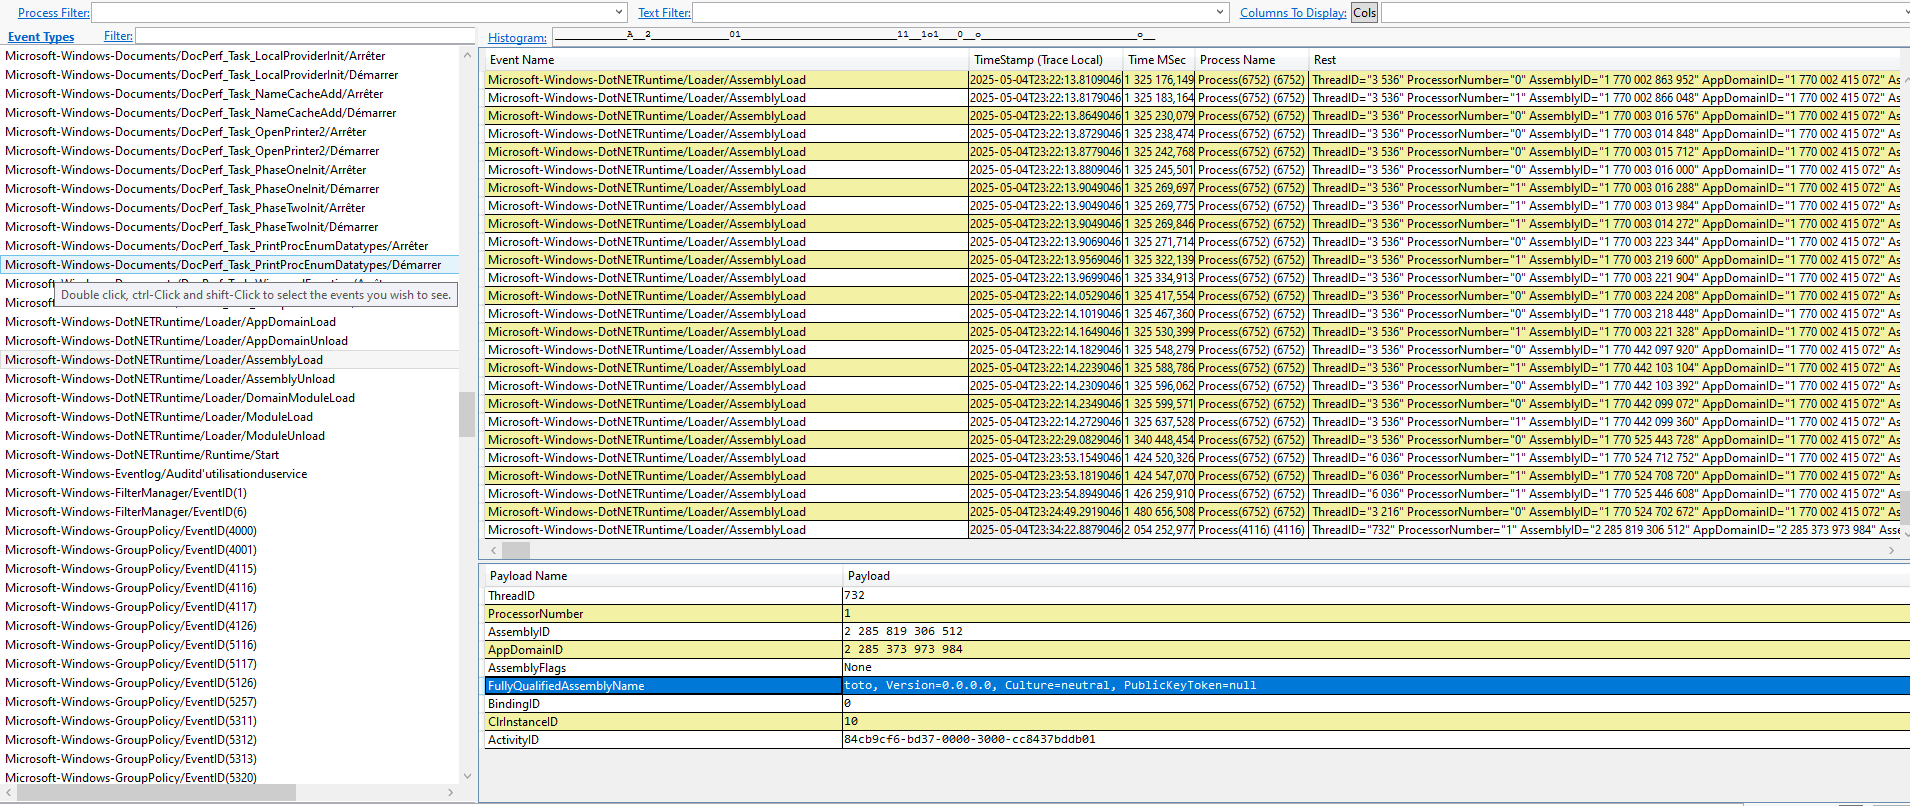 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 adityaks/strafer
Strafer: A tool to detect potential infections in Elasticsearch instances
 krmaxwell/maltrieve
A tool to retrieve malware directly from the source for security researchers.
 amorath/threatscraper
Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
 jacobsoo/rtf-cleaner
Extracts URLs from malicious RTF files exploiting CVE-2017-0199 and CVE-2017-8759 for malware analysis and threat intelligence.
 soheiltnt/jakeylogger
Python-based keylogger for capturing and logging keystrokes. Designed for educational security research and testing.
 destiny-creates/goxlr-malware-family
Malware analysis from the domain goxlr.net
 iphelix/dnschef
DNSChef - DNS proxy for Penetration Testers and Malware Analysts
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
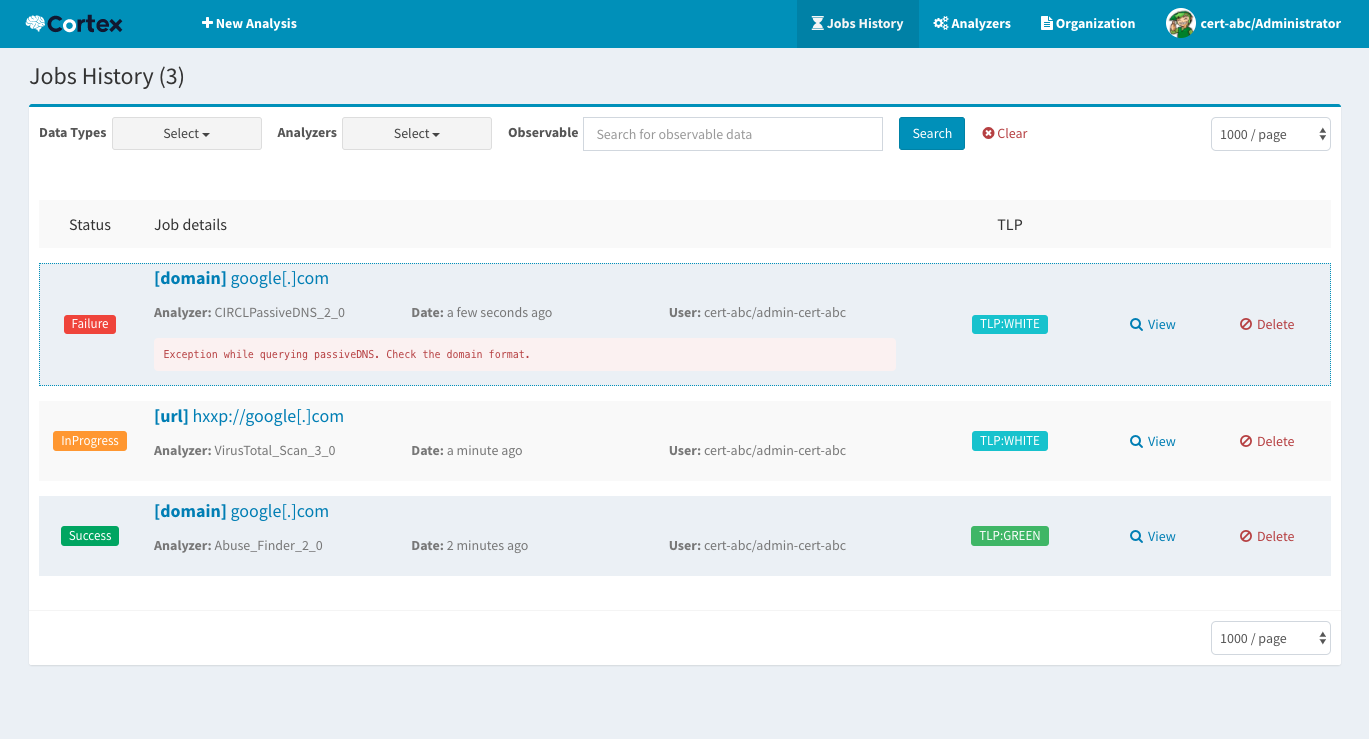 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
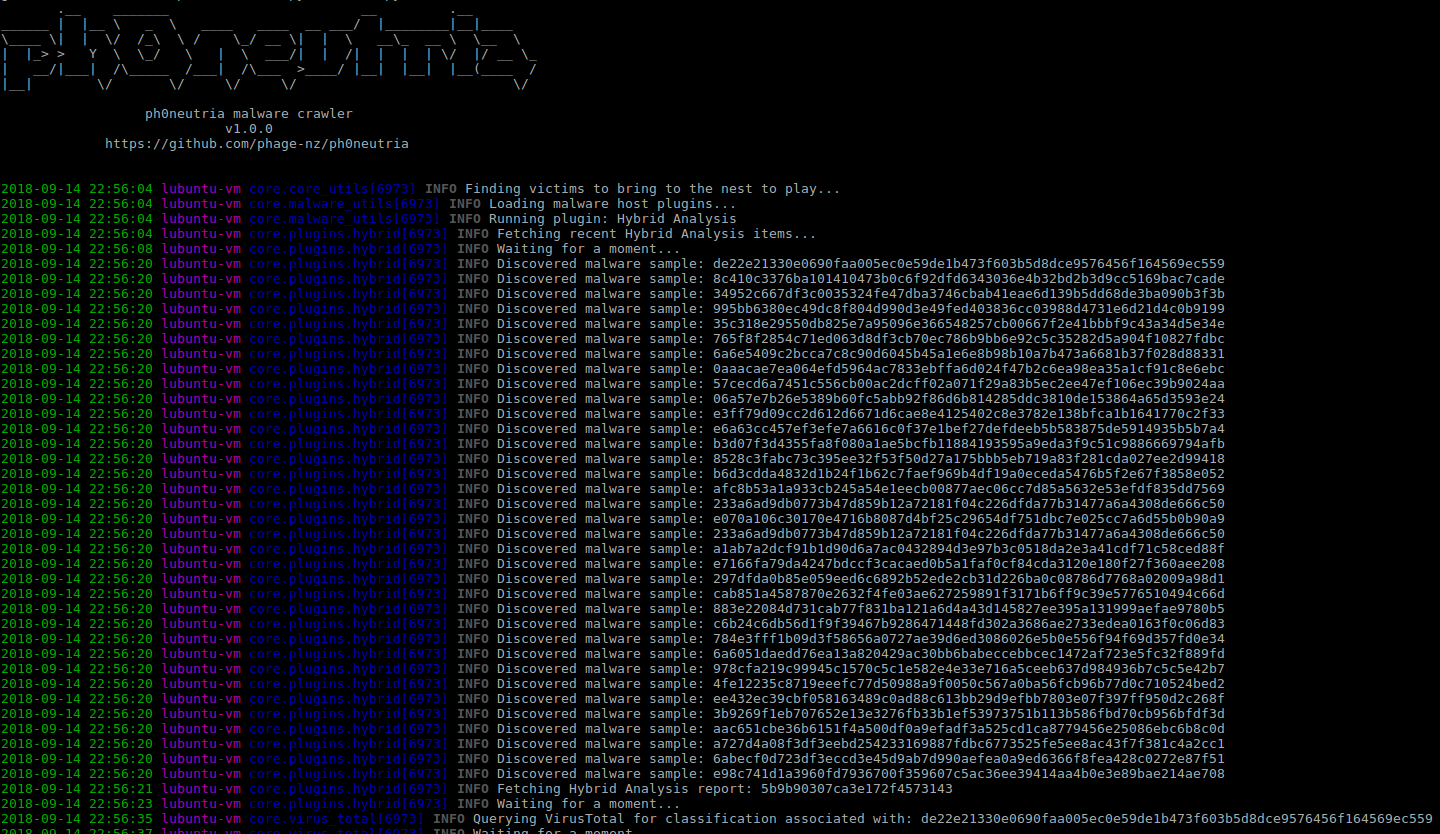 phage-nz/ph0neutria
ph0neutria is a malware zoo builder that sources samples straight from the wild. Everything is stored in Viper for ease of access and manageability.