
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
85 results
FileWatchTower preview

FileWatchTower

GitHubiomoath/filewatchtower

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
digital-forensicsforensicshash-analysis+4
292 years ago
kit_hunter preview

kit_hunter

GitHubsteved3/kit_hunter

A basic phishing kit scanner for dedicated and semi-dedicated hosting

malware-analysisphishing-toolsvulnerability-scanners+1
1093 years ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
showstopper preview

showstopper

GitHubcheckpointsw/showstopper

ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
debuggerseducationmalware-analysis+1
2264 years ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
command-and-controldata-exfiltrationeducation+8
1747 months ago
M-Botnet preview
Archived

M-Botnet

GitHubm507/m-botnet

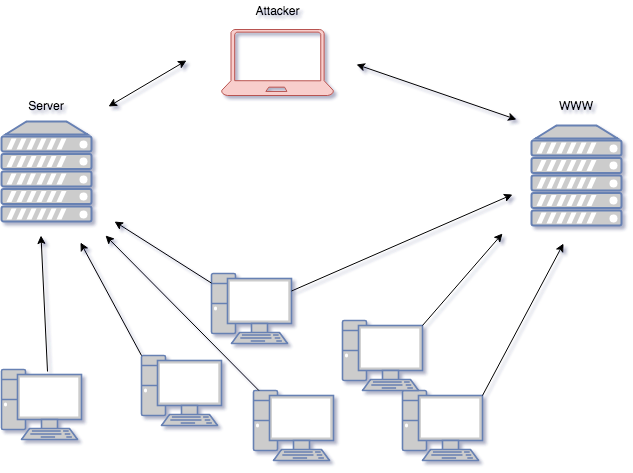
A C2 project that controls a self-propagating MS17-010 worm.
command-and-controleducationexploitation+4
785 years ago
LOLDrivers preview

LOLDrivers

GitHubmagicsword-io/loldrivers

Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
curated-resourceseducationforensics+5
1.8k3 days ago
AntiVE-BehaviorWatch preview

AntiVE-BehaviorWatch

GitHubnirvanaon/antive-behaviorwatch

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

anti-botdynamic-analysis-sandboxingids-ips-evasion+3
402 months ago
Malicious-MCP preview

Malicious-MCP

GitHubquinnbast/malicious-mcp

A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
ai-securitycommand-and-controldata-exfiltration+8
85 months ago
Dropper preview

Dropper

GitHubgmh5225/dropper

Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.

defensive-toolsexploitationmalware-analysis+4
21 year ago
drakvuf-sandbox preview

drakvuf-sandbox

GitHubcert-polska/drakvuf-sandbox

Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
dynamic-analysis-sandboxingforensicsmalware-analysis+2
1.3k1 month ago
nimcrypt preview

nimcrypt

GitHubicyguider/nimcrypt

PE Crypter written in Nim

binary-analysiscode-analysiseducation+9
1025 years ago
neto preview

neto

GitHubelevenpaths/neto

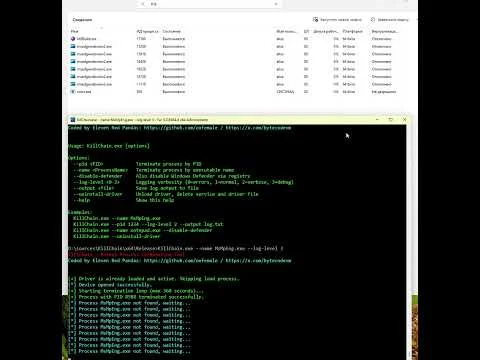
Neto | A tool to analyse browser extensions
code-analysiscryptographyinformation-gathering+2
887 years ago
KillChain preview

KillChain

GitHuboxfemale/killchain

Kernel Process Termination Tool ( CVE-2026-0828 exploit)
binary-exploitationexploitationmalware-analysis+3
365 months ago
Limon preview

Limon

GitHubmonnappa22/limon

Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
40510 years ago
mwcfg preview

mwcfg

GitHubc3rb3ru5d3d53c/mwcfg

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
binary-analysisdefensive-toolsmalware-analysis+3
1342 years ago
InfectPE preview

InfectPE

GitHubsecrary/infectpe

InfectPE - Inject custom code into PE file [This project is not maintained anymore]
binary-analysiseducationmalware-analysis+1
3249 years ago
YARA_Rules preview

YARA_Rules

GitHubmalgamy/yara_rules

Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…

curated-resourcesdefensive-toolsincident-response+3
653 years ago
Previous12345Next