
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
83 results
intelmq preview

intelmq

GitHubcerttools/intelmq

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
incident-responseinformation-gatheringintrusion-detection+6
1.1k5 months ago
silverboxcc preview

silverboxcc

GitHubbizdak/silverboxcc

Reverse engineered android malware, and this is a C&C server for it
android-securitycommand-and-controlmalware-analysis+3
28 years ago
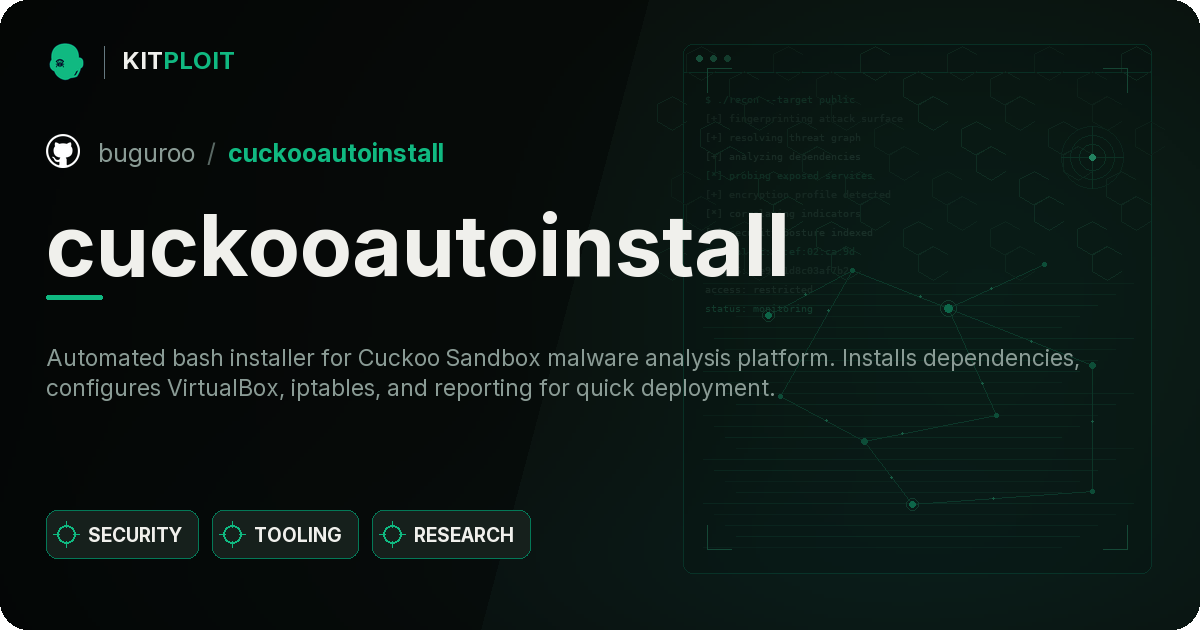
ios-malicious-bithunter preview

ios-malicious-bithunter

GitHubalipay/ios-malicious-bithunter

iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
binary-analysisdynamic-analysis-sandboxingios-security+3
895 years ago
cuckooautoinstall preview

cuckooautoinstall

GitHubbuguroo/cuckooautoinstall

Auto Installer Script for Cuckoo Sandbox
dynamic-analysis-sandboxingmalware-analysisscripting-automation+1
1648 years ago
die-python preview

die-python

GitHubelastic/die-python

Native Python3 bindings for @horsicq's Detect-It-Easy
binary-analysismalware-analysisreverse-engineering
887 months ago
maltrieve preview
Archived

maltrieve

GitHubkrmaxwell/maltrieve

A tool to retrieve malware directly from the source for security researchers.
crawlerinformation-gatheringmalware-analysis+2
5649 years ago
droidlysis preview

droidlysis

GitHubcryptax/droidlysis

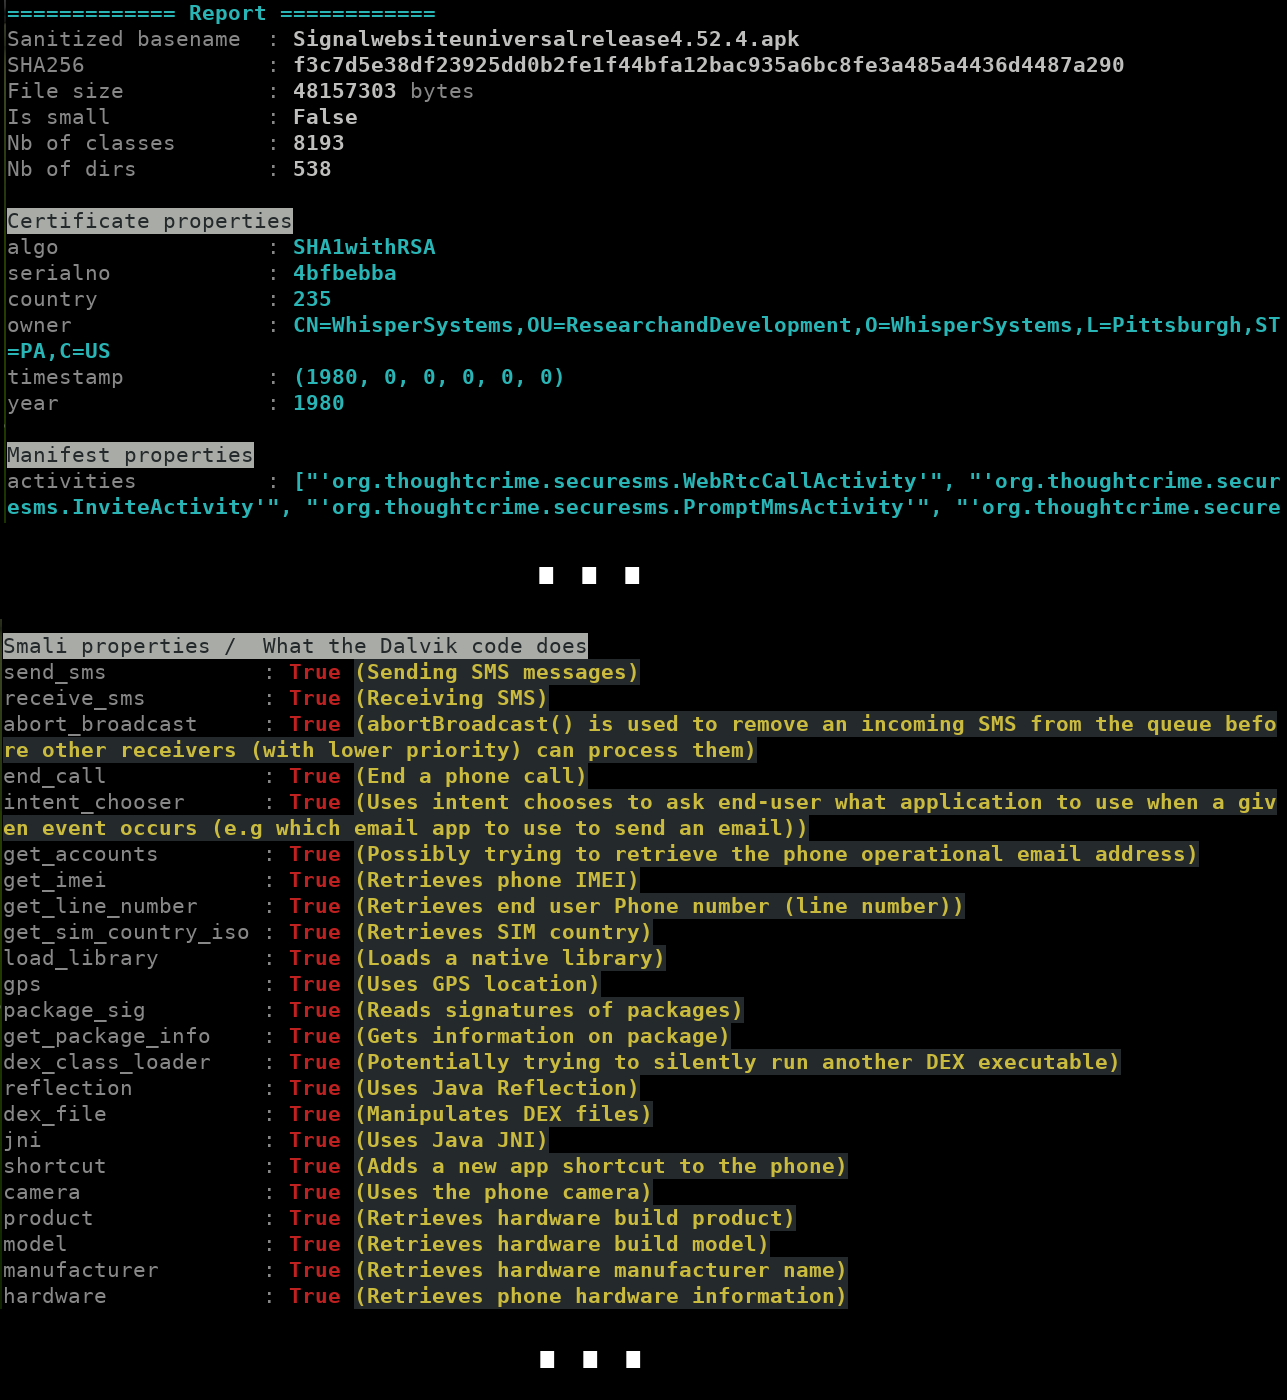
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
android-securityinformation-gatheringmalware-analysis+3
3121 month ago
From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack preview

From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack

GitHubmrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack

It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
educationexploitationincident-response+4
1 year ago
DepAlert preview

DepAlert

GitHubcybergabisoft/depalert

DepAlert is an open-source security gate for your CI/CD pipeline. It analyzes SBOMs against malware intelligence data and quickly tells you whether…

devsecopsmalware-analysissecret-detection+3
5 months ago
OffensiveRust preview

OffensiveRust

GitHubtrickster0/offensiverust

Rust Weaponization for Red Team Engagements.
binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
makin preview

makin

GitHubsecrary/makin

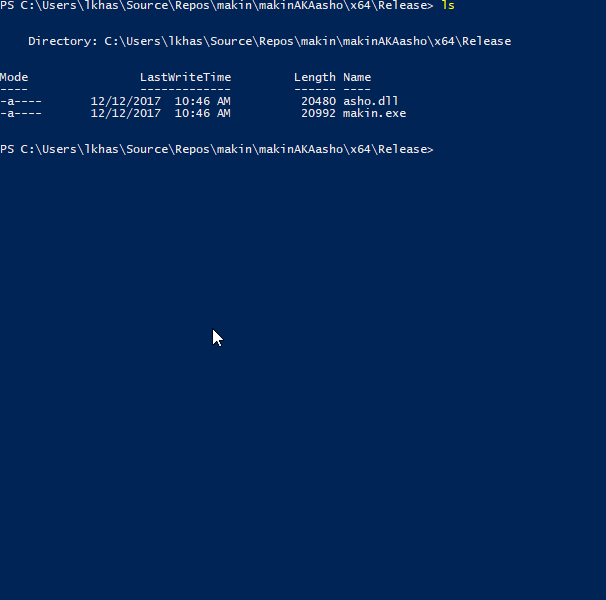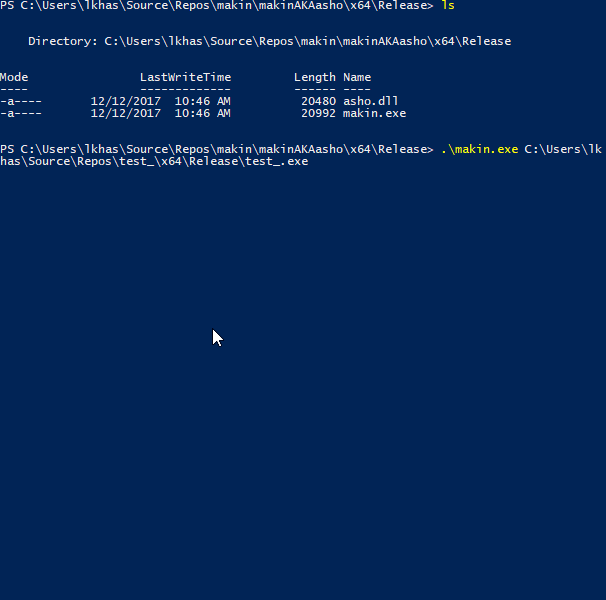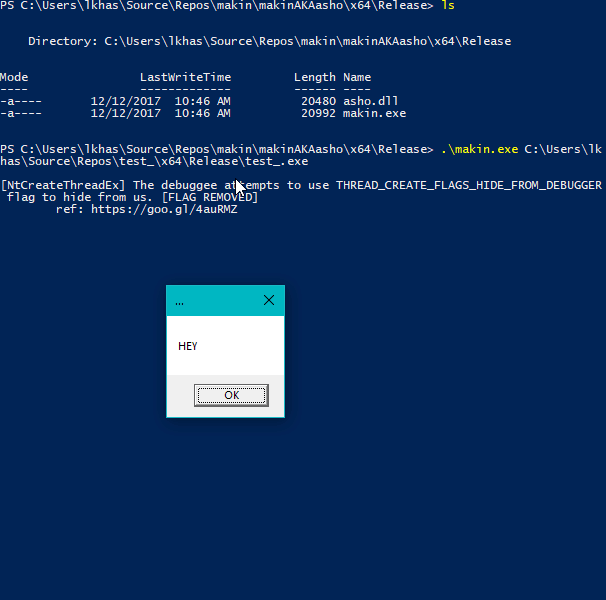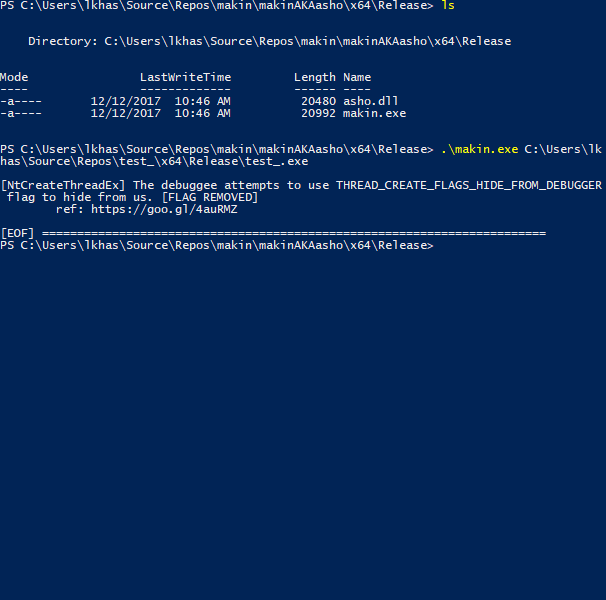
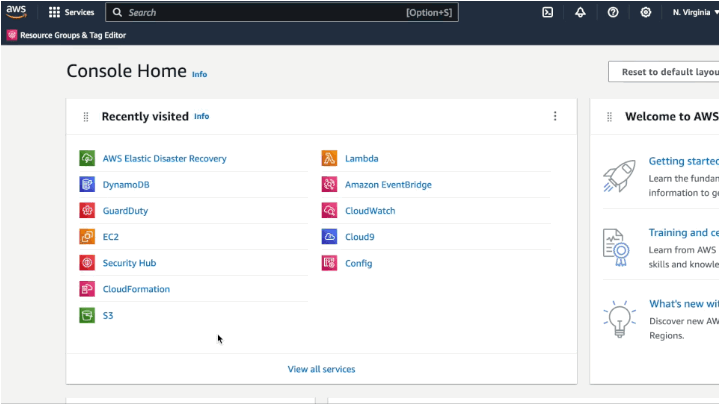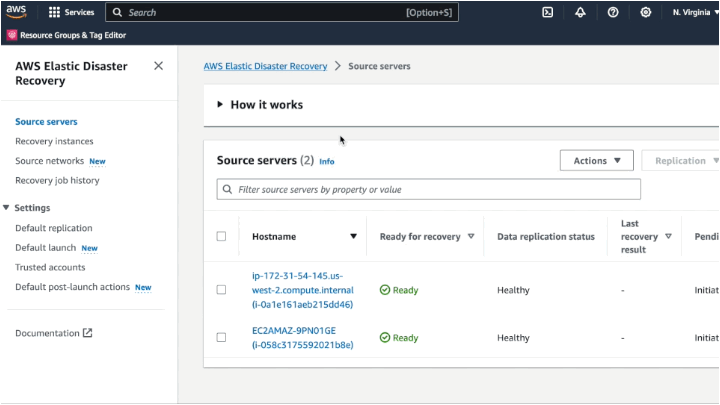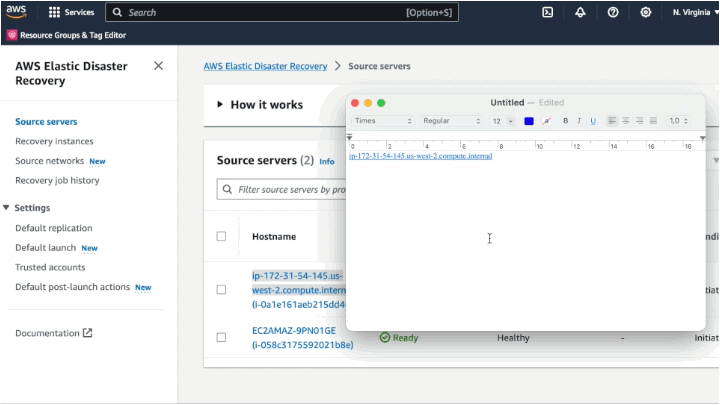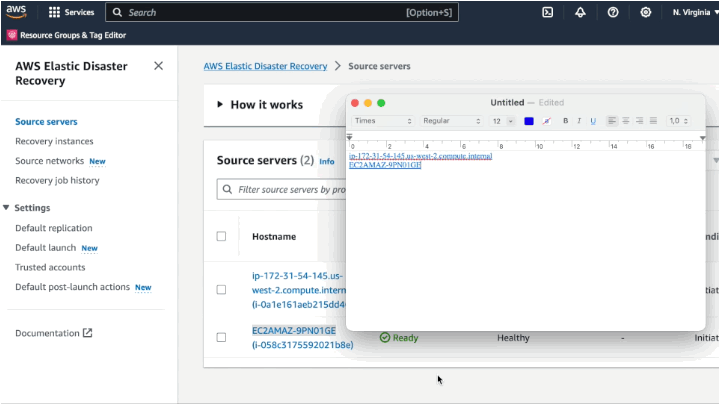
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
anti-botdebuggersdynamic-analysis-sandboxing+2
7427 years ago
drs-malware-scan preview

drs-malware-scan

GitHubaws-samples/drs-malware-scan

Perform file-based malware scan on your on-prem servers with AWS

cloud-securityincident-responsemalware-analysis+2
142 years ago
katana preview
Archived

katana

GitHubsaintly2k/katana

Katana Botnet used for DDoS attacks based on the Mirai Botnet. TEACHING PURPOSES ONLY! I CANNOT BE HELD RESPONSIBLE FOR ANYTHING YOU DO WITH IT! I…

command-and-controleducationexploitation+3
553 years ago
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.6k10h 36m ago
simplify preview

simplify

GitHubcalebfenton/simplify

Android virtual machine and deobfuscator
android-securitybinary-analysisdynamic-analysis-sandboxing+2
4.7k5 years ago
Imperius preview

Imperius

GitHubmatheuzsecurity/imperius

Make an Linux Kernel rootkit visible again.
defensive-toolsmalware-analysis
591 year ago
disrobe preview

disrobe

GitHub1-3-7/disrobe

Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
android-securitybinary-analysisfirmware-analysis+4
1414 days ago
PolyEngine preview

PolyEngine

GitHublongwayhomie/polyengine

PolyEngine is an evasive PE packer designed for CTF challenges and low-level Windows security education. It focuses on bypassing EDR and AV…

anti-botbinary-analysisctf+6
1672 months ago
Previous12345Next