
Diamorphine
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
malware-analysispersistence-mechanismsprivilege-escalation+1
m0nad/diamorphineLKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 matheuzsecurity/imperius
Make an Linux Kernel rootkit visible again.
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 kinryulabs/rootpacket-cve-2026-31431
Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…
 matheuzsecurity/modtracer
Detects hidden Linux kernel rootkits (LKM-based) and restores their visibility using kernel-level inspection techniques for forensic analysis and…

 vasyapokemon/cve-2026-31431
Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 solomon12354/lockinggirl-----cve-2022-0847-dirty_pipe_virus
Educational demonstration of CVE-2022-0847 (Dirty Pipe) Linux kernel exploit with automated compilation script for privilege escalation and file…
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
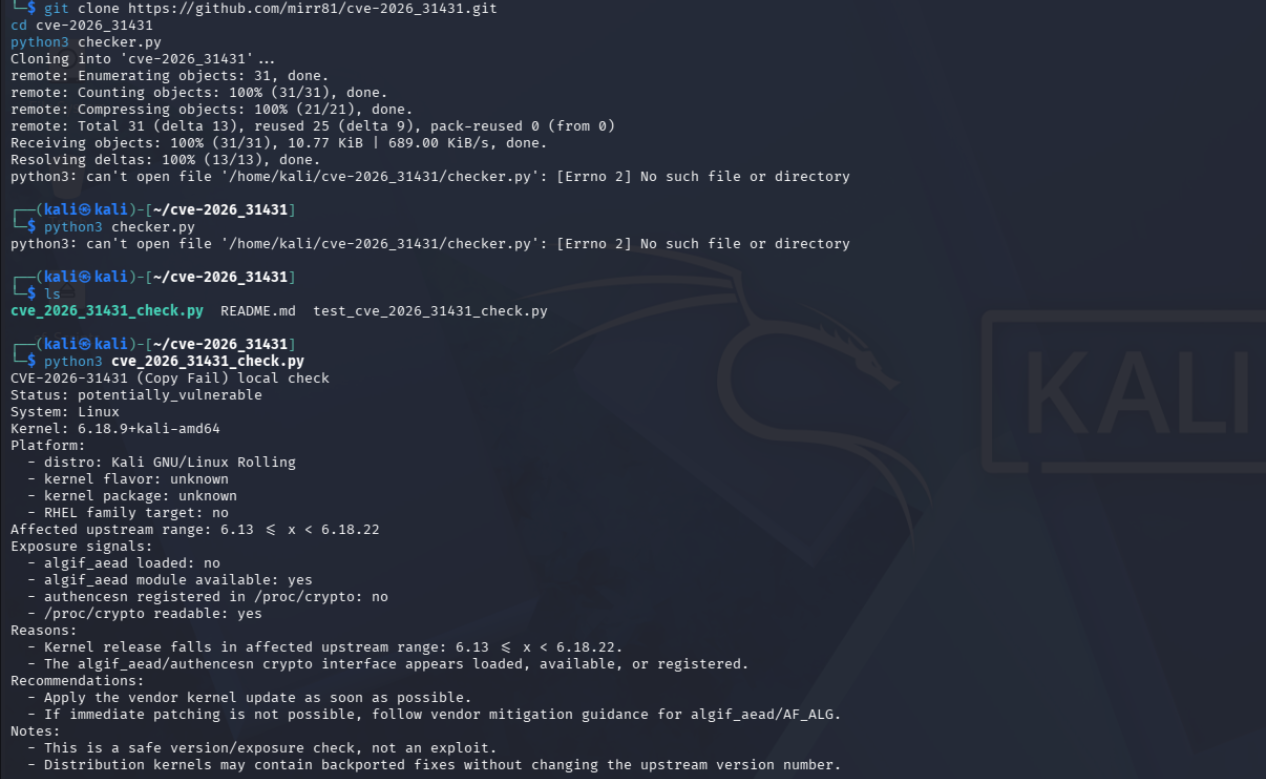 kuniyal08/copy-fail-cve-2026-31431-lab
Reproduced the fileless LPE CVE‑2026‑31431 (“Copy Fail”) on Kali Linux, then built auditd, Sigma & YARA detections to catch this stealthy kernel…
 wecooperate/imonitorsdk
The world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…