CVE-2026-31431-Copy-Fail

Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…

Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…

Educational demonstration of CVE-2022-0847 (Dirty Pipe) Linux kernel exploit with automated compilation script for privilege escalation and file…

Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…

Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…

Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

cPanel CVE-2026-41940 nuclear.x86 Security Audit & Cleanup Script

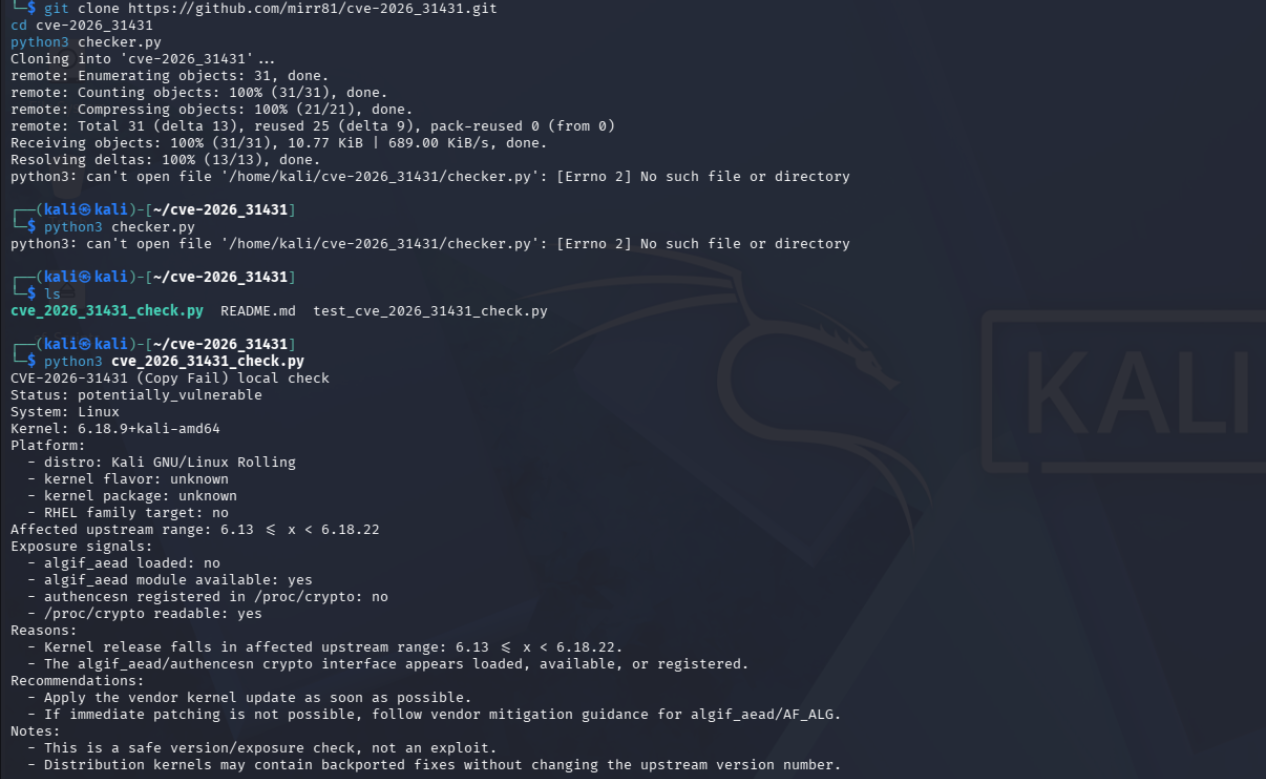
Reproduced the fileless LPE CVE‑2026‑31431 (“Copy Fail”) on Kali Linux, then built auditd, Sigma & YARA detections to catch this stealthy kernel…

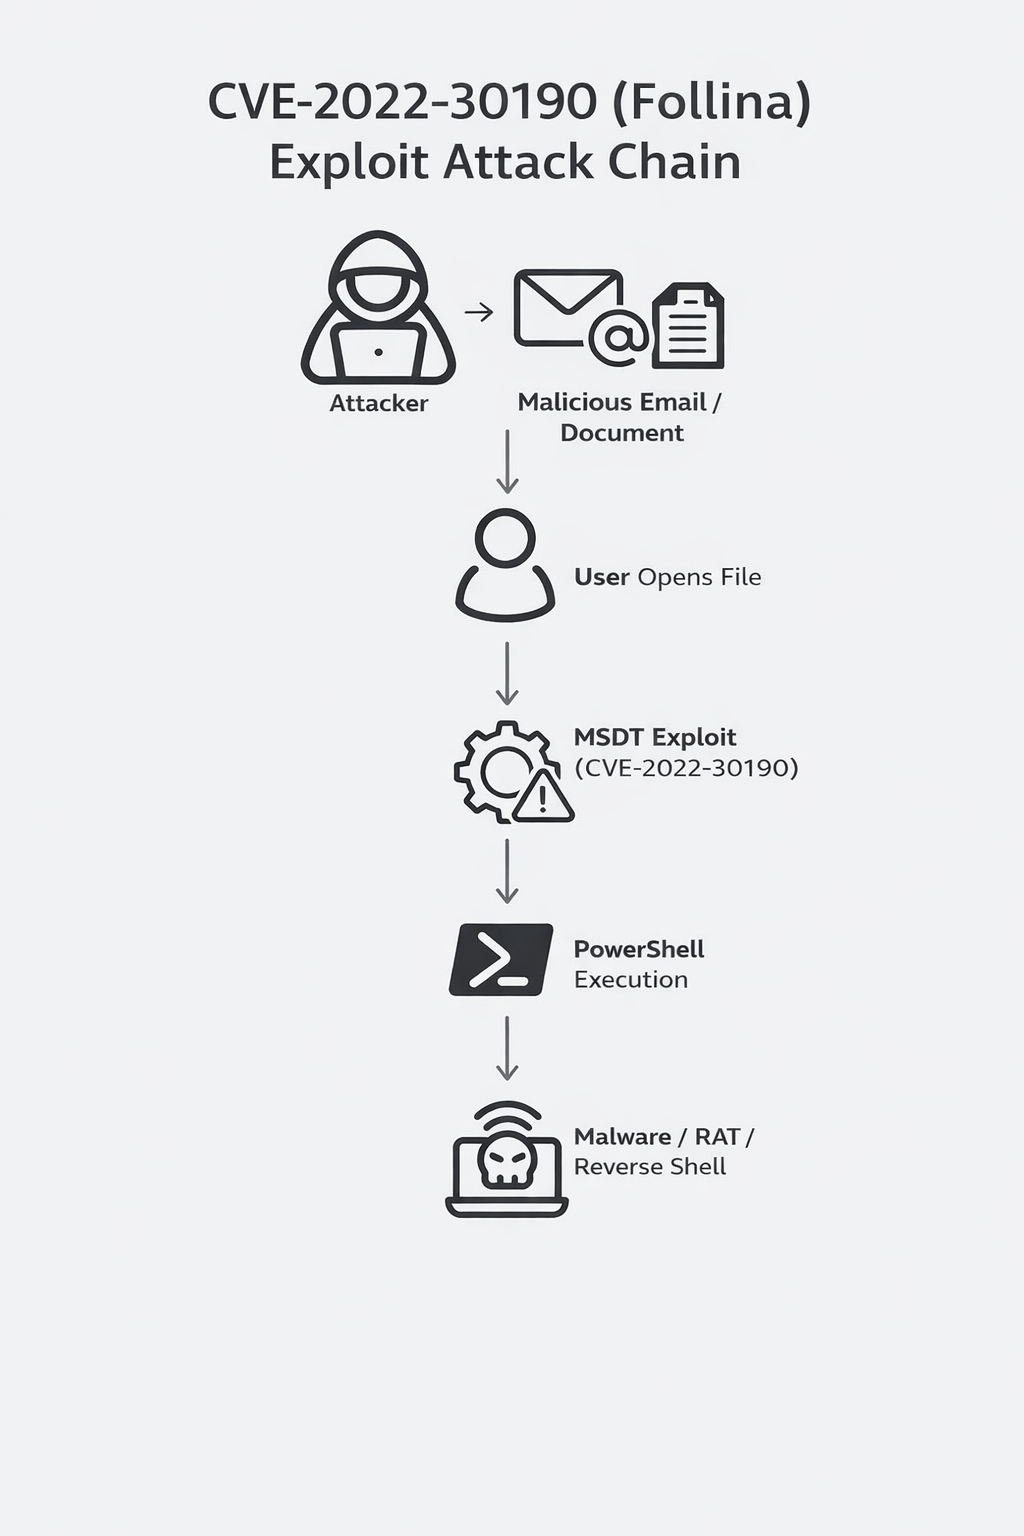
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

🪅 Windows & Linux userspace emulator

LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)

fireELF - Fileless Linux Malware Framework

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.

An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…

Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection