
my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…

Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…

Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…

Extracts URLs from malicious RTF files exploiting CVE-2017-0199 and CVE-2017-8759 for malware analysis and threat intelligence.

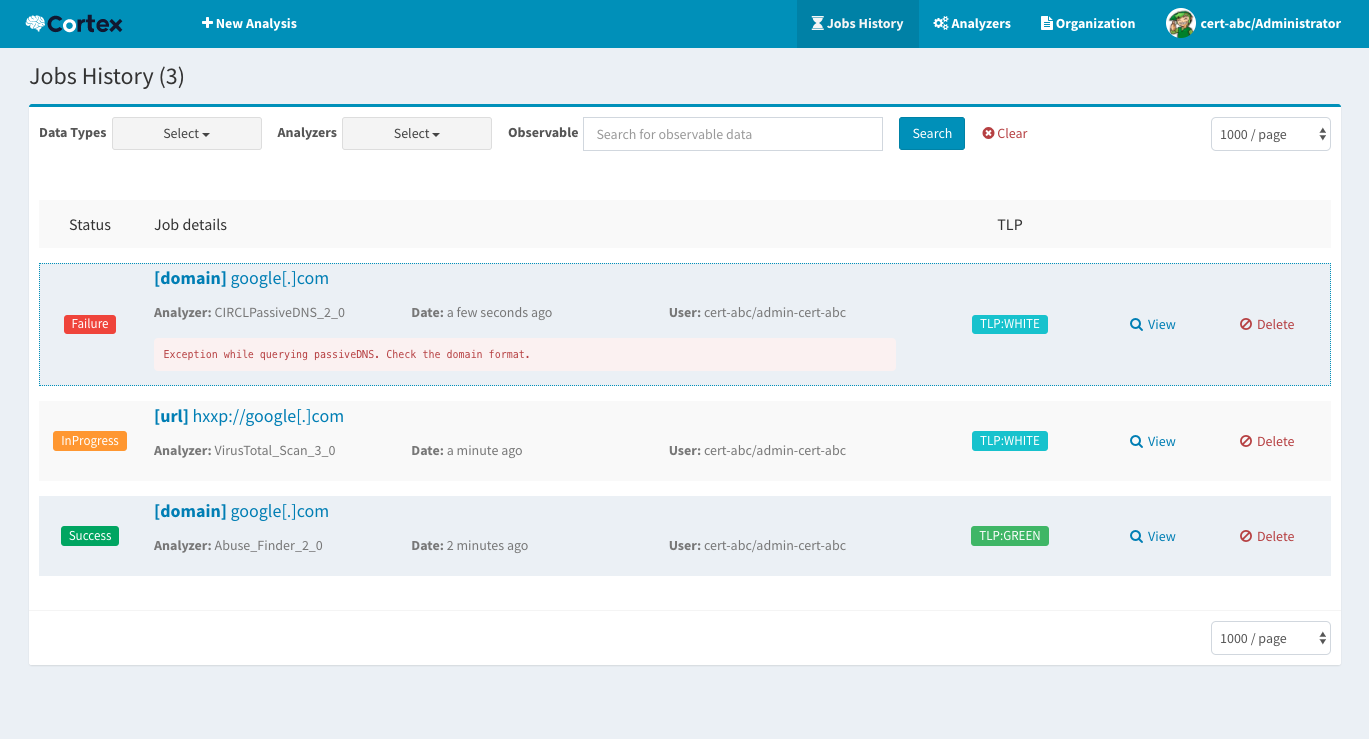
Cortex: a Powerful Observable Analysis and Active Response Engine

Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…

IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.

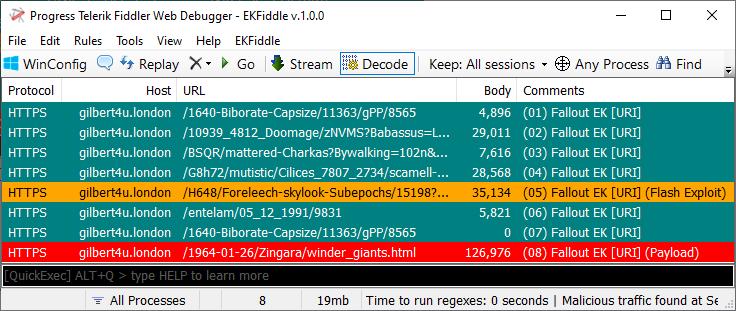
Your Swiss Army knife to analyze malicious web traffic based on the popular Fiddler web debugger.