
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
24 results
packer-tutorial preview

packer-tutorial

GitHubfrank2/packer-tutorial

A tutorial on how to write a packer for Windows!
binary-analysiseducationmalware-analysis+1
3182 years ago
YARA-Performance-Guidelines preview

YARA-Performance-Guidelines

GitHubneo23x0/yara-performance-guidelines

A guide on how to write fast and memory friendly YARA rules
educationmalware-analysisstatic-analysis
1751 year ago
polychrome-rs preview

polychrome-rs

GitHubdovelus/polychrome-rs

A PoC on how to use a Compute Shader as Payload
defensive-toolsencryption-decryption-toolsexploitation+5
717 days ago
AntiKernelDebug-POC preview

AntiKernelDebug-POC

GitHubgmh5225/antikerneldebug-poc

POC about how to detect windows kernel debug by pool tag.

debuggersdefensive-toolsmalware-analysis
123 years ago
Driver-PiDqSerializationWrite-Example preview

Driver-PiDqSerializationWrite-Example

GitHubgmh5225/driver-pidqserializationwrite-example

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
binary-analysisdebuggersdynamic-analysis-sandboxing+5
23 years ago
lupo preview

lupo

GitHubmalienist/lupo

WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
debuggersdynamic-analysis-sandboxingforensics+2
1024 years ago
AMSIDetection preview

AMSIDetection

GitHubwithsecurelabs/amsidetection

Proof-of-concept tool for detecting AMSI (Antimalware Scan Interface) bypasses and malicious in-memory script activity on Windows endpoints.
defensive-toolsdynamic-analysis-sandboxingmalware-analysis+1
326 years ago
TitanHide preview

TitanHide

GitHubmrexodia/titanhide

Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
anti-botbinary-analysisdebuggers+4
2.9k2 months ago
awesome-android-security preview

awesome-android-security

GitHubsaeidshirazi/awesome-android-security

A curated list of Android Security materials and resources For Pentesters and Bug Hunters
android-securitycurated-resourceseducation+6
2.0k1 month ago
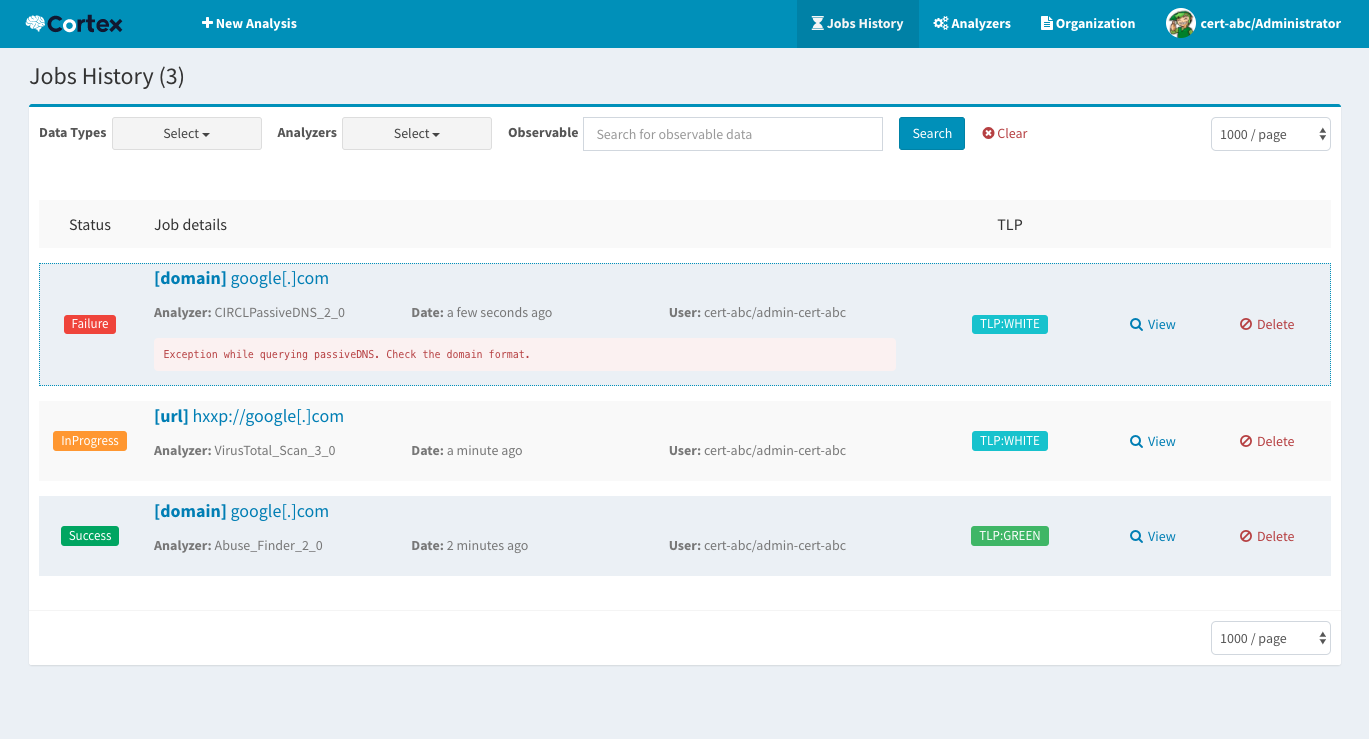
Cortex preview

Cortex

GitHubthehive-project/cortex

Cortex: a Powerful Observable Analysis and Active Response Engine
digital-forensicsincident-responseinformation-gathering+5
1.6k3 months ago
covertchannels-steganography preview

covertchannels-steganography

GitHubmindcrypt/covertchannels-steganography

A list of covert channels and steganography/steganalysis resources (books, papers & tools)

ctfcurated-resourcesdata-exfiltration+6
1064 years ago
JAKEYLOGGER preview

JAKEYLOGGER

GitHubsoheiltnt/jakeylogger

Python-based keylogger for capturing and logging keystrokes. Designed for educational security research and testing.

information-gatheringmalware-analysis
14 years ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
command-and-controldata-exfiltrationids-ips-evasion+8
21 month ago
rekall preview
Archived

rekall

GitHubgoogle/rekall

Rekall Memory Forensic Framework

digital-forensicsforensicsincident-response+3
2.0k5 years ago
EAC preview

EAC

GitHubgmh5225/eac

Compiles EAC and EOC anti-cheat SDKs, reversing research, and code resources to study how game anti-cheat systems integrate and operate.
binary-analysiscurated-resourceseducation+2
112 years ago
my-little-honeypot preview

my-little-honeypot

GitHubpandipanda69/my-little-honeypot

Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…

command-and-controliot-securitymalware-analysis+2
179 years ago
redxor preview

redxor

GitHubcorelight/redxor

Detection of Linux Malware C2 RedXOR - demonstration
defensive-toolseducationintrusion-detection+3
35 years ago
buttinsky preview

buttinsky

GitHubmushorg/buttinsky

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

information-gatheringintrusion-detectionmalware-analysis+2
8213 years ago
Previous12Next