
jd
 ejfkdev/jd
Go CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…
code-analysisdynamic-analysis-sandboxingmalware-analysis+3
3
ejfkdev/jdGo CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…

 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 slaughterjames/excelpeek
Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 shri142/zipscan
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
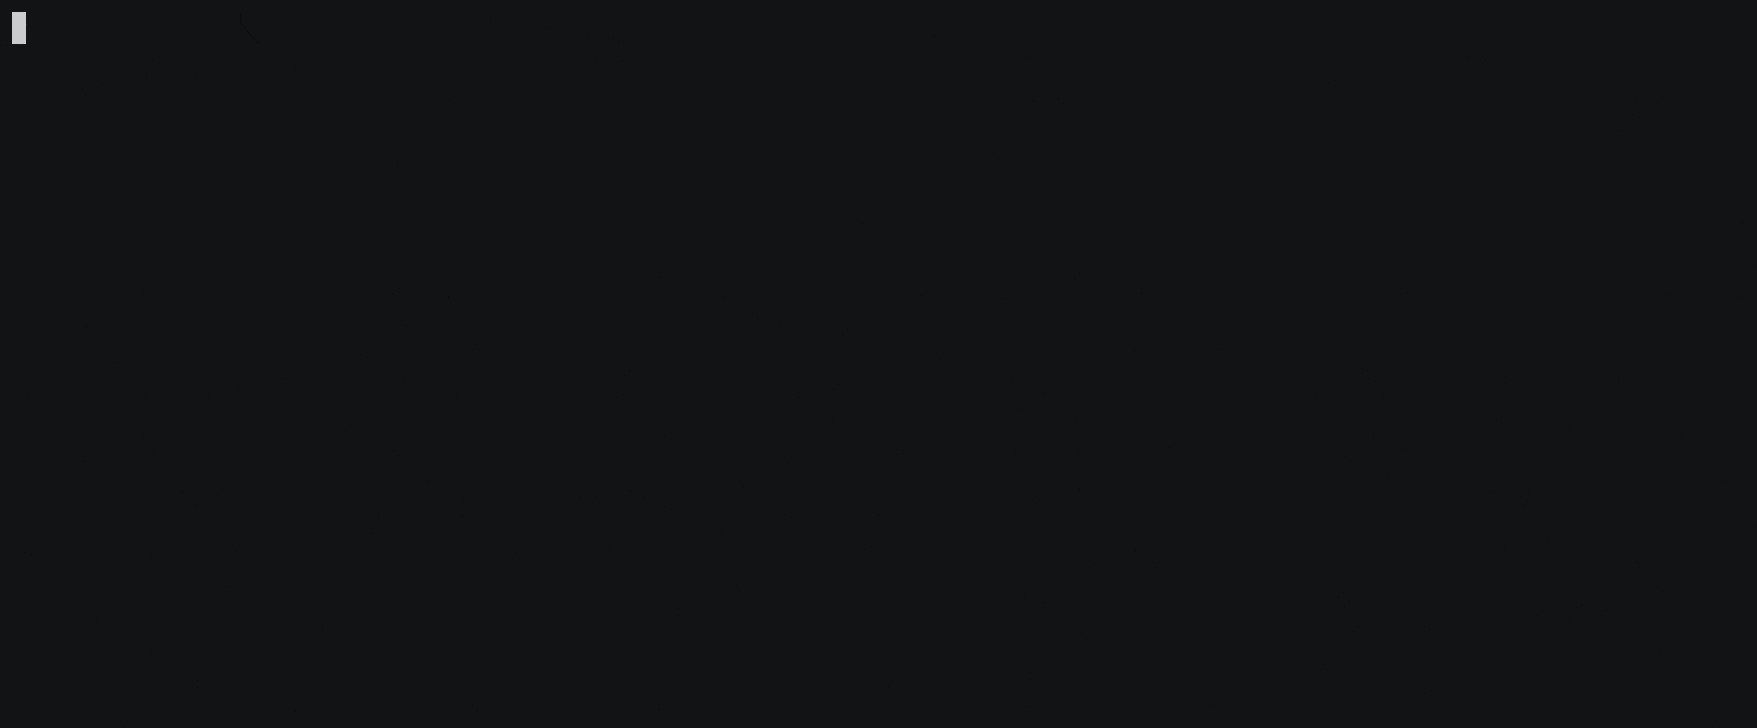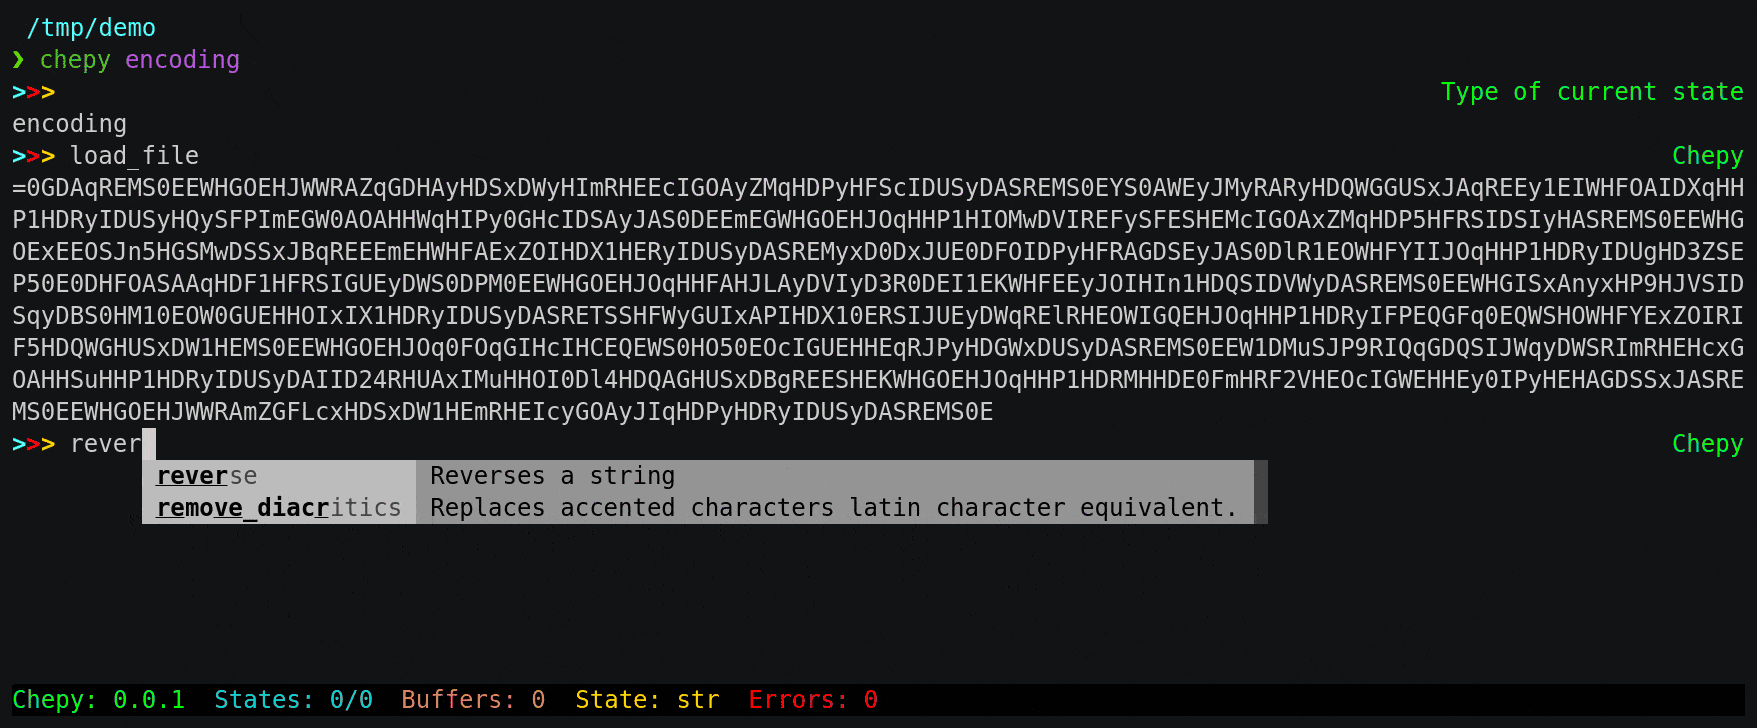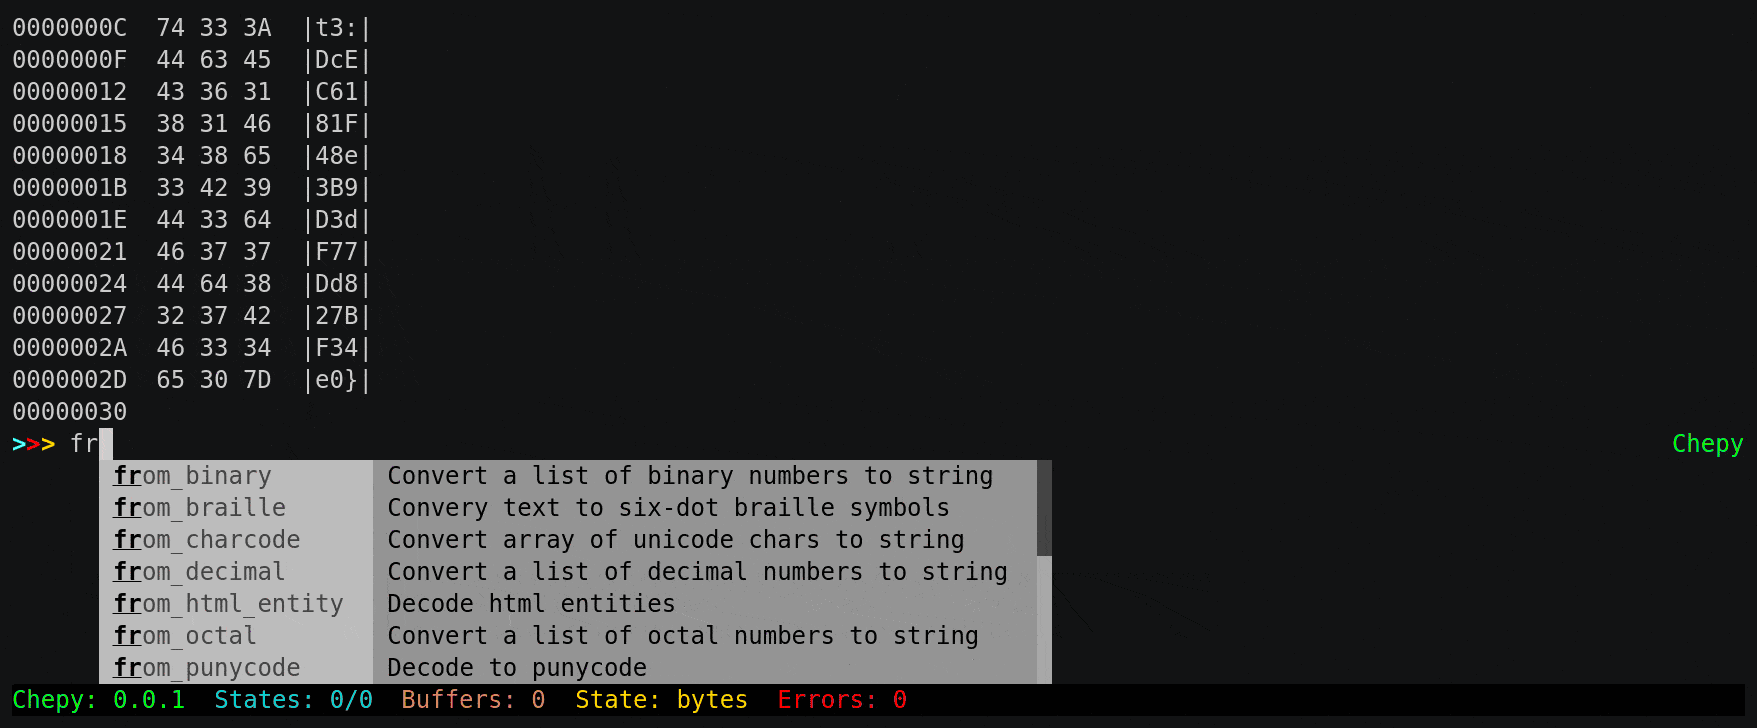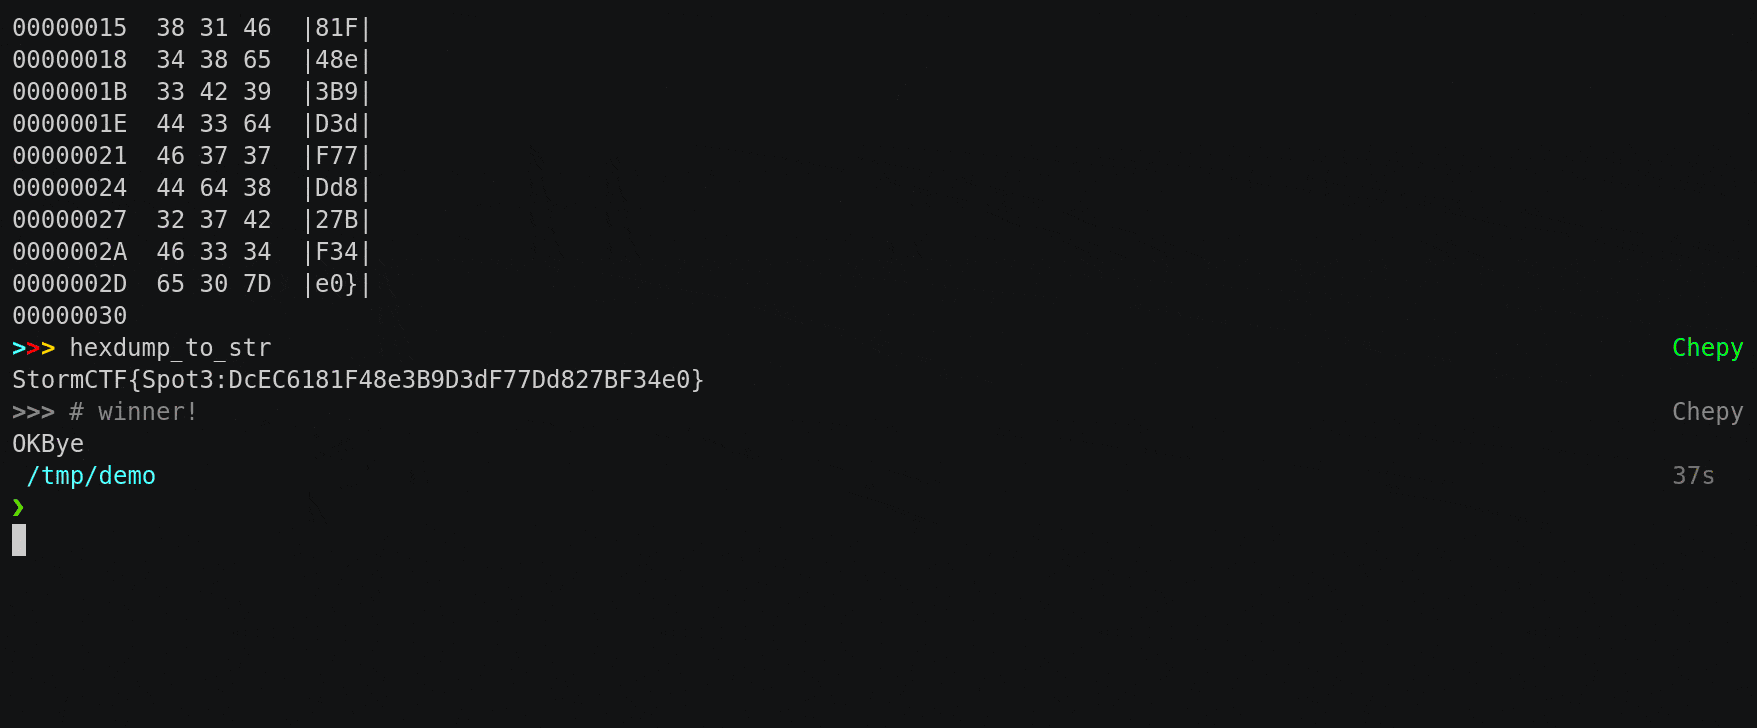 securisec/chepy
Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 bi8d0/driversentinel
DriverSentinel is a security tool developed in Go that detects malicious and vulnerable drivers on Windows systems by comparing them against the…
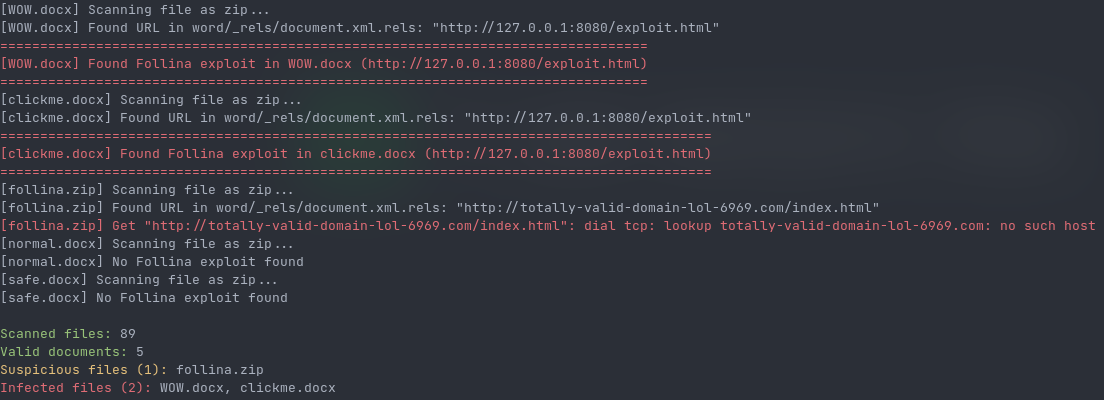 errornointernet/follinascanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
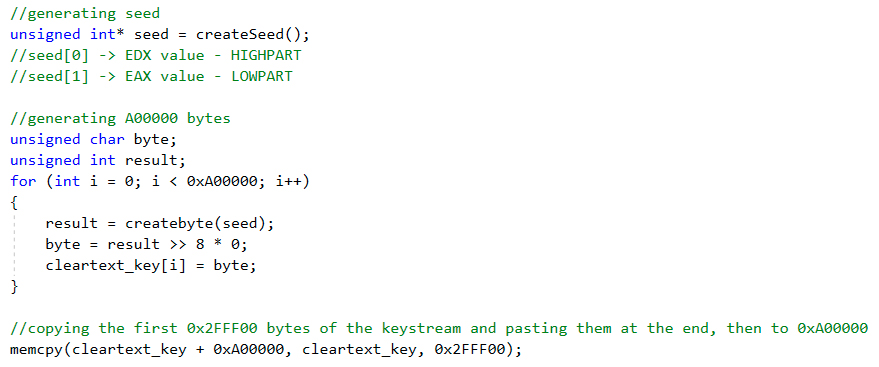 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
 jnschaeffer/cve-2022-44268-detector
Detect images that likely exploit CVE-2022-44268